Tag: News

  • Popcorn Time’s forgotten updater left millions of devices exposed to hijacking

    You may have forgotten about Popcorn Time. Unfortunately, its updater didn’t forget about your device.

    Security researchers have intervened to disable an abandoned update mechanism in Time4Popcorn, a version of the once-popular streaming app. If left running in the background, the updater could have allowed attackers to take control of Windows and Mac computers, even if their owners hadn’t opened the app in years.

    Eye Security estimates that the vulnerable updater was present on millions of devices worldwide, including 2.5–3 million Windows computers and around 250,000–350,000 Macs.

    Popcorn Time made watching movies and TV shows through BitTorrent look more like browsing Netflix. Rather than making users find torrent files and open them in a separate client, it wrapped the process in a familiar streaming-style interface.

    Amid concerns about copyright infringement and its possible consequences, the original developers abandoned it shortly after its launch in 2014. But because its source code was publicly available, other developers could pick it up and create their own versions, known as forks.

    One of those was Time4Popcorn, which was also distributed under the name “Popcorn Time.” That shared branding matters because people may have installed the affected software without ever seeing the Time4Popcorn name.

    The problem at hand

    Time4Popcorn was eventually abandoned too. But its update infrastructure was left behind, and at some point the domains associated with the software became available for others to register.

    In other words, the people maintaining the software had gone away. The software’s ability to accept instructions had not. Time4Popcorn’s updater used unencrypted HTTP connections and accepted executable updates without checking digital signatures to verify their authenticity. So, someone who controlled an update domain or was able to tamper with the unencrypted traffic could supply their own program instead.

    That combination created a remote code execution vulnerability, tracked as CVE-2026-30612, which could let an attacker run malicious software on a device. An attacker wouldn’t need to persuade someone to watch a movie or click a suspicious attachment. The forgotten updater could do the work for them.

    Although Android was affected too, users had an extra layer of protection. Its updater checked for updates when the application was opened, but installing an attacker-supplied APK required the user to approve the installation. It was not the same silent, background takeover route researchers found on Windows and macOS.

    What the researchers did

    Eye Security registered an abandoned update domain and used the vulnerable mechanism to distribute an update that disabled the updater itself. On Windows, it stopped and disabled the service; on macOS, it prevented the update process from starting. The researchers say their intervention did not delete users’ files or collect host data.

    By March 2026, Eye Security reported more than two million downloads of its updater-disabling fix, and update requests to its domains had fallen by 98%. Later that month, it transferred the 15 domains it controlled to the nonprofit Shadowserver Foundation.

    Researchers could not remotely disable the Android updater in the same way. And the desktop application still contained other weaknesses, including an obsolete Chrome engine dating from 2014 and disabled sandbox protections, which normally help contain malicious code.

    What users should do

    If you used Popcorn Time years ago, check the devices on which you installed it. Don’t assume that no longer using an application means its background components have stopped running.

    • Check your list of installed applications for Popcorn Time or Time4Popcorn. Pay particular attention to older Windows PCs, Macs, and Android devices where you may have forgotten about installing it. The affected fork was distributed under both names.
    • Remove the old application. There is no vendor security update for the abandoned Time4Popcorn software. Disabling the updater addresses one vulnerability, not the application’s other security weaknesses.
    • On Windows and macOS, check that the background updater is no longer running. Eye Security identifies the Windows component as Updater.exe, normally inside a Popcorn Time folder under Program Files or Program Files (x86), running through a service called Update Service. On macOS, the component is /Library/PrivilegedHelperTools/PT.updd, with a launch daemon at /Library/LaunchDaemons/PT.updd.plist. Its advisory provides instructions for disabling these components if needed.
    • On Android, uninstall the affected app rather than accepting an update prompt from it. The updater is part of the main application and cannot easily be disabled separately.
    • Use an up-to-date, real-time anti-malware solution to detect and block any attempts to install malware on your devices.

    As we saw recently, cybercriminals can use software updates to distribute malware. Remove abandoned apps and check for any background updaters they leave behind.


    From reporting threats to removing them.

    Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

    Source: Malwarebytes Labs · 2026-10-26

  • Patient records exposed in Quest breach: What you need to know

    Quest Diagnostics has confirmed that an unauthorized party accessed a system healthcare providers use to order laboratory tests and view results, affecting personal information and patient records.

    Quest is a major US laboratory testing company whose services help healthcare professionals diagnose and monitor medical conditions. Those services range from routine laboratory testing to specialized testing in areas such as cancer, infectious diseases, and neurology.

    What happened and what was stolen?

    The company learned of unauthorized access to its Quanum Lab Services Manager, or LSM, on October 21. The compromised platform lets healthcare professionals order tests, access results, review historical trends, and order supplies. Quest paused access to the platform and began investigating. Quest says its core business operations remain up and running.

    An investigation is ongoing. Quest has not yet published a count of affected patients or a complete list of the information accessed. It says it will notify affected patients, healthcare providers, and health plans.

    The company said:

    “personal information and patient records were affected.”

    It confirms that health information and personally identifiable information were involved, but has not specified whether these included Social Security numbers, insurance identifiers, payment information, particular test results, or account passwords.

    What patients can do now

    Quest says it will send notification letters to affected patients once its investigation is complete. Those letters will describe available resources, including credit and identity monitoring. If you receive one, read it carefully and follow the instructions. You can also check the FAQs posted in Quest’s breach notice for updates.


    A breach does not automatically mean someone has misused your information, but you can take these precautions while you wait for more details:

    • Verify unexpected messages independently. Don’t let a message about the breach rush you into clicking a link, sharing sensitive information, or making a payment. Go to Quest’s official website yourself or use contact details you already trust.
    • Review medical bills and insurance statements. Look for appointments, tests, prescriptions, or services you did not receive. The Federal Trade Commission (FTC) identifies unfamiliar medical bills and unexpected items on an Explanation of Benefits statement, which explains how your insurer processed a claim, as warning signs of medical identity theft. Report discrepancies to your healthcare provider and your insurer.
    • Review your credit reports. Look for unfamiliar accounts or debts and dispute errors. Free reports are available through AnnualCreditReport.com.
    • Act if you find signs of identity theft. Visit IdentityTheft.gov for a recovery plan. If someone has received care in your name, ask the providers involved for copies of your medical records and request corrections in writing.

    Medical identity theft is not just a financial problem; it can also affect your care. Someone using your identity to obtain treatment or submit insurance claims could introduce incorrect information into your health records. Checking medical statements and reporting anything unfamiliar can help you catch that misuse.


    Let’s face it, an incognito window can only do so much. 
     
    Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

    Source: Malwarebytes Labs · 2026-10-26
  • Hungarian Tycoon’s Firm Funded Pro-Orbán Advertising Agency, Records Show

    Hungarian Tycoon’s Firm Funded Pro-Orbán Advertising Agency, Records Show

    A firm owned by Hungarian construction mogul László Szíjj — who amassed a fortune under previous Prime Minister Viktor Orbán — donated about $863,000 to Megafon, a political advertising agency that promoted the former ruling party. 

    The donations are detailed in two years of annual financial statements from Szíjj’s firm, Vakond Via Kft., which were examined by OCCRP and Direkt36. The company made “cash grants” that totaled 300 million Hungarian forints to Megafon Digital Incubator Center, adding up to about $252,000 in 2024, and $611,000 the following year.

    Launched in 2020, Megafon became one of Hungary’s most influential political advertising agencies, mainly running social media campaigns in support of Orbán’s Fidesz party.

    But since Orbán’s stunning electoral defeat in April, after 16-years in power, Megafon has kept a low profile. The company’s website was taken offline in August, and its employees have fallen from 72 to three, according to information from a firm that provides commercial registry data.

    Neither Megafon nor Szíjj responded to requests for comment. 

    Megafon’s situation mirrors the condition of other media organizations that backed Fidesz, and received generous state advertising contracts or donations from government-friendly entrepreneurs. 

    Since coming to power, Hungary’s new prime minister, Péter Magyar, has taken steps to halt state advertising being funneled into pro-Fidesz media. Some outlets have stopped publishing, while others have downsized as their budgets dried up.

    OCCRP and Direkt36 recently reported that Megafon had received about $12 million between 2022 and 2024 from a firm owned by Lőrinc Mészáros, another wealthy pro-Orbán businessman. Mészáros, who is also a business partner of Szíjj, did not respond to questions at the time. 

    Magyar cited those findings in a Facebook post following publication, saying the reporting confirmed that Mészáros’ firm, while “funded by public money,” had supported Megafon’s “propaganda.” Magyar asked in the post how long the State Audit Office would “remain silent” about the funding.

    The State Audit Office has confirmed to Direkt36 it is investigating finances around this year’s election. 

    “The audit naturally includes an evaluation of news reports and conclusions published in the press, including an examination of Megafon’s activities,” the office said in an emailed response to questions.

    It is unknown if Szíjj’s firm, Vakond Via, made donations to Megafon this year. Vakond Via’s 2026 annual financial reports are not yet available, and the company did not respond to a request for comment. 

    Vakond Via is part of Szíjj’s sprawling Duna Group of companies. The conglomerate’s flagship firm, the road-building company Duna Aszfalt Út és Mélyépítő Ltd., “won the highest value of public contracts” in a ranking compiled by Transparency International. 

    The anti-corruption group’s Hungarian chapter calculated that Duna Aszfalt received around $2 billion worth of public contracts between 2018 and 2020.

    Source: OCCRP · 2026-10-26

  • Sri Lanka Records Zero Prosecutions Amid Online Scam Surge

    Sri Lanka Records Zero Prosecutions Amid Online Scam Surge

    Authorities in Sri Lanka have failed to successfully prosecute a single transnational cyber scam case, police have said, despite more than a thousand arrests so far this year of suspected members of Asian fraud syndicates who have surged into the South Asian country.

    The admission comes as experts warn the island nation is becoming a destination of choice for thousands of scam workers fleeing Southeast Asian nations such as Cambodia, which had in recent years become home to massive scam compounds, many of them reliant on trafficked workers.

    Recently crackdowns in scam centers in Southeast Asia have driven mostly Chinese-origin scam syndicates to set up shop in vulnerable states from Madagascar to Papua New Guinea.
    Among the countries of South Asia, Sri Lanka stands out for being at “serious risk of becoming a hub for industrial-scale cyber scams,” the Global Initiative Against Transnational Organized Crime (GI-TOC) said last month.

    From January until September, Sri Lankan police have conducted raids on 27 suspected scam compounds around the country and arrested 1093 people, Sri Lankan police spokesman Fredrick Wootler told OCCRP and Sri Lanka’s The Sunday Times. 

    The figure represents a dramatic rise from 2025, when just 26 people were arrested, Wootler said. An additional 573 suspected scammers were arrested the year prior.

    Despite the well-publicized arrests, “we have not had a successful prosecution yet” of anyone suspected of using Sri Lanka as a base for scamming victims abroad, Wootler said.

    The issue, Wootler explained, is that Sri Lanka’s current computer crime law, which dates from 2007, only allows cases to be opened on the basis of a complaint from a victim. Since the majority of those getting scammed live abroad, few complaints have been received.

    Instead, he added, the vast majority of suspected scammers are being charged for visa violations and being removed from the country.

    “The current government is …very much keen to see that this type of criminal networks [must] be taken away from Sri Lanka,” Wootler said. 

    The head of Sri Lanka’s police cyber crime unit, Chandima Arumapperuma, told reporters that the majority of suspects arrested so far carry passports from Asian countries such as China, Vietnam, India, and Indonesia. Many come with travel records showing they had previously been in Cambodia or Myanmar, both well-known scam hubs, she added.

    Efforts to interview suspects are hampered by language barriers while devices are often encrypted and difficult to analyse, Arumapperuma added.

    “The volume of devices we find in each raid is so high, usually about 200 phones and laptops, and we simply do not have the resources to process all of them,” she said.

    Adding to the difficulty, experts say, is another factor: Sri Lanka is desperate for foreign exchange. The tourism-dependent country offers visa-free travel to passport holders from 40 countries, including China. It has also opened up investment for online gambling and brick-and-mortar casinos, and has opened up a “special economic zone,” known as Colombo Port City, to attract investors in the digital economy sector.

    “Online gambling and offshore gambling operate in legal gray areas in Sri Lanka. The country has an economically distressed project, the Colombo Port City. And then it has a mechanism for bringing large numbers of foreigners,” said Jason Tower, a transnational crime expert at GI-TOC.

    In contrast to Southeast Asian scam hubs, where compounds have operated out in public view with protection from politicians and armed groups, Sri Lanka’s scam industry remains clandestine. But failure to tackle these networks could allow the industry to grow to a scale at which criminals become a force powerful enough to defy the government, Tower warned. 

    “The imagination is the limit. Going from what’s hidden and clandestine to what is open and obvious, “ he said.

    “Right now Sri Lanka’s sort of on the threshold.”

    Source: OCCRP · 2026-10-25

  • Chinese Scam Boss Murdered in Sri Lanka Had Multiple Identities

    Chinese Scam Boss Murdered in Sri Lanka Had Multiple Identities

    A Chinese cyber scam boss who was kidnapped and murdered in Sri Lanka’s capital in July went by three separate aliases and carried at least two passports, according to documents obtained by OCCRP and The Sunday Times.

    Chen Guoqing, 31, was abducted from the Colombo Port City special economic zone in the early hours of July 23 by a group of over a dozen men, one of them brandishing a pistol, according to a copy of the police investigative report into the incident. He was driven to a rural area over 70 kilometers east of Colombo, tortured to death, and his body was abandoned.

    The murder of Chen — and the hunt for his killers — received extensive media coverage in Sri Lanka, amid fears that the South Asian country is becoming a new base for Asian criminal syndicates that target victims around the world with sophisticated online fraud schemes.

    Sri Lankan police told OCCRP and the Sunday Times that they have arrested five Chinese nationals over the murder and are seeking another three suspects, who are believed to have fled the country. Local authorities have said they believed Chen was involved at a high level in international criminal activity and was murdered over a money dispute with other criminals.

    Investigative files show police recovered two passports belonging to the murder victim, each using a different name. One, a Cambodian passport, identified him as Chen Hao. The other, from Suriname, identified him as Tao Guoqing.

    Reporters were able to find the murder victim’s real name — Chen Guoqing — by crosschecking his Cambodian passport with a publicly available copy of naturalization and name change records from that country’s Gazette.

    Chen’s real name is not mentioned in the Sri Lankan police investigative report, and neither his Cambodian nor his Surinamese aliases have been reported in local media. 

    Details of Chen’s identity come as OCCRP and the Sunday Times have revealed that, despite over a thousand well-publicized arrests, Sri Lanka has failed to successfully prosecute a single person for using the country as a base to conduct online scams targeting foreigners.

    Brian Hanley, the Asia-Pacific Director of the Global Anti-Scam Alliance, said Chen’s murder highlights the vulnerability of Sri Lanka to infiltration by scam syndicates fleeing crackdowns in traditional Southeast Asian epicenters like Cambodia.

    “There’s weak enforcement [by Sri Lankan authorities],” Hanley said. “Scams pay. Nobody gets caught. Or if they do, there’s no sanction.”

    “For a country like Sri Lanka this level of scam activity could easily start to see a single digit contribution to their entire GDP.”

    Source: OCCRP · 2026-10-25

  • Cyprus Parliament Reviews Reports on Abramovich-Linked Asset Transfers

    Cyprus Parliament Reviews Reports on Abramovich-Linked Asset Transfers

    The Cypriot Parliament this week discussed recent revelations about corporate maneuvers that allowed firms ultimately owned by Russian billionaire Roman Abramovich to sidestep tax and transparency requirements.

    The parliamentary hearings followed an investigation last week by OCCRP, CIReN, BBC, and TBIJ. The reports detailed how the Cyprus affiliate of multinational accountancy firm Deloitte, and corporate service provider MeritServus, worked together to backdate documents relating to companies beneficially owned by Abramovich. 

    Doing so helped the companies retroactively transfer billions of dollars in assets from Cyprus to the British Virgin Islands, where they would not be subject to Cypriot laws on tax and public disclosure. 

    OCCRP reached out to Deloitte’s offices in Cyprus and internationally for comment on the parliamentary hearing, but did not receive a response by the time of publication. Deloitte Cyprus previously told OCCRP it “acts in compliance with applicable laws.”

    MeritServus has been dissolved and it was not possible to obtain a comment. 

    Lawyers for Abramovich, from the London firm of Kobre and Kim, noted that he “has not been identified as the subject of any investigation, nor has he been charged with any wrongdoing.”

    “Our client’s position is that he denies that he evaded tax or concealed his assets,” the firm said in an emailed response to questions. 

    During the session of Parliament’s Standing Committee on Institutions on Wednesday, representatives of several state bodies were questioned about the findings of the journalistic investigation. Government institutions present included the Finance and Justice Ministries, the Tax Commissioner’s Office, the State Prosecutor and Police, Auditor General, and Central Bank, as well as the Cyprus Securities and Exchange Commission.

    An official from the Justice Ministry told the committee that information published by the media outlets would be assessed, and that police investigations would be carried out to determine whether any criminal acts had been committed.

    A representative of the Cyprus Public Audit Oversight Board said the body had been in contact with Deloitte Cyprus since the publication of the reports. The representative referred to difficulties Deloitte Cyprus was experiencing in retrieving data and communications from the relevant period, but stated that the company would provide all relevant information as it became available. 

    Several representatives of regulatory bodies present at the hearings highlighted general improvement made in Cyprus since the period covered by media reports, particularly as a result of E.U. directives being transposed into national law.  

    Tax reform laws introduced in Cyprus in January increased the possible fine for failure to pay the Special Defense Contribution, one of the taxes the companies beneficially owned by Abramovich were obliged to pay. A fine could be as much as 100,000 euros ($112,200) in addition to four times the originally owed tax for repeat offenders.  

    Source: OCCRP · 2026-10-23

  • Many in Serbia’s Youth Movement Fear a Rigged Election on Sunday

    Many in Serbia’s Youth Movement Fear a Rigged Election on Sunday

    Riding an extraordinary wave of public mobilization, Serbia’s student-led opposition heads into Sunday’s snap parliamentary election genuinely believing it can break President Aleksandar Vučić’s 14-year grip on power.

    Yet beneath the euphoria of this week’s mass rallies lies a pervasive conviction among its supporters that the contest will be anything but fair—and that the ruling party will resort to outright ballot theft rather than concede defeat.

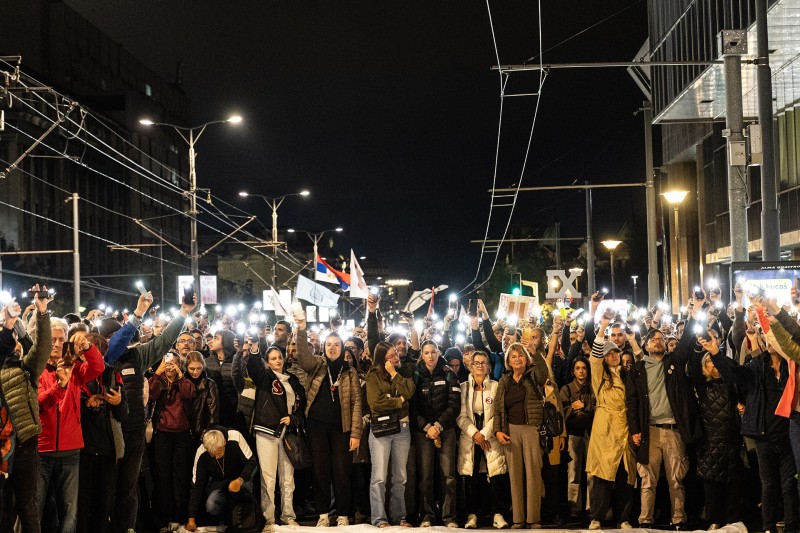
    On Thursday night, that tension was on full display as hundreds of thousands of people flooded into Belgrade’s central Slavija Square, filling the surrounding boulevards in a buoyant, flag-waving display of collective defiance. The assembly marked the movement’s final campaign rally ahead of an early vote that serves as the culmination of nearly two years of youth-led unrest against Vučić’s rule.

    What began in November 2024 as grief and outrage following the collapse of a newly renovated railway station canopy in the northern city of Novi Sad—a disaster that killed 16 people and was turned by the protesting youth into a lethal symbol of state corruption and crony contracting—has since metastasized into a nationwide rebellion.

    Now polling in a dead heat with the governing Serbian Progressive Party (SNS), the youth movement’s “Students’ List” has mounted the most formidable electoral challenge Vučić has faced in over a decade. But across the sea of demonstrators in the capital, few harbored illusions about how the ruling machine will be handling the vote.

    “I believe he will do anything he can to steal the votes and remain in power,” said Katarina Zajić, 45, a food technologist who works as an administrative clerk in the Belgrade municipality of Zemun.

    That skepticism is informed by years of documented electoral abuse. International election observers, led by the Organization for Security and Co-operation in Europe (OSCE) and backed by European Union institutions, have consistently found that while Serbian elections offer voters a nominal choice of candidates, the playing field is fundamentally compromised. In report after report, monitors have cited pervasive state capture of broadcast media, intense pressure on public-sector workers to mobilize for the ruling coalition, the routine abuse of public resources for partisan gain, and deep-seated anomalies in the voter register.

    Domestic watchdogs have leveled even harsher verdicts. The Center for Research, Transparency and Accountability (CRTA), Serbia’s prominent independent election observation group, concluded that recent election cycles—including the disputed parliamentary and municipal votes in 2023 and 2024—were “not free and fair.” The watchdog documented organized voter migration schemes, the mass registration of “phantom voters,” and the wholesale erasure of the boundary between state institutions and the ruling party.

    Vučić and his party have vehemently denied any wrongdoing, routinely dismissing allegations of electoral manipulation as the reflexive excuses of “sore losers” fabricating an alibi for their own political weakness.

    “These were by far the cleanest and fairest elections to date, and everyone knows it,” Vučić declared following the 2023 ballot, even as opposition leaders launched hunger strikes and thousands took to the streets to protest organized cross-border voter bussing. 

    For many of those who massed in Belgrade on Thursday, however, the gap between the government’s assurances and the documented reality on the ground has left them preparing for a confrontation that will not end at the ballot box.

    “Vučić never organized fair elections. He never won the elections he didn’t organize, and there won’t be any difference this time,” said David, 45, who attended Thursday’s rally. “The more people come out for the elections, the bigger the chance to win against him. But if he still tries to steal, well, I don’t know… the streets.”

    He paused, measuring the consequences of what might follow Sunday night.

    “Violence is the last answer,” he said. “But if that’s the answer, we’re probably going to have to go that way.”

    Source: OCCRP · 2026-10-23

  • Resident Evil maker Capcom warns of phishing after 11.7 million records exposed

    .kadence-column480618_38f885-ca > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{column-gap:var(–global-kb-gap-sm, 1rem);}.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;}.kadence-column480618_38f885-ca > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column480618_38f885-ca > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column480618_38f885-ca > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column480618_38f885-ca{position:relative;}@media all and (max-width: 1024px){.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column480618_38f885-ca > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}

    In this article

    • Capcom’s breach exposed 11.7 million account records.
    • Leaked details could fuel convincing phishing messages.
    • Passwords on 196 accounts were changed without permission.
    • Use CAPCOM ID? Check your account and enable two-factor authentication.

    Gamers are being warned to watch their inboxes after someone gained unauthorized access to Capcom’s online membership service.

    Capcom, the Japanese video game developer and publisher behind Resident Evil, Monster Hunter, and Street Fighter, disclosed a breach affecting more than 11.7 million CAPCOM ID records worldwide.

    The exposed information includes email addresses, account activity details, and IP addresses. A much smaller number of records also contained personal details such as dates of birth.

    The company says credit card information was not affected, and it has not confirmed that passwords originally chosen by customers were compromised, but someone changed the passwords on 196 accounts without authorization. Capcom has since reset those passwords.

    CAPCOM ID is the company’s unified account system for its websites and services, including online features in certain games. Users can also link it to gaming platform accounts, including PlayStation, Xbox, Steam, Epic Games, and Nintendo accounts.

    For players, the exposed information could help scammers make fake Capcom messages more convincing, potentially tricking them into handing over passwords or verification codes.

    Capcom discovered the incident on October 19, and says it has addressed the attack method. Games and services remain available, and the company plans to notify affected customers.

    The 11.7 million figure refers to affected records, so it may not represent that many individual users. Capcom is still investigating the impact, including how the passwords on 196 accounts were changed without permission and whether any other unauthorized activity occurred on those accounts.

    How to stay safe

    As with any breach, watch for phishing messages, particularly those using the breach to create urgency. If an email claims your account needs attention, open your browser and go to cid.capcom.com independently to check it. Capcom warns users not to follow URLs or open attachments in suspicious messages.

    You can also take these steps:

    • Enable CAPCOM ID’s two-factor authentication: This adds an authenticator-app code to the sign-in process, helping protect your account if someone obtains your password. Set it up from your Account page using a smartphone or tablet. Capcom recommends Google Authenticator or Microsoft Authenticator.
    • Check your account, especially if you received an unexpected password-change notice: Review your registered information and linked platform accounts from your Account page. If you cannot sign in, use Forgot your password? on the login page. See Capcom’s support page for instructions.
    • Use official support channels if you need help: Find the appropriate regional contact in Capcom’s breach notice, rather than trusting contact details in an unexpected message.

    Pro tip: Unsure whether a message is a scam? Malwarebytes’ Scam Guard can help you assess it and suggest what to do next.


    Something feel off? Check it before you click.  

    Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

    Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

    Try it free → 

    Source: Malwarebytes Labs · 2026-10-23

  • Sanctioned Investor in Cambodian Scam Compound Owns California Mansion

    Sanctioned Investor in Cambodian Scam Compound Owns California Mansion

    Brendon Luo was sanctioned in June by the U.S. Treasury Department, which alleged he was an investor in a cyber-scam compound operated by Cambodia’s Prince Group. Property records show he still owns a mansion in a gated community in southern California.

    The Prince Group is widely accused of involvement in compounds in Cambodia where thousands of trafficked workers were forced to commit industrial-scale cyberfraud. The Prince Group has strongly denied the accusations, but the U.S. has sanctioned more than 140 allegedly-associated entities and individuals, including Luo.

    The sanctions have not disrupted Luo’s ownership of a five bedroom mansion in Yorba Linda, a city of about 68,000 people that is part of the Los Angeles metropolitan area. Although no sale price was identified in property records, online real estate portals value the property at roughly $5 million.

    Luo was born in China and acquired passports from Cambodia, Vanuatu and Cyprus, according to information from sanctions notices as well as immigration records obtained by OCCRP.  

    A Cambodian government factsheet distributed to the media in September stated that Luo was the “registered owner” of Legend Innovation Co. Ltd. That company allegedly operated a scam compound named 8Park, which was dismantled this year by Cambodian authorities.

    The U.S. sanctions notice alleged that Luo and another individual were “major investors in a Prince Group… scam compound that was used to facilitate fraud operations.”

    A Prince Group spokesperson said in an emailed response to questions that the conglomerate has “never had any relationship with Legend Innovation.”

    “Brendon Luo had no role within the Prince Group of companies, nor was he associated with their operations throughout South Asia,” the spokesperson added.

    Legend Innovation was sanctioned separately by the U.K. government in March. The U.K. Treasury said 8Park was “believed to be Cambodia’s largest scam compound, with capacity to accommodate 20,000 trafficked workers”.

    Luo did not reply to requests for comment sent to multiple company email addresses, and no one answered calls to phone numbers listed for his Cambodian firms. However, a representative for Luo did respond to questions via the Prince Group spokesperson.

    “Mr. Luo did not own Legend Innovation and had no role in it, or the construction or operation of any business that was conducted by it on the land in question,” Luo’s representative said. “Mr. Luo has never been associated with, nor had any ownership interest, in the companies referenced, or in their alleged scam operations.”

    The representative added that Luo “never held a role of any kind with Prince.”

    Luo’s California mansion in the “Enclave at Yorba Linda” development is down the street from a property that was owned by Chen Sokly. OCCRP recently identified Chen Sokly as the person referred to as “co-conspirator 2” in a U.S. federal court indictment of Prince Group founder and chairman Chen Zhi. The indictment charges Chen Zhi with alleged wire fraud and money laundering conspiracy. 

    American authorities alleged that co-conspirator 2 was a Prince Group “enforcer” who protected the conglomerate’s scam operations from police. Chen Sokly has not been charged in the case.

    The Prince Group spokesperson previously told OCCRP that the conglomerate and its chairman were innocent of the U.S. allegations, adding that it was “not a criminal syndicate but a collection of legitimate businesses serving millions of people and employing tens of thousands of people across the globe.” 

    Luo was listed as a director of Prince Plaza Investment Co. Ltd. In October 2025, the U.S. Treasury Department included that company on a list of sanctioned firms it said were “owned or controlled by, or purport to act for or on behalf of, members of Prince Group TCO [Transnational Criminal Organization].” 

    As previously reported by OCCRP, Luo’s real estate portfolio also includes a luxury condominium in downtown Tokyo.

    Source: OCCRP · 2026-10-23