ARCHIVE
Malware
-
Citrus Ransomware: VLESS for traffic, Sn00py for encryption, and LLMs lending a hand
We break down the Citrus Ransomware group's attacks: the attackers' TTPs and tooling, including VLESS traffic tunneling and LLM use, plus their links to Toy Ghouls.
SRC // Securelist (Kaspersky GReAT) -
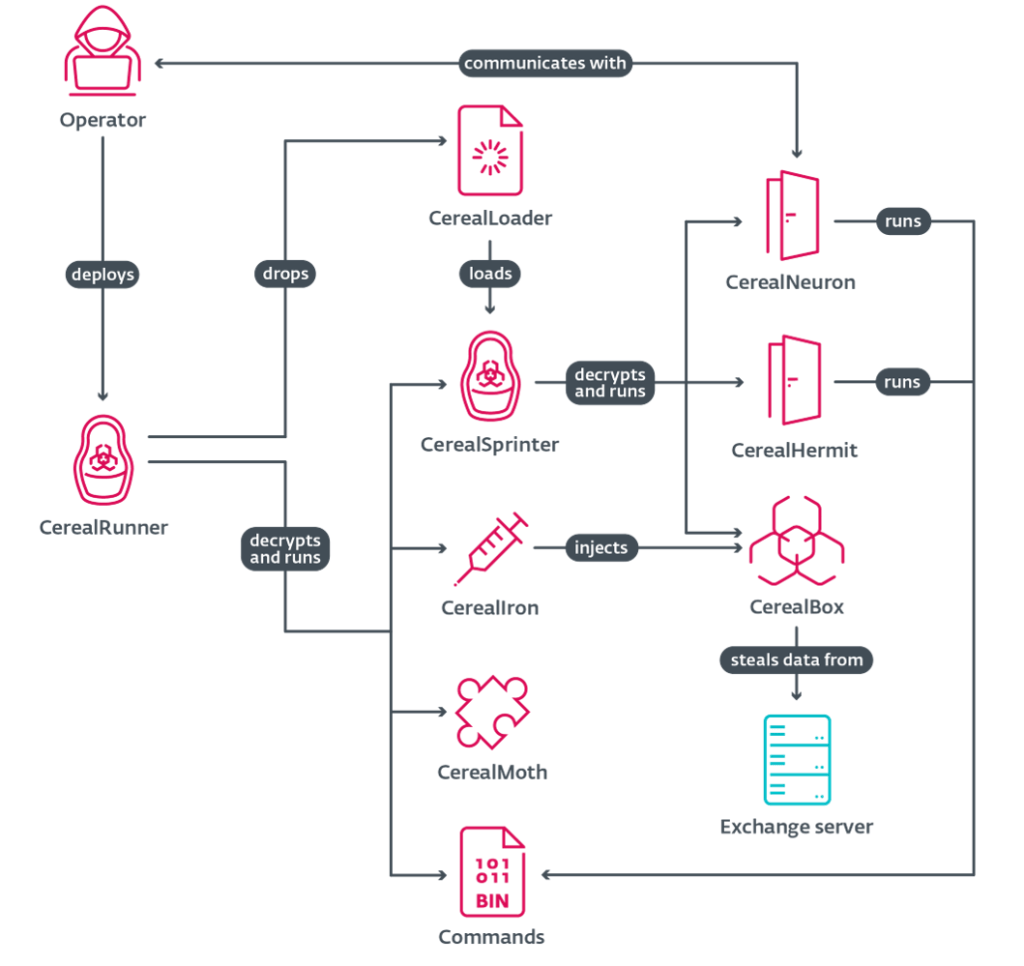
Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room
ESET found Russia-Linked APT group Turla using a new toolset, dubbed Cereal, on government Exchange servers in Kazakhstan and Romania. ESET Research detailed a previously undocumented toolset it calls Cereal,…
SRC // Security Affairs -
AI-Powered Malware Analysis Uncovers Hidden Phishing Threats and Reduces SOC Workload
AI powered malware analysis helps teams reveal hidden phishing attacks, connect related threats and automate reports to reduce investigation workload.
SRC // HackRead -
Russian hackers compromised government email servers to steal NATO, EU correspondence
Russian state-linked hackers have compromised government email servers in Romania and Kazakhstan to secretly intercept messages exchanged with NATO and European Union officials, researchers said.
SRC // The Record -
Ca: Data breach at The Children’s Foundation
Tim Durkin reports: The Children’s Foundation has issued a privacy notice following a data breach involving its IT service provider, Highland Shores Children’s Aid Society. An unauthorized third party accessed…
SRC // DataBreaches.net -
Turla’s Cereal malware turns victims’ Exchange servers into spy hubs
Russia-aligned group Turla planted a modular .NET toolset on Microsoft Exchange servers at two government organizations, one in Kazakhstan and one in Romania, and used it to copy selected email…
SRC // Help Net Security -
QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices
Taiwanese vendor QNAP urges users to update Plex Media Server after reports of NAS compromises through the Plex2Shell vulnerability chain. QNAP urges users to update Plex Media Server through the…
SRC // Security Affairs -
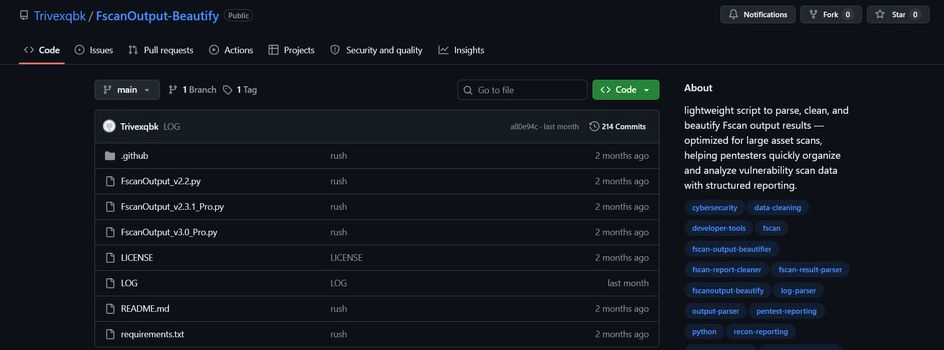
Fake GitHub Security Tools Infect Over 2,000 PCs With Malware
Fake GitHub security tools are spreading malware that disables defenses, steals sensitive data and infects over 2,000 PCs. Cybersecurity firm Doctor Web has found malware hidden in GitHub projects that…
SRC // Security Affairs -
An average of 8 minutes is all hackers need to log in with stolen credentials
Attackers used stolen credentials to log in an average of eight minutes after infection across 27 confirmed infostealer cases, according to a report from Elastic Security Threat Command. Researchers also…
SRC // Help Net Security -
Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly
Brenner Base Tunnel SE confirms a breach and Everest claims 812 GB. What we know, what we don’t, and why overblown alarm helps propaganda more than the attackers. Brenner Base…
SRC // Security Affairs