ARCHIVE
Malware
-
Who Runs the Ransomware Group Qilin?
Brian Krebs reports: The cybercrime group Qilin has emerged as the world’s most active ransomware affiliate program, claiming at least 365 victim organizations in the past three months alone. But…
SRC // DataBreaches.net -
Hackers Deploy Malware in Fresh ScreenConnect Campaign
The attackers exploited a vulnerability in a legitimate extension to bypass ScreenConnect authentication. The post Hackers Deploy Malware in Fresh ScreenConnect Campaign appeared first on SecurityWeek.
SRC // SecurityWeek -
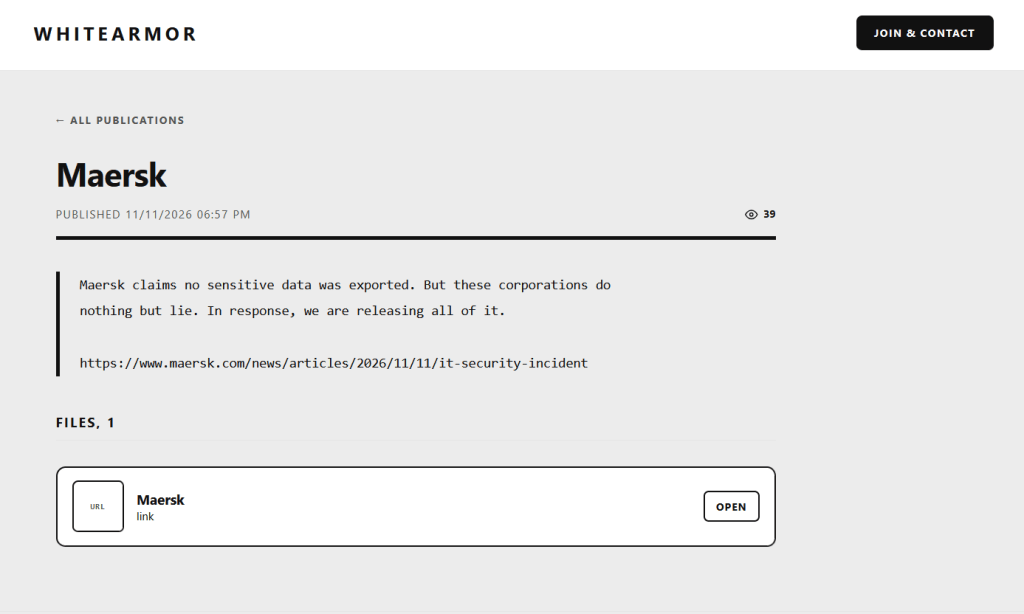
WhiteArmor Demands $5 Million from Maersk, Claims Theft of 100GB of Data
Maersk confirms a data breach involving a legacy system, while WhiteArmor claims 100GB of stolen data and demands a $5 million ransom. A.P. Moller Maersk, the Danish shipping giant, says…
SRC // Security Affairs -
The XG Files: Falcon C2 Flying Under The (Browser) Radar
We uncover Falcon C2, a browser-based threat framework targeting governments via malicious scripts, extensions, and the Antino implant. The post The XG Files: Falcon C2 Flying Under The (Browser) Radar…
SRC // Palo Alto Networks Unit 42 -
ESET Links Cereal to Turla in Romanian Server Breach Case — Defense News
UA News reports: Slovak cybersecurity company ESET said that servers of a Romanian government institution were compromised in December 2025. The malware selected emails related to NATO and the European…
SRC // DataBreaches.net -
TinstaPorn Android Malware Poses as Casino App to Collect User Data
A fake Macau casino app uses rigged betting odds to exploit gamblers while collecting phone numbers, location data…
SRC // HackRead -
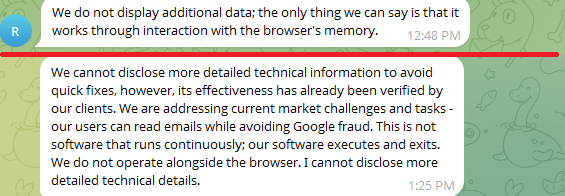
Hackers Advertise a $1,000 Gmail Tool That Allegedly Survives Password Resets
Hackers advertise a $1,000-a-month tool claiming persistent Gmail access after password resets, but its effectiveness remains unverified. A developer of hacking tools is selling a $1,000 per month feature that…
SRC // Security Affairs -
Citrus Ransomware: VLESS for traffic, Sn00py for encryption, and LLMs lending a hand
We break down the Citrus Ransomware group's attacks: the attackers' TTPs and tooling, including VLESS traffic tunneling and LLM use, plus their links to Toy Ghouls.
SRC // Securelist (Kaspersky GReAT) -
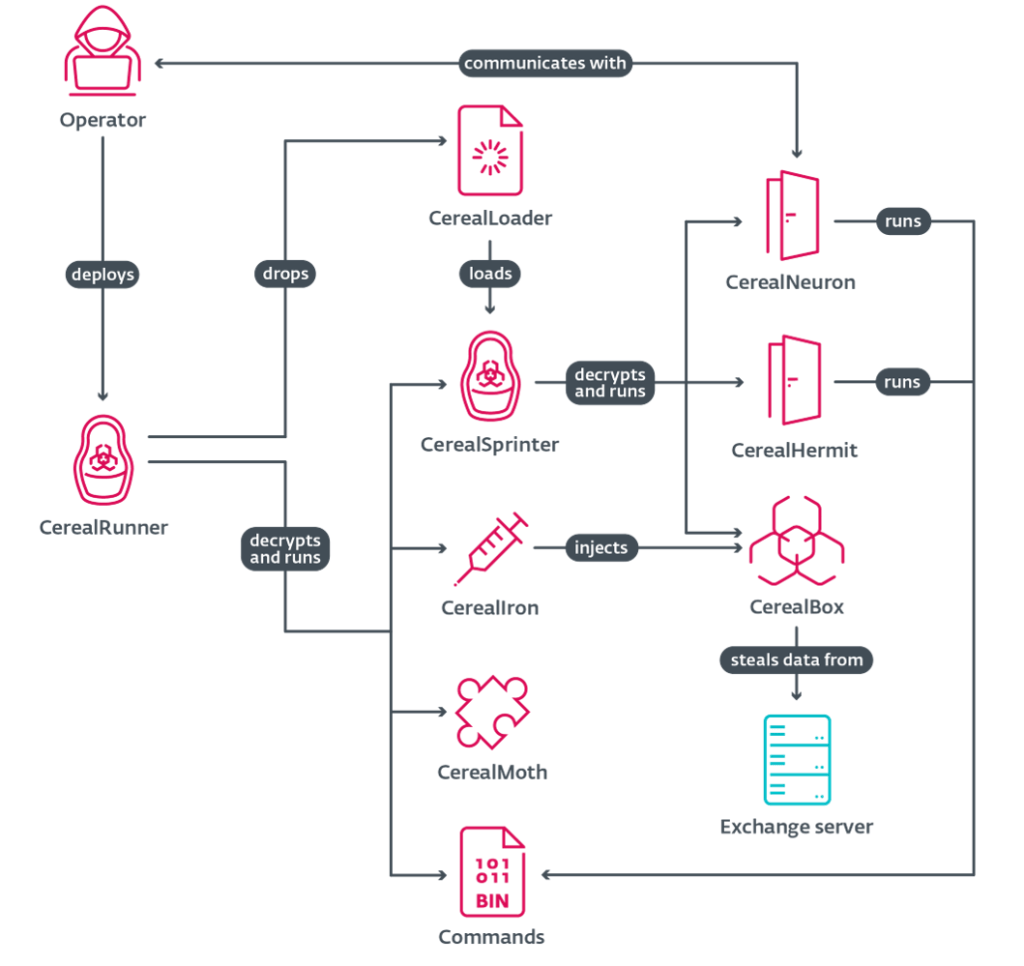
Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room
ESET found Russia-Linked APT group Turla using a new toolset, dubbed Cereal, on government Exchange servers in Kazakhstan and Romania. ESET Research detailed a previously undocumented toolset it calls Cereal,…
SRC // Security Affairs -
AI-Powered Malware Analysis Uncovers Hidden Phishing Threats and Reduces SOC Workload
AI powered malware analysis helps teams reveal hidden phishing attacks, connect related threats and automate reports to reduce investigation workload.
SRC // HackRead