ARCHIVE
Malware
-
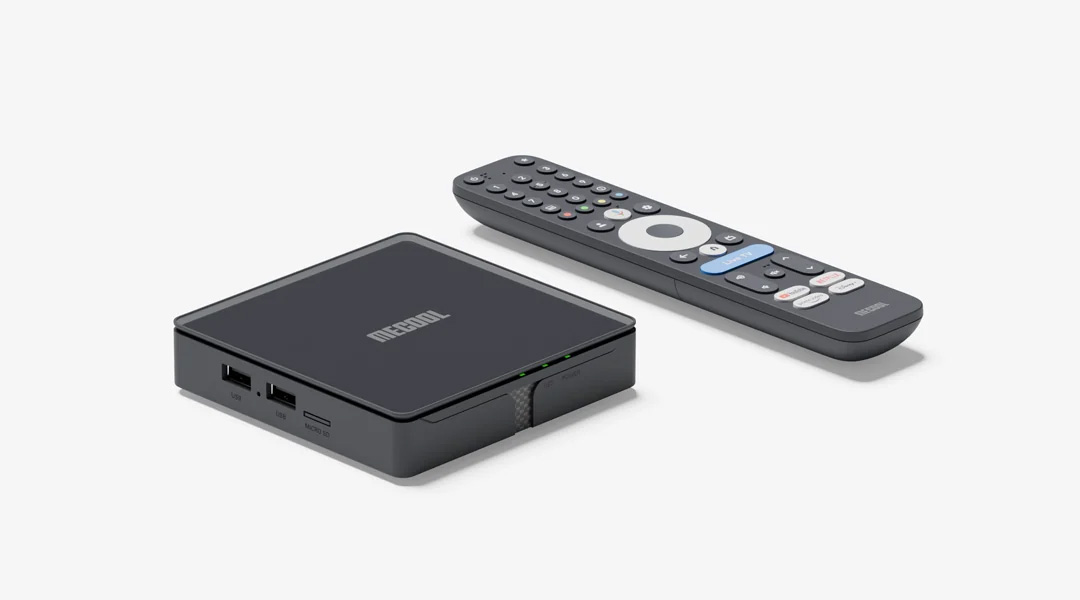
Google dismantles botnet secretly running on 1.3 million Android TV boxes
Google has cut ties with the company behind the botnet campaign.
SRC // Ars Technica Security -
Binance CEO says ‘months-long campaign’ led to $6.3 billion theft as N. Korea denies responsibility
North Korean attackers "combined a range of techniques, including social engineering by fake recruitment interviews," Binance said about the multibillion-dollar crypto heist it discovered in October.
SRC // The Record -
Cursor Distributed Claude Code Extensions With SSH Backdoor Code
Malicious Claude Code extensions targeted Windows and macOS developers through Cursor collecting device details and planting files for persistent remote access.
SRC // HackRead -
Gorbag APT group hits Ukrainian courts and city councils with self-deleting malware
ESET has been tracking a Russia-aligned group it calls Gorbag, which has been breaking into Ukrainian organizations since at least February 2025 using spearphishing attachments and a stealer that erases…
SRC // Help Net Security -
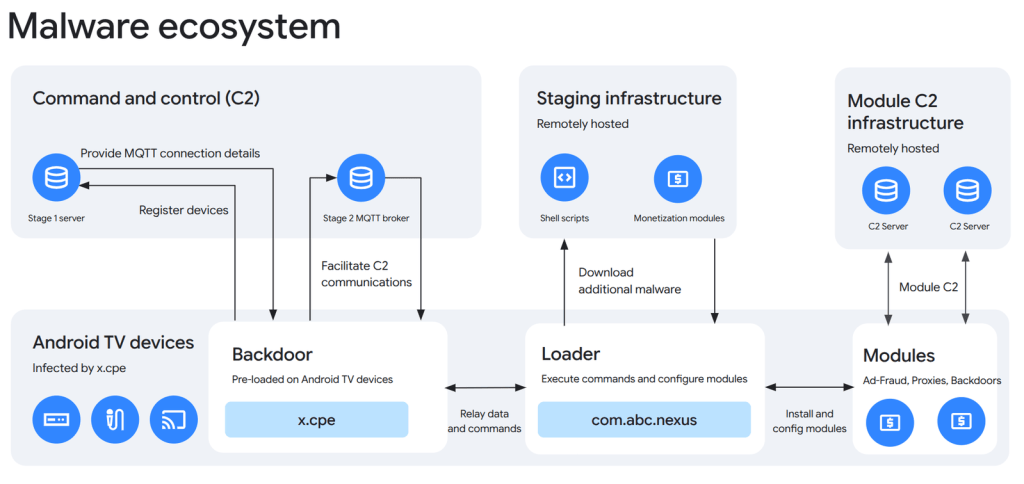
Inside XCPE, the botnet that turned set-top boxes into proxy servers
Google dismantled a 1.3 million-device botnet allegedly built by Android TV box maker Videostrong to enable ad fraud and proxy abuse. Google and its partners dismantled a backdoor called XCPE…
SRC // Security Affairs -
Apple’s spyware notifications reach the Bundestag: what the BSI says to do now
Apple warns German Bundestag lawmakers of mercenary spyware attacks; BSI urges victims to assume compromise. The German government is warning politicians and public figures that they were targeted by government-backed…
SRC // Security Affairs -
Hackers hit UNM hospital, then apologize and offer patients $2,500. In a new statement, they reveal more about the incident.
In more than 20 years of blogging about breaches, DataBreaches has never seen ransomware threat actors offer monetary compensation to patients affected by their attack. We have seen threat actors…
SRC // DataBreaches.net -
HHS’ Office for Civil Rights Settles Ransomware Investigation of Lehigh Valley Health Network
DataBreaches.net previously covered the 2023 Lehigh Valley Health Network breach by AlphV (aka “BlackCat”). The breach garnered a lot of public attention when the threat actors crossed a line by…
SRC // DataBreaches.net -
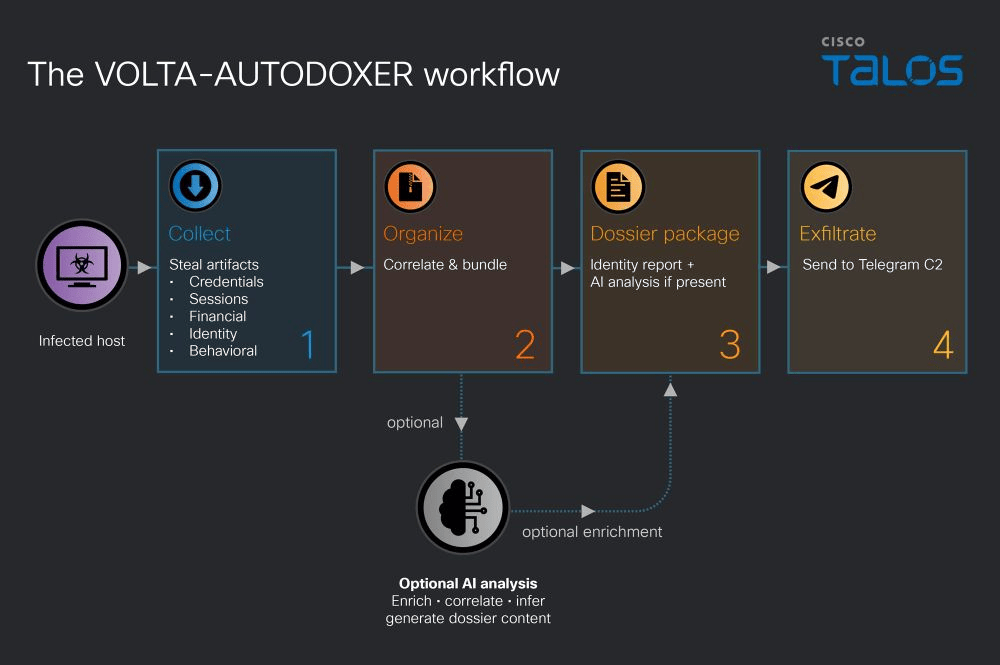
VOLTA, the infostealer that asks an AI which victims are worth the effort
VOLTA is an AI-powered infostealer that steals personal data, then uses LLMs to assess victims’ value and rank targets for attackers. Cisco Talos has analyzed a new Windows infostealer called…
SRC // Security Affairs -
Google disrupts XCPE botnet, bans the company behind it
Google shut down the servers behind XCPE, a backdoor hidden in the firmware of Android TV set-top boxes. Google’s Threat Intelligence Group attributes the operation with high confidence to Videostrong…
SRC // Help Net Security