ARCHIVE
Malware
-
Russia denies intercepting Romanian government emails
Russia has denied accusations that its state-backed hackers targeted a Romanian government institution in an attempt to intercept emails exchanged with NATO and the European Union.
SRC // The Record -
Telegram Widgets Hit by RCE Demos, Malware Warning Days After Launch
Kaspersky suspects exploitation of Telegram’s new widgets to deliver WebRAT, as researchers demo RCE and Pavel Durov disputes the claims. The post Telegram Widgets Hit by RCE Demos, Malware Warning…
SRC // SecurityWeek -
ArcticRAT Android Malware Uses Grok AI to Analyse Stolen Banking Texts
ArcticRAT Android malware can inspect installed apps, sort through SMS alerts and collect financial details, while remote-control features…
SRC // HackRead -
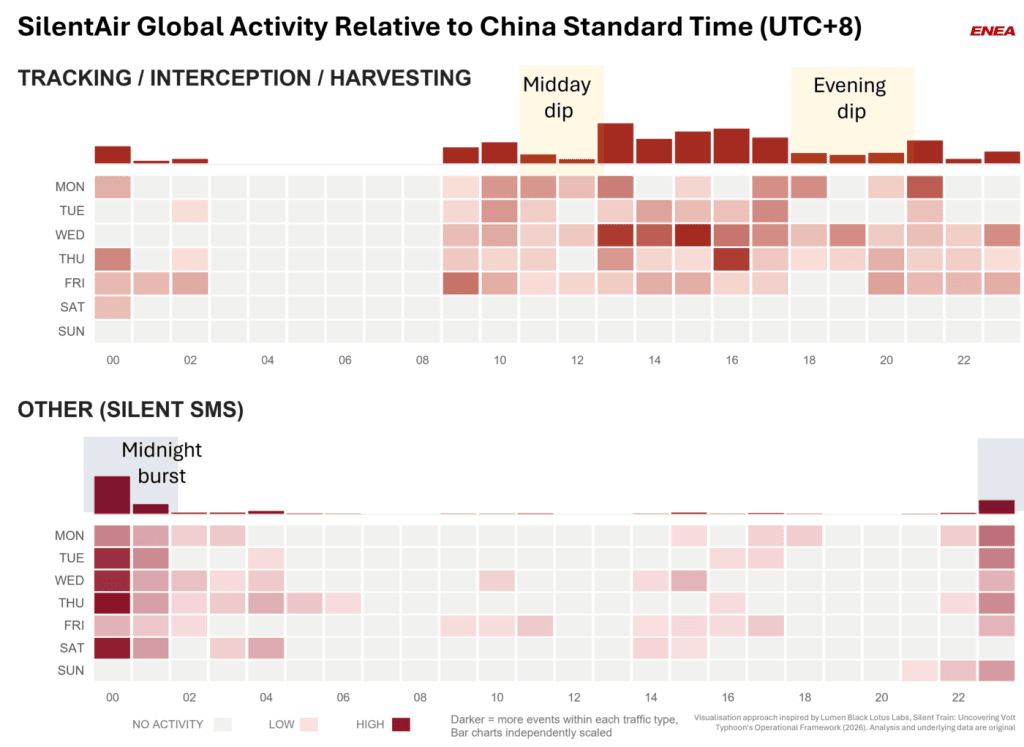
SilentAir and LIMINAL PANDA Target Telecom Networks to Spy on Subscribers
Researchers uncover two threat groups, SilentAir and LIMINAL PANDA, exploiting mobile networks to spy on users and intercept calls and text messages. Telecom security firm Enea published research on two…
SRC // Security Affairs -
A USB worm’s second life: Retadup spreading CoffeeLoader
A new version of CoffeeLoader is spreading through Retadup, an old USB worm whose infrastructure was seized by law enforcement back in 2019.
SRC // Securelist (Kaspersky GReAT) -
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 123
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Exchange for breakfast: Turla’s Cereal tricks are not for…
SRC // Security Affairs -
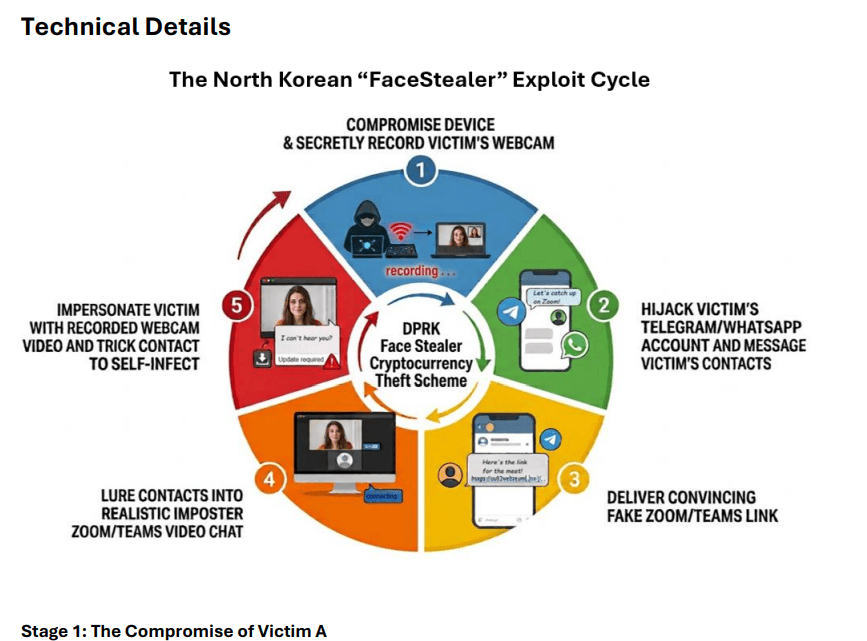
North Korea ‘s Crypto Theft Operations: DOJ Seizes $1.2 Billion and Disrupts Hacker Infrastructure
The DOJ seized over $1.2 billion from North Korea ‘s Binance theft, and says the same hackers are targeting open-source developers The U.S. Department of Justice announced two separate but…
SRC // Security Affairs -
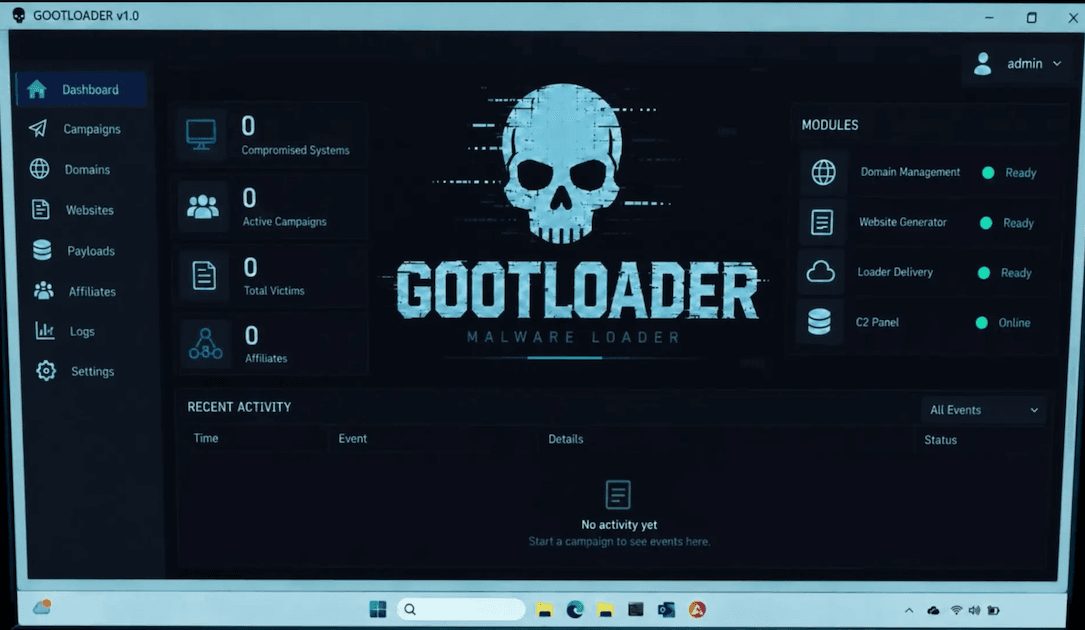
DOJ: Gootloader used in at least 44 ransomware attacks costing $29 million since 2018
In a briefing adjacent to European announcements about an international anti-malware operation, U.S. officials detailed the history and impact of the Gootloader ransomware.
SRC // The Record -
Fake GTA 6 download goes after Steam logins and crypto wallet data
Cynet researchers followed a “GTA 6 EXE file download” link from a Google Colab notebook to a ZIP archive and found a WARDEN Stealer loader inside. The malware takes saved…
SRC // Help Net Security