ARCHIVE
SOCRadar
-
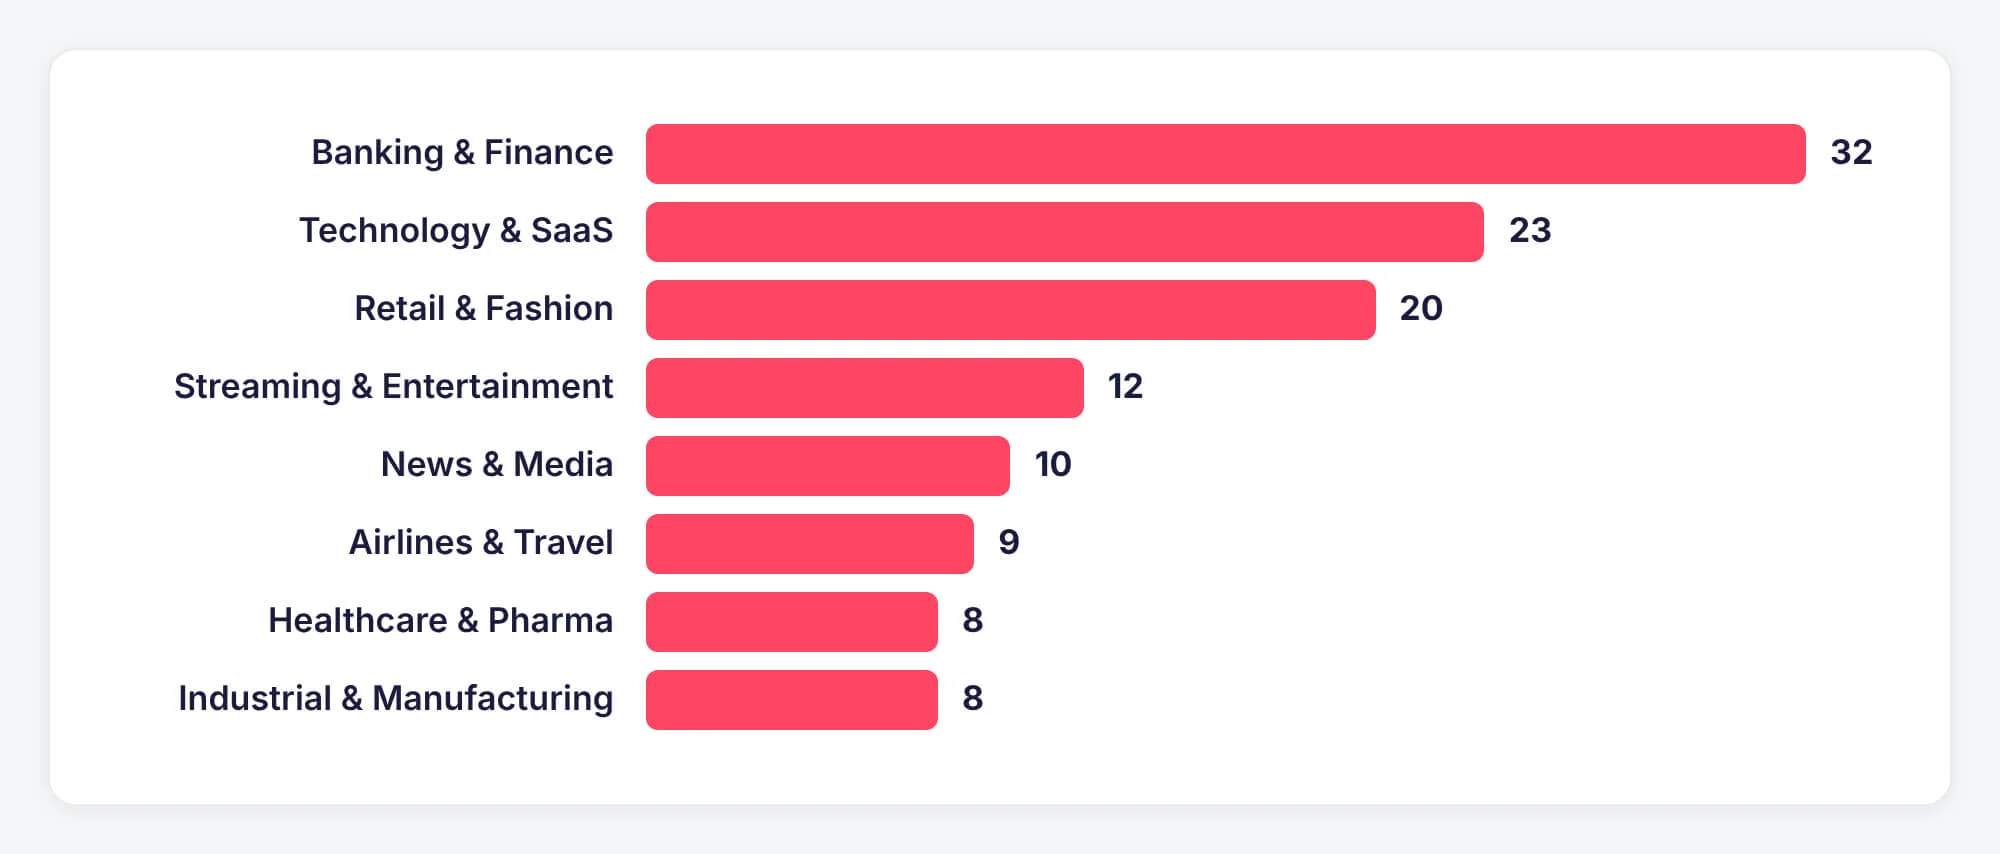
Optimizely Attack Hits Zoom, BBC, CNN With Skimmer, iOS Kits
An Optimizely supply chain attack on November 16, 2026, turned a trusted experimentation script into a malware delivery channel for some of the world’s best-known websites. For nearly 19 hours,…
SRC // SOCRadar -
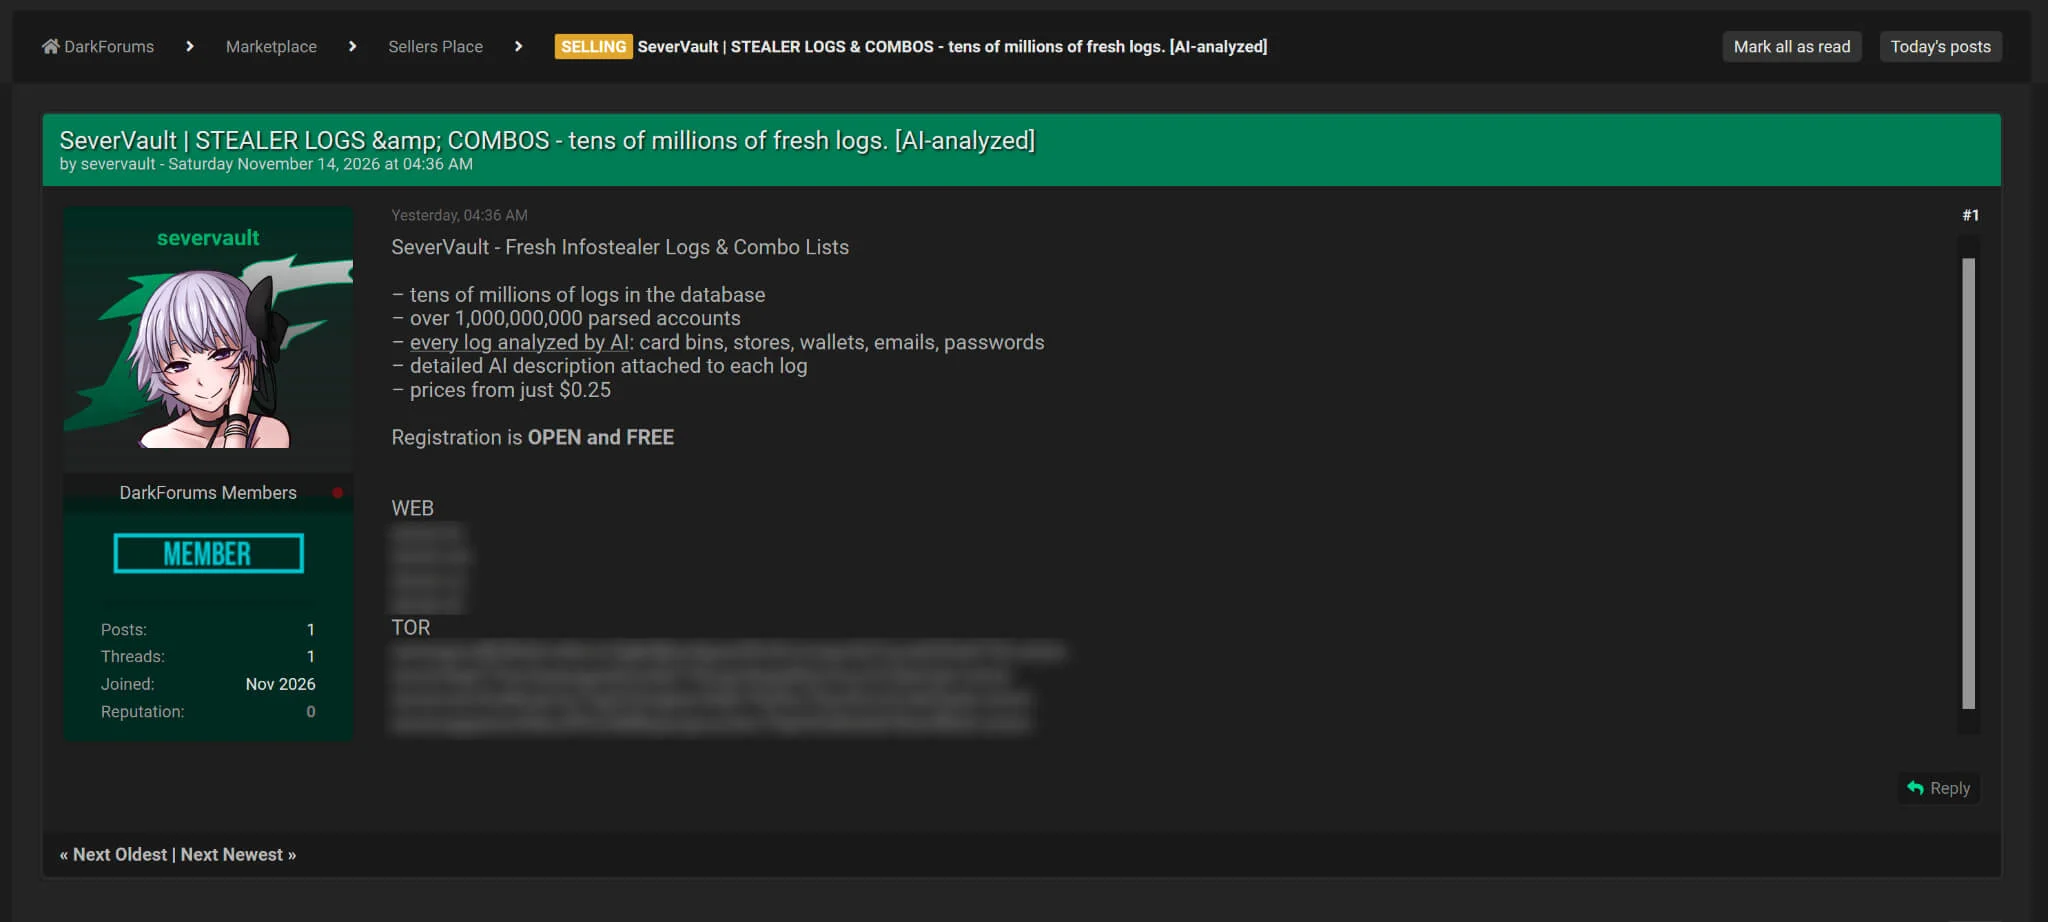
SeverVault: Infostealer Logs Sold as AI Victim Profiles
On November 14, 2026, a seller on DarkForums opened a thread for SeverVault, a shop offering infostealer logs and combo lists. The pitch leans on scale and automation: an inventory…
SRC // SOCRadar -
Unpatched Danfoss AK-SM800A Flaws Allow Takeover
Six unpatched vulnerabilities in the Danfoss AK-SM800A, a system manager that runs refrigeration in supermarkets and cold storage sites, could let a remote attacker take over the controller without logging…
SRC // SOCRadar -
Best DNS Servers for Security and Privacy (2026)
Every connection your devices make starts with a DNS lookup, answered by a resolver that translates domain names into IP addresses and sees every domain you request. Choosing one is…
SRC // SOCRadar -
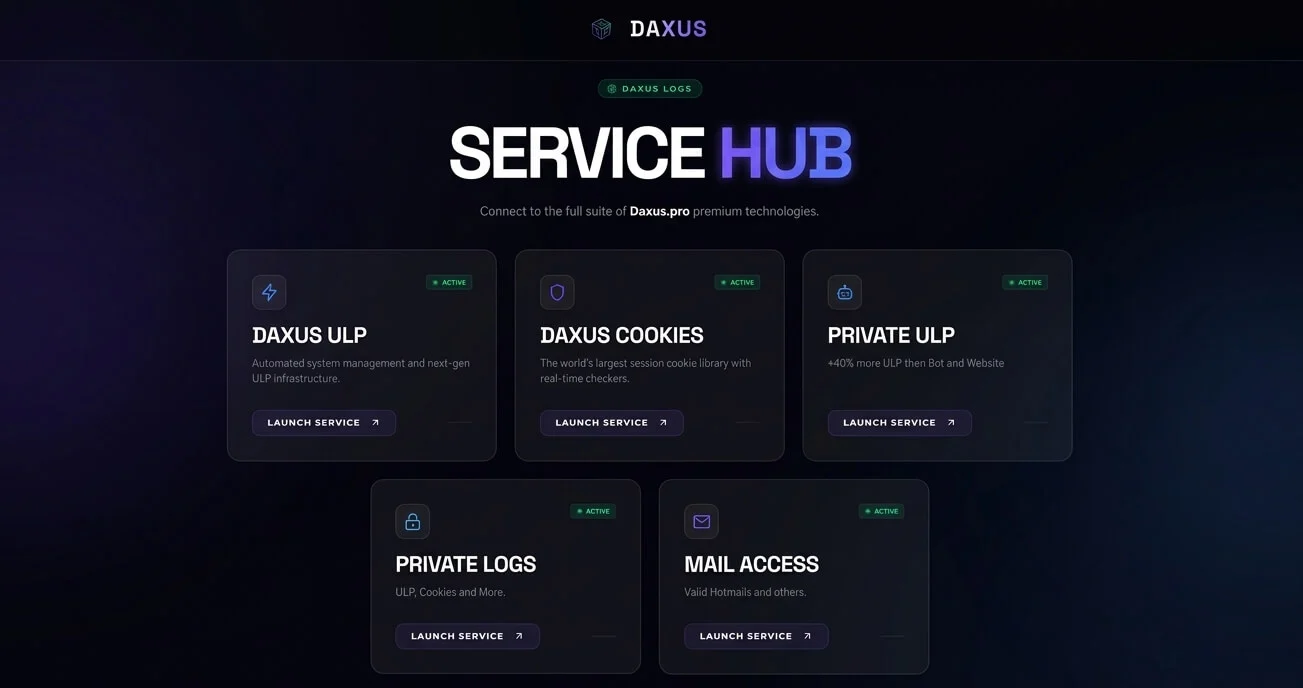
TSMC Leak Claim, Daxus Logs, Kazakhstan Court, Greek Ticketing, and Telegram Data
SOCRadar Dark Web Team identified several underground posts, including an alleged TSMC data leak, a Daxus credential marketplace advertising nearly 3 million records, and a claimed Kazakhstan Supreme Court database…
SRC // SOCRadar -
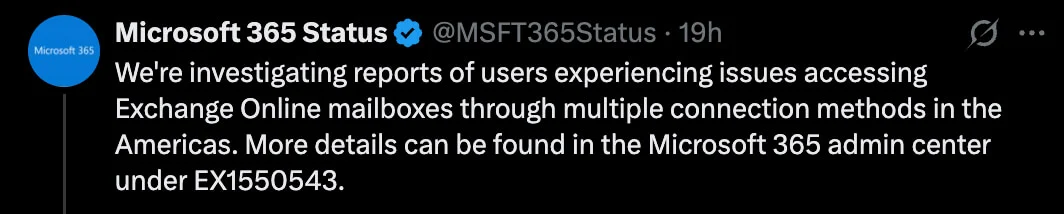
Microsoft Outlook Outage: What You Need to Know
The Microsoft Outlook outage that started on November 12, 2026, began as an Exchange Online mailbox access problem in the…
SRC // SOCRadar -
CVE-2026-119618: Apache HTTP/2 Race Condition RCE
The Apache Software Foundation has released Apache HTTP Server 2.4.71 to fix CVE-2026-119618, a critical race…
SRC // SOCRadar -
4EverAble2Shell At a Glance
4EverAble2Shell is an N-central zero-day exploit chain that lets an unauthenticated remote attacker run commands as root on an on-premises N-able N-central server. An independent researcher released a proof of…
SRC // SOCRadar -
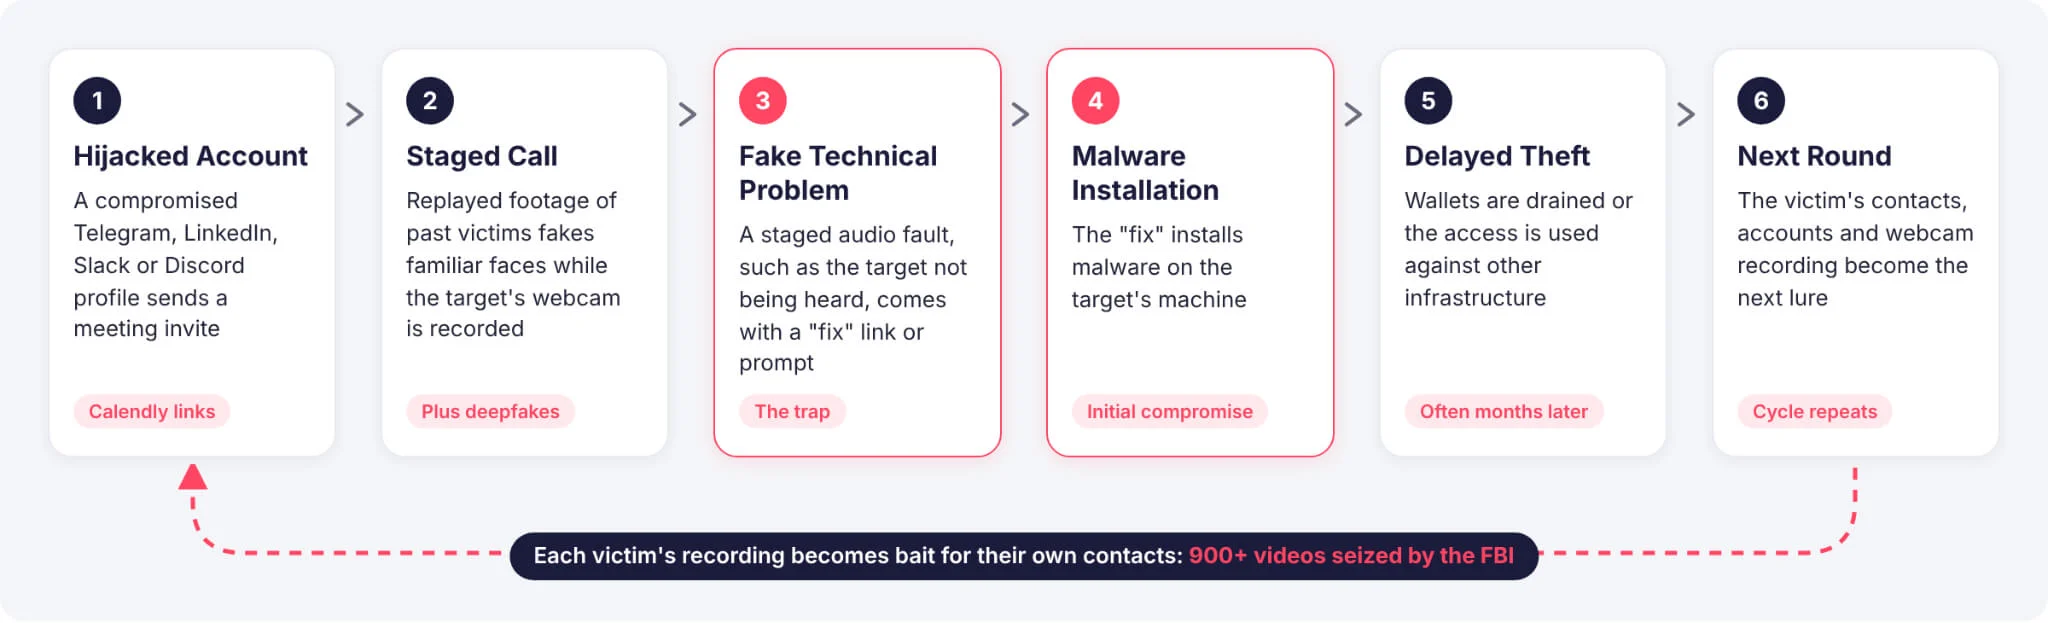
FaceStealer: FBI Disrupts Fake Video Call Crypto Scam
The FBI and the U.S. Department of Justice have disrupted FaceStealer, a North Korean social engineering campaign that used hijacked accounts, replayed webcam footage and fake video calls to steal…
SRC // SOCRadar -
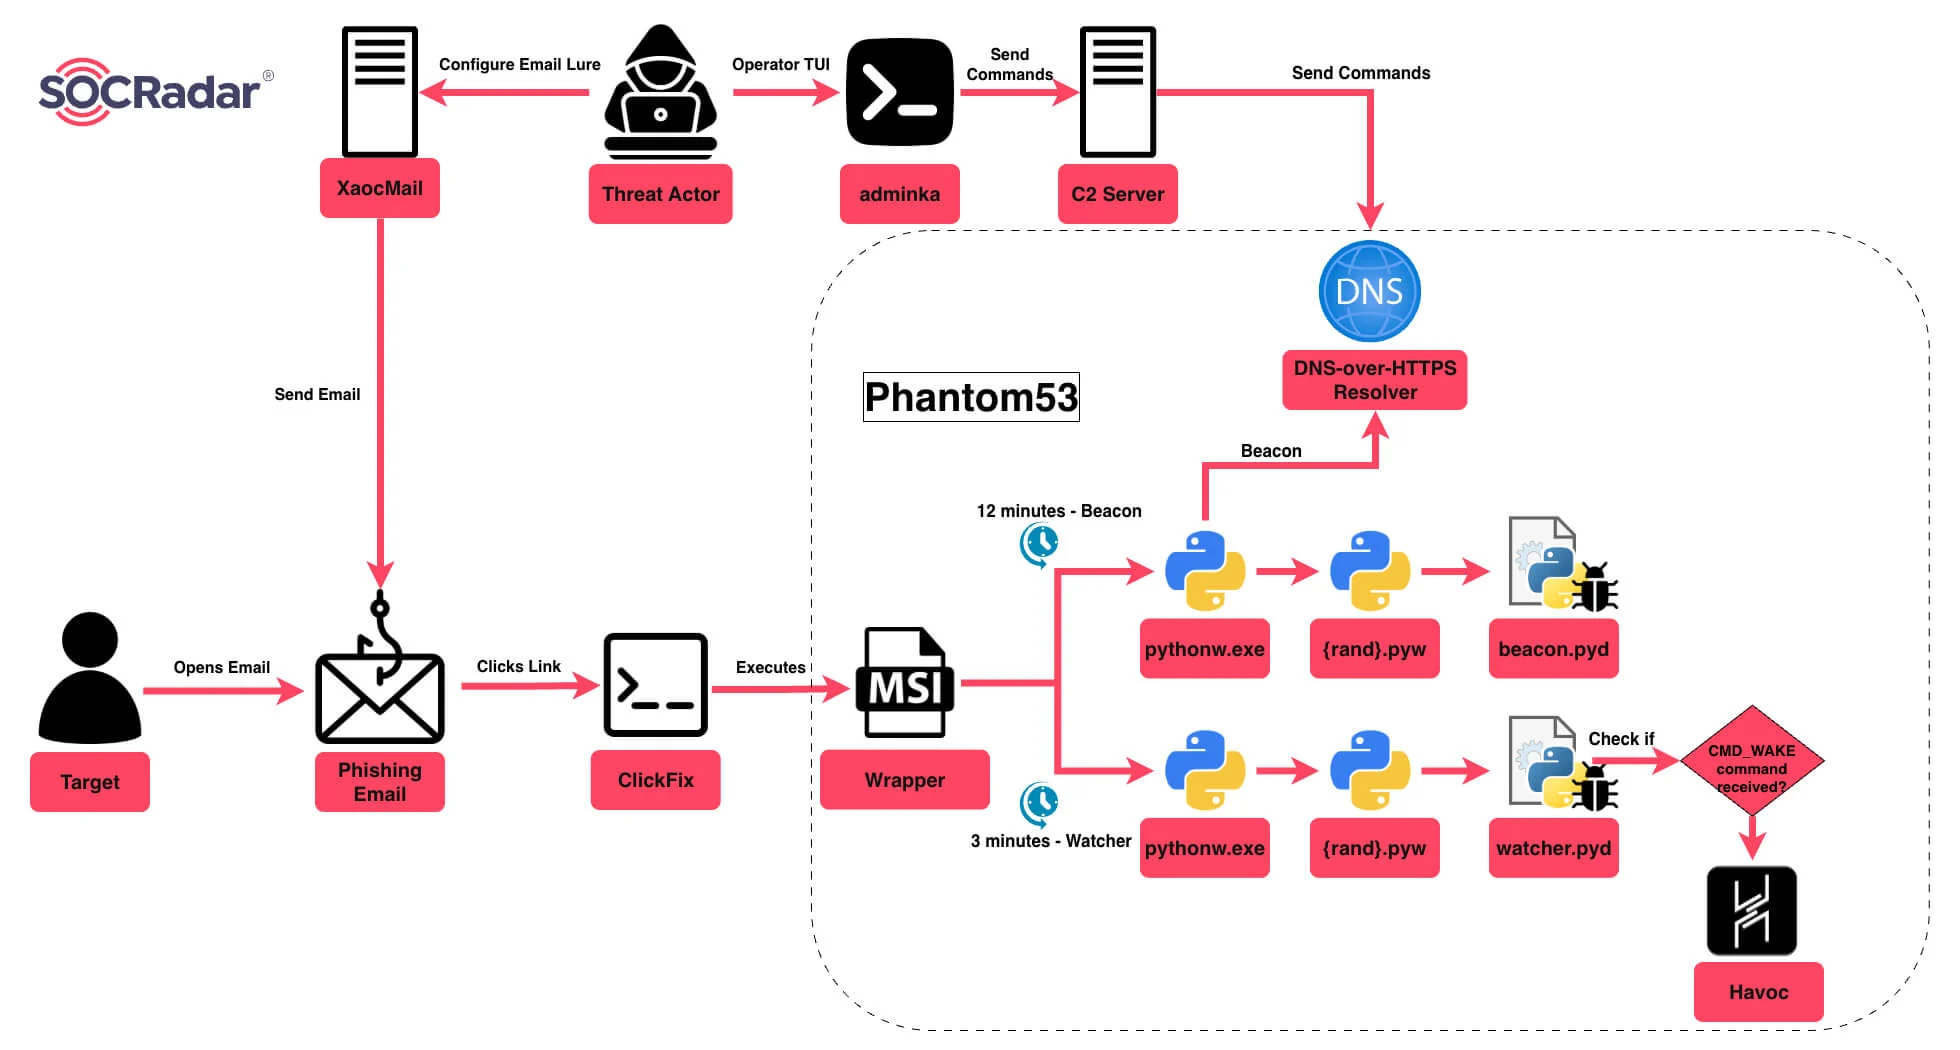
XaocMail ClickFix Campaign Drops Phantom53 and HavoX Across Latin America, Asia, and Europe
Threat actors continue to refine and scale their operations, increasingly integrating artificial intelligence to harden attack infrastructure and accelerate deployment. The SOCRadar Threat Research Unit (STRU) recently identified a multi-stage…
SRC // SOCRadar