JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
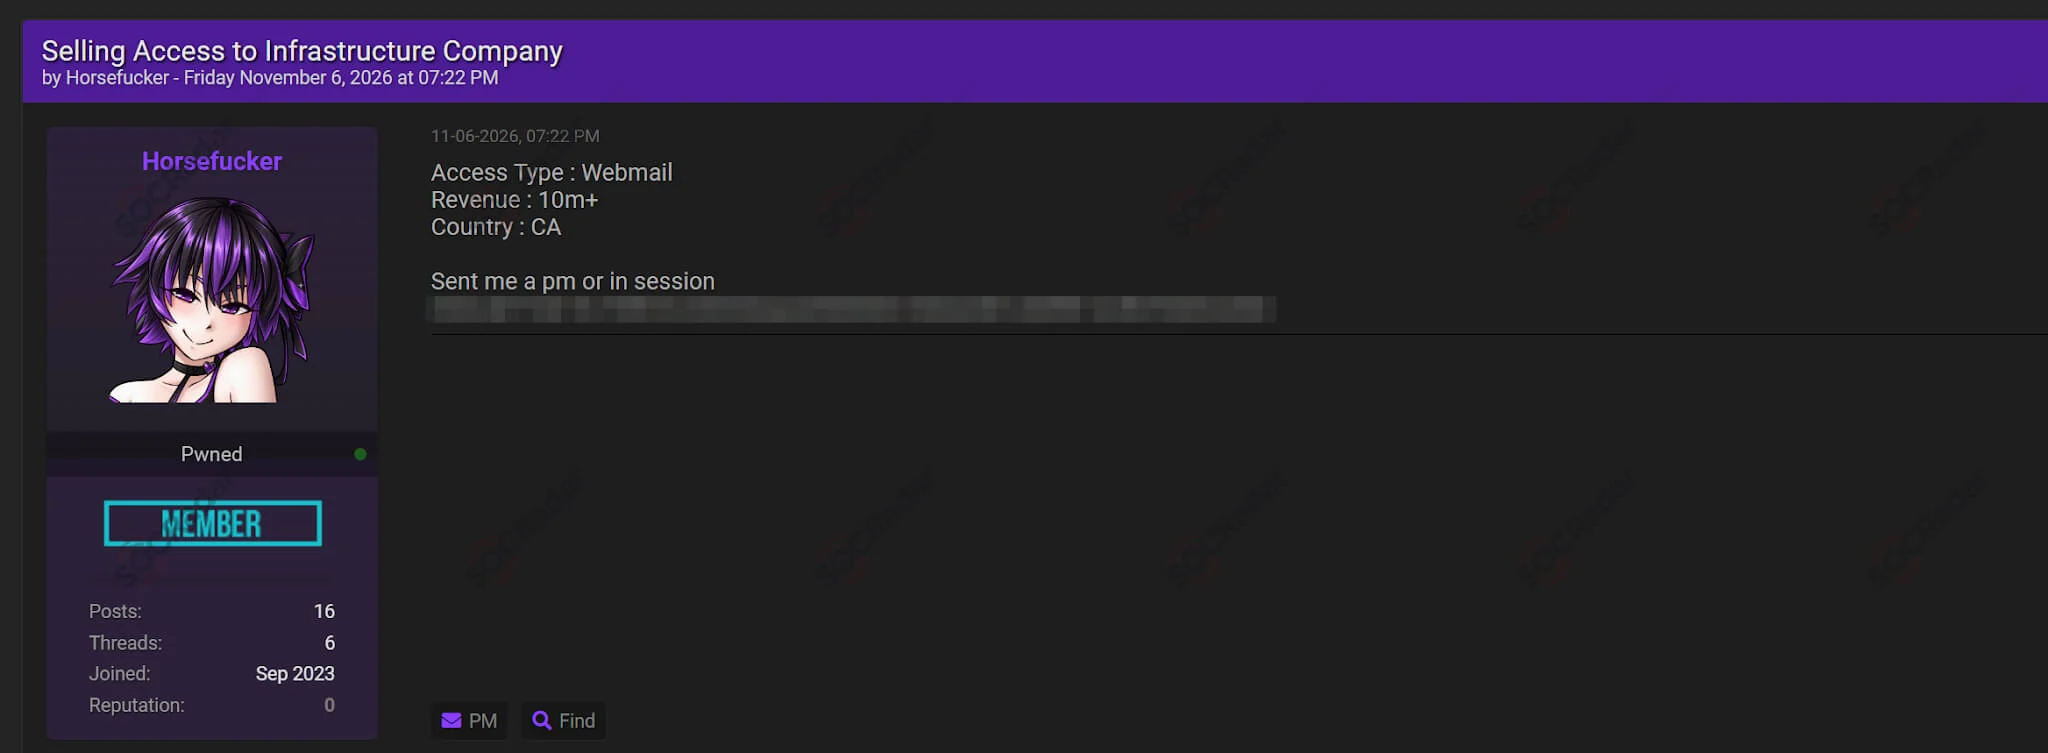
Canadian Webmail Access, US Bank Dump, Peru Leak, Spencer’s Breach, and ZoomInfo Sale
SOCRadar Dark Web Team identified several underground posts, including an alleged webmail access sale targeting a Canadian infrastructure company, a claimed US banking database dump involving sensitive credentials, and an…
SRC // SOCRadar -
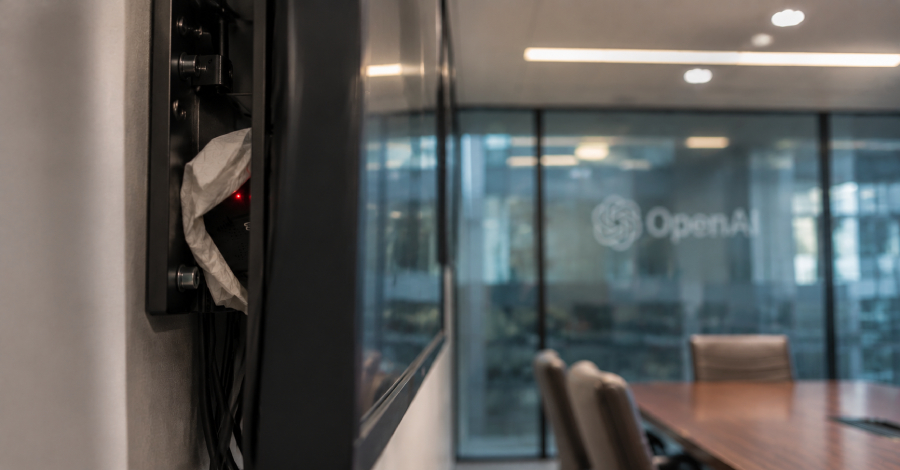
Former OpenAI Engineer Pleads Not Guilty to Planting Covert Device in Executive Meeting Room
The OpenAI engineer who was arrested and charged last month for planting a covert audio recording device in the company’s office has pleaded not guilty. According to reports from Bloomberg…
SRC // The Hacker News -
The BBC has a plan for a Black Sky event, and it runs on FM radio
The BBC plans to use emergency FM radio to keep the UK informed during prolonged blackouts, with a self-sufficient studio ready for 72 hours. If electricity fails across the UK…
SRC // Security Affairs -
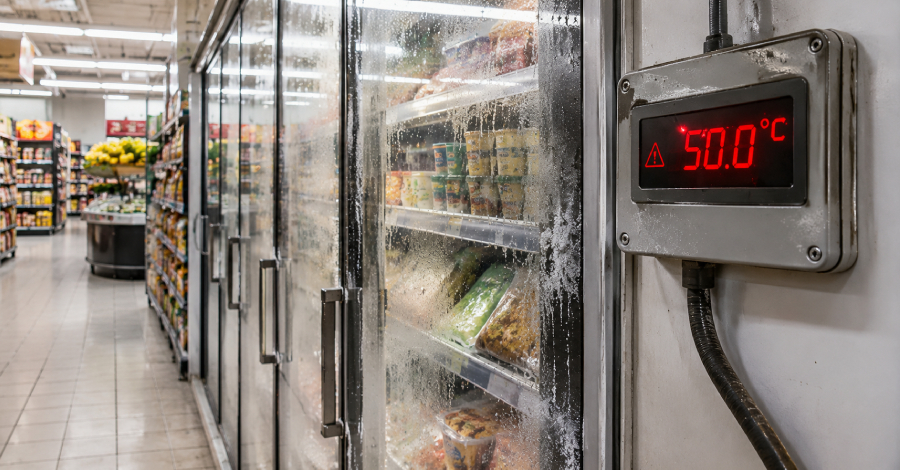
U.S. Agencies Warn Refrigeration Controller Attacks Could Cause Fires and Inventory Losses
U.S. government agencies have warned that threat actors are actively targeting industrial refrigeration and cold-chain monitoring systems globally with an aim to cause service disruptions, fire hazards, and loss of…
SRC // The Hacker News -
CISA Flags SonicWall SonicOS MFA Bypass Flaw Amid Reports of Possible Exploitation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a high-severity vulnerability impacting SonicWall SonicOS to its Known Exploited Vulnerabilities (KEV) catalog, following reports that it said may have…
SRC // The Hacker News -
Wirken: Open-source AI agent gateway
Wirken is an open-source gateway that sits between messaging apps and AI agents. It assumes any agent can be turned against its owner and limits what a compromised one can…
SRC // Help Net Security -
An average of 8 minutes is all hackers need to log in with stolen credentials
Attackers used stolen credentials to log in an average of eight minutes after infection across 27 confirmed infostealer cases, according to a report from Elastic Security Threat Command. Researchers also…
SRC // Help Net Security -
Linus Torvalds sees signs AI-prompted patch flood has peaked
Fixes are arriving faster than new bug reports for one major Linux project
SRC // The Register — Security -
Ransomware claim: Cuomo LLC (anubis)
Inside a law firm data breach.Group: anubisSector: Not FoundDiscovered: 2026-11-09 03:59 UTCAttack date: 2026-11-09 03:58 UTCThis entry reflects a claim published by an extortion group and collected by a public…