JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Ransomware claim: niclibya.com (krybit)
National Investment Holding Company is a Libyan joint-stock holding company established in 1986, headquartered in Tripo…Group: krybitCountry: LYSector: OtherVictim website: niclibya.comDiscovered: 2026-11-09 09:05 UTCAttack date: 2026-11-09 09:05 UTCThis entry reflects…
-
Ransomware claim: sumoteks.com (krybit)
Sumoteks Tekstil Ürünleri Üretim ve Pazarlama Limited Şirketi is a Turkish manufacturer of knitwear. It was founded …Group: krybitSector: TechnologyVictim website: sumoteks.comDiscovered: 2026-11-09 09:05 UTCAttack date: 2026-11-09 09:04 UTCThis entry…
-
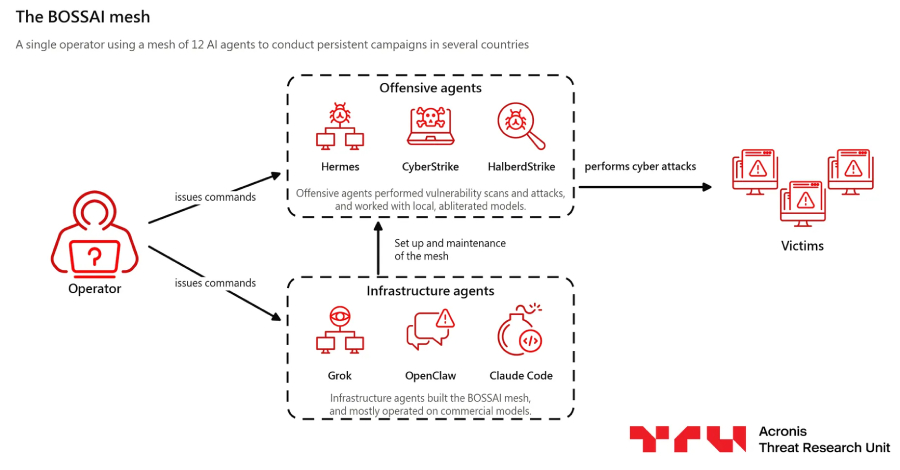
Taiwan-Based Hacker Used BOSSAI AI Agents to Steal Taipei Emergency Dispatch Records
A single attacker using AI agents pulled emergency dispatch records covering seven Taipei districts, researchers at Acronis’s Threat Research Unit said last week. The agents also found a Taipei fire…
SRC // The Hacker News -
Google DeepMind’s AI Agents Make 1024-Bit RSA Keys Cheaper to Attack
Working with cryptographers, DeepMind’s AI agents cut the cost of forging RSA-1024 signatures and found a cheaper way to factor keys. The post Google DeepMind’s AI Agents Make 1024-Bit RSA…
SRC // SecurityWeek -
Ransomware claim: AUDIT ENTITY: roycegroup (audit team)
AUDIT ID: 57FD7689754A6F21 / DISCOVERY DATE: 2026-10-31Group: audit teamDiscovered: 2026-11-09 08:25 UTCThis entry reflects a claim published by an extortion group and collected by a public tracker. It has not…
SRC // RansomLook — Recent Posts -
Ransomware claim: AUDIT ENTITY: hnopvm.org (audit team)
AUDIT ID: 2AE3CE243E823521 / DISCOVERY DATE: 2026-10-31Group: audit teamDiscovered: 2026-11-09 08:25 UTCThis entry reflects a claim published by an extortion group and collected by a public tracker. It has not…
SRC // RansomLook — Recent Posts -
Ransomware claim: AUDIT ENTITY: jltrust.com (audit team)
AUDIT ID: 1E2CF5D71F581238 / DISCOVERY DATE: 2026-10-31Group: audit teamDiscovered: 2026-11-09 08:26 UTCThis entry reflects a claim published by an extortion group and collected by a public tracker. It has not…
SRC // RansomLook — Recent Posts -
Ransomware claim: AUDIT ENTITY: Pelican ICT (audit team)
AUDIT ID: 17BACA24A3932895 / DISCOVERY DATE: 2026-10-31Group: audit teamDiscovered: 2026-11-09 08:26 UTCThis entry reflects a claim published by an extortion group and collected by a public tracker. It has not…
SRC // RansomLook — Recent Posts -
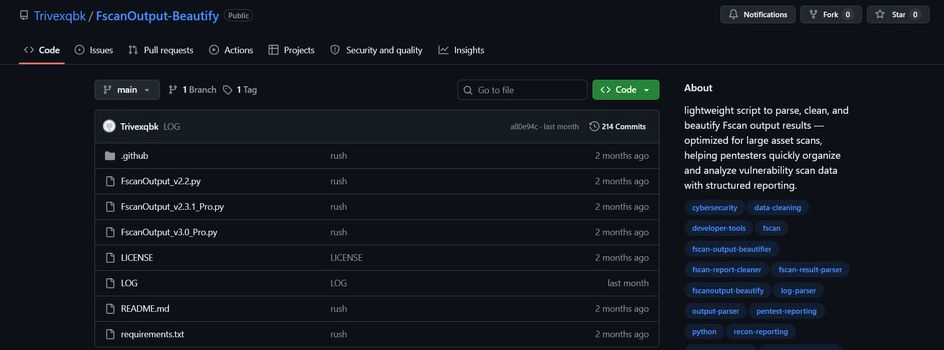
Fake GitHub Security Tools Infect Over 2,000 PCs With Malware
Fake GitHub security tools are spreading malware that disables defenses, steals sensitive data and infects over 2,000 PCs. Cybersecurity firm Doctor Web has found malware hidden in GitHub projects that…
SRC // Security Affairs -
A week in security (November 2 – November 8)
A list of topics we covered in the week of November 2 to November 8 of 2026
SRC // Malwarebytes Labs