ARCHIVE
Hacking
-
$6.3 Billion Stolen from Binance in Attack Attributed to North Korea
Binance links a $6.3 billion crypto theft to a compromised DevOps laptop, with North Korean hackers blamed by blockchain analysts. Binance was investigating suspicious transfers that early estimates put at…
SRC // Security Affairs -
How to prioritize remediation after a pentest: a practitioner workflow
A practical pentest workflow combines CVSS, EPSS and business impact to validate findings, prioritize fixes and document remediation decisions. Remediation prioritization after a pentest is the process of ranking and…
SRC // Security Affairs -
Hacker leaks data on more than 40,000 Homeland Security employees
A hacker leaks personal data on more than 40,000 DHS employees, including CBP, ICE and CISA staff, after an undisclosed breach. Personal details of thousands of U.S. Department of Homeland…
SRC // Security Affairs -
Binance Probes Suspected $5.8 Billion Crypto Hack, $3 Billion Frozen
Binance investigates a $5.8 billion crypto theft, with $3 billion in assets frozen. The exchange says user funds are safe as investigators trace funds.
SRC // HackRead -

Binance Investigates Suspicious Crypto Transfers Worth Up to $5.8 Billion
Binance probes suspicious crypto transfers worth up to $5.8 billion as Tether and Circle freeze $1.79 billion in stablecoins linked to the activity. Binance is investigating a potential security incident…
SRC // Security Affairs -
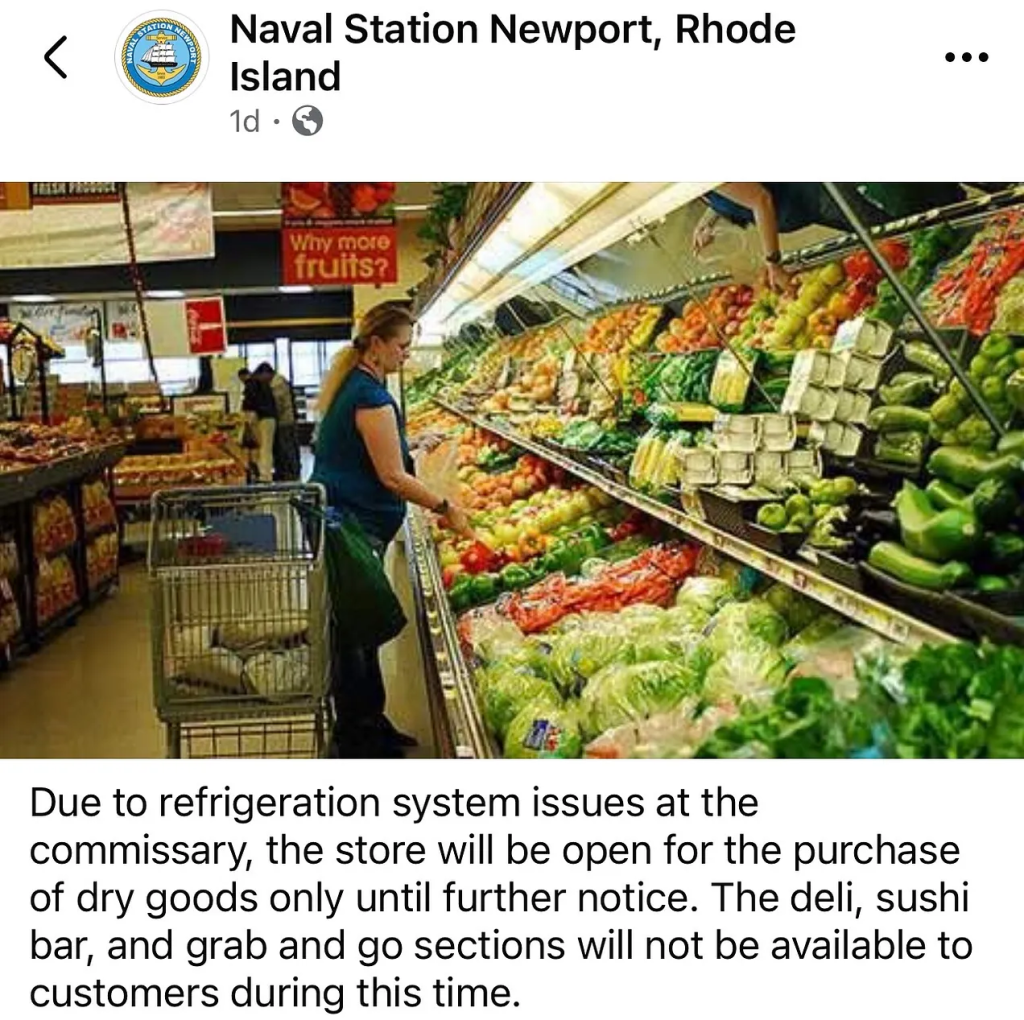
US Probes Suspected Hack Behind Military Base Freezer Failures
The Pentagon treats August freezer failures at US military bases as a suspected hack and is working with French investigators after a supermarket attack. The Pentagon is investigating freezer failures…
SRC // Security Affairs -
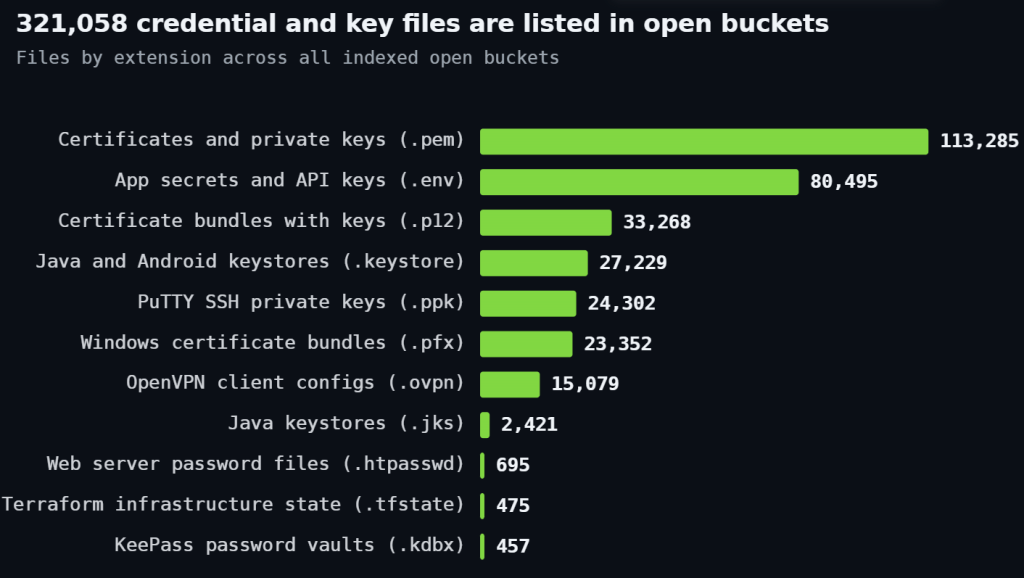
484,142 Exposed Cloud Buckets Contain 18 Billion Files
42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups. The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026,…
SRC // Security Affairs -
U.S. CISA adds Linux Kernel and Broadcom VMWare ESX flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel and Broadcom VMWare ESX flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Linux Kernel and…
SRC // Security Affairs -
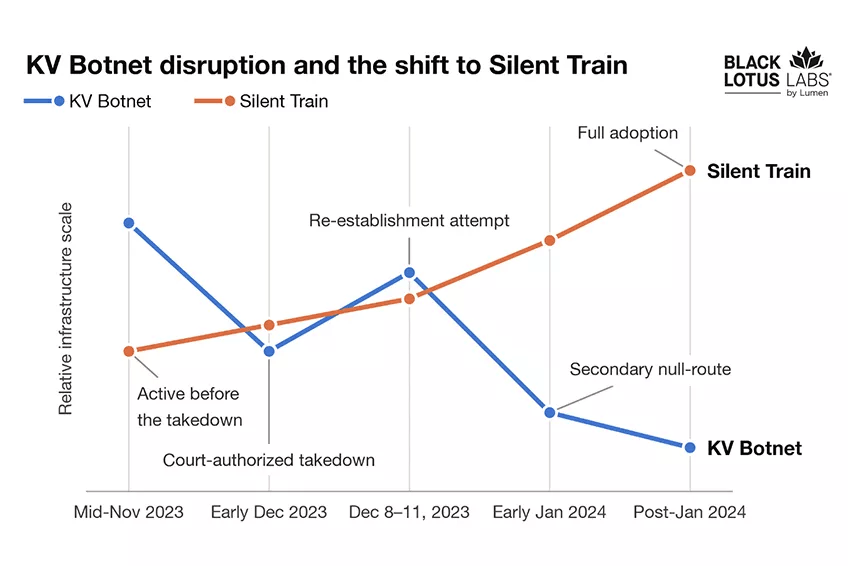
Volt Typhoon Used Silent Train to Hide Zero-Day Attacks
Volt Typhoon used disposable relay chains to hide zero-day attacks on critical systems. Lumen linked Silent Train to at least four zero-days. Lumen’s Black Lotus Labs has spent three years…
SRC // Security Affairs -
Bias in Qwen3-Coder Model
Interesting research: TL;DR: Chinese AI models now sit inside Western products, and some carry geopolitical triggers: tell the model who the code is for, and the security of what it…
SRC // Schneier on Security