JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
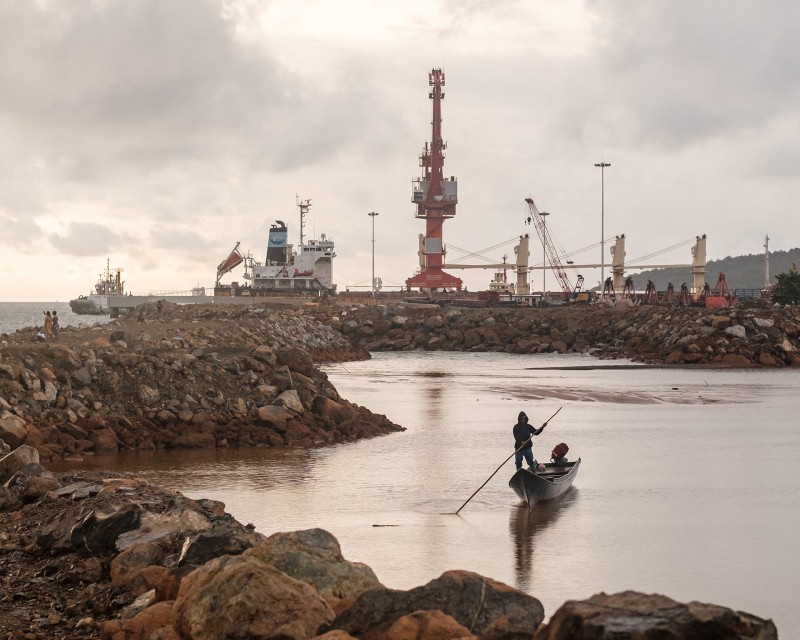
From Flights to ‘Incentives,’ Indonesian Nickel Giant Harita Approved Payments for Local Politicians and Leaders
Leaked records show the major Indonesian nickel miner Harita Group approved hundreds of thousands of dollars in “incentives” for community leaders, flights for politicians, and financial support for military projects…
SRC // OCCRP -
Certification authority eMudhra defends its laughably weak private keys
Says it passed audits and made just a minor mystery error
SRC // The Register — Security -
How APT41 revived the BlackLotus bootkit to attack diplomatic organizations in Central Asia
Kaspersky GReAT experts discovered a new UEFI bootkit, BlackX. It exploits the Baton Drop vulnerability (CVE-2022-21894) and is similar to the BlackLotus bootkit.
SRC // Securelist (Kaspersky GReAT) -
ZDI-26-786: NoMachine nxwebrunner Heap-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of NoMachine. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of…
-
ZDI-26-787: NVIDIA Megatron Bridge YAML File Parsing Code Injection Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of NVIDIA Megatron Bridge. User interaction is required to exploit this vulnerability in that the target must visit…
-
ZDI-26-788: Cisco Snort OLE VBA Decompression Stack-based Buffer Overflow Remote Code Execution Vulnerability
This vulnerability allows remote attackers to execute arbitrary code on affected installations of Cisco Snort. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating…
-
ZDI-26-789: OpenSSL CMP Use of Externally-Controlled Format String Information Disclosure Vulnerability
This vulnerability allows remote attackers to disclose sensitive information on affected installations of OpenSSL. Authentication is not required to exploit this vulnerability. The ZDI has assigned a CVSS rating of…
-
ZDI-26-790: OpenSSL CMS AuthEnvelopedData Improper Validation of Integrity Check Value Vulnerability
This vulnerability allows network-adjacent attackers to tamper with CMS AuthEnvelopedData messages on affected installations of OpenSSL. An attacker must first obtain the ability to modify CMS AuthEnvelopedData messages in order…
-
UAE Transitions 50% of Government Services to Agentic AI
The United Arab Emirates says it’s creating a foundation of security and safety as it transforms its public service footprint.
SRC // Dark Reading -
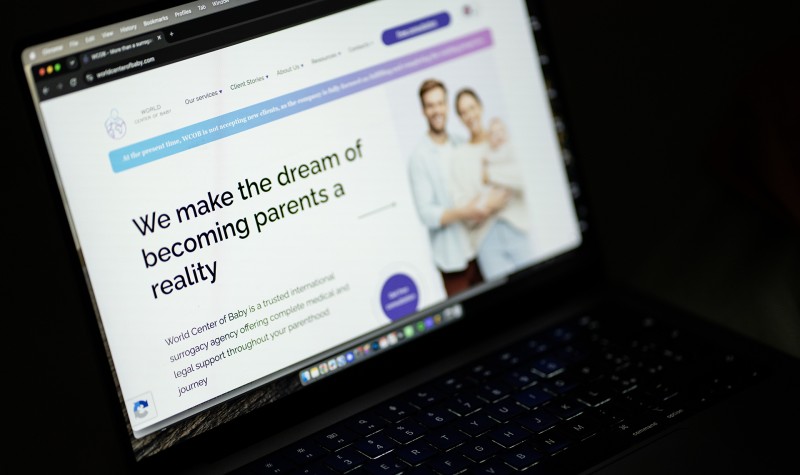
Collapsed Surrogacy Agency Loses U.S. Civil Case After Court No-Show
World Center of Baby plunged surrogates and prospective parents into chaos when it announced it was filing for bankruptcy. Now the agency’s U.S. corporate entity must pay out tens of…
SRC // OCCRP