JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilities
But cyberattacks aren’t directly to blame, Trump administration officials said. The post Consensus mounts that tech outages were fueled by patching of AI-discovered vulnerabilities appeared first on CyberScoop.
SRC // CyberScoop -
Coinbase blocks $4.7 million in transfers to Elon Musk deepfake scam
Coinbase says it blocked $4.7 million in cryptocurrency transfers to scammers promoting a fake giveaway using an AI-generated deepfake of Elon Musk during a Tesla livestream that attracted more than…
SRC // BleepingComputer -
GHSA-82w8-65qw-gch6: ALTCHA PHP: verifySolution bypasses HMAC signature check when challenge signature is absent
Severity: HIGHCVE: CVE-2026-71481Ecosystems: composerPackages: altcha-org/altchaIn altcha-org/altcha v2, the verifySolution method skips HMAC signature verification when the signature field is absent from the challenge payload, even when hmacSignatureSecret is configured. An…
SRC // GitHub Security Advisories -
Strike Graph Launches Integration AI to Automate Continuous Compliance Evidence Using Any Existing Tool
New agentic AI solution leverages APIs to collect compliance evidence from systems and applies it to over 30 frameworks with no duplicate work.
SRC // Dark Reading -
GHSA-7jvc-9xq8-frff: Outstatic: Authenticated GitHub REST proxy can send OAuth token to non-GitHub origins
Severity: MEDIUMCVE: CVE-2026-71425Ecosystems: npmPackages: outstatic### Impact Outstatic’s authenticated GitHub REST proxy accepted an unvalidated endpoint parameter and constructed an upstream GitHub API URL by string concatenation while attaching the authenticated…
SRC // GitHub Security Advisories -
GHSA-ff87-73jp-f3v4: Atomic Server: Unauthenticated full-response SSRF in Atomic-Server /bookmark endpoint
Severity: HIGHCVE: CVE-2026-69158Ecosystems: rustPackages: atomic-server## Summary Atomic-Server exposes a `GET /bookmark` endpoint that fetches an attacker-supplied URL server-side, parses the response, and reflects the fetched content back to the caller.…
SRC // GitHub Security Advisories -
GHSA-pfwx-xjp4-qxcj: Atomic Server: Unauthenticated `/setup` invite grants write access to the entire Drive
Severity: CRITICALCVE: CVE-2026-69157Ecosystems: rustPackages: atomic-server## Summary atomic-server provisions a well-known invite at `{server}/setup` with `write = true`, `target` = the Drive root, and `usagesLeft = 1`. Invite redemption **ignores the…
SRC // GitHub Security Advisories -
GHSA-8vc4-8hjq-988p: Atomic Server: Arbitrary file read via user-controlled `internalId` in the `/download` handler (leaks root agent private key)
Severity: HIGHCVE: CVE-2026-69156Ecosystems: rustPackages: atomic-server## Summary The Commit apply path enforces **no allowlist of writable properties**, so any authenticated Agent can set the `internalId` string (datatype `string`, no character validation)…
SRC // GitHub Security Advisories -
GHSA-x277-3wcg-g9r2: Atomic Server: Stored XSS via uploaded files served inline (same-origin) on `/download` → account takeover
Severity: HIGHCVE: CVE-2026-69155Ecosystems: rustPackages: atomic-server## Summary Files uploaded via `POST /upload` are served back by `GET /download/{path}` using `actix_files::NamedFile`. For `text/html` and `image/svg+xml`, actix-files (0.6.6) sets `Content-Disposition: inline`, so the…
SRC // GitHub Security Advisories -
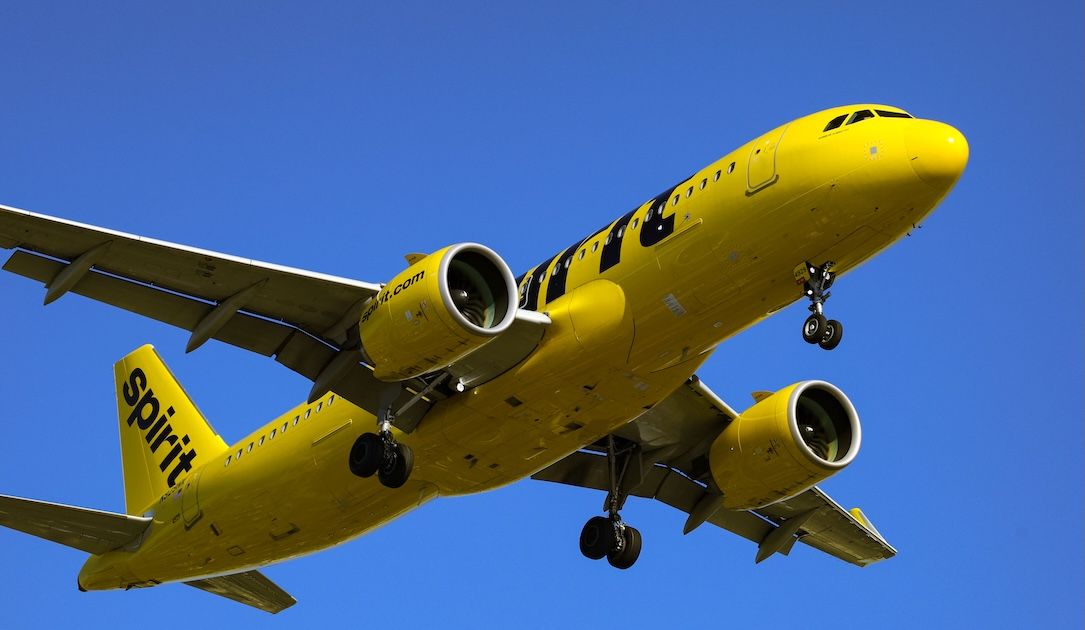
Judge signs off on sale of Spirit Airlines’ data to Google
Google can take possession of defunct Spirit Airlines’ data for $10 million, a federal bankruptcy judge has ruled. The tech giant agreed to protections as it plans to use the…
SRC // The Record