JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Ransomware claim: Comercial en Fletes México, S.A. de C.V. (Eclipse)
Comercial en Fletes México, S.A. de C.V. (widely recognized by its initials CFM) is a highly established regional leader in the federal freight transport and large-scale logistics sector. Headquartered in…
-
Multiple ERP Access Claims Span 13 Organizations Across Nine Countries After Alleged 0-Day Exploitation
An actor using the handle “Lenken” claims to have access to multiple ERP environments across organizations in South Africa, the United States, Iraq, India, Austria, Saudi Arabia, the United Arab…
SRC // Dark Web Informer -
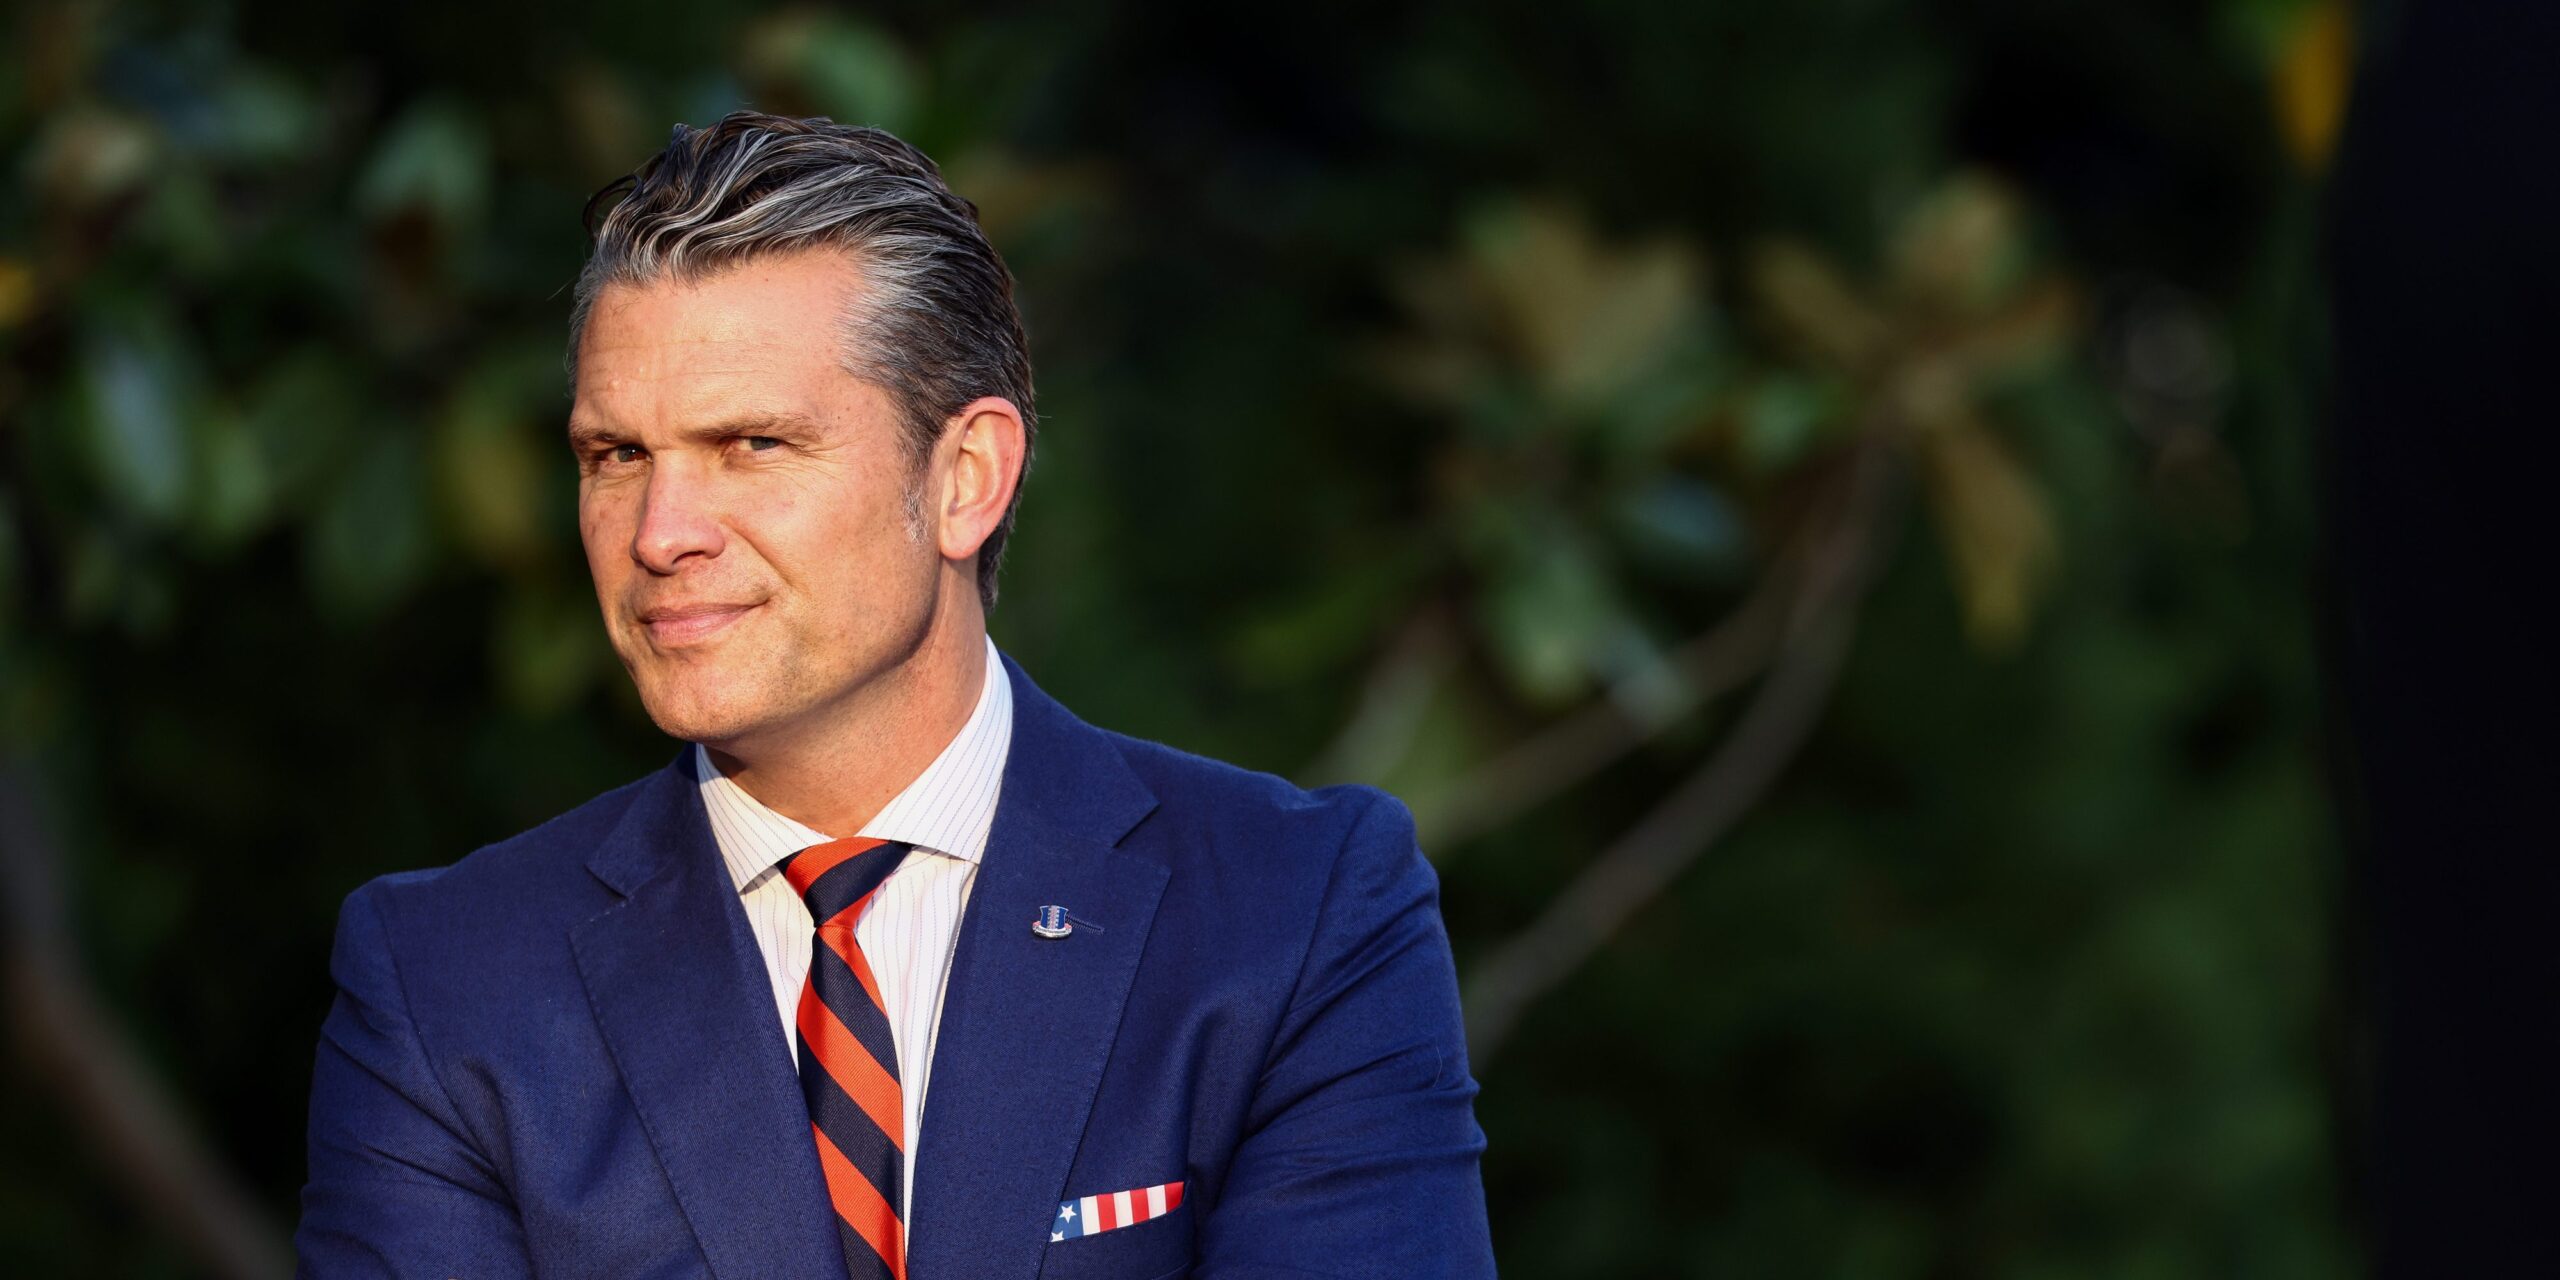
Pentagon Officials Float Names of Hegseth’s Replacement
As Pete Hegseth fights for his job after the midterm Republican wipeout, Ron DeSantis and Mike Waltz are just some of the names being mentioned. The post Pentagon Officials Float…
SRC // The Intercept -
GHSA-47w9-6r3f-938g: LXD has restricted project bypass leading to arbitrary command execution
Severity: CRITICALEcosystems: goPackages: github.com/canonical/lxdReported from https://github.com/lxc/incus/security/advisories/GHSA-48q5-w887-33wv ### Summary Instance snapshots ignore the `restricted.containers.lowlevel=block` setting; allowing for arbitrary command execution on the Incus server by abusing lowlevel hooks such as `raw.lxc`…
SRC // GitHub Security Advisories -
GHSA-7mr3-28h5-m5vx: LXD has project restriction bypass for custom volume copy across projects
Severity: HIGHEcosystems: goPackages: github.com/canonical/lxdReported from https://github.com/lxc/incus/security/advisories/GHSA-64f3-v33m-w89f ### Summary Missing authorization checks exist for custom volume copying where an attacker knowing the name of a project that they don't have access…
SRC // GitHub Security Advisories -
GHSA-qx75-2p3r-pwm5: LXD has project restriction bypass in instance copy across projects
Severity: HIGHEcosystems: goPackages: github.com/canonical/lxdReported from https://github.com/lxc/incus/security/advisories/GHSA-c9f5-j9c3-mhrg ### Summary Missing authorization checks exist for instance copying where an attacker knowing the name of a project that they don't have access to…
SRC // GitHub Security Advisories -
GHSA-r4hm-p9f9-fj9v: GeoNode has Stored XSS in Documents metadata abstract field
Severity: MEDIUMCVE: CVE-2026-55649Ecosystems: pipPackages: GeoNodeThe abstract metadata of documents is not sanitised. It’s possible to store arbitrary HTML (and JS) that will be executed when visiting the page.
SRC // GitHub Security Advisories -
GHSA-fqpv-mq26-pr4j: GeoNode has Unrestricted File Upload
Severity: MEDIUMCVE: CVE-2026-46429Ecosystems: pipPackages: GeoNodeThe upload service validation can be circumvented with specially crafted requests, allowing for the storage and serving of malicious files.
SRC // GitHub Security Advisories -
GHSA-9fpx-fr6j-2vh6: GeoNode has OS command injection via uploaded file layer name
Severity: HIGHCVE: CVE-2026-33050Ecosystems: pipPackages: GeoNodeArbitrary OS commands can be executed on the GeoNode by uploading a vector file with a crafted layer name.
SRC // GitHub Security Advisories -
GHSA-j93m-3j9p-m5m8: LXD has CreateCustomVolumeFromBackup nil-pointer dereference on volumes[0].snapshots[*].expires_at
Severity: MEDIUMCVE: CVE-2026-9639Ecosystems: goPackages: github.com/canonical/lxd## Summary (sibling-field variant of CVE-2026-40197 fix 05bc272) `(*lxdBackend).CreateCustomVolumeFromBackup` in [`lxd/storage/backend_lxd.go`](https://github.com/canonical/lxd/blob/05bc272/lxd/storage/backend_lxd.go) contains an unguarded `*time.Time` dereference on the `ExpiresAt` field of every volume-snapshot entry in an…
SRC // GitHub Security Advisories