JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
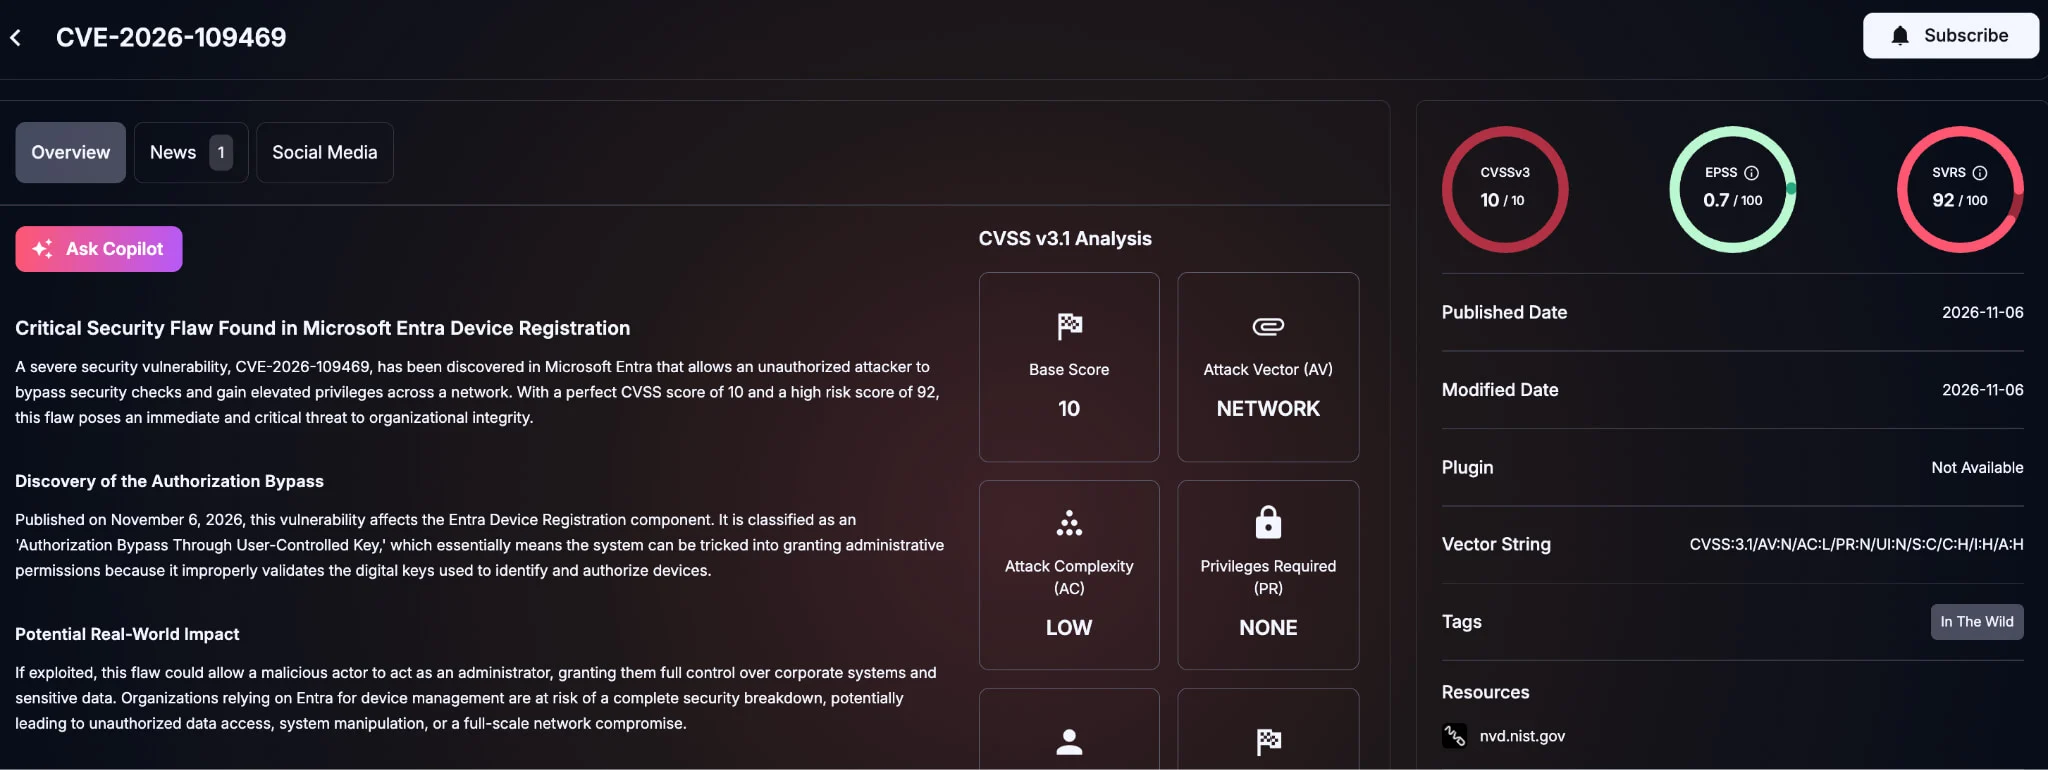
CVE-2026-109469: CVSS 10 Entra Device Registration Flaw
Microsoft has disclosed CVE-2026-109469, a critical elevation of privilege vulnerability in Entra Device Registration, the cloud service that registers and joins devices to Microsoft Entra ID. The flaw carries a…
SRC // SOCRadar -
Ransomware claim: Actualize Consulting (krybit)
Actualize Consulting Engineers Private Limited is an engineering and digital transformation services company based in I…Group: krybitCountry: USSector: Professional ServicesVictim website: Actualize ConsultingDiscovered: 2026-11-10 13:34 UTCAttack date: 2026-11-10 13:34 UTCThis…
-
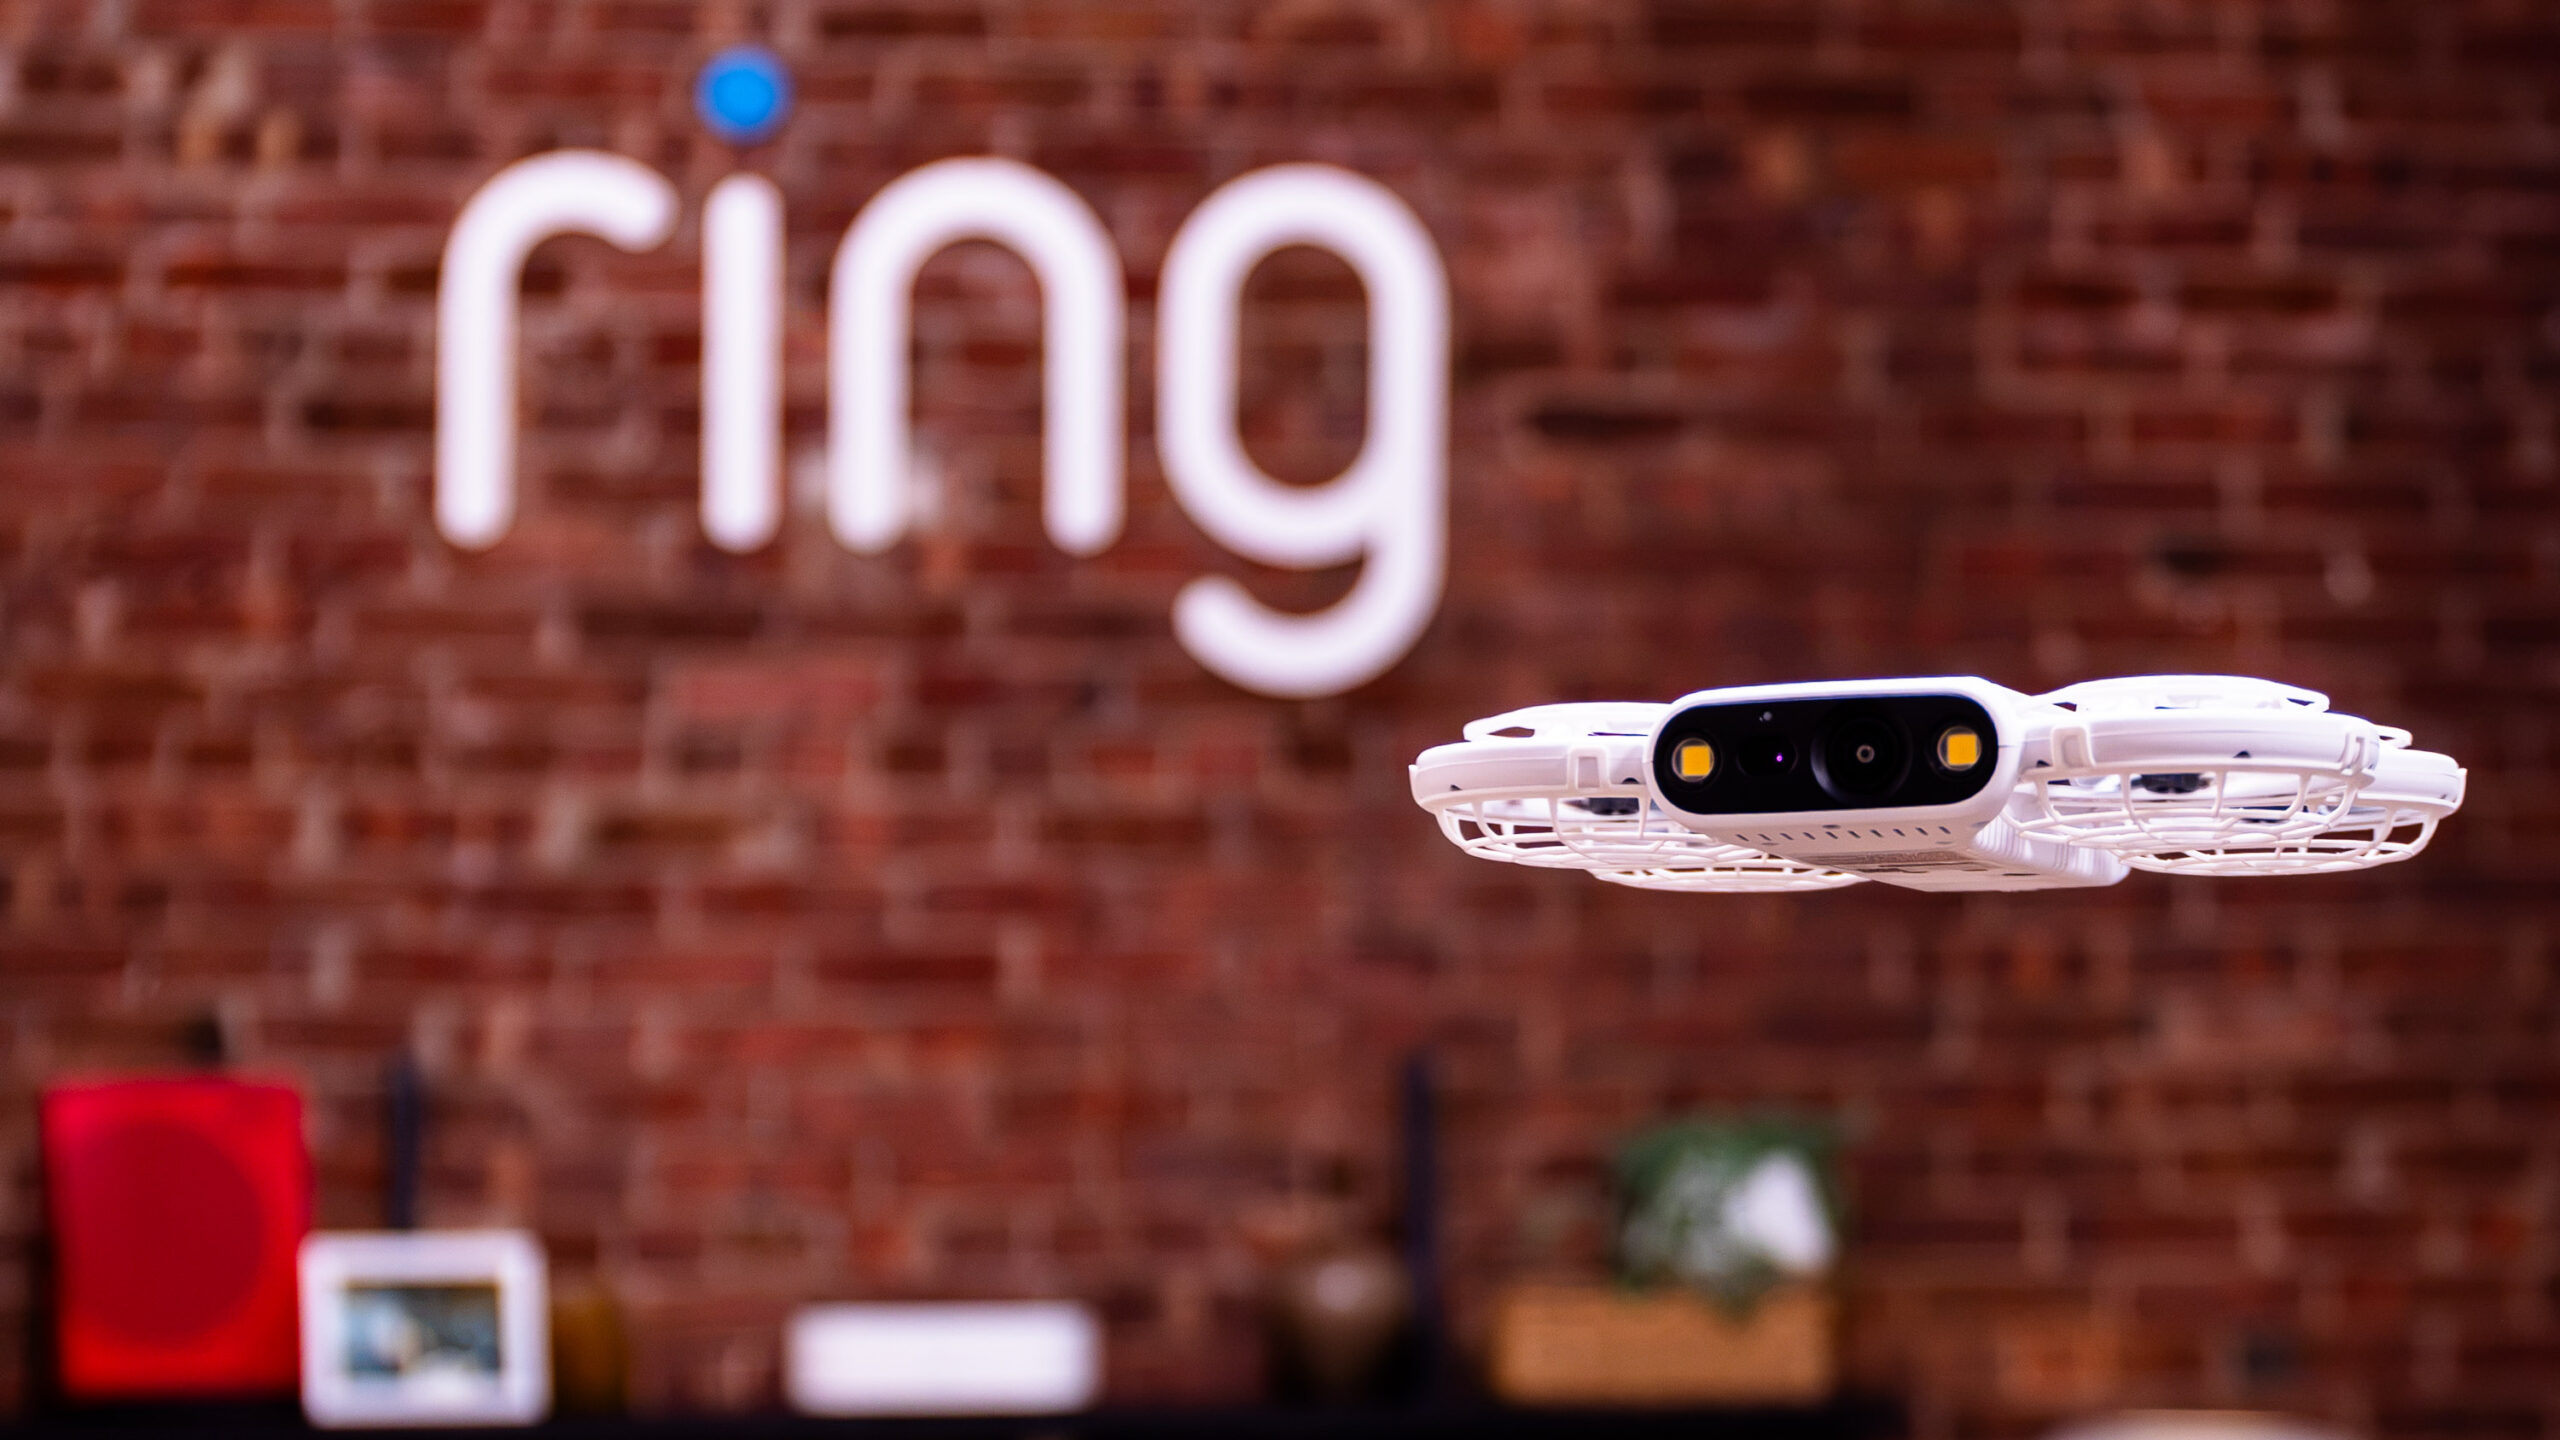
Ring’s new drone patrols your home to keep an eye on things – even upstairs
Alongside the Ring Drone Cam, Ring introduced the Rover Cam for businesses. It investigates disturbances and streams 4K footage.
SRC // ZDNet Security -
Chrome zero-day whack-a-mole continues as 2026 tally hits 8
Another Chrome memory bug gets squashed, but not before attackers got their hands on it
SRC // The Register — Security -
Over a Dozen Organizations Hit in Qubole Supply Chain Attack
Hackers used compromised Qubole IAM credentials to steal customer files, secrets, keys, environment variables, and credentials. The post Over a Dozen Organizations Hit in Qubole Supply Chain Attack appeared first…
SRC // SecurityWeek -
Update Chrome now to fix a flaw attackers are exploiting
Google has released Chrome updates for desktop and Android to patch a zero-day vulnerability already being exploited in attacks.
SRC // Malwarebytes Labs -
CISA tweaks cyber incident form to spot attacks that might be linked
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has updated its online incident reporting form to help analysts spot when attacks on different organizations may be part of the same…
SRC // Help Net Security -
Session, Filen and Other Desktop Apps Still Trust the Cracked eMudhra Keys
Many Electron desktop apps, Session and Filen among them, still trust October’s cracked eMudhra certificates. Some also skip update signature checks, which opens a path to fake updates.
SRC // Privacy Affairs -
How AI security failures are endangering your supply chain – and what you can do
New research provides a stark look at the AI supply chain and the risks it brings to businesses.
SRC // ZDNet Security -
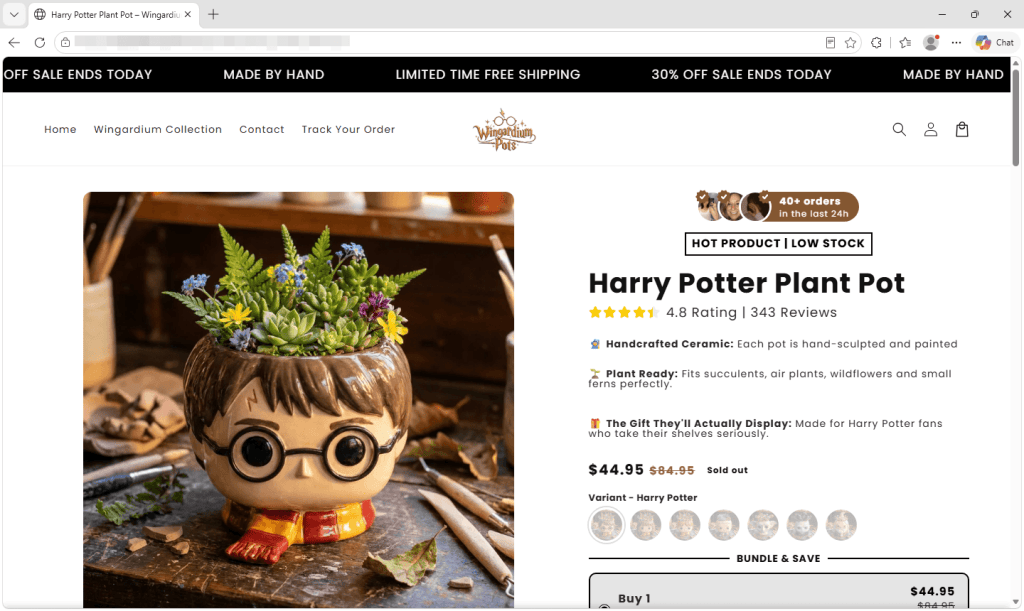
Before you buy an advent calendar, check these warning signs
Copied storefronts, fake urgency, and contradictory product claims are among the warning signs we found on suspicious advent calendar sites.
SRC // Malwarebytes Labs