JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
‘TheMailer’ Phishing Kit Puts AI in the Driver’s Seat
The commercial kit uses attacker-supplied AI models to personalize lures, evade spam filters, and scale campaigns to tens of thousands of targets.
SRC // Dark Reading -
GHSA-8vm9-f75m-5h2m: Filament Curator: Stored XSS via unsanitized SVG upload served inline
Severity: MEDIUMCVE: CVE-2026-69241Ecosystems: composer, composer, composerPackages: awcodes/filament-curator, awcodes/filament-curator, awcodes/filament-curator## Summary SVG files uploaded through the Curator media panel are stored and served inline without any sanitization. An authenticated user with…
SRC // GitHub Security Advisories -
How CISA is prioritizing companies for talks about security improvements
CISA acting director Nick Andersen made his remarks after speaking at FedTalks, presented by FedScoop. The post How CISA is prioritizing companies for talks about security improvements appeared first on…
SRC // CyberScoop -
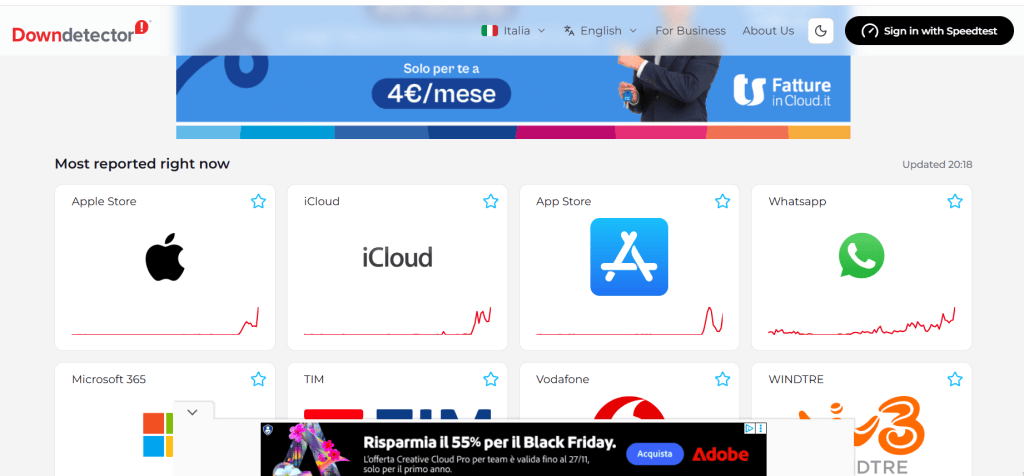
Apple Services Disrupted as NSA Network Goes Down and Equinor Faces Cyberattack
Apple and NSA services faced outages as Equinor reported a cyberattack, highlighting the risks facing increasingly connected infrastructure. Apple customers faced widespread service problems on November 17, with issues affecting…
SRC // Security Affairs -
Japan takes Fugaku supercomputer offlline after cyberattack
The Fugaku supercomputer operated by Japan’s RIKEN Center for Computational Science has been taken offline following a security breach. […]
SRC // BleepingComputer -
GHSA-828w-6qgx-3rcf: Filament Curator: Cross-tenant media metadata disclosure via Curator picker search
Severity: MEDIUMCVE: CVE-2026-63389Ecosystems: composer, composer, composerPackages: awcodes/filament-curator, awcodes/filament-curator, awcodes/filament-curatorSummary In multitenant Filament panels, an authenticated user could retrieve media metadata belonging to other tenants by typing in the Curator media-picker…
SRC // GitHub Security Advisories -
GHSA-xhv5-8fpq-g7hf: qbee-agent: Local Privilege Escalation and Arbitrary File Tampering via Symlink Following in createFile helper
Severity: HIGHCVE: CVE-2026-62336Ecosystems: goPackages: go.qbee.io/agentThis is a Local Privilege Escalation (LPE) vulnerability stemming from improper symlink handling (CWE-59: Link Following) and improper ownership management (CWE-282) inside the qbee-agent file manager…
SRC // GitHub Security Advisories -
GHSA-pr4x-6fj4-gm4h: EGroupware: User-Controlled Identity Provider Selection in SAML Authentication
Severity: MEDIUMCVE: CVE-2026-63672Ecosystems: composer, composerPackages: egroupware/egroupware, egroupware/egroupware### Summary The login() function at line 130 passes the raw user-supplied value `$_REQUEST['idp']` directly to SimpleSAMLphp's `requireAuth()` with only a regex check that…
SRC // GitHub Security Advisories -
Borrowed Code, Real Consequences: What OPTIMJACK Teaches Us
The OPTIMJACK supply chain attack demonstrates how a compromised vendor script can expose websites, highlighting the need for strict segmentation. The post Borrowed Code, Real Consequences: What OPTIMJACK Teaches Us…
SRC // Palo Alto Networks Unit 42 -
GHSA-c5q4-97jw-jggh: AWS-advanced-jdbc-wrapper: Java Deserialization RCE via Cache Poisoning
Severity: HIGHCVE: CVE-2026-14265Ecosystems: mavenPackages: software.amazon.jdbc:aws-advanced-jdbc-wrapper### Impact The AWS Advanced JDBC Wrapper is an open-source JDBC driver wrapper that extends a JDBC driver to enable Amazon Aurora and AWS Cloud features…
SRC // GitHub Security Advisories