JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Over 35,000 Grok-Built Apps Exposed Online, Some Leaking Confidential Data and Passwords
Of the 37,571 Grok-built apps that security company Claroc found online, 35,578 were open to anyone without a sign-in, the researchers said yesterday. They included 24 apps built by staff…
SRC // The Hacker News -
Fortinet Patches Nearly 100 Vulnerabilities
The massive drop comes after the company integrated frontier AI models into its product security testing. The post Fortinet Patches Nearly 100 Vulnerabilities appeared first on SecurityWeek.
SRC // SecurityWeek -
Shipping giant Maersk probes ‘IT security incident,’ data theft
Says it ‘strongly’ suspects attack limited to legacy system, and that nothing sensitive is at risk
SRC // The Register — Security -
Three People Arrested for AI-Enhanced Impersonation Fraud
It’s hard to believe how lucrative this crime can be: According to a press release from the United States attorney’s office for the southern district of New York, three men…
SRC // Schneier on Security -
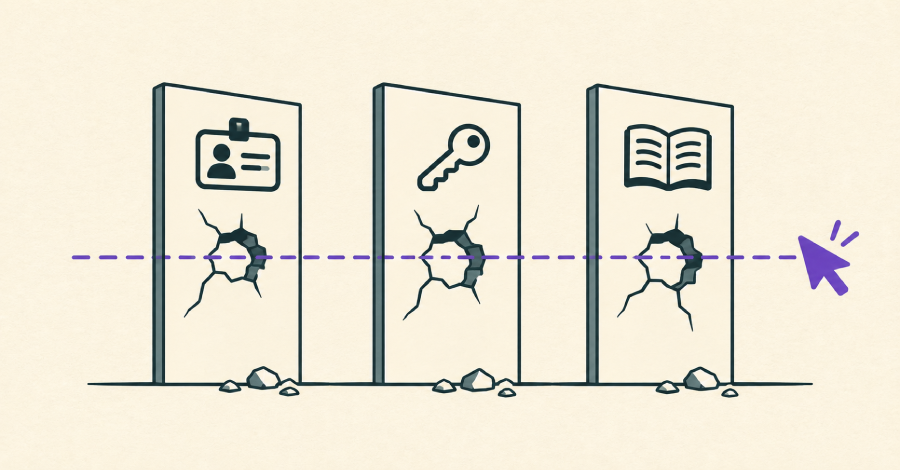
We Built An Agent That Broke All of Our Security Rules. Here’s What We Learned.
We tell customers three things about securing AI agents: they need their own identities, access that fits the job they’re given, and traceability that’s separate from any human’s. That was…
SRC // The Hacker News -
Rubrik enhances DevOps Protection to preserve legitimate work during recovery
Rubrik has announced cyber recovery capabilities for DevOps platforms Microsoft Azure DevOps and GitHub. With built-in anomaly detection, blast radius investigation, and surgical recovery, organizations will be able to detect…
SRC // Help Net Security -
eMudhra Revokes 8 More CAs It Previously Declared Unaffected by Key Compromise
The in-house Python script behind eMudhra’s October key compromise has now cost the company 8 more of its intermediate certificate authorities (CAs), even though it did not weaken their keys.…
SRC // The Hacker News -
Phala Breach: OpenRouter Users Told to Treat DeepSeek Prompts as Exposed
“Confidential AI” host Phala says an attacker could read prompts OpenRouter sent to its DeepSeek V4 Flash 0731 server for 18 days. Rotate any secrets they contained.
SRC // Privacy Affairs -
NCSC scheme will help critical organisations test their cyber defences
New NCSC Cyber Adversary Simulation scheme will help critical organisations strengthen their resilience through rigorous, real-world testing by trusted providers.
SRC // NCSC UK -
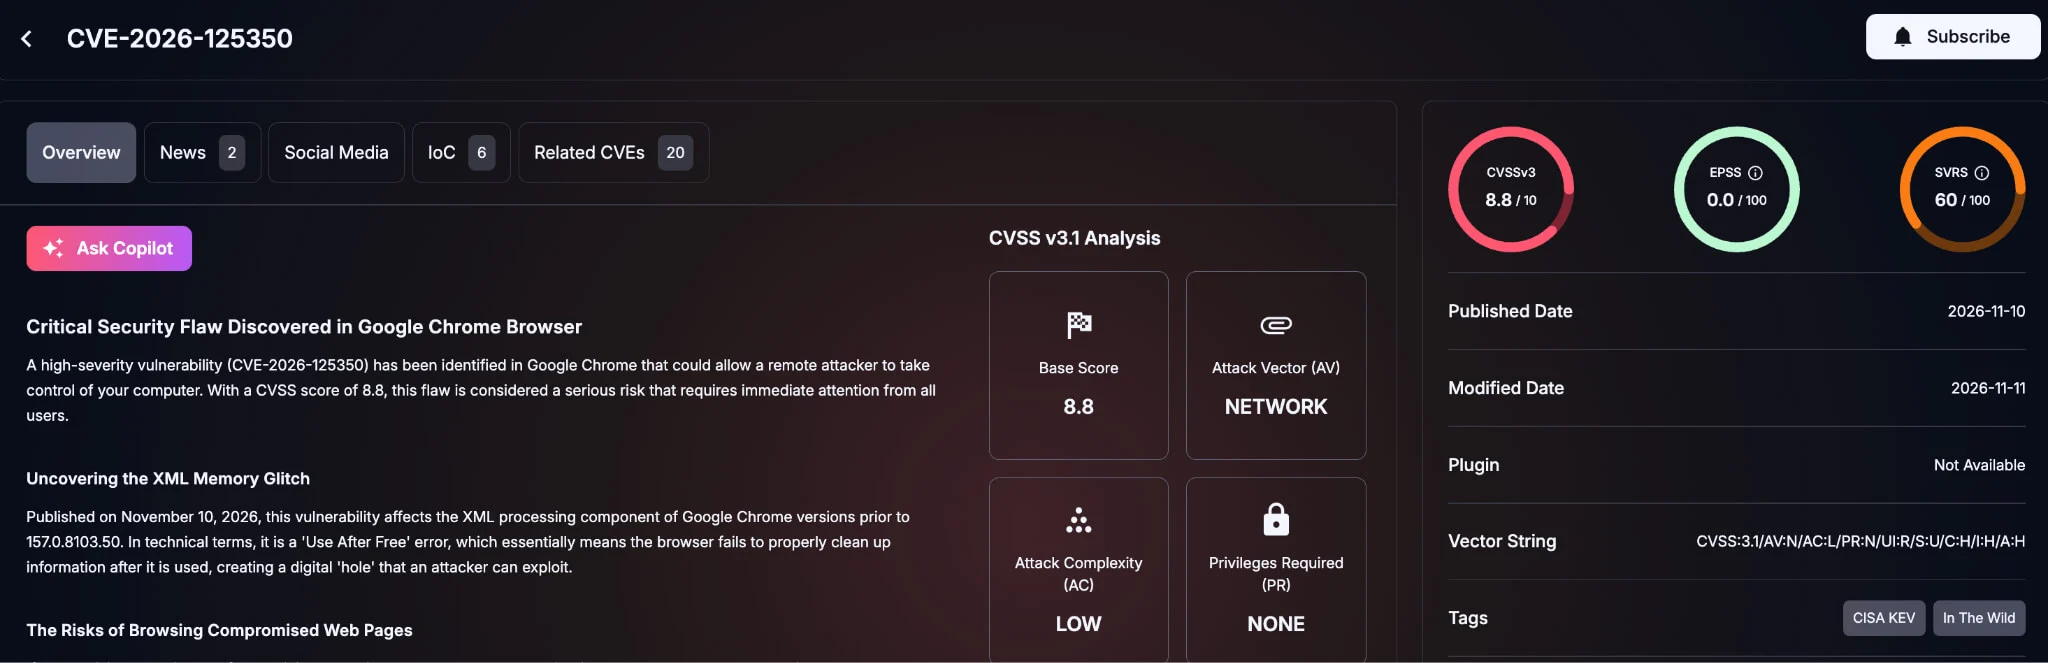
CVE-2026-125350: Google Fixes Exploited Chrome XML Zero-Day
Google has patched CVE-2026-125350, a high-severity use-after-free in Chrome’s XML handling that attackers are already exploiting. The fix landed in the Stable channel on November 9, 2026, three days after…
SRC // SOCRadar