JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Ransomware claim: York University (qilin)
N/AGroup: qilinCountry: CASector: EducationVictim website: www.yorku.caDiscovered: 2026-11-12 06:49 UTCAttack date: 2026-11-12 00:00 UTCThis entry reflects a claim published by an extortion group and collected by a public tracker. It has…
-
Attacker Used 4,837 Hijacked GitHub Accounts to Run a CI Secret Stealer in 1,806+ Repositories
Starting Tuesday, an attacker used stolen credentials for 4,837 GitHub accounts to plant a secret stealer in repositories those accounts could write to, according to Aikido Security, a security software…
SRC // The Hacker News -
Dagster: Open-source cloud-native data pipeline orchestrator
Dagster is an open source orchestrator for data pipelines. It decides what runs, in what order, and when. It also tracks how the tables, datasets, machine learning models, and reports…
SRC // Help Net Security -
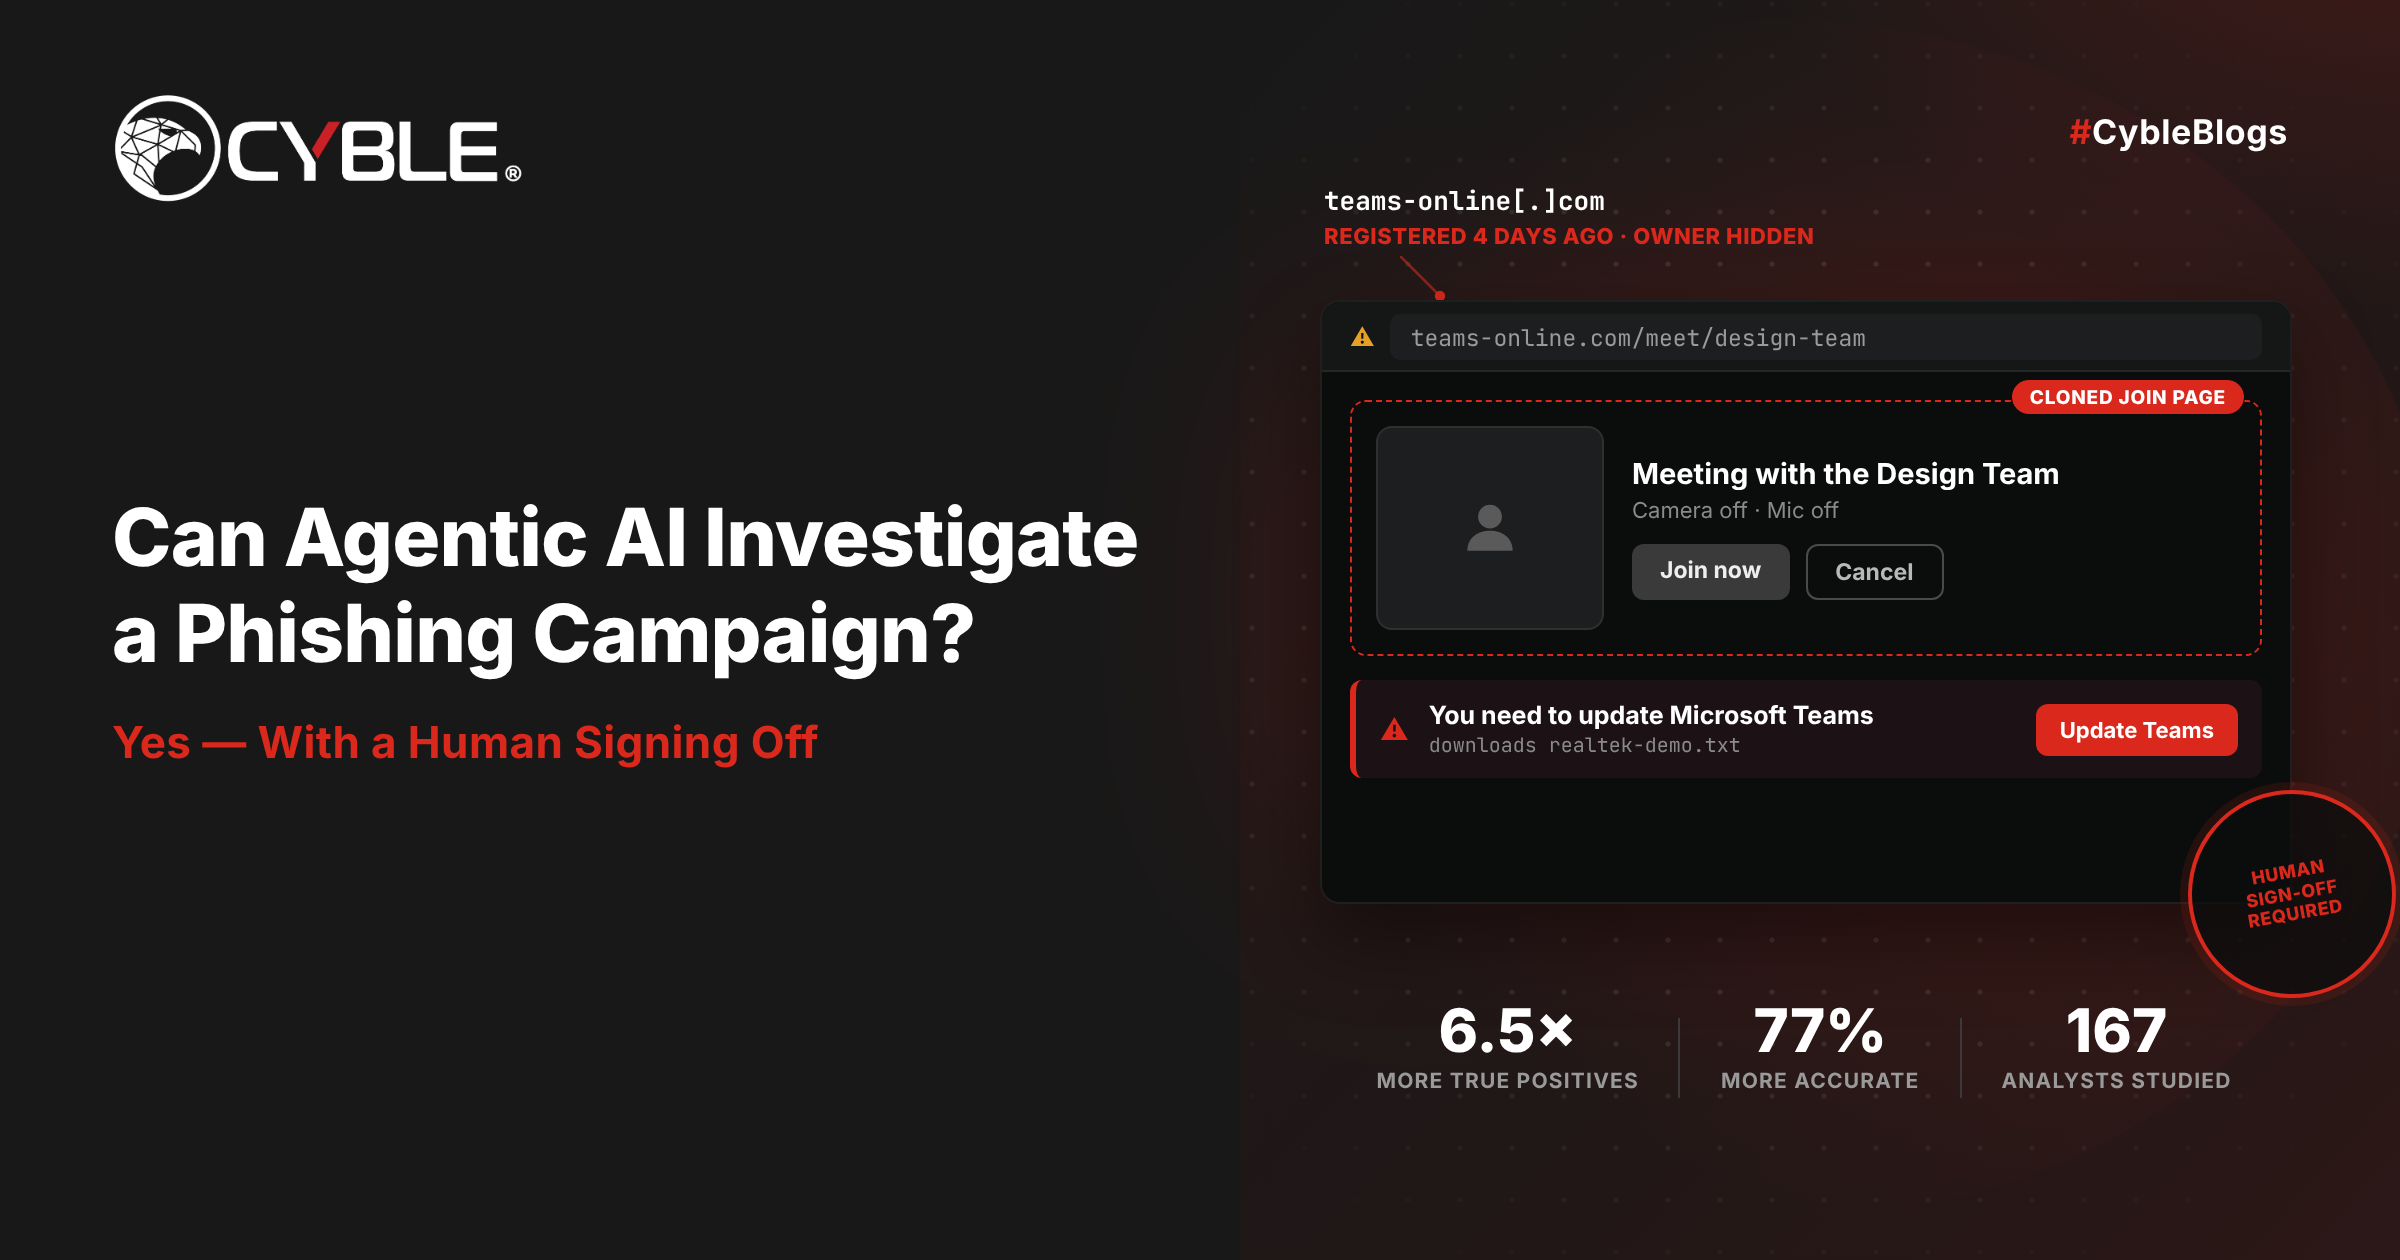
Can Agentic AI Investigate a Phishing Campaign? Evidence Walkthrough
Yes, with a human signing off. An agentic AI can run most of a phishing investigation on its own. It can pull domain registration records, open the lure safely, pivot…
SRC // Cyble Research -
Poland takes its national e-government platform offline after a cyberattack
Poland takes its e-government platform ePUAP offline after stopping a cyberattack, disrupting access to public services. Poland temporarily shut down ePUAP, the government platform citizens and businesses use to reach…
SRC // Security Affairs -
Who collects the keys when an AI agent retires?
Think about the last time a good engineer left your company. Someone collected the laptop and the badge. IT revoked their logins before the end of the day. Their manager…
SRC // Help Net Security -
CISOs say OT will survive a cyberattack, but their engineers aren’t so sure
Ask industrial security chiefs whether their plants would keep running through a full IT compromise, and every one who answered the SANS 2026 ICS/OT survey says yes. Thirty-eight percent expect…
SRC // Help Net Security -
Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely
A critical flaw in Apache HTTP Server’s HTTP/2 module, mod_http2, can let a remote attacker run code on the server. Tracked as CVE-2026-119618, it affects versions 2.4.55 through 2.4.70 and…
SRC // The Hacker News -
Bots pose as AI agents, AI agents pose as humans, and defenses believe both
Over one week in October, an online marketplace took 414,210 visits from traffic wearing the name of a widely used consumer AI agent. Every visit went for the sign-in page,…
SRC // Help Net Security -
ScreenConnect Attacks Target at Least 288 Endpoints Across 48 Organizations With Rogue Clients
ConnectWise has taken the precautionary step of disabling five third-party extensions in partner environments following reports of unauthorized access. In an advisory posted on its site, the company said there…
SRC // The Hacker News