JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
CISO Conversations: Patti Degnan – Part of the Job Is Deciding What Not to Do
Patti Degnan’s identity was stolen in 2006. It set her on a path to the CISO seat at endpoint security firm Glow. The post CISO Conversations: Patti Degnan – Part…
SRC // SecurityWeek -
Dizigom illegal streaming service with 21M monthly visits shuts down
The Alliance for Creativity and Entertainment (ACE) has announced the shutdown of Dizigom, one of Turkey’s largest piracy sites, after a settlement agreement with the site’s operators. […]
SRC // BleepingComputer -
Russian Espionage Actor Star Blizzard Focuses on Cloud Identities for Mass Data Theft
New Google analysis of Star Blizzard, aka Cold Relic, highlighted the group’s growing focus on compromising cloud environments to steal data and facilitate further attacks
SRC // Infosecurity Magazine -
Chrome 158 Patches 204 Vulnerabilities
Google handed out $11,000 for five externally reported flaws but has yet to determine the amounts to be paid for 36 bugs. The post Chrome 158 Patches 204 Vulnerabilities appeared…
SRC // SecurityWeek -
Java4Shell: A critical flaw with a narrow reach
Researchers used AI to find a Java vulnerability and named it Java4Shell. Here’s why organizations need to patch.
SRC // Malwarebytes Labs -
Norwegian Gas Giant Equinor Says It’s Under Cyberattack. Production Keeps Running
Norwegian Gas Giant Equinor confirms cyberattack on IT systems, with no impact on production or confirmed data theft. Equinor, Europe’s largest gas supplier, said on 17 November it had detected…
SRC // Security Affairs -
Java4Shell OpenJDK flaw: Exploitation is tricky and hinges on specific CPUs (CVE-2026-114938)
CVE-2026-114938, a memory corruption flaw in Open Java Development Kit’s Base64 decoder, can allow unauthenticated attackers to run code on servers hosting widely used Java applications. Nicknamed “Java4Shell” by Calif,…
SRC // Help Net Security -
Microsoft Agent Framework Releases Poisoned With Credential Stealer
Versions 1.26.1 and 1.26.2 of agent-framework on PyPI steal Azure, Azure DevOps, and GitHub Actions credentials when Python starts. The post Microsoft Agent Framework Releases Poisoned With Credential Stealer appeared…
SRC // SecurityWeek -
Quality Isn’t The Main Worry About AI Pentesting — Data Privacy and Production Safety Are
AI is speeding up how software is built, which means more code, more changes, and more chances for vulnerabilities to reach production. It’s speeding up how attackers find and exploit…
SRC // The Hacker News -
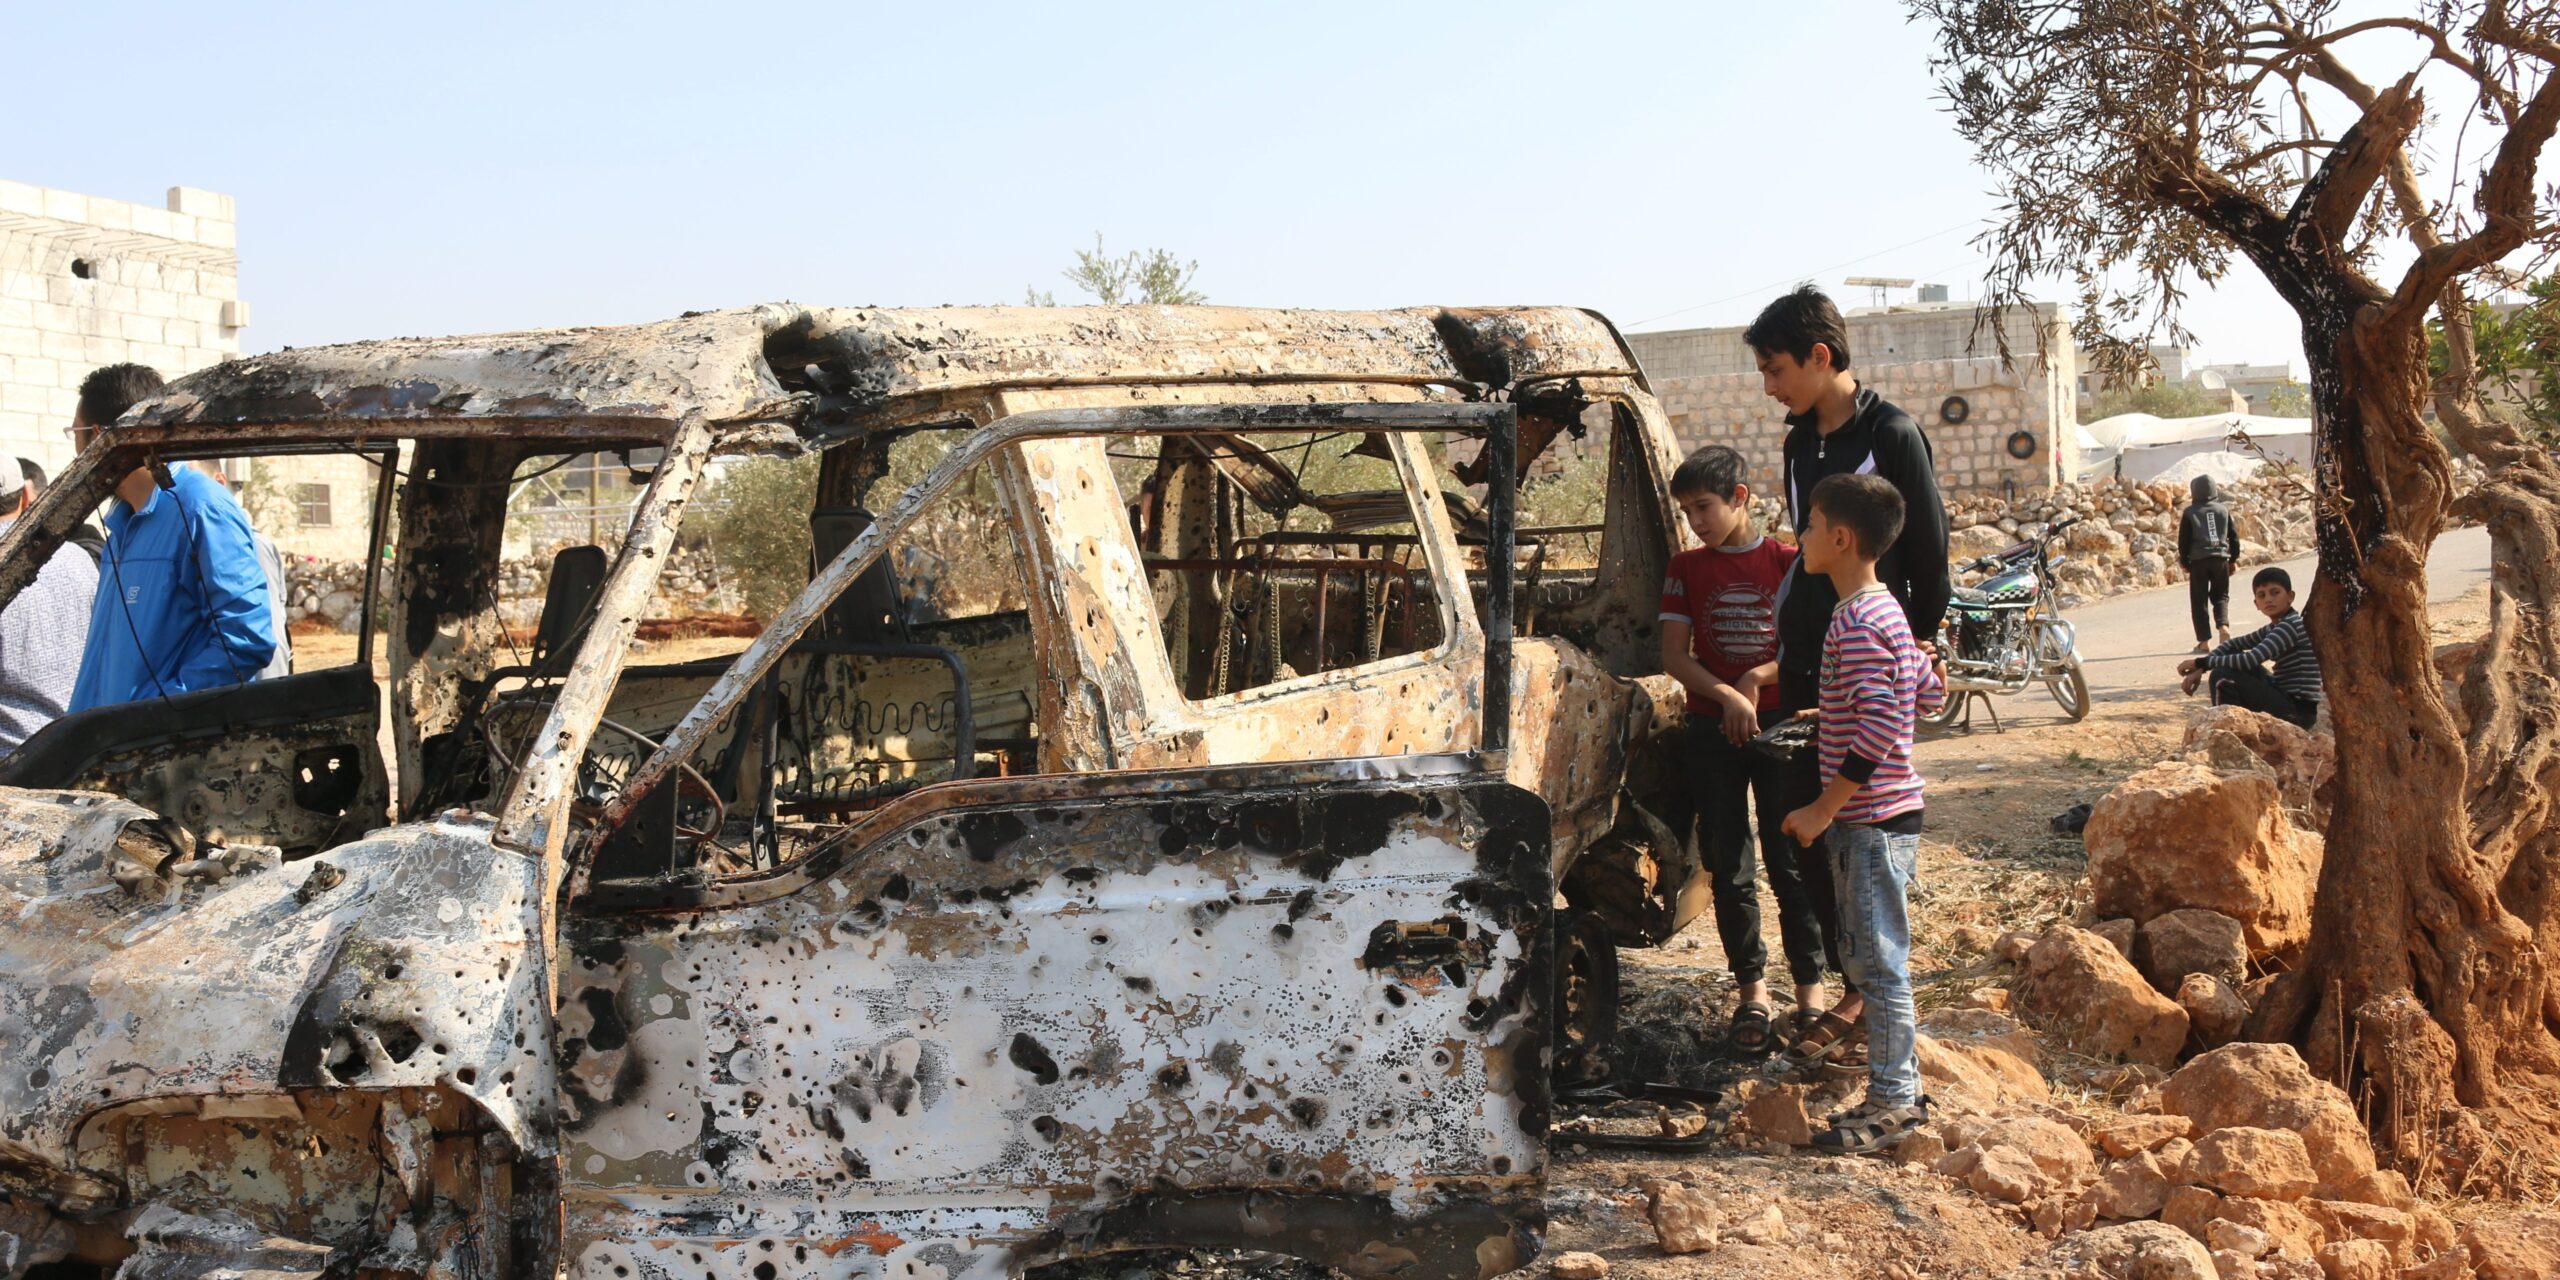
When the U.S. Military Implemented AI, Civilian Deaths Rose
There is no evidence, as advocates claim, that the introduction of Project Maven reduced harm or made targeting more accurate. The post When the U.S. Military Implemented AI, Civilian Deaths…
SRC // The Intercept