ARCHIVE
SOCRadar
-
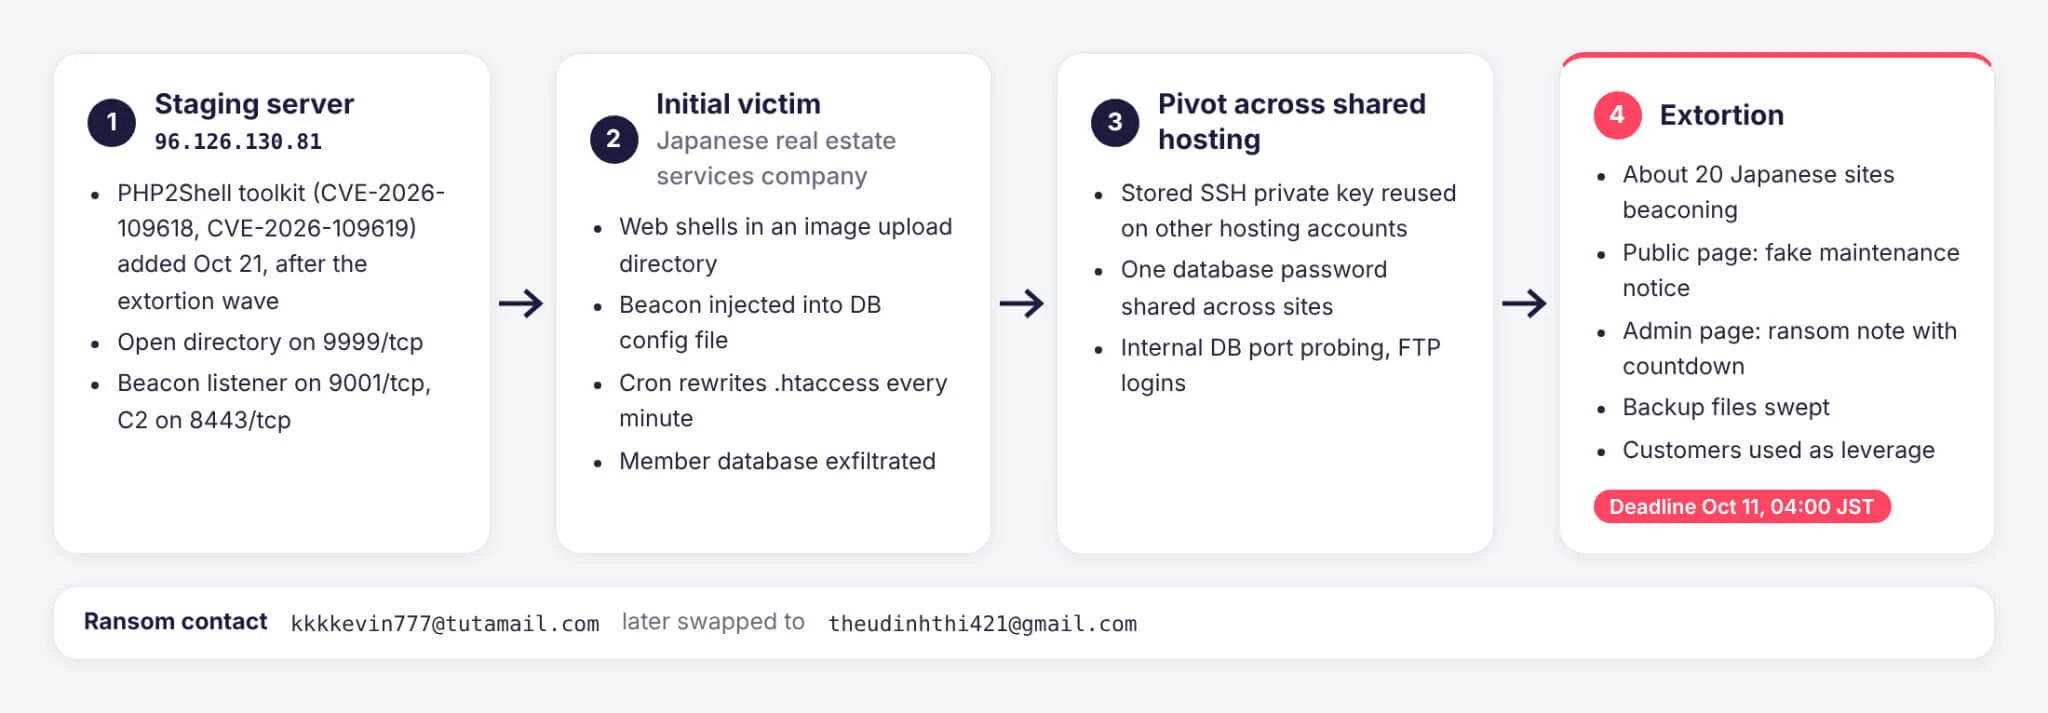
PHP2Shell Weaponized After Japanese Real Estate Extortion
An exposed server ties an extortion wave on about 20 Japanese property sites to an operator who later weaponized PHP2Shell (CVE-2026-109618, CVE-2026-109619)…
SRC // SOCRadar -
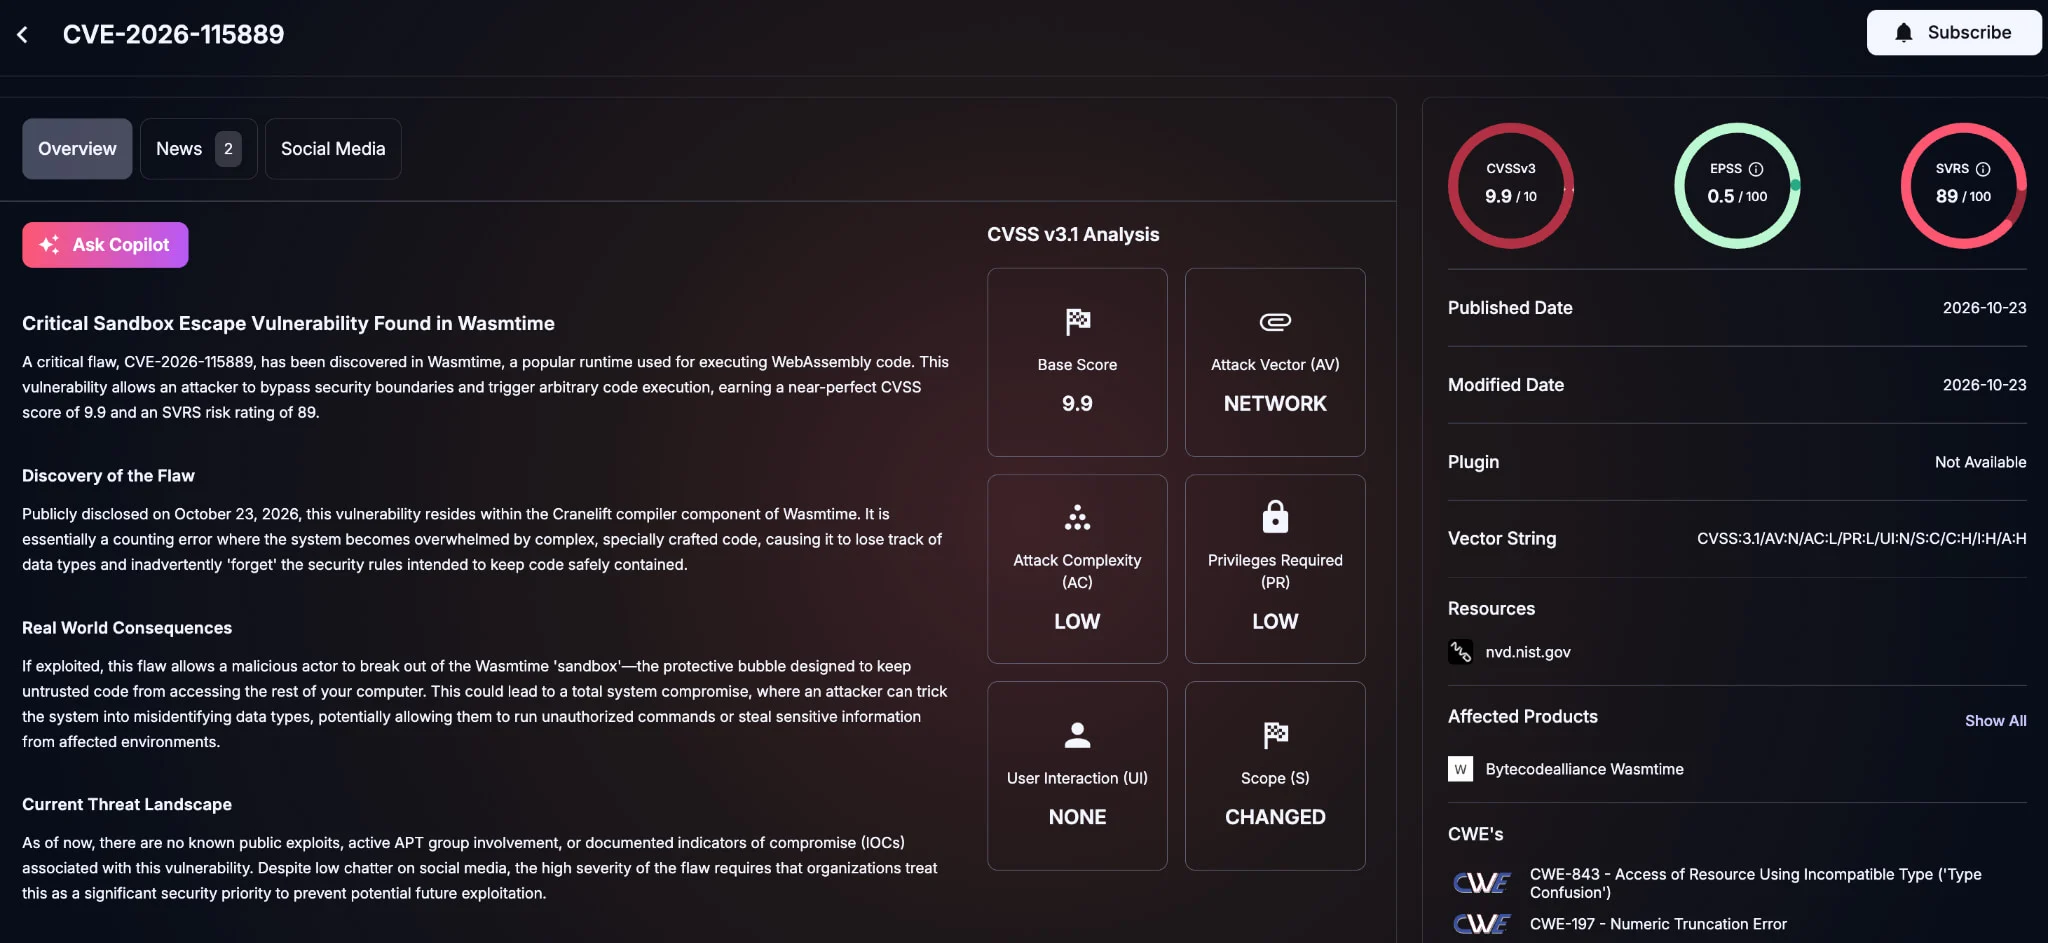
Wasmtime Sandbox Escape Flaws Patched in Cranelift
Two critical Wasmtime sandbox escape flaws, CVE-2026-115889 and CVE-2026-115893, let a crafted WebAssembly (Wasm) module push the Cranelift compiler into generating unsafe machine code. The Bytecode Alliance fixed both on…
SRC // SOCRadar -
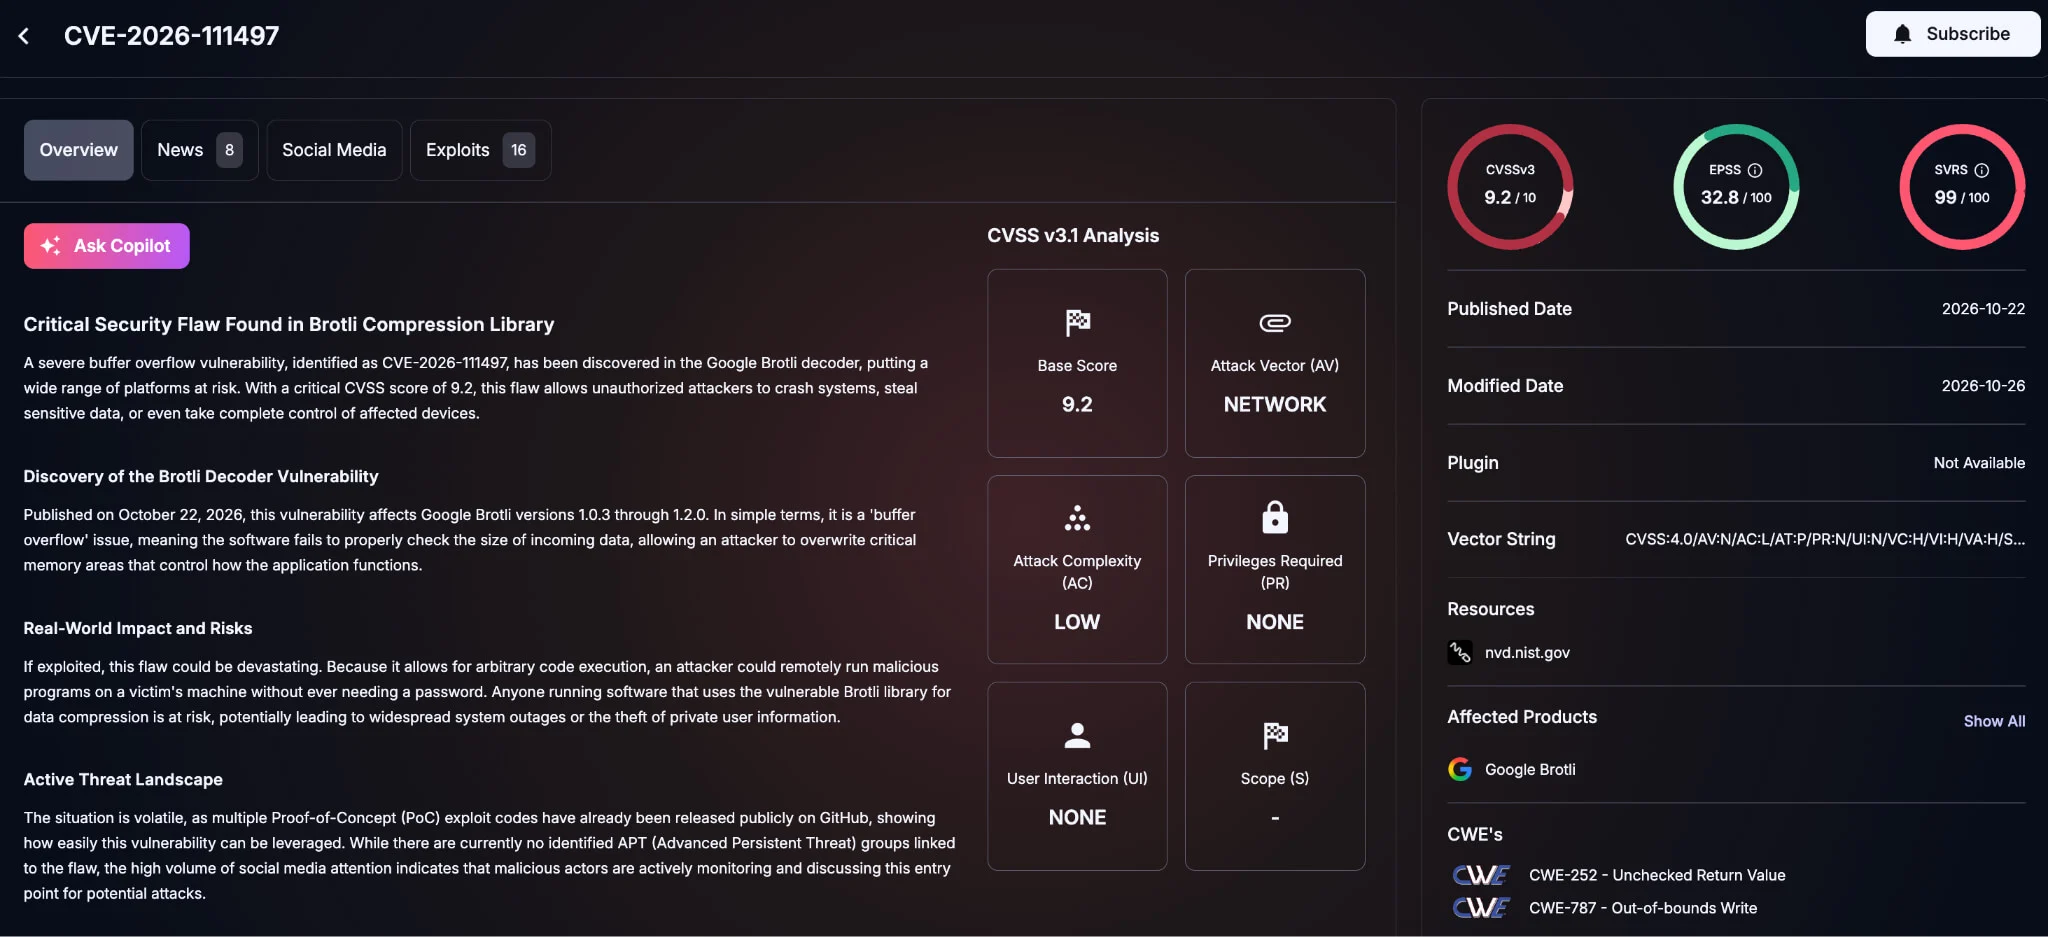
Node2Shell: Brotli Flaw Hits Python Packages
[Update] October 28, 2026: CISA Adds Node2Shell to KEV as Exploit Traffic Emerges [Update] October 27, 2026: PHP Ships Windows Builds With Brotli Fix The Node2Shell Brotli flaw (CVE-2026-111497), disclosed…
SRC // SOCRadar -
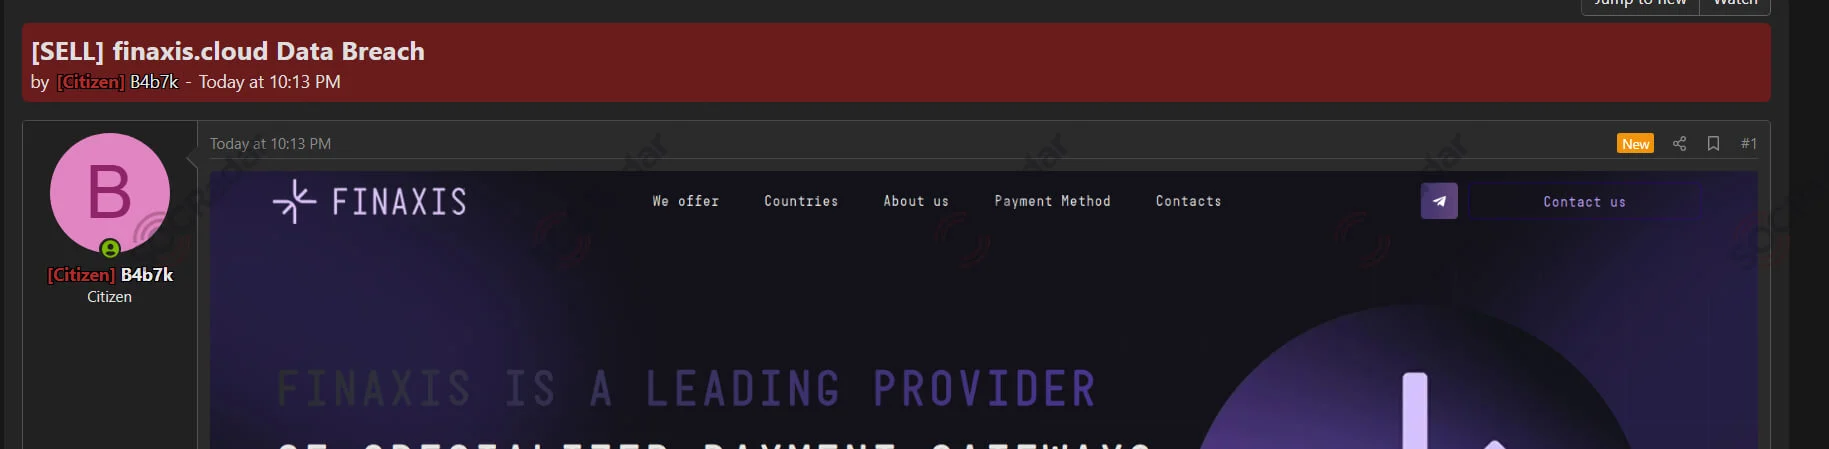
Finaxis, WoWInstaller, Moodle, MyHairCare & HT Médica Leaks
SOCRadar Dark Web Team identified several underground posts, including an alleged Finaxis.cloud data sale involving 400GB of information, a resurfaced WoWInstaller database containing historical user credentials, and an alleged Argentine…
SRC // SOCRadar -
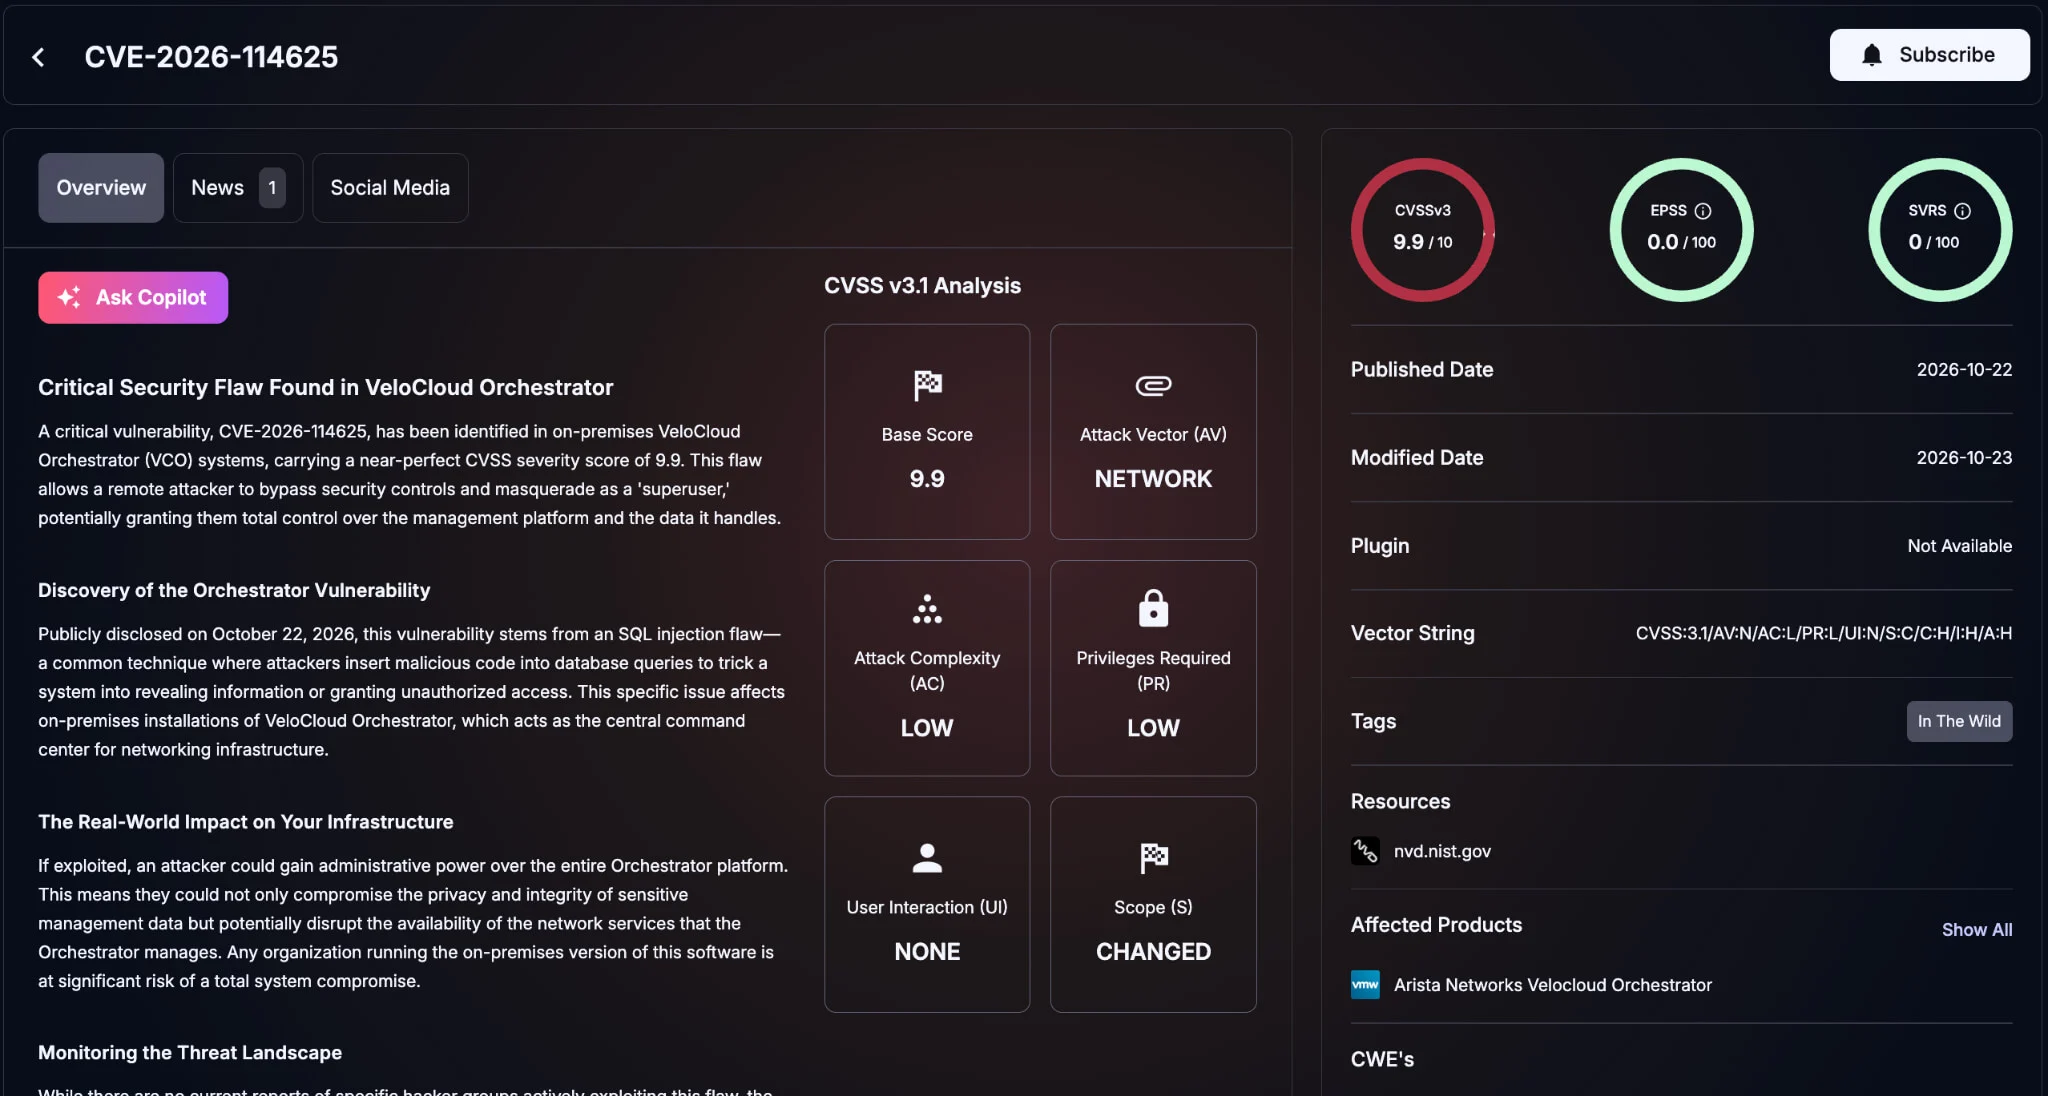
CVE-2026-114625: Actively Exploited VeloCloud Orchestrator Flaw Grants Superuser Access
CVE-2026-114625 is an actively exploited SQL injection flaw in VeloCloud Orchestrator that lets authenticated users gain superuser operator privileges…
SRC // SOCRadar -
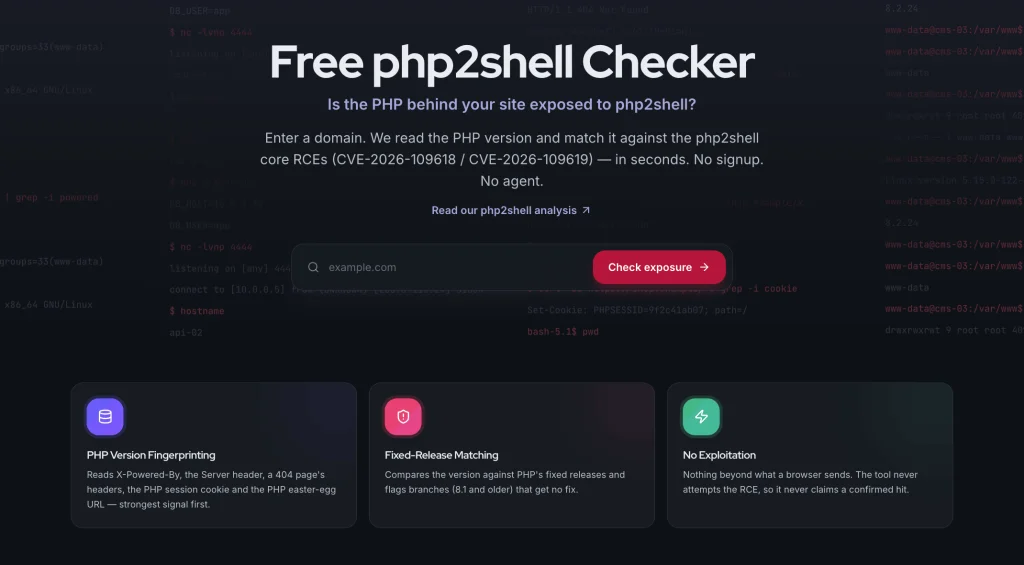
PHP2Shell Exploit Tooling Found on Exposed Attacker Server
SOCRadar Threat Intelligence Unit (STRU) researchers found PHP2Shell exploit tooling on an attacker-controlled server whose working directory was exposed…
SRC // SOCRadar