The Investigatory Powers Commissioner’s Office (IPCO) in its annual report for 2025, published Thursday, said it was “very concerned” and “disappointed with the time it has taken GCHQ to investigate” the issue.
Source: The Record · 2026-10-30
The Investigatory Powers Commissioner’s Office (IPCO) in its annual report for 2025, published Thursday, said it was “very concerned” and “disappointed with the time it has taken GCHQ to investigate” the issue.
Source: The Record · 2026-10-30
Bedrock Data has announced AI-assisted remediation, which federates the work of fixing data exposure to the data owners across the enterprise. Bedrock Data discovers who owns each exposed dataset, opens a ticket for that owner in the Jira or ServiceNow workflow the enterprise already runs and supplies the context needed to fix it. When the owner closes the ticket, Bedrock Data validates that the exposure is remediated and reopens the ticket if it is not. … More
Source: Help Net Security · 2026-10-30
.kadence-column482616_9de20c-07 > .kt-inside-inner-col{padding-top:20px;padding-right:20px;padding-bottom:10px;padding-left:20px;}.kadence-column482616_9de20c-07 > .kt-inside-inner-col{column-gap:var(–global-kb-gap-sm, 1rem);}.kadence-column482616_9de20c-07 > .kt-inside-inner-col{flex-direction:column;}.kadence-column482616_9de20c-07 > .kt-inside-inner-col > .aligncenter{width:100%;}.kadence-column482616_9de20c-07 > .kt-inside-inner-col{background-color:#ffe5e5;}.kadence-column482616_9de20c-07 > .kt-inside-inner-col:before{opacity:0.3;}.kadence-column482616_9de20c-07{position:relative;}@media all and (max-width: 1024px){.kadence-column482616_9de20c-07 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}@media all and (max-width: 767px){.kadence-column482616_9de20c-07 > .kt-inside-inner-col{flex-direction:column;justify-content:center;}}
Binance says a security incident affected approximately $6.3 billion in cryptocurrency. Its initial investigation points to a compromised DevOps engineer’s laptop as a possible entry point.
The exchange says it has frozen around $3 billion with help from blockchain partners. It has promised to cover all losses using its emergency fund and company funds. Binance is reportedly the largest cryptocurrency exchange by daily trading volume.
In an update on October 30, Binance said attackers may have used a compromised laptop belonging to a DevOps engineer to access a service container and submit unauthorized withdrawal transactions. The company said:
“We have found no evidence of any wallet private key leak.”
This doesn’t mean that one employee could simply transfer billions of dollars. Binance co-CEO Richard Teng told BleepingComputer the attacker did not simply use one engineer’s permissions. The incident involved a more complex process, rather than a single “one-click” action. Binance also said investigators had identified additional breach points.
Blockchain intelligence firms TRM Labs and Chainalysis have linked the theft to TraderTraitor, a North Korean hacking group associated with previous cryptocurrency thefts. TRM Labs estimates that about $6.36 billion left Binance wallets across ten blockchains, with most of it moving within about 20 minutes.
Binance says approximately $3 billion has been frozen on-chain, while blockchain analysts have reported somewhat different totals. For now, those figures should be treated as developing estimates rather than a final accounting of recovered funds or the exchange’s ultimate losses.
Binance.com users (Binance.US was not affected) should check their accounts, avoid follow-up scams, and respond quickly if they spot signs of a separate compromise.
Pro tip: Unsure whether a message is a scam? Check it with Malwarebytes’ Scam Guard for an assessment and advice on what to do next.
Source: Malwarebytes Labs · 2026-10-30
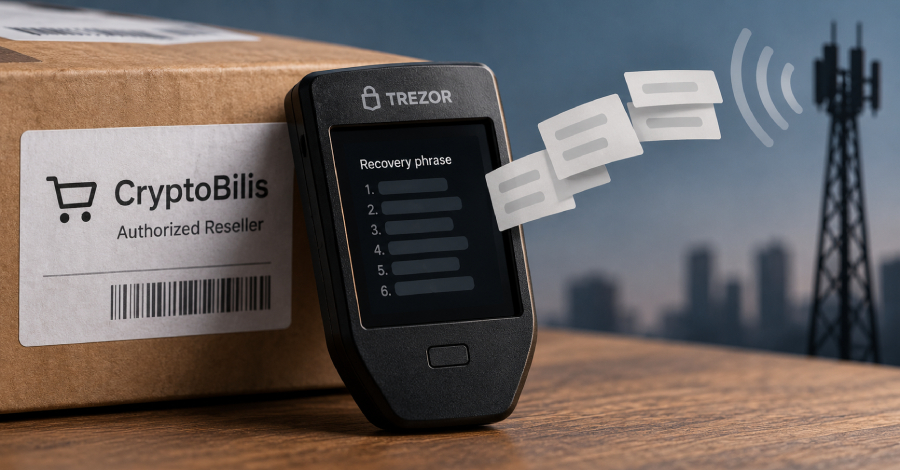
A Trezor Safe 5 hardware wallet bought from the reseller CryptoBilis has an extra circuit board that sends out the recovery phrase over a mobile network, a customer has reported.
Trezor has not yet examined the device. It is telling everyone who bought a Trezor from CryptoBilis since March 2026 to move their funds to a new wallet with a new recovery phrase.
Trezor said in a blog post 
Source: The Hacker News · 2026-10-30
Remediation prioritization after a pentest is the process of ranking and ordering security findings based on their risk, exploitability, and business impact. A penetration test can produce any number of findings, ranging from the very low (zero) to the very high (hundreds).
The security of the tested organization depends on the findings management processes addressing the most important results first.
When prioritizing pentest results, some practitioners rely solely on frameworks like the Common Vulnerability Scoring System (CVSS). The logic is sound: the higher a vulnerability’s CVSS score is, the more risk it poses, and the sooner you should fix it, right?
Unfortunately, the reality is much more complicated. Boiling down a complex ecosystem of risk into a one-dimensional number means ignoring the wider business context. In the end, that means you fix vulnerabilities that pose serious theoretical risk first, while genuine exposures get pushed to the back of the queue.
Lets use two hypothetical vulnerabilities as an example.
Now think about which one you would fix first.
Would you prioritize the“critical” flaw on an intranet site, containing no sensitive data that attackers could only reach if they’d already compromised your internal network? Or would you prioritize the “medium” flaw on an API that processes live credit card transactions, and that any script kiddie could manipulate?
Across an entire organization, or multiple organizations if you’re a consultant or MSP, those critical flaws can really pile up. In one AI pentesting survey of 158 base practitioners by Pentest-Tools.com, conducted in June 2026, 68.4% of respondents said a 500+ candidate finding set would strain the team or be unmanageable.
Approaching risk prioritization by trying to fix every “Critical” finding is going to exhaust you and your team. That’s when people make mistakes, and you end up with a major incident on your hands.
That same distinction, in part, separates a candidate finding from a validated one. For example, vulnerability with a high CVSS score but near-zero exploitability should remain a candidate. To graduate a vulnerability from a candidate to a legally and technically validated finding, it must pass through a strict filter that involves three processes.
The first step is to eliminate as much administrative noise as possible. That means deduplicating findings and removing any that are obviously non-exploitable.
Then, you need to confirm exploitability. That typically means executing a safe, controlled attack path against the target environment to prove that a state change, data exposure, or privilege escalation can actually occur.
Finally, you need concrete evidence. A validated finding cannot rely on a generic tool’s “confidence score.” It must include comprehensive proof that a developer or auditor can immediately follow:
Now, many vendors are going to claim that AI-generated findings ease the strain of exploit validation. In many cases, they’re telling the truth. But as with any AI technology, a healthy level of skepticism is important. According to the same study, 81.7% of respondents encounter AI-generated findings that need significant manual exploit validation at least sometimes.
Together, CVSS, Exploit Prediction Scoring System (EPSS) scores, and business context create a single risk ranking that reflects real-world danger to the tested organization.
CVSS, as mentioned earlier, measures theoretical severity. It tells you how bad a flaw is in a vacuum, but is entirely blind to context. EPSS measures probability. It tells you how likely an attacker is to exploit a flaw in the wild over the next 30 days, but doesn’t measure the potential impact of an exploitation.
Business context measures operational impact. It tells you the value of the affected asset, how easily an attacker can reach a flaw, and what they can steal. It tells you nothing, however, about the threat itself. Ultimately, business context is expressed as residual risk, the danger left over after you factor in your existing defenses. Calculating it relies on measuring four factors:
By checking these boxes, you won’t waste time fixing a “Critical” bug locked in an empty, disconnected server. Instead, you’ll prioritize the “Medium” bug on your public checkout page that hackers are actively trying to breach.
Sometimes, you’re not going to have much time for remediation. That’s natural. In those situations, prioritize validated findings with high threat activity (EPSS score) and critical business exposure. They’re the findings that pose the most threat to your organization.
Prioritization done well is itself evidence. A ranked, validated list, with a written reason for what was deprioritized, is what a team can defend later.
You’ll need to record the owner (the specific individual accepting the risk), the date of the decision, the technical operational basis for deprioritization (such as an active compensating control), and a hard review date for re-evaluation.
A prioritized ranking list counts as valid audit evidence because it proves compliance alignment with several major security frameworks. For example:
A ranked, validated list also gives MSPs and MSSPs a clear, auditable record of truth that clients can either accept or challenge with their own evidence. This transparency ensures both sides agree on which real-world risks need to be addressed first.
A defensible ranking record contains the validated asset identification, its technical CVSS severity, its real-world EPSS probability, the active compensating controls defining its residual list, the formal sign-off from the risk owner, and the targeted review schedule.
About the Author: Josh Breaker-Rolfe is a Content writer at Bora. He graduated with a degree in Journalism in 2021 and has a background in cybersecurity PR. He’s written on a wide range of topics, from AI to Zero Trust, and is particularly interested in the impacts of cybersecurity on the wider economy.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, pentest)
Source: Security Affairs · 2026-10-30
Threat actors are attempting to exploit a high-severity unauthenticated race condition leading to remote code execution.
Source: SecurityWeek · 2026-10-30
Dream found that a suspected Chinese-nexus actor gained root access to Palo Alto Network firewall servers to target government organizations
Source: Infosecurity Magazine · 2026-10-30
The alert is critical. The fix is known. And the ticket sits in a queue for days. Security teams understand the risk, but the people who keep applications available need proof that the change won’t break anything.
Their concerns are practical. An IPS protection could block legitimate traffic. A configuration change could interrupt a service. An endpoint policy could affect an application
Source: The Hacker News · 2026-10-30
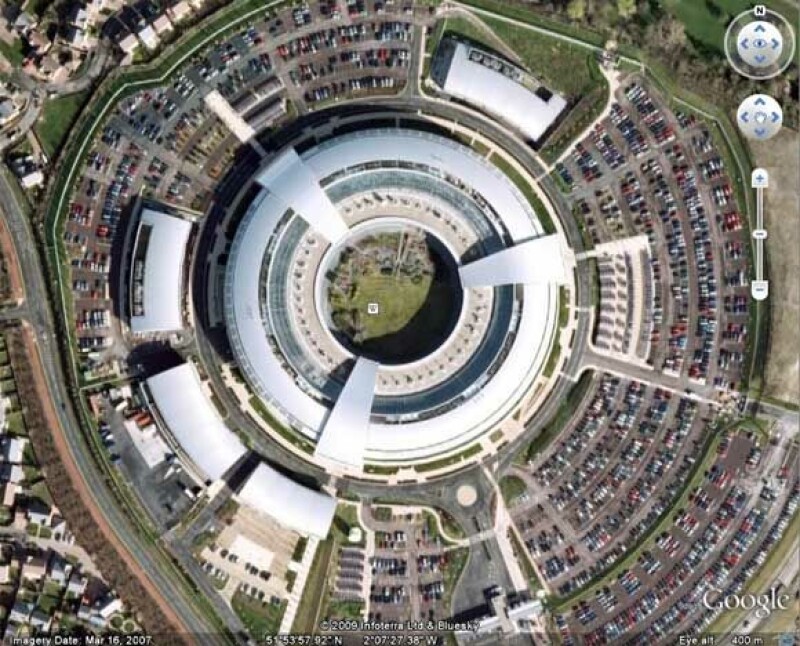
Thousands of GCHQ storage drives containing sensitive data have been lost for years, and the British signals intelligence agency still cannot explain where they are. According to the Investigatory Powers Commissioner’s Office’s (IPCO) annual report, the missing storage drives have been known to officials for years, and may contain data related to the Investigatory Powers Act (IPA). “I remain concerned that GCHQ has not yet established a sufficiently clear understanding of the scale, location, and recoverability of lost removable media that may contain IPA-related data, notwithstanding that the underlying issues were first drawn to my attention several years ago,” wrote investigatory powers commissioner Lord Brian Leveson. “While I recognize the technical and practical challenges involved, the passage of time without a comprehensive account heightens the importance of sustained senior focus and assured remediation. Given the potential sensitivity of the material involved, I will continue to monitor progress closely.” Described as “a very significant number,” the report notes that GCHQ has scoped the maximum number of potentially lost drives, but is unaware of the exact scale of the issue. The agency has embarked on “a program of further work” to locate as many of the lost devices as possible, which includes implementing an automated asset-tracking system by the end of the year. After this is up and running, it said it will be able to provide a more precise number of lost drives. A GCHQ spokesperson told The Register: “As IPCO have reported, our management system for removable media was previously not sufficiently robust to effectively track the items that were registered for use. IPCO are right to note the flaws in the data the system produced, and we have taken action against all their recommendations. “We recognize the importance of security of removable media in our systems, and have a range of measures to mitigate the risks posed by these items. The findings in the report have been addressed comprehensively, and all necessary steps to correct this issue have been taken.” Peter Sommer, digital forensics expert and visiting professor at de Montfort and Birmingham City universities, told us: “Bearing in mind the sort of highly sensitive data collected and processed by GCHQ IPCO is right to be very concerned, the more so as the issue is already several years old. Vast quantities of data can be stored on the cheapest lowest cost hard disks and cards. At a much more modest level as an expert witness I know how important it is to keep careful track of the data entrusted to me.” Losing important devices is not an achievement that’s exclusive to GCHQ. Myriad stories like this have emerged from all corners of the public sector over the years, such as the British Minidstry of Defence misplacing USB drives containing secret information in the mid-noughties, civil servants routinely losing their BlackBerry handsets, and UK police losing thousands of devices, too. The missing storage drives comprise just one of the agency’s various transgressions highlighted by IPCO in its report. There are also “significant concerns” over the lax safeguards used to restrict the UK’s overseas partners when accessing bulk-intercepted data collected by GCHQ. IPCO was satisfied at how GCHQ ensured its own analysts remained compliant with safeguards around accessing confidential material related to journalism, journalistic sources, and privileged legal information. However, there were concerns around how these same safeguards were applied to its international partners, which have access to its so-called bulk data interception “product.” The report notes that most partners were properly restricted from accessing such material, although an internal probe found that there were inadequate arrangements in respect to one partner and their access to journalistic material. Both GCHQ and the overseas agency committed to rectifying the situation. GCHQ was also questioned after a software bug in a web app “used by a relatively small section of the public” misidentified individuals thought to be participating in terrorist activities. The agency identified and reported the flaw in the software, which it used for “target discovery work,” and although it only affected a small number of individuals, the errors led to five port stops made under the Terrorism Act and caused “serious prejudice” to the victims. A port stop, for the uninitiated, involves law enforcement detaining a suspect at a UK port, airport, train station, or within one mile of the Northern Ireland border, and can be carried out without suspicion. Once detained, individuals have a legal responsibility to provide passwords to their electronic devices, which can be seized for up to seven days, and in some cases have their biometric markers taken. Failure to comply can lead to a three-month prison term. IPCO ruled, however, that there was ultimately no error made as defined by the IPA. “This is because the activity was lawfully authorised under an interception warrant and the adoption of an unintentionally and unforeseeably imperfect target discovery methodology did not constitute such an error,” the report stated. Despite the agency’s vast technical expertise, IPCO said that the issue affecting the software was not foreseeable. GCHQ was not the only offender among the UK intelligence community (UKIC), with MI5’s mishandling of the infamous Agent X case taking center stage in the report. Agent X was an anonymous MI5 informant whose real identity has never been publicly released. A secret inquiry by IPCO as well as the report revealed that MI5 managed Agent X despite knowing he was a violent misogynist obsessed with extreme violence. Lord Leveson said “the case of Agent X is as serious as anything I have dealt with as Commissioner,” after MI5 gave false evidence to the High Court and Investigatory Powers Tribunal to protect a foreign neo-Nazi informant who was under police investigation for abusing his partner, referred to publicly as “Beth.” ®
Source: The Register — Security · 2026-10-30
Thousands of GCHQ storage drives containing sensitive data have been lost for years, and the British signals intelligence agency still cannot explain where they are. According to the Investigatory Powers Commissioner’s Office’s (IPCO) annual report, the missing storage drives have been known to officials for years, and may contain data related to the Investigatory Powers Act (IPA). “I remain concerned that GCHQ has not yet established a sufficiently clear understanding of the scale, location, and recoverability of lost removable media that may contain IPA-related data, notwithstanding that the underlying issues were first drawn to my attention several years ago,” wrote investigatory powers commissioner Lord Brian Leveson. “While I recognize the technical and practical challenges involved, the passage of time without a comprehensive account heightens the importance of sustained senior focus and assured remediation. Given the potential sensitivity of the material involved, I will continue to monitor progress closely.” Described as “a very significant number,” the report notes that GCHQ has scoped the maximum number of potentially lost drives, but is unaware of the exact scale of the issue. The agency has embarked on “a program of further work” to locate as many of the lost devices as possible, which includes implementing an automated asset-tracking system by the end of the year. After this is up and running, it said it will be able to provide a more precise number of lost drives. A GCHQ spokesperson told The Register: “As IPCO have reported, our management system for removable media was previously not sufficiently robust to effectively track the items that were registered for use. IPCO are right to note the flaws in the data the system produced, and we have taken action against all their recommendations. “We recognize the importance of security of removable media in our systems, and have a range of measures to mitigate the risks posed by these items. The findings in the report have been addressed comprehensively, and all necessary steps to correct this issue have been taken.” Peter Sommer, digital forensics expert and visiting professor at de Montfort and Birmingham City universities, told us: “Bearing in mind the sort of highly sensitive data collected and processed by GCHQ IPCO is right to be very concerned, the more so as the issue is already several years old. Vast quantities of data can be stored on the cheapest lowest cost hard disks and cards. At a much more modest level as an expert witness I know how important it is to keep careful track of the data entrusted to me.” Losing important devices is not an achievement that’s exclusive to GCHQ. Myriad stories like this have emerged from all corners of the public sector over the years, such as the British Minidstry of Defence misplacing USB drives containing secret information in the mid-noughties, civil servants routinely losing their BlackBerry handsets, and UK police losing thousands of devices, too. The missing storage drives comprise just one of the agency’s various transgressions highlighted by IPCO in its report. There are also “significant concerns” over the lax safeguards used to restrict the UK’s overseas partners when accessing bulk-intercepted data collected by GCHQ. IPCO was satisfied at how GCHQ ensured its own analysts remained compliant with safeguards around accessing confidential material related to journalism, journalistic sources, and privileged legal information. However, there were concerns around how these same safeguards were applied to its international partners, which have access to its so-called bulk data interception “product.” The report notes that most partners were properly restricted from accessing such material, although an internal probe found that there were inadequate arrangements in respect to one partner and their access to journalistic material. Both GCHQ and the overseas agency committed to rectifying the situation. GCHQ was also questioned after a software bug in a web app “used by a relatively small section of the public” misidentified individuals thought to be participating in terrorist activities. The agency identified and reported the flaw in the software, which it used for “target discovery work,” and although it only affected a small number of individuals, the errors led to five port stops made under the Terrorism Act and caused “serious prejudice” to the victims. A port stop, for the uninitiated, involves law enforcement detaining a suspect at a UK port, airport, train station, or within one mile of the Northern Ireland border, and can be carried out without suspicion. Once detained, individuals have a legal responsibility to provide passwords to their electronic devices, which can be seized for up to seven days, and in some cases have their biometric markers taken. Failure to comply can lead to a three-month prison term. IPCO ruled, however, that there was ultimately no error made as defined by the IPA. “This is because the activity was lawfully authorised under an interception warrant and the adoption of an unintentionally and unforeseeably imperfect target discovery methodology did not constitute such an error,” the report stated. Despite the agency’s vast technical expertise, IPCO said that the issue affecting the software was not foreseeable. GCHQ was not the only offender among the UK intelligence community (UKIC), with MI5’s mishandling of the infamous Agent X case taking center stage in the report. Agent X was an anonymous MI5 informant whose real identity has never been publicly released. A secret inquiry by IPCO as well as the report revealed that MI5 managed Agent X despite knowing he was a violent misogynist obsessed with extreme violence. Lord Leveson said “the case of Agent X is as serious as anything I have dealt with as Commissioner,” after MI5 gave false evidence to the High Court and Investigatory Powers Tribunal to protect a foreign neo-Nazi informant who was under police investigation for abusing his partner, referred to publicly as “Beth.” ®
Source: The Register Security · 2026-10-30