SOCRadar Dark Web Team identified several underground posts, including an alleged 500GB Pataya Food data leak, an alleged Belgian military archive containing more than 2,700 files, and an alleged Chinese Housing Provident Fund database exposing 25.4 million records. Other posts detailed claimed DDoS attacks by Anka Team and an alleged sale of Super Administrator access to Vijay Sales’ internal systems.
Alleged Pataya Food 500GB Data Leak is Detected
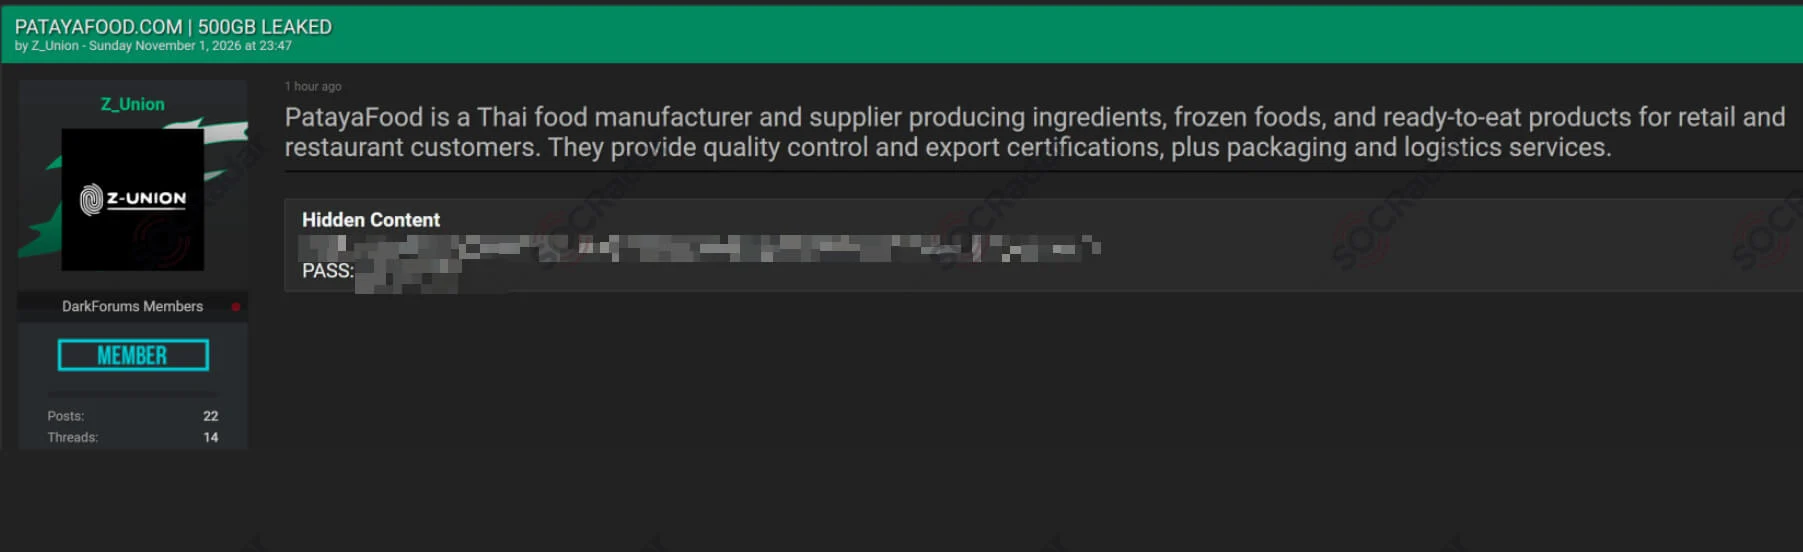
SOCRadar Dark Web Team detected a dark web post claiming to leak 500GB of data allegedly belonging to Pataya Food Industries, a Thai food manufacturer and supplier. The actor, operating under the alias Z_Union, shared a BitTorrent magnet link and password for accessing the purported dataset.
The company operates in food production and distribution, supplying ingredients, frozen foods, and ready-to-eat products. Although the specific contents of the archive have not been disclosed, the alleged exposure could involve sensitive corporate information, internal documents, or business records. The authenticity of the dataset and the extent of any compromise remain unverified.
Alleged Belgian Military Database Archive is Offered for Sale
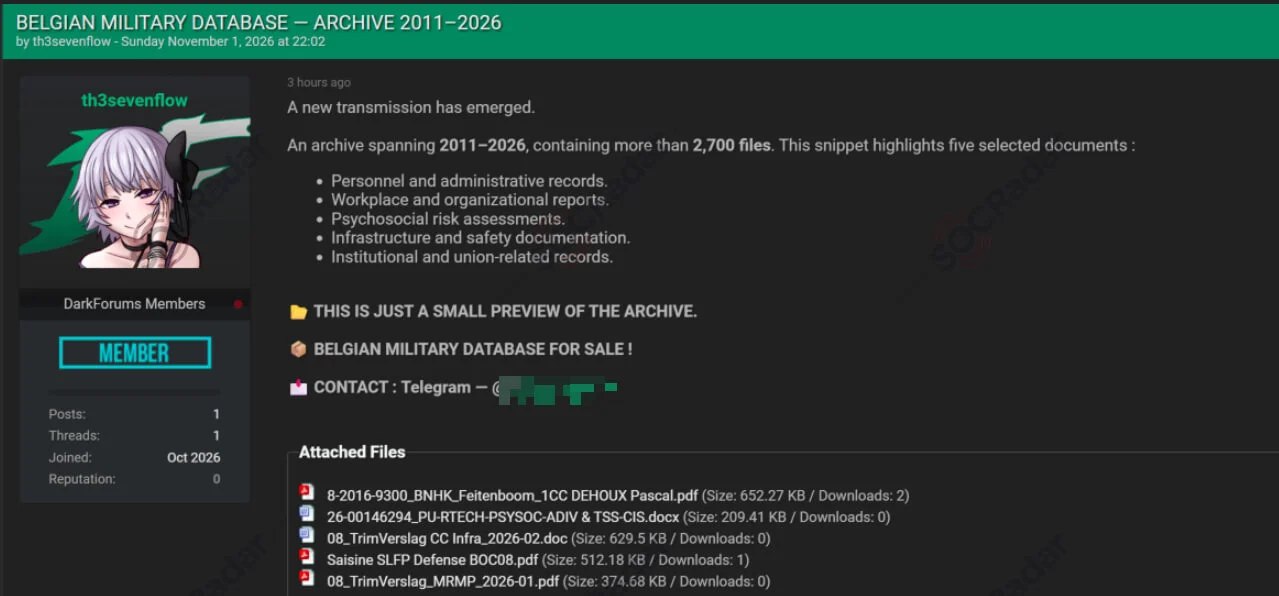
SOCRadar Dark Web Team identified a post advertising an alleged Belgian military database archive containing more than 2,700 files spanning 2011 to 2026. The seller, using the alias th3sevenflow, provided a preview of several documents and offered the complete archive for sale.
The advertised contents reportedly include personnel and administrative records, organizational reports, psychosocial risk assessments, infrastructure and safety documentation, and union-related files. If authentic, the exposure could reveal sensitive personnel information and internal operational details, potentially creating privacy and security risks for affected military personnel and institutions.
Alleged China Housing Provident Fund Leak Exposes 25.4 Million Records
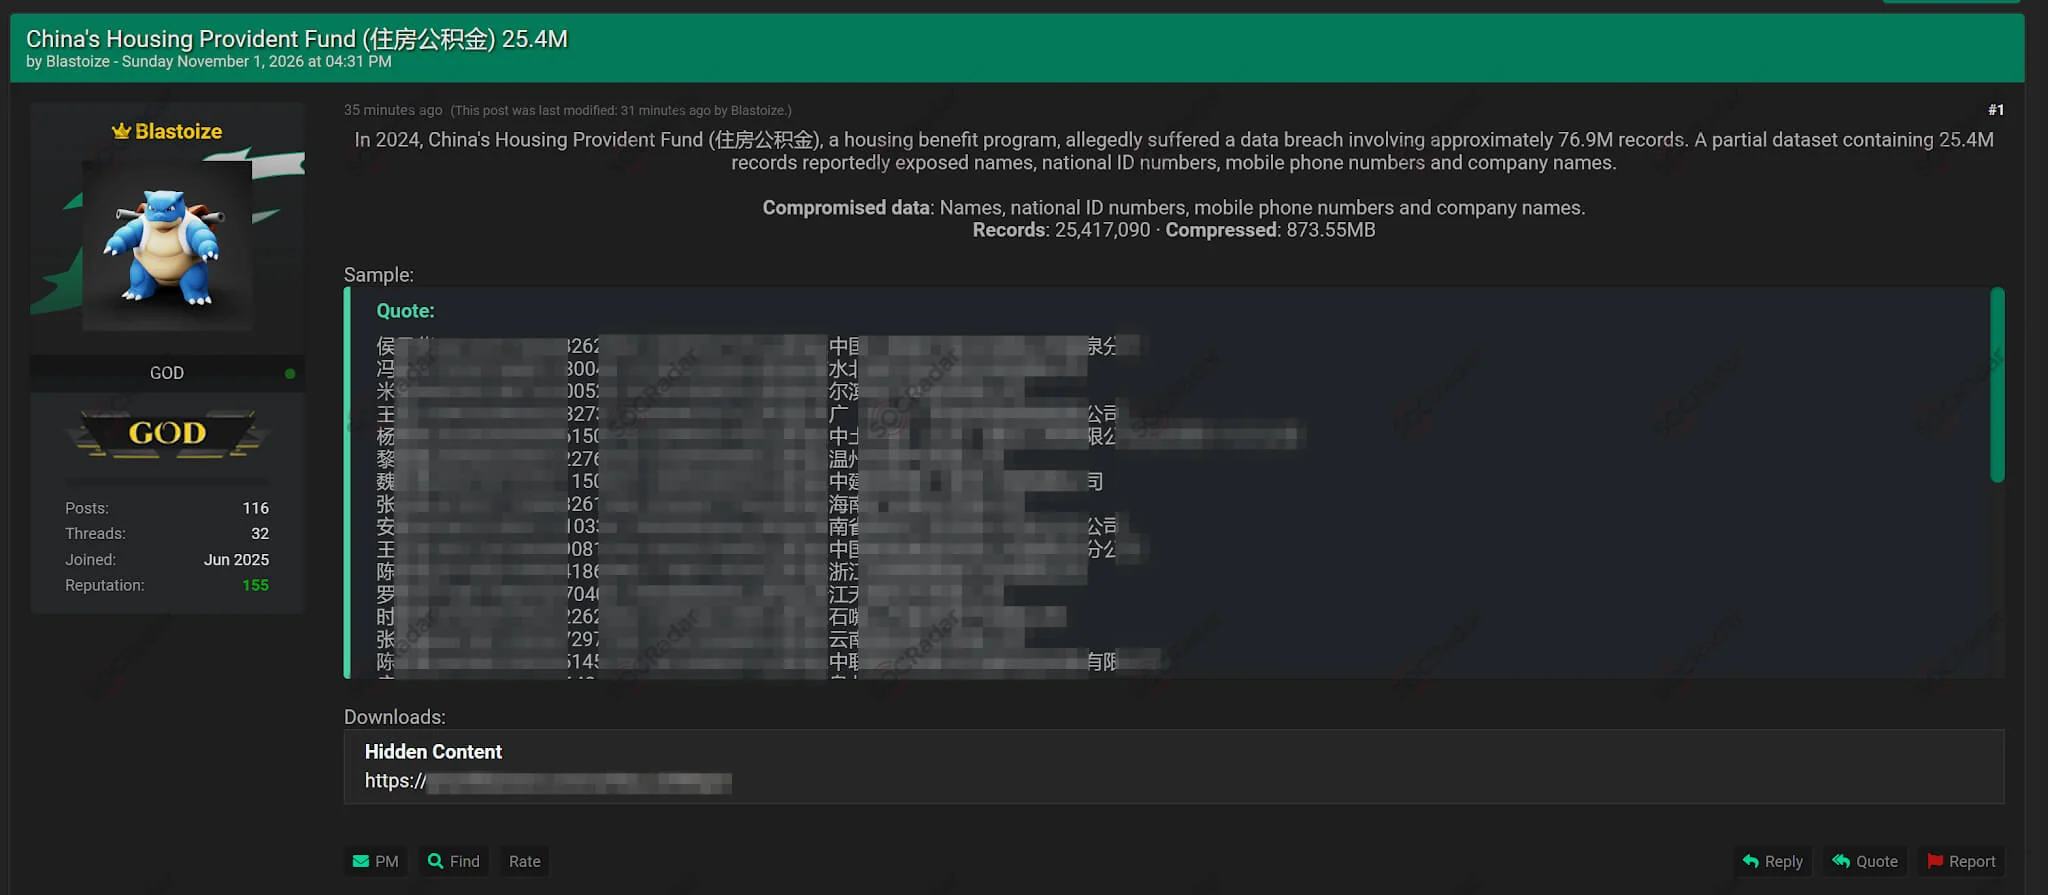
SOCRadar Dark Web Team detected a forum post claiming to release 25,417,090 records allegedly belonging to China’s Housing Provident Fund. The actor, identified as Blastoize, claimed the dataset originated from a larger breach involving approximately 76.9 million records in 2024.
The released archive reportedly contains names, national identification numbers, mobile phone numbers, and associated company names, with a compressed size of approximately 873.55MB. The seller provided sample records and a download link. If authentic, the exposure could facilitate identity theft, targeted phishing, and social engineering attacks against individuals whose personal information appears in the dataset.
Alleged Vercel Internal Database and Source Code Sale is Detected
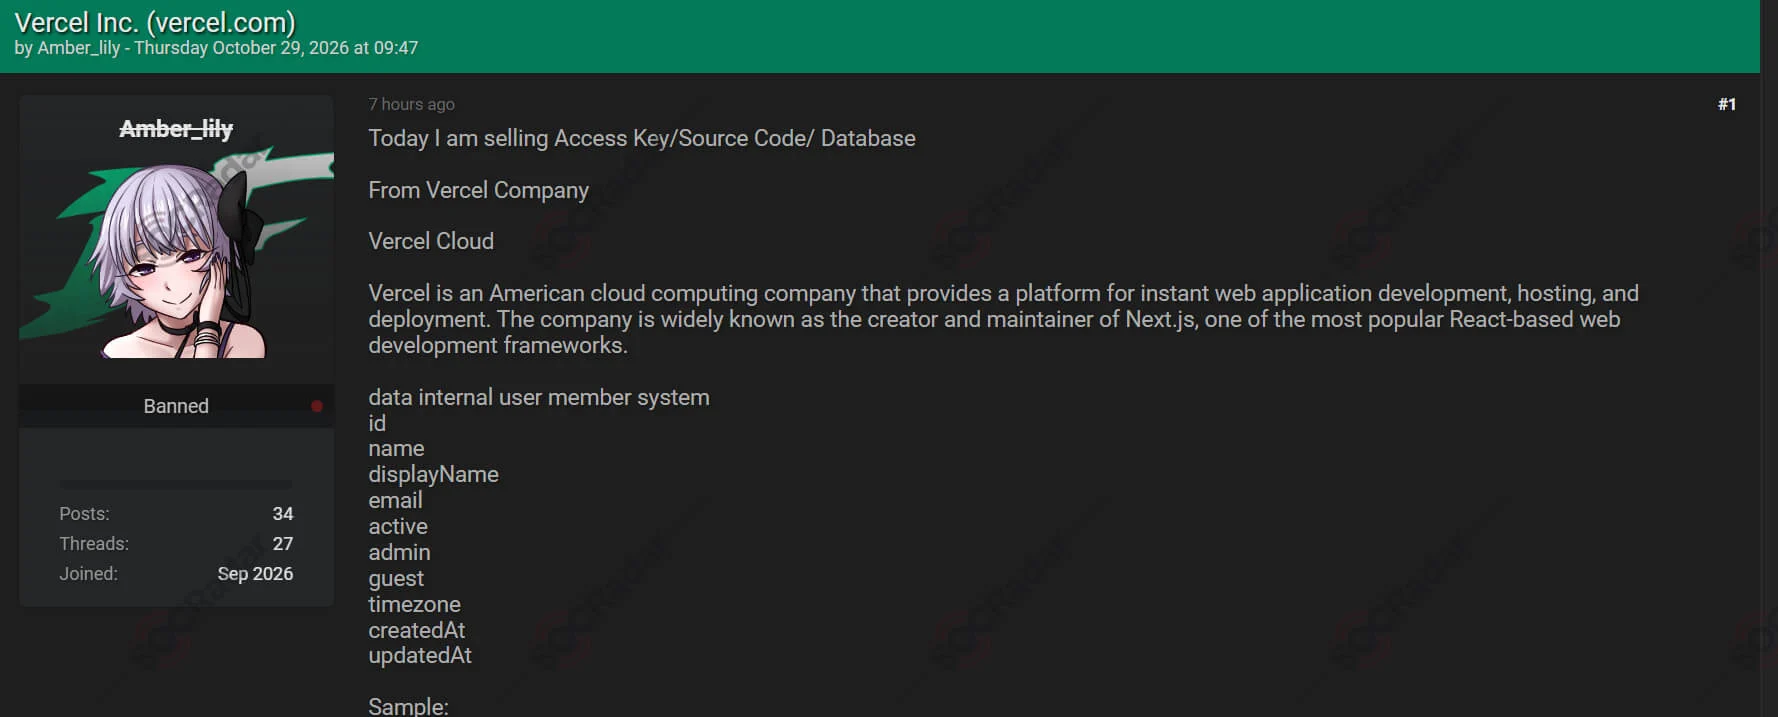
SOCRadar Dark Web Team detected a dark web post advertising an alleged Vercel internal database, source code, and access keys for sale. The threat actor, operating under the alias Amber_lily, claimed to possess sensitive information belonging to the U.S.-based cloud computing company, which provides web application hosting and deployment services and maintains the Next.js framework.
The actor shared sample records allegedly extracted from Vercel’s internal user management system, including names, corporate email addresses, account IDs, administrative privileges, account status, time zones, and activity timestamps. The authenticity of the dataset and claims involving source code and access keys remain unverified. If confirmed, the exposure could facilitate targeted phishing, unauthorized access to internal systems, and potential supply chain security risks.
Alleged Vijay Sales Super Administrator Access is Offered for Sale
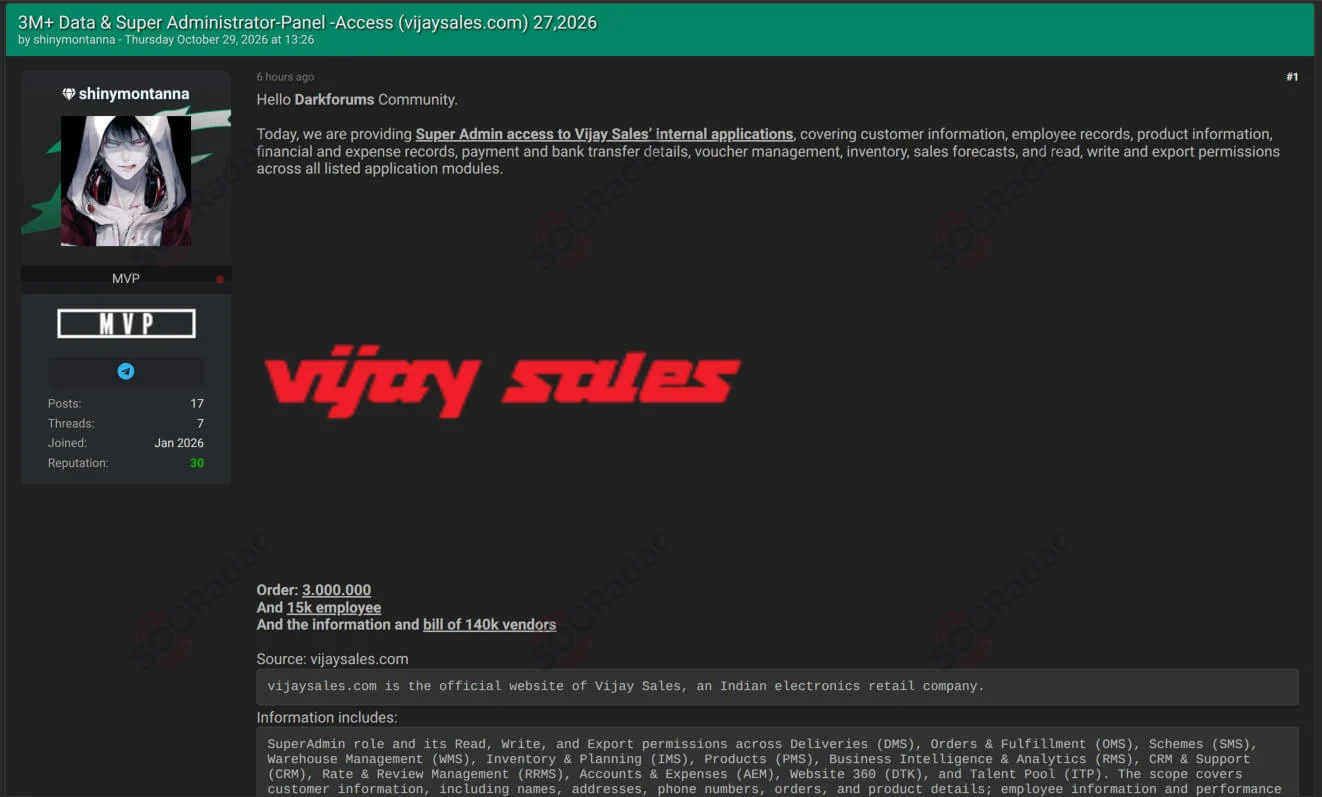
SOCRadar Dark Web Team detected a post advertising alleged Super Administrator access to Vijay Sales, an Indian electronics retailer. The seller, operating under the alias shinymontanna, claimed to possess access to internal business applications with read, write, and export permissions across multiple operational modules.
The listing reportedly covers approximately 3 million order records, 15,000 employee records, and information associated with 140,000 vendors. The advertised access extends to order fulfillment, inventory management, customer relationship management, financial records, and internal sales forecasts. The actor reportedly requested $25,000 for the access. If verified, the compromise could facilitate data theft, financial fraud, and unauthorized manipulation of business operations.
Powered by DarkMirror
Gaining visibility into deep and dark web threats can be extremely useful from an actionable threat intelligence and digital risk protection perspective. However, monitoring all sources is simply not feasible, which can be time-consuming and challenging. One click-by-mistake can result in malware bot infection. To tackle these challenges, SOCRadar’s DarkMirror screen empowers your SOC team to follow up with the latest posts of threat actors and groups filtered by the targeted country or industry.
Source: SOCRadar · 2026-11-02