T-Mobile’s new T-Mix plans deliver tons of extras ranging from streaming to mobile discounts, but there are some caveats to know.
Source: ZDNet Security · 2026-10-27
T-Mobile’s new T-Mix plans deliver tons of extras ranging from streaming to mobile discounts, but there are some caveats to know.
Source: ZDNet Security · 2026-10-27
Nathan Hamiel outlines potential SecOps horror in the AI midst, as core technical capabilities go the way of reading an atlas or remembering phone numbers.
Source: Dark Reading · 2026-10-27
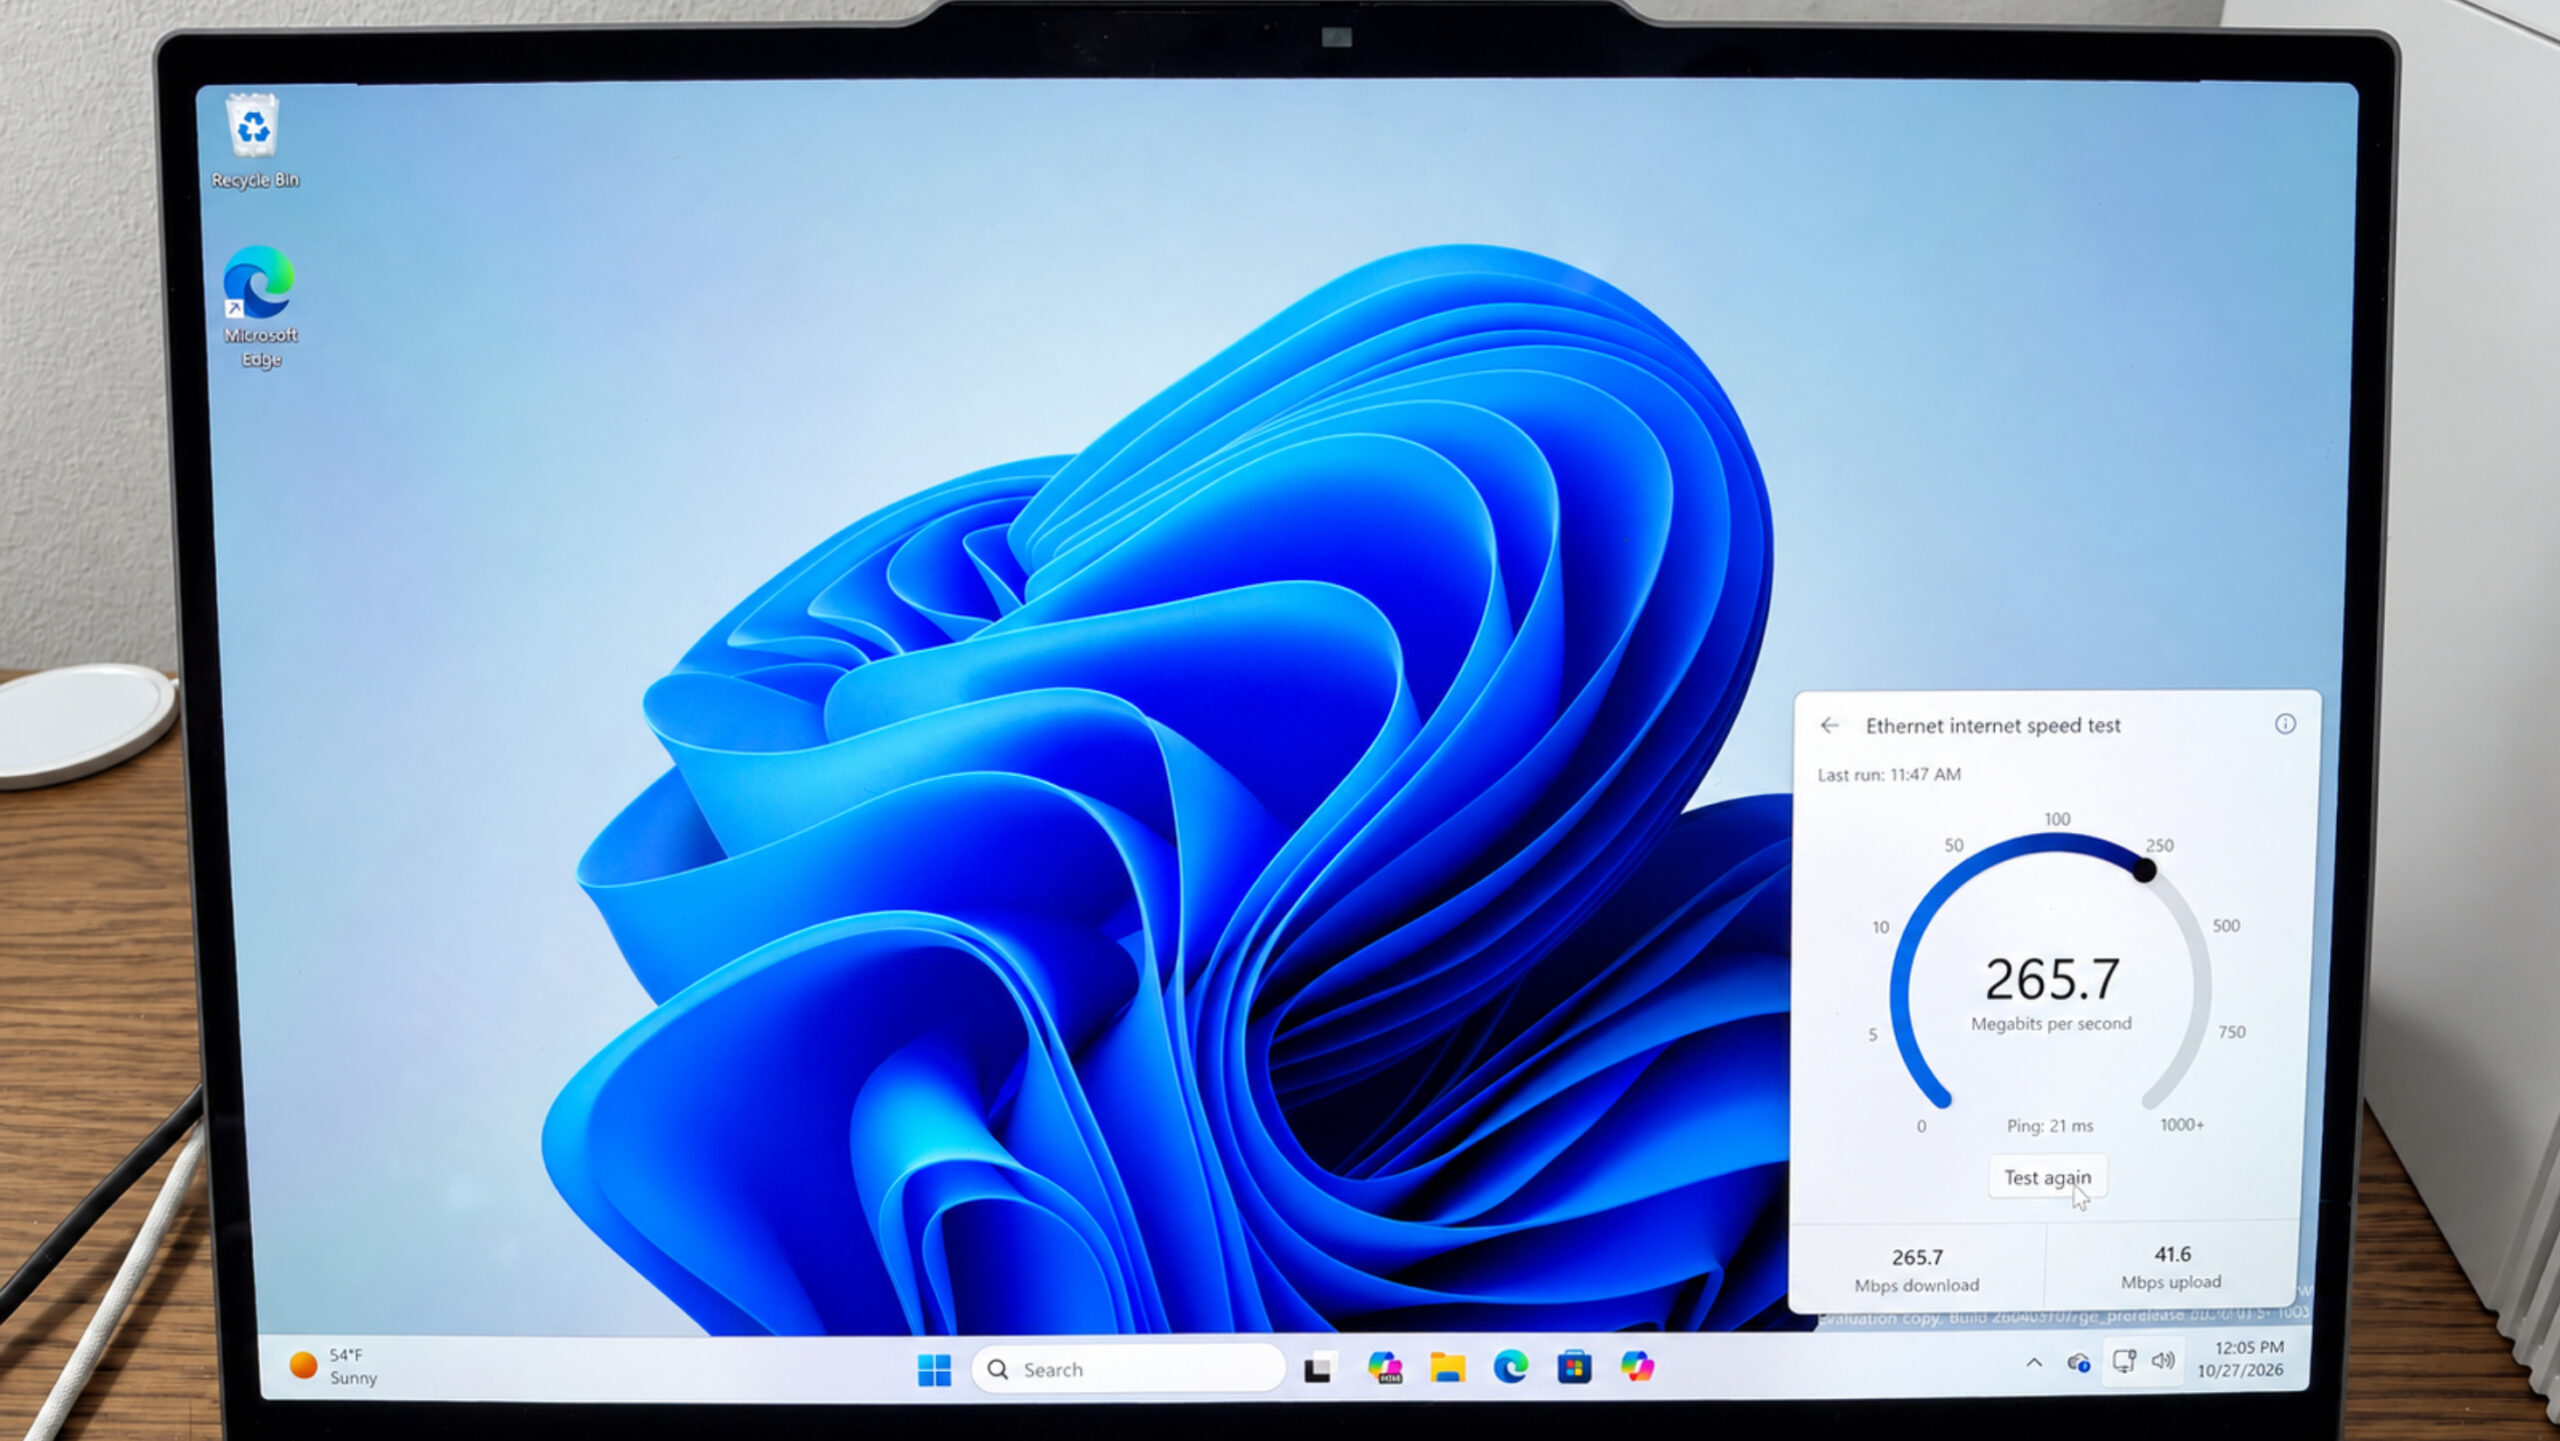
Available to Windows Insiders, the built-in tool measures your upload and download speeds over Ethernet or Wi-Fi.
Source: ZDNet Security · 2026-10-27
This new tool proves it’s still best to limit the info you share with chatbots.
Source: ZDNet Security · 2026-10-27
The Guardian has reported on new findings by the Citizen Lab and SHARE Foundation that a Serbian professor and prominent supporter of the country’s student movement was targeted with Pegasus spyware. The investigation also found that a Serbian prosecutor who investigated a scheme to help the Trumps build a tower in Belgrade was also targeted.
These discoveries follow the Citizen Lab’s earlier confirmation that a Serbian pro-democracy student activist’s device was infected with Pegasus spyware. At least 15 cases of Pegasus targeting have been identified ahead of Serbia’s October 25 national elections.
Source: Citizen Lab · 2026-10-27
The malware’s focus on AI tools expands the traditional infostealer playbook to expose a forest of AI sessions, sensitive business data, and developer infrastructure from a single compromised endpoint.
Source: Dark Reading · 2026-10-27
The University of New Mexico is working to restore systems following the incident, which has been claimed by the BYOD ransomware group
Source: Infosecurity Magazine · 2026-10-27
The University of New Mexico is canceling classes across the medicine, nursing, and pharmacy faculties for a second day amid continued efforts to recover from a “cybersecurity event.” The attack targeted the Health Sciences Center on Monday, the Uni revealed, forcing it to shut down systems, cancel appointments and clinics at UNM Health hospitals, and divert ambulances to healthcare facilities in nearby Albuquerque and Santa Fe. Hospital appointments and clinics return to normal today, although nonessential UNM Health Sciences Center staff are being asked to remain at home. “The University of New Mexico Health Sciences Center (HSC), which includes the UNM Health clinical delivery system, experienced a cybersecurity event Monday, Oct. 26, 2026,” the university said in a statement on Monday evening. “HSC information technology security teams immediately took steps to contain the event and protect the network. They also notified state and federal law enforcement and engaged external partners to assist with the investigation. “Leadership activated an Emergency Operations Center to coordinate the response and provide guidance to HSC employees, students, and UNM Health system frontline providers.” The university announced the attack at 1430 local time, immediately cancelling all remaining clinics and classes, dismissing everyone other than critical and clinical staff, and urging patients not to attend HSC facilities. It has not commented on the nature of the cyberattack, although that hasn’t stopped researchers from speculating about ransomware’s involvement. Rumors were fuelled by the newly assembled BYOD ransomware group claiming responsibility for the attack on Monday afternoon. It’s important to note that just because a purported ransomware group took credit for the attack, it does not mean they actually were responsible, nor does it mean they deployed a ransomware/locker payload as part of the attack. However, the group’s take on the digital raid is that it compromised 36,000 machines, “both [Active Directory] forests,” two Oracle databases, the personal data belonging to every student and employee, as well as internal emails and data from other systems. As Reg readers know, a cybercriminal’s word is never one to be trusted. Yet BYOD’s claims about breaching Trump Mobile’s customer database appear to have held up It was a bold debut, even for a ransomware crew: BYOD’s first named victim was the US president’s smartphone biz, with data allegedly leaked for all 3,615 customers. A rival group, EndZone, claimed a similar breach a week earlier, and some experts suggested the two could be one and the same. In May, the Trump Mobile was found leaking thousands of people’s data via a poorly secured website. The Trump Organization did not respond to our requests for more information in either of these cases. A UNM spokesperson declined to answer our additional questions, directing us back to its public statement. ®
Source: The Register Security · 2026-10-27
The University of New Mexico is canceling classes across the medicine, nursing, and pharmacy faculties for a second day amid continued efforts to recover from a “cybersecurity event.” The attack targeted the Health Sciences Center on Monday, the Uni revealed, forcing it to shut down systems, cancel appointments and clinics at UNM Health hospitals, and divert ambulances to healthcare facilities in nearby Albuquerque and Santa Fe. Hospital appointments and clinics return to normal today, although nonessential UNM Health Sciences Center staff are being asked to remain at home. “The University of New Mexico Health Sciences Center (HSC), which includes the UNM Health clinical delivery system, experienced a cybersecurity event Monday, Oct. 26, 2026,” the university said in a statement on Monday evening. “HSC information technology security teams immediately took steps to contain the event and protect the network. They also notified state and federal law enforcement and engaged external partners to assist with the investigation. “Leadership activated an Emergency Operations Center to coordinate the response and provide guidance to HSC employees, students, and UNM Health system frontline providers.” The university announced the attack at 1430 local time, immediately cancelling all remaining clinics and classes, dismissing everyone other than critical and clinical staff, and urging patients not to attend HSC facilities. It has not commented on the nature of the cyberattack, although that hasn’t stopped researchers from speculating about ransomware’s involvement. Rumors were fuelled by the newly assembled BYOD ransomware group claiming responsibility for the attack on Monday afternoon. It’s important to note that just because a purported ransomware group took credit for the attack, it does not mean they actually were responsible, nor does it mean they deployed a ransomware/locker payload as part of the attack. However, the group’s take on the digital raid is that it compromised 36,000 machines, “both [Active Directory] forests,” two Oracle databases, the personal data belonging to every student and employee, as well as internal emails and data from other systems. As Reg readers know, a cybercriminal’s word is never one to be trusted. Yet BYOD’s claims about breaching Trump Mobile’s customer database appear to have held up It was a bold debut, even for a ransomware crew: BYOD’s first named victim was the US president’s smartphone biz, with data allegedly leaked for all 3,615 customers. A rival group, EndZone, claimed a similar breach a week earlier, and some experts suggested the two could be one and the same. In May, the Trump Mobile was found leaking thousands of people’s data via a poorly secured website. The Trump Organization did not respond to our requests for more information in either of these cases. A UNM spokesperson declined to answer our additional questions, directing us back to its public statement. ®
Source: The Register — Security · 2026-10-27
Apple’s newest Mini is the first iPad ever with an IP67 rating for dust and water resistance.
Source: ZDNet Security · 2026-10-27