Tag: Technology

  • Ransomware claim: Digital Triumph (N0n)

    telecommunications services · Malaysia | Employee payroll records with names, national identity numbers and wages, statutory filings 2016 to 2025; Audited financial statements, tax filings and company bank account numbers; 2,552 customer invoices and delivery orders; The full customer service data room covering 309 organizations including banks, an embassy and government offices; The CRM customer database and the company mail archive, 8,700+ verified business emails with customer correspondence | [NOT PAID — EXPOSED]

    • Group: N0n
    • Country: MY
    • Sector: Technology
    • Discovered: 2026-10-31 07:58 UTC
    • Attack date: 2026-10-31 07:57 UTC

    This entry reflects a claim published by an extortion group and collected by a public tracker. It has not been independently verified.

    Source: ransomware.live — Recent Victims · 2026-10-31

  • Ransomware claim: CommTank (thegentlemen)

    commtank.com CommTank Inc is a US storage tank contractor founded in 1997 in Winchester, Massachusetts, specializing in installation, removal, inspection and maintenance of underground and aboveground storage tanks across New England and the Mid-Atlantic. With 50 to 100 employees and estimated revenue of 10 to 25 million dollars, it serves government facilities, hospitals, schools and industrial clients across 8 states. Its services cover the full tank lifecycle including UST and AST installation, leak testing, cathodic protection, soil remediation and emergency spill response. Led by founder Rick Connolly, it holds EPA, MA DEP, CT DEEP and NFPA certifications and runs its own field crews without subcontracting core work. It also provides Phase I and II environmental site assessments and SPCC compliance planning. The company has built a niche in high-barrier tank services requiring specialized licensing and regulatory expertise.

    • Group: thegentlemen
    • Country: US
    • Sector: Technology
    • Victim website: commtank.com
    • Discovered: 2026-10-31 07:19 UTC
    • Attack date: 2026-10-30 11:32 UTC

    This entry reflects a claim published by an extortion group and collected by a public tracker. It has not been independently verified.

    Source: ransomware.live — Recent Victims · 2026-10-31

  • Ransomware claim: NOVADATA (thegentlemen)

    novadata.com.ar NOVADATA S.A. is an Argentine IT integration group founded in 1994 in Buenos Aires, comprising Novadata, Net Service and Compañía Global de Servicios with 130 plus certified professionals. It provides IT infrastructure, business continuity, AI, pay-per-use HPE GreenLake, microinformatics and 24/7 Service Desk services to major corporations across Argentina. It holds HPE Platinum, Microsoft Gold, Cisco Silver, VMware Enterprise and Symantec Gold partner certifications, adding Huawei Enterprise Authorized Reseller status in 2026. Major clients include Bayer, Veolia, La Anónima, Petrobras, Citibank, Roche and Bimbo, many with over 10 years of partnership. The group completed a financial restructuring agreement from 2014, declared fulfilled by court in March 2026. Recent strategic moves include an AI alliance with AYI Group, Fortinet cybersecurity training and launch of Novadata GREEN IT asset disposition services.

    • Group: thegentlemen
    • Country: AR
    • Sector: Technology
    • Victim website: novadata.com.ar
    • Discovered: 2026-10-31 07:19 UTC
    • Attack date: 2026-10-30 11:39 UTC

    This entry reflects a claim published by an extortion group and collected by a public tracker. It has not been independently verified.

    Source: ransomware.live — Recent Victims · 2026-10-31

  • Apple notifications alert victims in 99 countries about mercenary spyware infections

    Apple has sent new notifications of mercenary spyware infections to almost 100 countries, with recipients including journalists and documentary filmmakers.

    “Today’s notification is being sent to targeted users in 99 countries, and to date we have notified users in over 150 countries in total,” the company said. “The extreme cost, sophistication, and worldwide nature of mercenary spyware attacks make them some of the most advanced digital threats in existence today. As a result, Apple does not attribute the attacks or the notice you’re receiving to any specific attackers or geographical regions.”

    Apple didn’t immediately respond to a request for comment Friday about the countries targeted. Researchers and groups that work on spyware said the notifications were significant, however.

    “This again promises to be an important set of notifications with a bunch of cases, based purely on what we see publicly,” said John Scott-Railton, senior researcher at The Citizen Lab at the University of Toronto. He also posted on social media about how potential victims could defend themselves, warning people to be cautious about companies that offer paid solutions to spyware infections.

    He cautioned that the lack of notification doesn’t rule out an infection. The steps Apple recommends, which Scott-Railton seconded, were to enable Lockdown Mode and to get in touch with the digital rights group Access Now.

    “The number of Apple threat notifications we are seeing from countries around the world indicates that the fight against the scourge of spyware abuse is far from over,” said Natalia Krapiva, senior tech-legal counsel with Access Now. “While we have increased our capacity to investigate spyware abuse, and companies like Apple have done a lot to notify and protect people from it, repressive states continue to use these powerful surveillance technologies, including against civil society actors and opposition figures.”

    Apple sent its last major batch of notifications in August. The notifications frequently lead to victims approaching Access Now, The Citizen Lab and other groups seeking further assistance and prompting deeper investigations.

    The notifications come shortly before the final rounds of negotiations over industry standards for commercial hacking tools being developed under the voluntary Pall Mall Process. The industry guidelines follow an earlier set of guidelines catered to governments.

    “The states that will ultimately adopt these guidelines must come to terms that the current system is not working, and that the spyware industry must face some real consequences for the uncontrolled sale of these tools and refusal to curb the abuses,” Krapiva said.

    Source: CyberScoop · 2026-10-30

  • Leaked DHS employee archive, Icepick, faces challenges to stay online

    A company working on behalf of the Department of Homeland Security sought to cut off online access to information on more than 41,000 employees that hacktivists said they obtained from a database breached at DHS.

    A search tool for the database, named Icepick, went offline for a spell before coming online again Thursday under a different registrar.

    Icelandic hosting company FlokiNET said Thursday that it received a request from DHS contractor ZeroFox to remove the data, which it refused.

    “By mid-morning, icepi.cx no longer resolved. Its registrar, CentralNic, had placed the domain on serverHold,” FlokiNET said in a blog post. “Our refusal kept nothing online. The request that decided the outcome to take the site down was not the one sent to us. A registrar reached the opposite conclusion the same morning, published nothing, and a global audience lost access to the site. In the meantime the site is online again under a domain from a different registrar.”

    CentralNic and ZeroFox did not immediately respond to requests for comment Thursday.

    DHS said late Wednesday that it was working to protect its employees against any breach.

    “DHS is aware of a potential breach and is actively working to address the situation swiftly and effectively,” a spokesperson said. “We take all security threats against our employees and officers seriously and will work to ensure all are properly protected. We will update the public when more information is available.”

    The social media site Bluesky was also blocking links to the archive because it shared people’s contact information without their permission, although a company official said changes were coming because the wording had identified it as a malicious link.

    FlokiNET said it refused the ZeroFox request that mislabeled the archive as part of a doxxing campaign.

    “Doxxing publishes private details about private people so that others can find them at home. Icepick publishes work identities of government employees,” it wrote. “Who they work for. What their role is. How they can be reached in that role. The information describes people in the exercise of public authority, not in their private lives. Federal officers carrying out an enforcement programme are not private individuals while they are carrying it out.”

    “The public has a legitimate interest in knowing who is doing that work, under whose authority, and in which office,” it continued. “Journalists cannot report on an agency whose personnel are structurally unknowable.”

    ZeroFox said that regardless of that, the data made it possible to locate people whose information was in the database.

    “The request does not depend on who the listed individuals are or what their duties are,” ZeroFox wrote to FlokiNET. “It rests on two facts: the data was stolen, and it is personal data that identifies and locates real people.”

    Source: CyberScoop · 2026-10-29

  • Transferring Unused IPv4 Addresses in Asia Pacific: The Complete APNIC Playbook

    Understand APNIC IPv4 transfer rules, buyer requirements, fees and approval steps, with helpful checks to assess address blocks before completing a transaction.

    Source: HackRead · 2026-10-29

  • Next-gen privacy protocols: WireGuard vs OpenVPN vs Shadowsocks

    Compare WireGuard, OpenVPN and Shadowsocks for speed, privacy, enterprise access and censorship resistance, including VPN tunnels differ from encrypted proxies.

    Source: HackRead · 2026-10-28

  • Marissa Mayer Can’t Keep Pretending ‘Gender Doesn’t Matter’

    Marissa Mayer Can’t Keep Pretending ‘Gender Doesn’t Matter’


    Marissa Mayer Can’t Keep Pretending 'Gender Doesn't Matter'

    In Sunday’s edition of the New York Times, Marissa Mayer, former president and CEO of Yahoo, told her interviewer something so absurd it’s since gone viral. 

    Struggling with the “impossible task” of naming three things that she loves about her own 10 year old daughter, the New York Times reports, Mayer asked the AI assistant she just launched to do that thinking for her. It delivered the perfect answer, Mayer said: “It came back and was like, your daughter is empathetic, creative and an animal lover.” Everyone is piling onto that absurd anecdote right now, rightfully so. What she has to say about gender in tech, however, is more out of touch than that.

    Saying sensational things on the record — especially knowing that the reporter will not be able to resist using such a shocking story as the lede — is a savvy strategy. For someone as influential as Mayer, telling the list story is transparently a result of years of media training. Mayer is selling her new app, Dazzle, which accesses your camera roll and analyzes your life based on the photos you take. It’s disturbing to see her talk about relinquishing basic cognitive skills like “plan a birthday party” to AI. But the rest of the story gets into something Mayer has talked about for more than a decade: “the gender card,” as she’s called it. 

    “I never play the gender card,” she told Steven Levy in a 2015 interview. “The moment you play into that, it’s an issue. […] In technology we live at a rare, fast-moving pace. There are probably industries where gender is more of an issue, but our industry is not one where I think that’s relevant.” She repeats similar sentiments in Sunday’s NYT interview.

    The height of Mayer’s career coincided with the girlbossification of everything, during the Lean In era, when Notorious RBG and “well behaved women rarely make history” mugs were everywhere. She’s been asked about gender in tech one million times, and has mostly dismissed it. But a decade after the tech girlboss reigned, her thoughts on this haven’t seemed to evolve much. 

    Later in the NYT piece, she brushed off the notion that gender has any bearing on who gets to participate in the tech industry. She also brushes off a question about bias baked into AI models, something that’s been studied and proven extensively, and instead names female AI executives like Fei-Fei Li as the reason well-documented bias doesn’t exist. She asserts that passion overrides gender, as if just being “passionate” enough erases decades of women’s experiences in the tech workforce.

    “To me, gender fades into the background. I talk about passion as a gender neutralizing force,” she told the NYT. “If you’re excited about something, gender doesn’t matter.”

    Meanwhile, male figureheads of the AI industry are out here posting slop videos about sperm on main. Half of women in tech leave the industry by 35, earn 84 cents to their male counterparts’ dollar, and women founders receive half the amount of funding that male founders do.

    Earlier this month, event organizers canceled one of the biggest gatherings of women and non-binary technologists, the Grace Hopper Celebration. “Unlike past events, this year, both individual registrations and sponsorship commitments came in significantly below our expectations and, ultimately, below the level needed to cover critical operating expenses,” the organizers wrote in a statement. Bloomberg reported that this comes after years of declining attendance, with around 15,000 people attending in 2025, making it the fewest since 2016. 

    In 2023, GHC attendees reported standing in lines for hours to talk to recruiters, being shoved, harassed, and cut in front of by the hundreds of men who’d suddenly flooded the conference. “They trampled over attendees, shoved their way into the recruiter’s booth to wave their resumes in front of their faces, verbally assaulted attendees, and physically pushed and shoved attendees in line,” one attendee said. 

    After the GHC 2026 cancellation was announced, Kayley Seow, a tech worker who was at the 2023 conference, contacted me to talk about what it meant to her. She said she felt “pretty shattered” when she heard the conference wouldn’t happen this year. “GHC is such a pillar of the community that you don’t expect to fall, or in this case, not run. Despite its flaws, it continues to be an important space for people hoping to get into tech and those already in it. I’d been recommending it to every undergrad or woman technologist to attend.” There are other, similar conferences held around the country, but GHC is hard to recreate, Seow told me. “Other organizations exist but they operate virtually, there’s events here and there in the Bay, but it’s impossible to find something as concentrated as GHC.” 

    The people she knows who are most affected are current undergrads who planned to go to GHC to connect with recruiters, find internships, and land graduate jobs, Seow said. “They’re disappointed, and a little scared, since it’s October and we’re coming up on the end of internship recruiting season, especially for the international students who were hoping to talk to the bigger companies at GHC that have the resources to take on international students as interns.” It’s still unclear whether there will be a conference in 2027.

    GHC’s cancellation this year follows a string of blows to organizations that support women technologists. Women Who Code, a nonprofit that awarded more than $3.5 million in scholarships and supported a community of 360,000 members, shut down in 2024 after 11 years, citing funding issues.  

    Things are very different today than they were when Mayer was the first-ever pregnant CEO of a Fortune 500 company. In 2025, at the direction of President Donald Trump’s executive order “Ending Radical and Wasteful Government DEI Programs and Preferencing” and other orders, civil servants across the federal government from NASA to the Social Security office and the CDC had to drop everything to scrub mentions of diversity, equity and inclusion from their systems. This wasn’t just symbolic or semantic. The National Institutes of Health terminated billions of dollars worth of nearly 2,300 federal research grants, cuts that disproportionately affected women and early career researchers. Led entirely by inexperienced men in their early 20s and spearheaded by Elon Musk, the now-defunct Department of Government Efficiency canceled funding that would have advanced potentially lifesaving research projects focused on pregnancy and reproductive health, chronic illness, and vaccine safety for women. The damage done by DOGE cuts to the advancement of science and technology that would have been done by women and would have improved women’s lives around the world is immeasurable and widespread; it’s hard to imagine believing gender plays no role in STEM today in light of what we have seen under the Trump administration over the last year and a half, especially.

    But in a way, Mayer is right: Drinking one’s own Kool-Aid is a non-gendered issue. Earlier this year, Sam Altman suggested AI generating podcasts to interact with your kids about their days and got similarly roasted for a week straight. He deserved it, and so does she.

    Source: 404 Media · 2026-10-27
  • Cybersecurity CEO Indicted for Allegedly Scamming Millions From Ransomware Victims

    Cybersecurity CEO Indicted for Allegedly Scamming Millions From Ransomware Victims

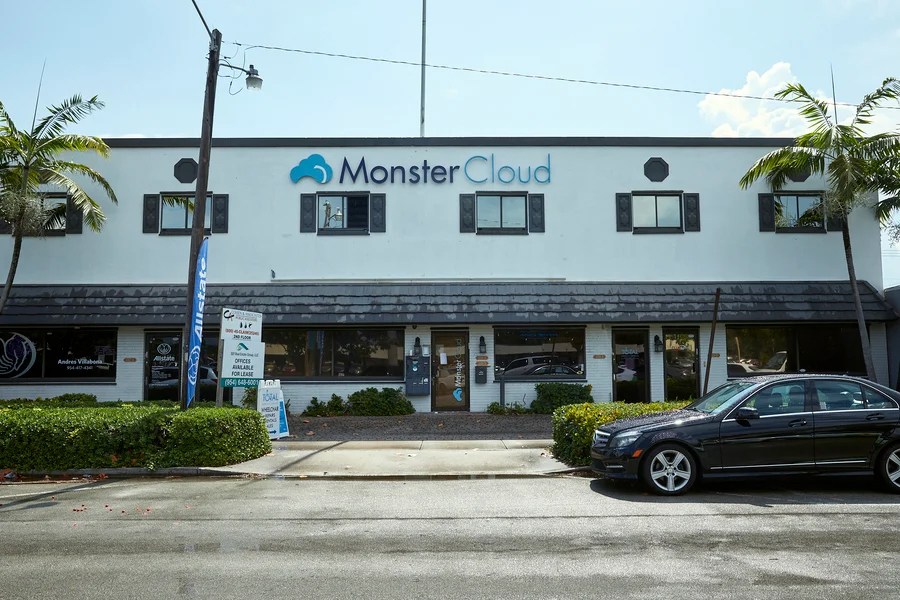
    Palm trees and green hedges grow in front of a white two-story building with a sign that reads MonsterCloud.
    A federal grand jury indicted Zohar Pinhasi last month for allegedly defrauding clients of his ransomware data recovery business, MonsterCloud. Jeffery Salter, special to ProPublica

    A Florida man who was the subject of a 2019 investigation by ProPublica was indicted last month on federal charges that he defrauded clients of his ransomware data recovery firm. 

    According to the Justice Department, the man, Zohar Pinhasi, told customers he could recover their encrypted files without having to pay hackers, when, in reality, he paid the ransom and charged victims a hefty fee on top.

    The indictment mirrors the findings from ProPublica’s 2019 article “The Trade Secret,” which centered on Pinhasi and his scheme. The outlet found that the ransomware victims were being harmed twice: once by the hackers, who locked their targets’ files and demanded ransom, and a second time by MonsterCloud, Pinhasi’s Florida-based data recovery firm, which misled its clients about not paying ransoms.

    “By falsely claiming to decrypt ransomware without paying off the ransomers, the defendant re-victimized his clients while extracting a hefty profit for himself,” U.S. Attorney Joseph Nocella said in an Oct. 7 press release. “Our Office will vigorously prosecute ransomware attackers who prey on Americans from across the world and those who cynically profit from their criminal activity.”

    When ProPublica published its story in 2019, ransomware was growing into one of the world’s most pervasive cyberthreats. Hackers locked the data of governments, schools and businesses, holding the decryption key for a ransom payment, which they usually demanded in bitcoin and other types of difficult-to-trace cryptocurrency. 

    ProPublica’s reporting focused on how U.S. industries, from data recovery firms like MonsterCloud to insurance giants that cover ransom payments, all fueled the extortion economy. Ransomware remains a widespread threat today, and the threat to national security has grown as hackers linked to hostile foreign governments are believed to use ransomware as a cover for espionage. The prevalence of AI tools is also making it easier for attackers to spread ransomware.

    Pinhasi, who went by the alias Zack Green, told ProPublica in 2019 that MonsterCloud never promised clients that their data will be recovered by any particular method. “How we do it, it’s our problem,” he told ProPublica. “You will get your data back. Sit back, relax and enjoy the ride.” He called MonsterCloud’s data recovery methods a “trade secret.”

    Pinhasi hung up when reached on his cellphone this month. A message left with a representative at MonsterCloud’s office phone number and a message left with his attorney were not returned. A spokesperson for the U.S. Attorney’s Office said Pinhasi pleaded not guilty to the federal charges.

    In its 2019 investigation, ProPublica interviewed MonsterCloud’s clients and ransomware experts and found that in certain cases the firm must have paid ransoms on behalf of clients. MonsterCloud’s services were particularly popular with local law enforcement agencies, who are loath to engage with or pay criminal hackers. Several interviewed by ProPublica at the time said they chose MonsterCloud to help them recover from ransomware because they believed the firm would never pay a ransom.

    Pinhasi, who described himself to ProPublica as a former IT security intelligence officer for the Israeli military, said in 2019 that MonsterCloud handled up to 30 calls a day and had about 20 employees in South Florida as well as extensive global contacts. 

    Federal investigators found that, over the course of the scheme, Pinhasi allegedly charged clients more than $19 million and paid more than $8 million in ransom payments. In one example, Pinhasi made a ransom payment of about $8,200 but charged the client about $150,000. If convicted, he faces up to 20 years in prison.

    In the Justice Department’s October press release, an FBI official said Pinhasi had “turned the victim’s crisis into his own profit center. This deception is unacceptable, and the FBI is committed to ensuring accountability for those who choose to victimize the very people who trusted them for help.”

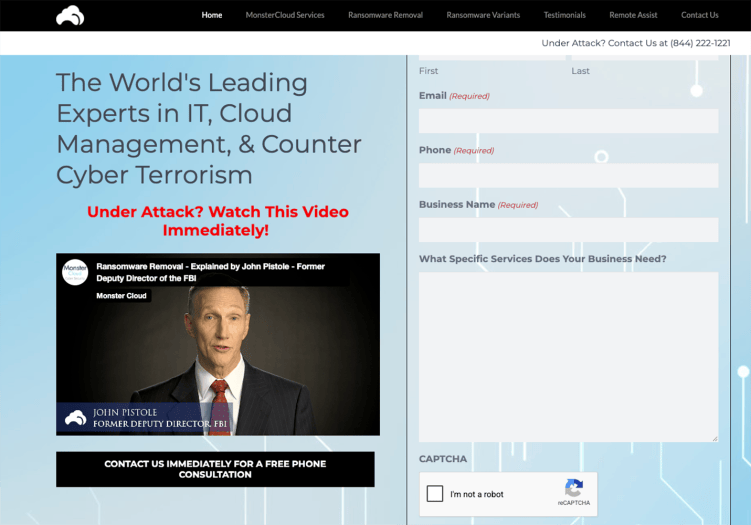
    The Justice Department did not address ProPublica’s 2019 finding that one of the FBI’s own was among Pinhasi’s associates at MonsterCloud. John Pistole, a former deputy director of the FBI under Robert Mueller, was prominently featured in a promotional video on MonsterCloud’s homepage. “Police departments, government agencies, hospitals, small business and Fortune 500 firms trust MonsterCloud to help recover from attacks and protect against new ones,” Pistole said in the video. “MonsterCloud’s proprietary technology and expertise protects their professional reputations and organizational integrity.”

    Pistole was not mentioned by name in the Pinhasi indictment.

    In 2019, Pinhasi touted MonsterCloud’s ties to law enforcement as evidence of its integrity. Pistole, who also headed the Transportation Security Administration under President Barack Obama, was listed on MonsterCloud’s website as the only member of its “Cyber Security Advisory Council.” 

    Pistole did not respond to a request for comment for this story. In a 2019 interview, he said he became acquainted with Pinhasi after MonsterCloud reached him through a speaker’s bureau and that MonsterCloud paid him indirectly through that group. He said Pinhasi scripted his testimonial and that he was well aware that in most cases — including MonsterCloud’s — the only way to decrypt data locked by ransomware is to pay the hackers. “That’s the business model as I understood it,” Pistole told ProPublica at the time. “Based on my experience and knowledge, ransom is paid and they facilitate the best practices moving forward.”

    A spokesperson for the U.S. Attorney’s Office declined to comment on Pistole’s connection to MonsterCloud.

    A webpage with the words: “The World’s Leading Experts in IT, Cloud Management, & Counter Cyber Terrorism. Under Attack? Watch This Video Immediately!” A video appears showing a man with short cropped hair wearing a suit and tie with the caption: John Pistole, Former Deputy Director, FBI.
    John Pistole, a former deputy director of the FBI under Robert Mueller, was prominently featured in a promotional video on MonsterCloud’s homepage. Screenshot by ProPublica

    Source: ProPublica · 2026-10-26

  • Giant Crypto Super PAC Funnels Big Money to Former Trump Official’s Firm to Support… Democrats?

    Giant Crypto Super PAC Funnels Big Money to Former Trump Official’s Firm to Support… Democrats?

    The Fellowship PAC, a super PAC fueled by crypto industry cash that once lavished praise on Donald Trump, is making a surprising pivot.

    When it was founded a year ago, news reports suggested that Fellowship PAC would concentrate on supporting Republicans.

    Since June, however, the only candidates Fellowship PAC has spent on have been Democrats, including those who have criticized the president’s meme coin, and it is getting help from a former Trump administration official’s company.

    Since June, the only candidates Fellowship PAC has spent on have been Democrats.

    Fellowship PAC funneled $600,000 since this summer through a firm co-founded by former Trump crypto adviser Bo Hines to help reelect Rep. Ritchie Torres of New York; Rep. Maggie Goodlander of New Hampshire; and Sen. Mark Warner of Virginia. The Democrats are considered crypto allies, and none of them are facing competitive elections this fall.

    All those advertising dollars have been spent through a vendor called Nxum Group, which was co-founded by Hines, a former Republican congressional candidate and Trump administration official.

    Hines did not return a request for comment, and it is not known whether he has personally been involved in the Nxum Group’s work on behalf of Fellowship PAC. In congressional races in 2022 and 2024, he presented himself as a Trump-loving MAGA acolyte.

    There is a thick web of ties between Hines, Fellowship PAC, and one of the biggest players in the crypto industry, a stablecoin company called Tether.

    Before Trump’s election, Hines was involved in promoting a Trump-themed meme coin that made a handful of investors millions before plummeting in value. After Trump’s election, the president tapped Hines to serve as the head of the White House Council of Advisers on Digital Assets. In that role, Hines helped pass a law that created stablecoin regulations that benefited Tether.

    As Hines served in the Trump administration, Tether was paying money to the firm that Hines co-owned, Nxum Group, according to a report last week in the Wall Street Journal. Nxum Group told the news outlet that Hines had no involvement in the company’s business dealings with Tether during that time. Hines said in a June 2025 ethics disclosure that he had only a “passive investment interest” in the company.

    Hines left the Trump administration in August 2025 and, a month later, Tether announced that he would serve as the CEO of its U.S. branch.


    Related

    Who’s Spending in Your Congressional Election? We Tracked the Front Groups Fueling the 2026 Midterms.


    Tether also has ties to Fellowship PAC. The newly created Fellowship PAC received a $10 million donation in January from Tether’s U.S. banking firm, Cantor Fitzgerald. In April, Fellowship PAC announced that Tether’s vice president of regulatory affairs would serve as its chair.

    Although it launched with a splash last year by claiming that it had a $100 million war chest, the PAC has never reported as much as that in official campaign finance disclosures. The PAC’s last receipt was in January, and its cash on hand dwindled to $250,000 as of October 14.

    Throughout the midterm elections, Fellowship PAC has leaned heavily on Nxum Group to spend advertising dollars on various congressional races.

    Fellowship PAC spent exclusively on Republicans until its first expenditure on behalf of a Democrat, Torres, in June. That spending coincided with public polls showing increasingly dismal fortunes for Republicans in the midterm elections. Since then, the PAC has spent exclusively on Democratic candidates.

    Torres’s and Warner’s campaigns did not respond to requests for comment. Goodlander’s campaign said she had nothing to do with the $150,000 that Fellowship PAC spent on digital advertising in her race. The money, the PAC disclosed in filings, had been routed through Nxum Group on August 31.

    “Congresswoman Goodlander has been one of the strongest advocates in Congress for cracking down on Big Tech and crypto profiteering and getting dark money out of politics,” her campaign said in a statement. “Like all campaigns, we’re legally barred from coordinating with outside groups like these, so you’d need to ask them why they’re spending in this race.”

    The PAC did not return a request for comment.


    Related

    Crypto Darling Gillibrand’s 11th-Hour Flip-Flop Helps Block Trump Crypto Bill


    Goodlander, Torres, and Warner are all rated as strong supporters of the crypto industry on an industry scorecard. Still, all three have been critical of Trump’s personal dealings in the industry though his $TRUMP meme coin, which has helped make him $1.4 billion from crypto ventures.

    Warner recently ran an ad of his own attacking Trump over the meme coin.

    “That’s not governing. It’s grifting,” the Democratic senator said. “The corruption needs to stop.”

    Source: The Intercept · 2026-10-23

    Documents