ARCHIVE
Security
-
Hackers steal data of 1.6 million SBC Medical Group customers
SBC Medical Group has warned in a filing with the U.S. Securities and Exchange Commission (SEC) that two cybersecurity incidents exposed sensitive customer and employee information, including personal data belonging…
SRC // BleepingComputer -
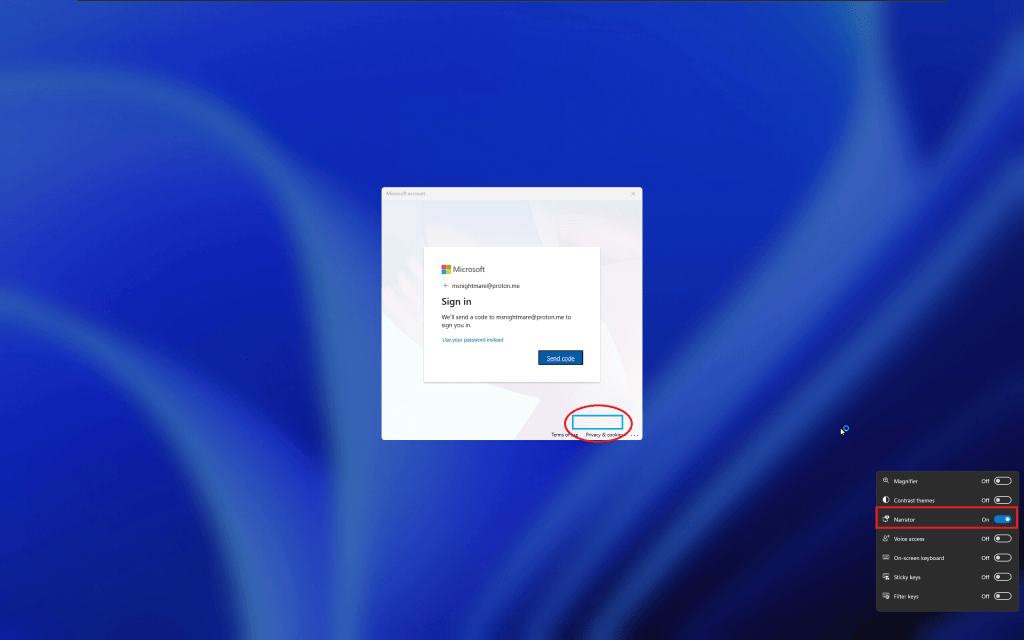
Chaotic Eclipse Releases FastUnlock, a New Windows Zero-Day Vulnerability
The researcher Chaotic Eclipse released FastUnlock, a new Windows zero-day vulnerability exploiting Narrator to bypass the lock screen. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released…
SRC // Security Affairs -
ASUS warns of critical hard-coded key flaw in Control Center Express
ASUS released Control Center Express v1.7.29 to fix three critical vulnerabilities that could let remote attackers gain administrative control of the management console and the devices it manages. [...]
SRC // BleepingComputer -
Chase, Visa, Mastercard confirm third-party cyberattacks that may have exposed customers’ info
First service outages, then data breaches…what's next?!
SRC // The Register — Security -
Nvidia adds possible hack to list of very bad things under investigation
Ransomware group sets a deadline for the chipmaker to pay up - or see its data leaked
SRC // The Register — Security -
Transport for London breach exposes 265,000 Oyster card users’ data
Transport for London (TfL) has announced that around 265,000 Oyster photocard customers may have had their account details exposed in a data breach. [...]
SRC // BleepingComputer -
Meta Muse booked an Airbnb without permission – and that’s not the worst of it
Meta employees have reported alarming privacy violations involving Muse, including unauthorized actions. An investigation also found the AI agent accessed private messages.
SRC // ZDNet Security -
Google will launch Android app verification requirement globally in January 2027
Google says almost all developers have already gotten on board with verification.
SRC // Ars Technica Security -
U.S. CISA adds Apache Axis, Vanderbilt REDCap,BerriAI LiteLLM, and Synology DSM flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apache Axis, Vanderbilt REDCap,BerriAI LiteLLM, and Synology DSM flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added…
SRC // Security Affairs -
Google Built a Giant ‘Mirror Dimension’ Internet to Test Its Chrome AI Agents
The company’s alternate-universe internet serves as a massive sandbox that allows the Chrome team to properly train AI browsing agents—without the risk of them going rogue.
SRC // WIRED Security