ARCHIVE
Security
-
UNM Health Shuts Clinics and Diverts Patients During Security Incident
A cybersecurity incident forced UNM Health to divert ambulances, cancel appointments, and pause care while it contained the threat. On Monday, October 26, the University of New Mexico Health System…
SRC // Security Affairs -
Fake ChatGPT and Claude Apps Use Signed Executables to Install Yoba Malware
Fake ChatGPT and Claude apps spread Yoba malware through GitHub, using signed executables to load a cryptominer on…
SRC // HackRead -
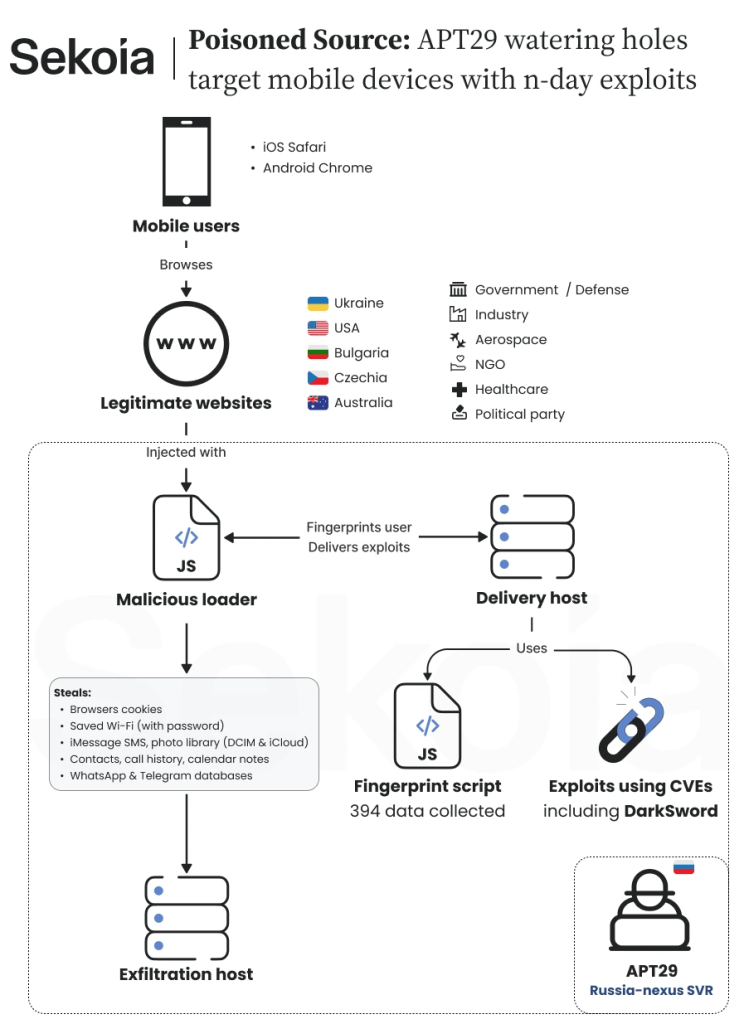
Russian APT29 Targets Mobile Users with Watering Hole Attacks
Russia-linked group APT29 targeted iOS and Android users through hijacked websites and a compromised analytics service. Sekoia says a large-scale watering hole campaign is going after iOS and Android users,…
SRC // Security Affairs -
GhostMap Android flaw lets malicious app trigger persistent boot loop
Attackers can force Android devices into a continuous boot loop using a specially crafted app that requires no permissions and only needs to be installed. [...]
SRC // BleepingComputer -
U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Apple flaw, tracked as CVE-2024-27834 (CVSS score…
SRC // Security Affairs -
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers
A Canadian man was extradited to the U.S. to face charges over hacking universities and hijacking their computers to mine cryptocurrency. A Canadian man, Ryan James Roach (35), has been…
SRC // Security Affairs -
Apple turns iCloud into spy cloud, will start looking at public share links
Content shared with anyone who has the URL will be scanned for 'harmful content,' though the iMaker hasn't defined that term
SRC // The Register — Security -
Vercel rolls out new protection against stolen session cookie attacks
Vercel is gradually rolling out Device Bound Session Credentials (DBSC) on its platform as a key defense against information stealer malware. [...]
SRC // BleepingComputer -
Zyxel fixes zero-day exploited to hack nearly 1,000 network switches
Zyxel has patched a zero-day vulnerability in its GS1900 series network switches that hackers exploited to compromise nearly 1,000 devices worldwide and steal configuration files and credentials. [...]
SRC // BleepingComputer