ARCHIVE
Security
-
LockBit Ransomware: Timeline, Status and the Attacks We Reported
Where LockBit stands in November 2026, how it works, a dated timeline, and which of seven attacks it claimed in 2023–24 were ever confirmed.
SRC // Privacy Affairs -
AI Pentest Tool AntiFox Abused To Steal AWS Credentials
Arctic Wolf saw attackers use the AntiFox pentest platform to hit IIS servers and AWS accounts. Arctic Wolf Labs has published research on attackers using AntiFox, an open-source, Chinese-language agentic…
SRC // Security Affairs -
eMudhra revokes 8 more CA certificates after private key mishap
Certificate authority eMudhra has revoked eight additional intermediate CA certificates after an investigation into its recent certificate security incident found improper handling of private keys during the certificate-generation process. [...]
SRC // BleepingComputer -
Notion says Fireworks breach exposed customer AI chat transcripts
Notion, the digital workspace platform, disclosed that a security breach at its AI infrastructure provider, Fireworks AI, exposed Notion AI chat transcripts in a small number of workspaces. [...]
SRC // BleepingComputer -
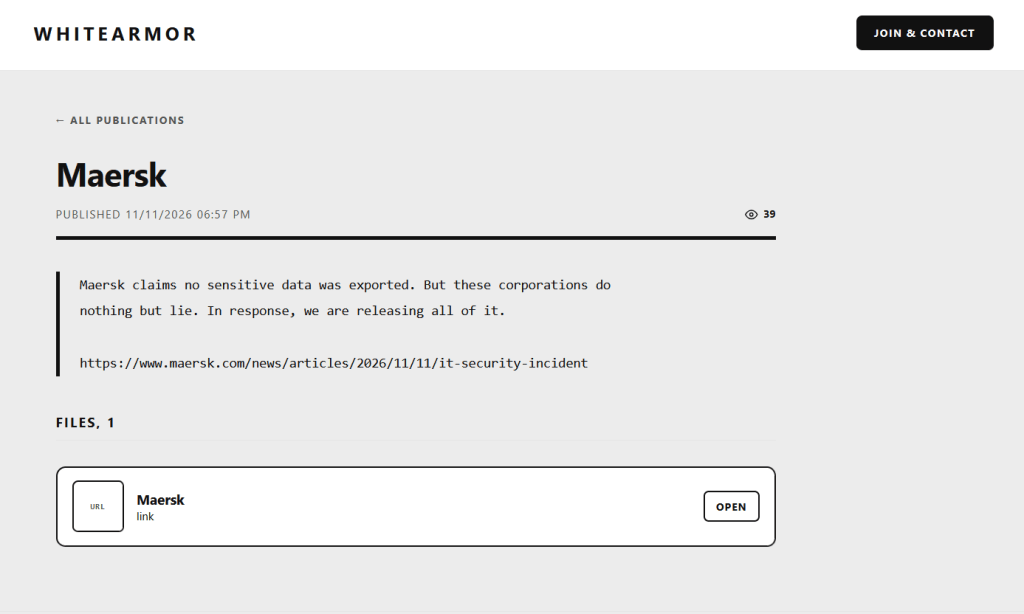
WhiteArmor Demands $5 Million from Maersk, Claims Theft of 100GB of Data
Maersk confirms a data breach involving a legacy system, while WhiteArmor claims 100GB of stolen data and demands a $5 million ransom. A.P. Moller Maersk, the Danish shipping giant, says…
SRC // Security Affairs -
Maersk confirms data breach as WhiteArmor ransomware demands $5 million
Maersk announced that a threat actor gained unauthorized access to a local legacy system inherited through an earlier acquisition and extracted data from it. [...]
SRC // BleepingComputer -
Hackers use AntiFox AI agents in AWS credential-theft attacks
Attackers are using Alibaba Cloud to host self-managed instances of AntiFox, an open-source agentic penetration testing platform, to target web services and AWS environments. [...]
SRC // BleepingComputer -
eBPF Rootkits: Why Underground Actors Are Taking Notice
Linux eBPF rootkits can hide malicious activity and evade traditional detection methods without loading kernel modules. Flare reveals how these techniques are spreading through underground forums, where threat actors are…
SRC // BleepingComputer -
TinstaPorn Android Malware Poses as Casino App to Collect User Data
A fake Macau casino app uses rigged betting odds to exploit gamblers while collecting phone numbers, location data…
SRC // HackRead -
N-able releases security hotfixes for zero-day vulnerabilities
N-able released hotfixes to address zero-day bugs affecting its N-central remote monitoring and management (RMM) platform, which were publicly disclosed over the weekend and forced it to take vulnerable hosted…
SRC // BleepingComputer