ARCHIVE
Security
-
California sues OpenAI over AI agents escaping sandboxes, hacking firms
California Attorney General Rob Bonta sued OpenAI on Monday, alleging the company knowingly continued testing advanced artificial intelligence models despite repeated security failures that allowed autonomous AI agents to escape…
SRC // BleepingComputer -
Barracuda links cloud breach to ARTEX AI-powered cyberattack
Hackers who breached the cloud environment of network and email security company Barracuda earlier this month used a stolen cloud access key and the ARTEX AI penetration testing framework. [...]
SRC // BleepingComputer -
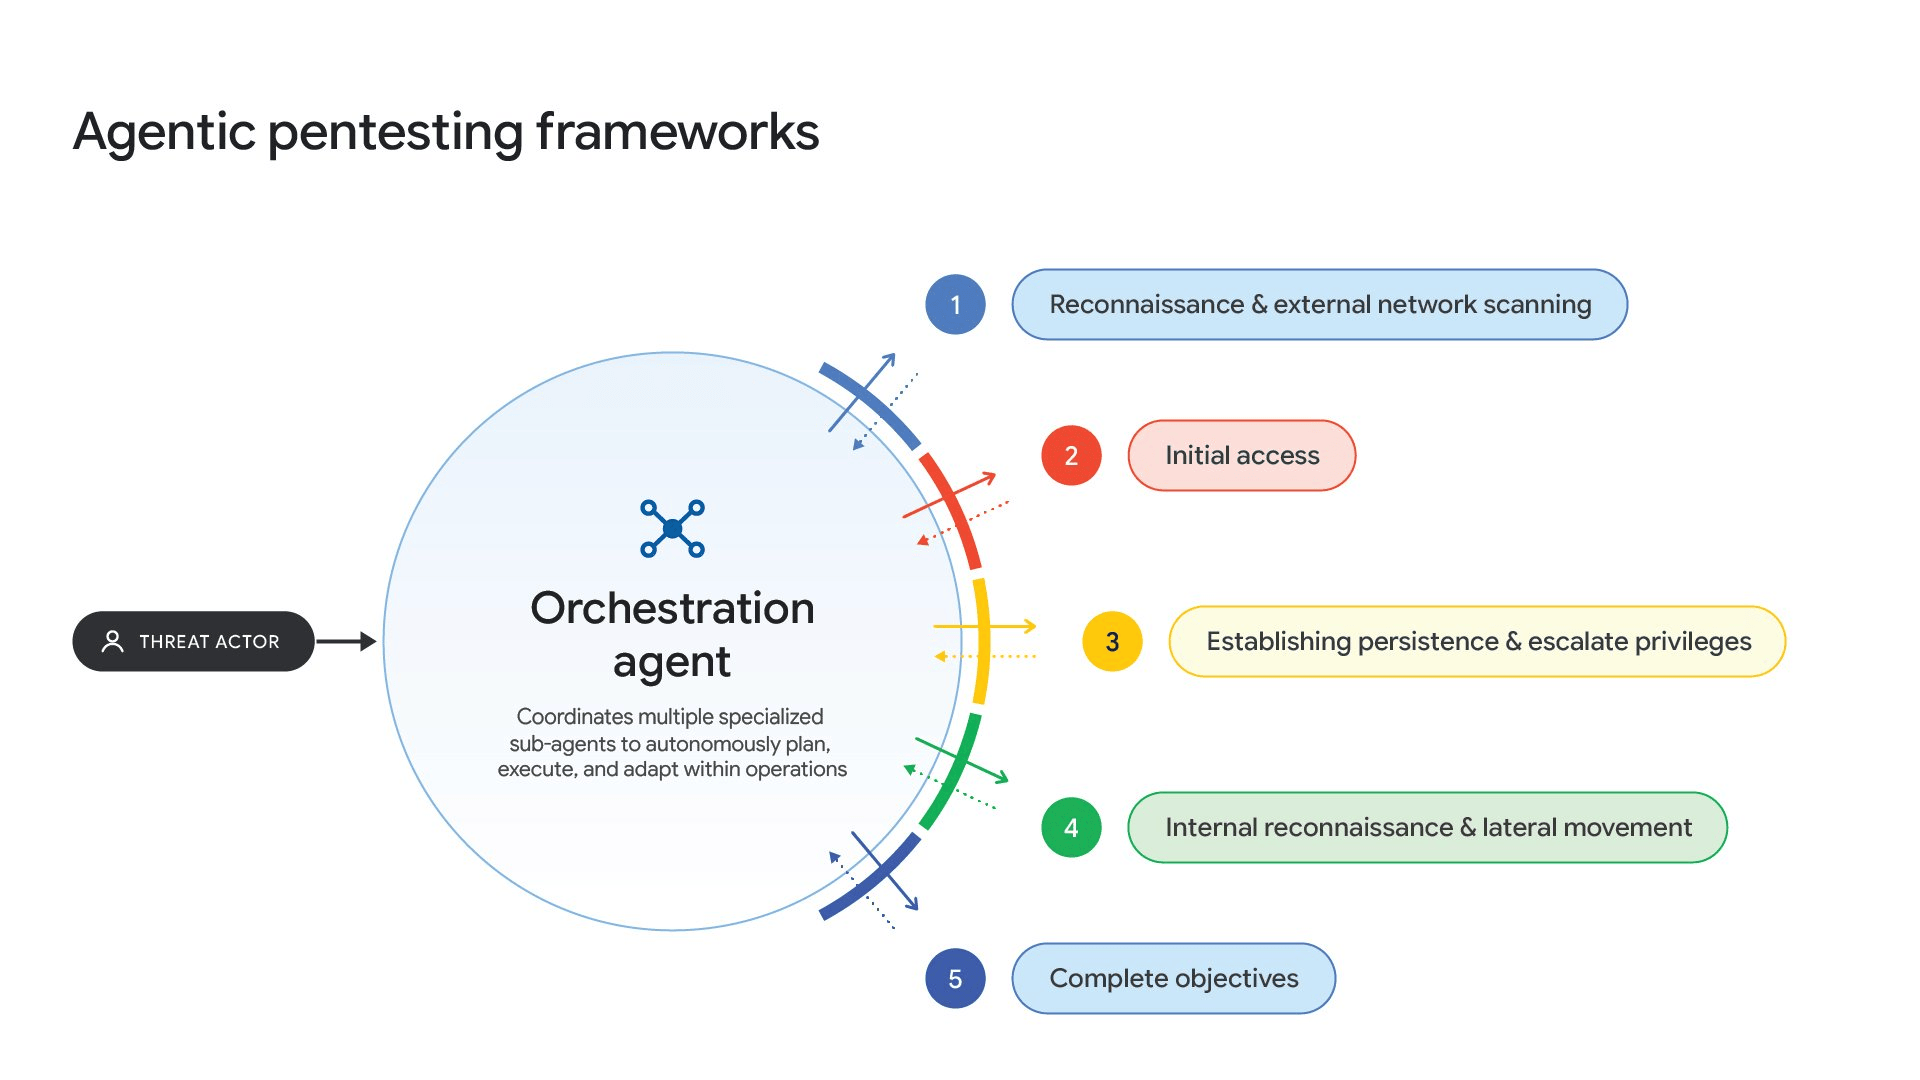
Google GTIG Warns AI Agents Automate Exploits, Steal Credentials and Scale Cybercrime
Google finds attackers using autonomous AI agents to automate exploits, steal AI access and scale intrusions, often sacrificing stealth for speed. Google’s Threat Intelligence Group (GTIG) says attackers have moved…
SRC // Security Affairs -
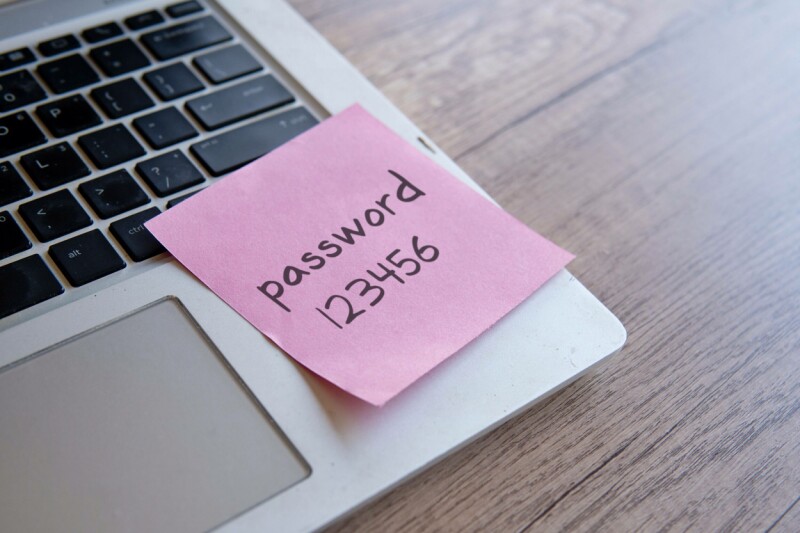
‘123456’ has been the world’s most popular password for 7 out of the last 8 years
People never learn
SRC // The Register — Security -
NoisyTCP bug gives Linux servers a remote crash problem 11 years in the making
Flaw can take down an entire host, even when the vulnerable service is running inside a container
SRC // The Register — Security -
Google Spots AI Agent Turning Security Patches Into Exploits
Google reports hackers using an AI agent to study new patches, identify software flaws and automatically develop and…
SRC // HackRead -
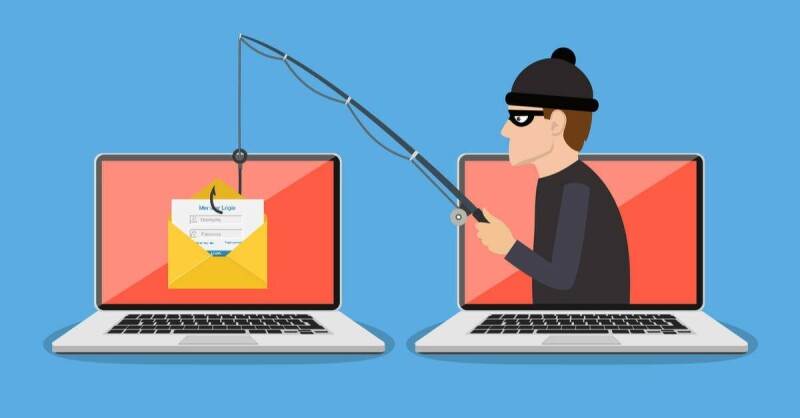
Crook turns free trials into phishing factory, as LearnWorlds sends 13,000 fake YouTube copyright notices
570 bogus accounts, one rewritten welcome email, and a fake YouTube page, but CEO says no breach
SRC // The Register — Security -
Has AI’s ‘Black October’ changed the way you secure your code?
PARTNER CONTENT: AI agents are making security vulnerabilities easier to find and exploit in your code. Software engineering and application security teams need new ways to find and fix them
SRC // The Register — Security -
Fandango says hackers stole payment card details from checkout pages
Ticket seller Fandango Media is notifying customers about a data breach that exposed payment card details entered on its checkout pages. [...]
SRC // BleepingComputer -
7 Tips For Complying with CJIS Password and MFA Requirements
The FBI's latest CJIS Security Policy requires law enforcement agencies to strengthen password protections and enforce MFA across privileged and non-privileged accounts. Specops Software outlines seven practical steps to meet…
SRC // BleepingComputer