ARCHIVE
Pierluigi Paganini
-
Google fixes the eighth actively exploited Chrome zero-day of 2026
Google patched nine Chrome flaws, including a V8 vulnerability tracked as CVE-2026-125350, that attackers have been actively exploiting in the wild. Google has addressed multiple security vulnerabilities, one of which,…
SRC // Security Affairs -
France Blames Iran for the Supermarket Fridge Attacks
France blames Iran for supermarket fridge attacks. What’s known, what remains unclear, and how to secure exposed controllers. French Foreign Minister Jean-Noël Barrot said Iran’s Revolutionary Guard Corps was behind…
SRC // Security Affairs -
CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers
US agencies warn attackers are going after industrial refrigeration controllers. The fixes are basic, and most start with getting them off the internet. CISA, the FBI, HHS, USDA and the…
SRC // Security Affairs -
SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7
Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used…
SRC // Security Affairs -
Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa
French Bank Crédit Mutuel Arkéa says hackers exploited a service provider to steal up to $133 million using the bank’s own account. French cooperative bank Crédit Mutuel Arkéa was hit…
SRC // Security Affairs -
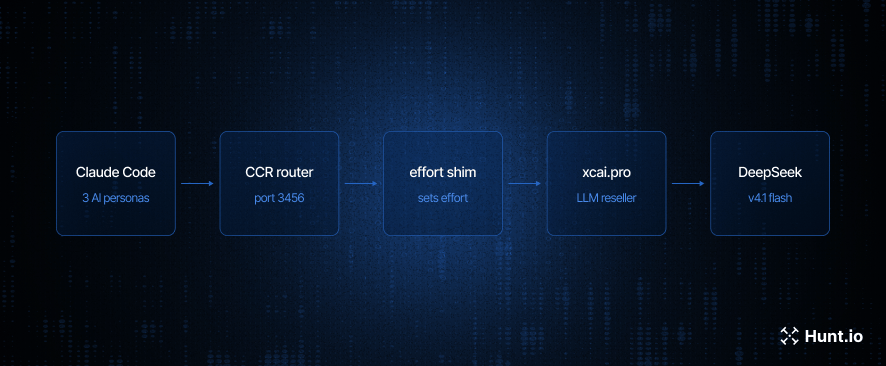
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches
Hunt.io traced ARTEX servers and AI-powered hacking tools used in breaches affecting seven South Korean financial institutions. Between late September and early October 2026, seven South Korean financial institutions had…
SRC // Security Affairs -
One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers
Software vendors can boost revenue by tracking customer usage across products, while AI accelerates pricing and consumption decisions. It is hard to find any software vendor that sells just one…
SRC // Security Affairs -
U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
U.S. CISA adds SonicWall SonicOS SSLVPN vulnerability CVE-2026-19868 to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a SonicWall SonicOS SSLVPN flaw, tracked as CVE-2026-19868…
SRC // Security Affairs -
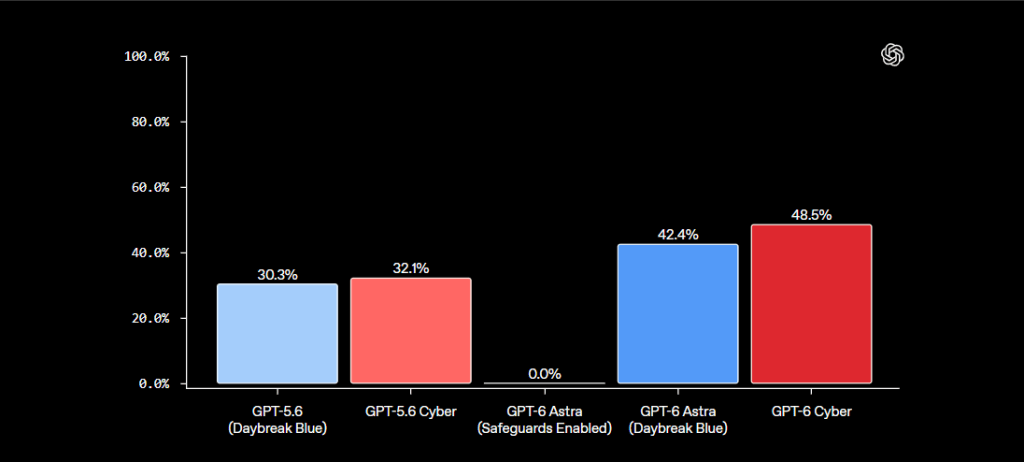
OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries
OpenAI GPT-6 Cyber found 81 high-severity Firefox flaws and hundreds of Linux bugs, raising new questions about AI-powered cyber risks. OpenAI has introduced GPT-6 Cyber, a model built for security…
SRC // Security Affairs