ARCHIVE
Pierluigi Paganini
-
Cyberattack on Austrian Foreign Ministry Exposes Diplomatic Staff Data
Austrian Foreign Ministry Hacked, Staff Contact Details Accessed Hackers accessed Austrian Foreign Ministry records containing staff contact details, including employees at diplomatic missions abroad. Austrian Foreign Ministry confirmed a cyberattack…
SRC // Security Affairs -
CVE-2026-23871: WhatsApp Bug Helped Scammers Make Messages Look Legitimate
WhatsApp patched three security flaws, including one exploited in a real scam campaign to make fraudulent messages appear more credible. WhatsApp’s November security advisory fixes three flaws, including CVE-2026-23871, a…
SRC // Security Affairs -
Hackers Exploit Cisco Expressway Flaw CVE-2026-76466 to Breach Russian Organization
Cisco Expressway flaw CVE-2026-76466 is being exploited to gain root access and move from exposed devices into internal networks. Attackers have exploited a critical flaw, tracked as CVE-2026-76466 (CVSS score…
SRC // Security Affairs -
Trump’s First Move After the Outages: Fire the Cyber Director
Trump fired his national cyber director days after outages hit Microsoft, US flights, and the NSA’s classified network. No link to a cyberattack confirmed. The White House fired national cyber…
SRC // Security Affairs -
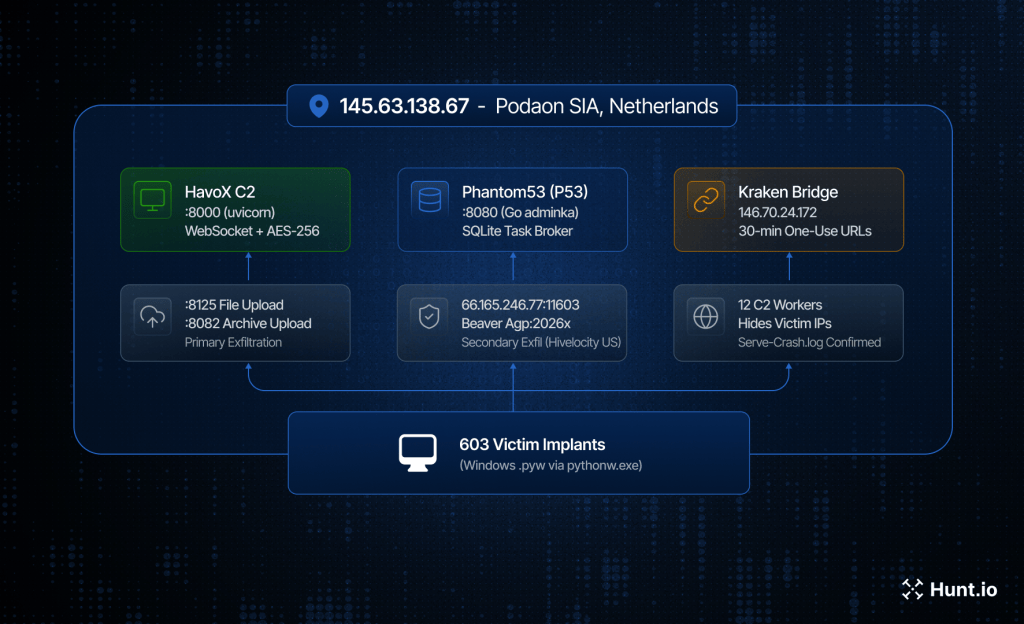
Hunt.io Uncovers Russian-Speaking Credential Theft Operation Targeting US Banks and Government Accounts
Hunt.io uncovered a credential-stealing operation that compromised 603 PCs and exposed bank, government and password manager accounts. Hunt.io found an exposed open directory sitting on a Netherlands VPS, and inside…
SRC // Security Affairs -
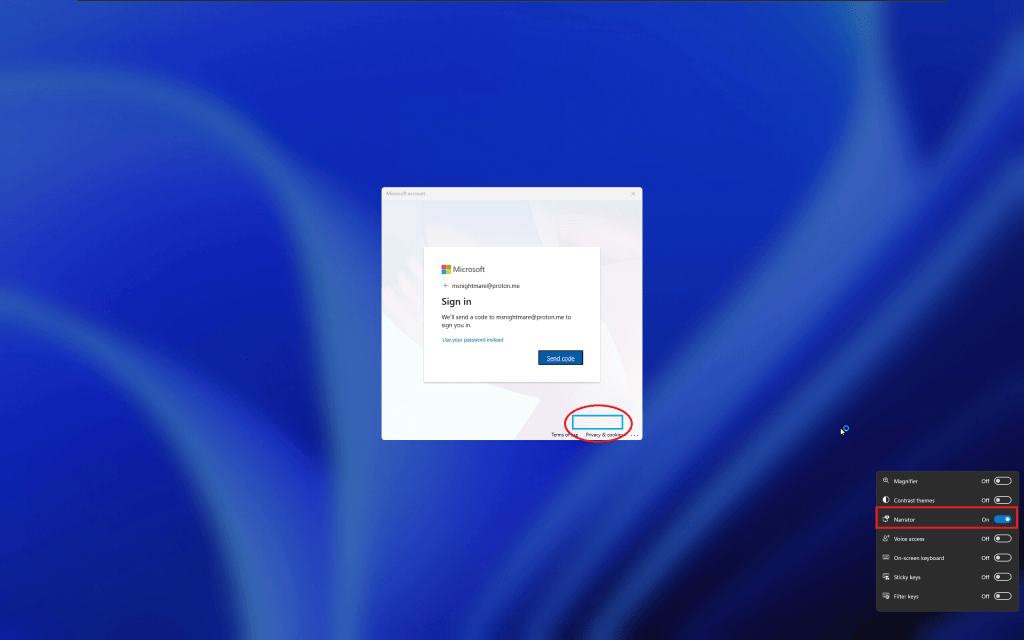
Chaotic Eclipse Releases FastUnlock, a New Windows Zero-Day Vulnerability
The researcher Chaotic Eclipse released FastUnlock, a new Windows zero-day vulnerability exploiting Narrator to bypass the lock screen. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released…
SRC // Security Affairs -
U.S. CISA adds Apache Axis, Vanderbilt REDCap,BerriAI LiteLLM, and Synology DSM flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apache Axis, Vanderbilt REDCap,BerriAI LiteLLM, and Synology DSM flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added…
SRC // Security Affairs -
European Commission Cyberattack: ARTEX AI Tool Suspected in Prolonged Disruption
A cyberattack disrupted EU Commission services for over ten days. ARTEX is suspected, while investigators assess whether staff data was stolen. A cyberattack has disrupted internal European Commission systems for…
SRC // Security Affairs -
PHP Warns of Critical Flaws Ahead of November Security Release
PHP will patch critical security flaws across supported versions, including a session handling bug that could allow remote code execution. The PHP development team announced a new security release scheduled…
SRC // Security Affairs -
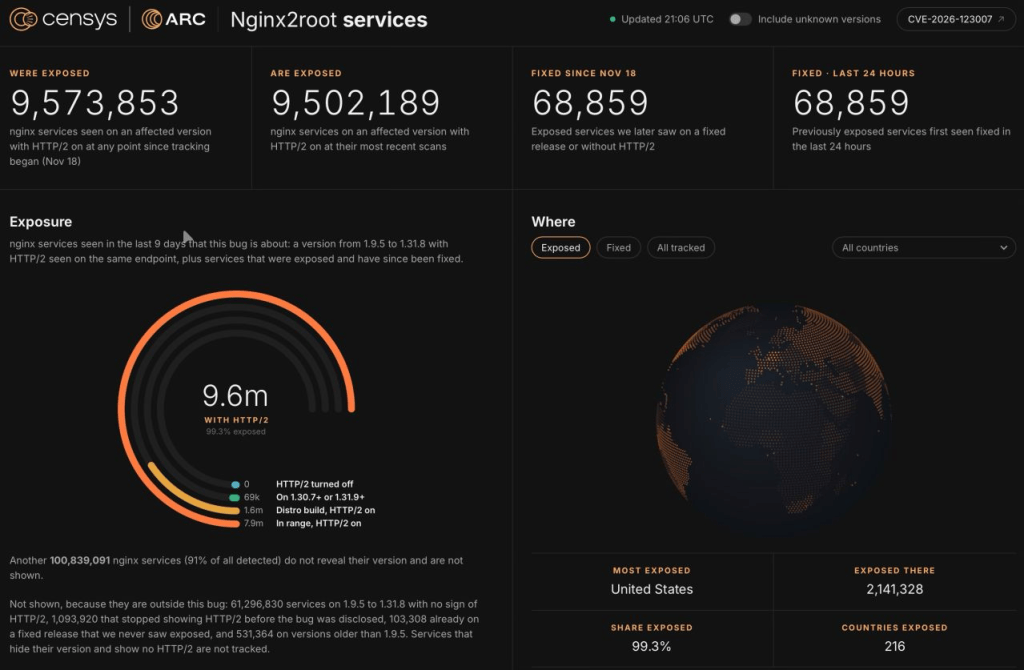
nginx2root:AI Discovers Five Critical nginx Flaws and a Path to Root
nginx2root exposes five critical nginx flaws and a Linux kernel bug that can lead to remote code execution and root access. Xint Research has disclosed nginx2root, five distinct nginx vulnerabilities…
SRC // Security Affairs