ARCHIVE
LLM
-
The forced audit: how AuditTeam’s OpsAgent framework masks ransomware as consulting
How does a ransomware gang sell a “forced audit”? We break down AuditTeam’s OpsAgent implant, its Rust rewrite, and the extortion model demanding a consulting fee to delete stolen data.
SRC // Securelist (Kaspersky GReAT) -
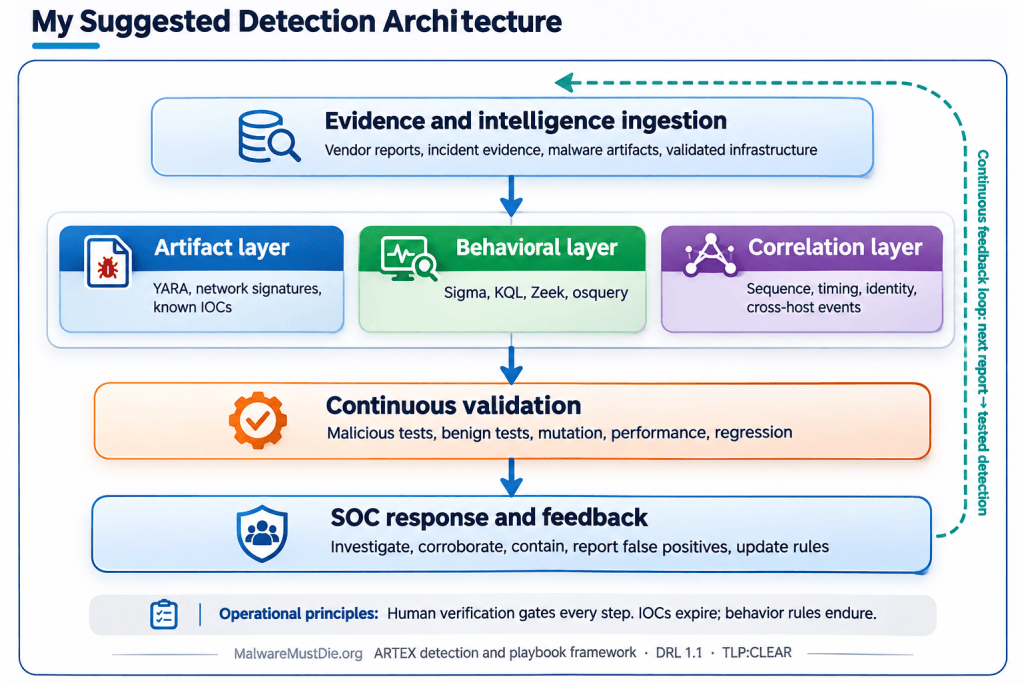
From Report to Tested Detection in Hours: The ARTEX Signature Pack
The researcher MalwareMustDie released an open ARTEX detection pack in seven formats, built on behavior and a repeatable playbook, because attackers now turn weeks into hours. The researcher MalwareMustDie released…
SRC // Security Affairs -
AI Doesn’t Have to Go Rogue to Break the World
This essay is adapted from a keynote speech delivered at the DEF CON 34 conference in Las Vegas on August 7, 2026. The essay originally appeared in CyberScoop. I want…
SRC // Schneier on Security -
ARTEX and AI-Powered Red Teaming Tools: What Defenders Need to Know
Learn what Unit 42 discovered about attacker use of AI-powered red team tools, and how to mitigate these attacks. The post ARTEX and AI-Powered Red Teaming Tools: What Defenders Need…
SRC // Palo Alto Networks Unit 42 -
Citrus Ransomware: VLESS for traffic, Sn00py for encryption, and LLMs lending a hand
We break down the Citrus Ransomware group's attacks: the attackers' TTPs and tooling, including VLESS traffic tunneling and LLM use, plus their links to Toy Ghouls.
SRC // Securelist (Kaspersky GReAT) -
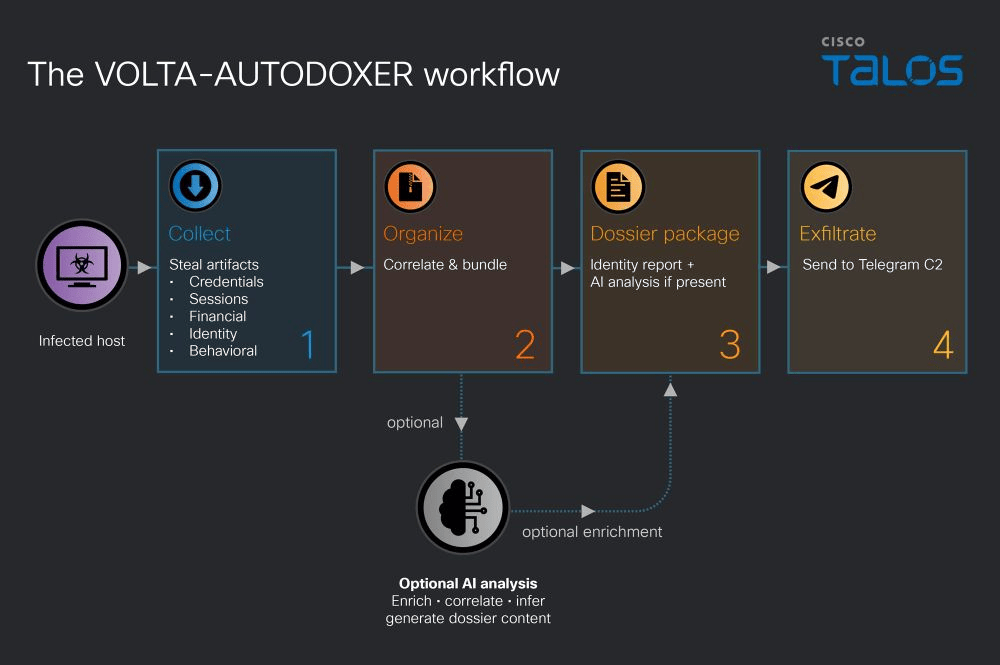
VOLTA, the infostealer that asks an AI which victims are worth the effort
VOLTA is an AI-powered infostealer that steals personal data, then uses LLMs to assess victims’ value and rank targets for attackers. Cisco Talos has analyzed a new Windows infostealer called…
SRC // Security Affairs -
CyberStrikeAI in the wild: the use of AI in real-world attacks on organizations
We analyze a series of attacks on educational institutions that were fully automated during the post-exploitation phase using the CyberStrikeAI penetration testing framework.
SRC // Securelist (Kaspersky GReAT) -
Filter generation in practice: from algorithms to LLMs
We automate filter generation for security alerts using an algorithm, a large language model, and a group of LLM agents.
SRC // Securelist (Kaspersky GReAT) -
AI-Powered Espionage Campaign Targets Government Linux Infrastructure
Our analysis an AI-powered espionage campaign targeting government Linux infrastructure with custom malware, web shells, and advanced credential theft. The post AI-Powered Espionage Campaign Targets Government Linux Infrastructure appeared first…
SRC // Palo Alto Networks Unit 42