JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Suspected ransomware affiliate extradited to US over $500 million in extortion demands
A 43-year-old Kazakh national accused of helping a ransomware crew steal data from US hospitals and schools, then threatening to publish patients’ medical information, has been extradited from Italy, the…
SRC // Help Net Security -
Ransomware claim: Optimil Machinery (akira)
Optimil Machinery Inc. is a globally recognized leader in primary and secondary log processing machinery, specializing in log and board optimization systems for sawmills. The company focuses on designing and…
-
Airlock Digital blocks unauthorized AI agent actions at the endpoint
Airlock Digital has announced the availability of Agentic Control with the release of Airlock Digital v7.1. Agentic Control includes dedicated Agentic Steering capabilities for AI agents, allowing customers to extend…
SRC // Help Net Security -
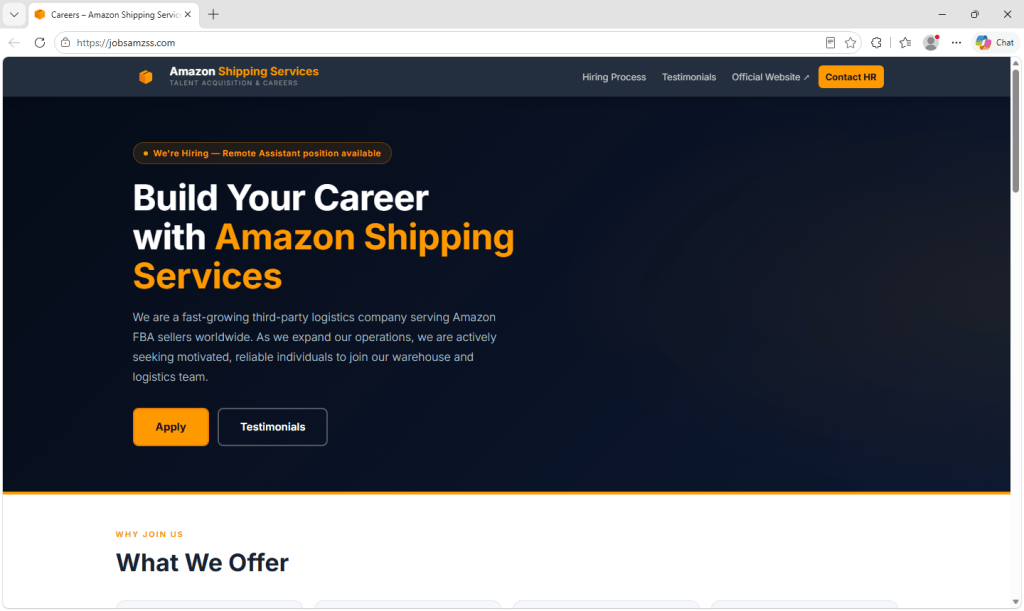
“Amazon” job offer promises $5,000 a month, but it’s got all the signs of a scam
Lookalike Amazon sites advertise high-paying remote jobs, but has all the signs of a reshipping scam.
SRC // Malwarebytes Labs -
‘Not rocket surgery’ claims researcher who found six Danfoss fridge controller zero-days in under an hour
Even strict authentication mode has a hole, we’re told, while basic exploit defenses are missing from the firmware
SRC // The Register — Security -
MSP ScreenConnect Servers Targeted in Month-Long Campaign
More than 40 servers received over 688,000 requests exploiting CVE-2026-84869 to execute guest-pushed files. The post MSP ScreenConnect Servers Targeted in Month-Long Campaign appeared first on SecurityWeek.
SRC // SecurityWeek -
Ransomware claim: New England Orthopedic Surgeons (Booba Project)
Medical Practices Stolen data: 5 GB.Group: Booba ProjectCountry: USSector: HealthcareVictim website: www.neortho.comDiscovered: 2026-11-17 13:20 UTCAttack date: 2026-11-17 13:16 UTCThis entry reflects a claim published by an extortion group and collected…
-
Grok Bots Attempt to Access Corporate Data Without User Approval
Two AI agents, separately over a five-day period, autonomously tried to access connected applications, including Google Calendar, Gmail, Slack, and GitHub, without account owner approval.
SRC // Dark Reading -
Alleged ransomware group member extradited from Italy to face US charges in hospital, school extortion case
A Kazakh national charged in a ransomware and extortion conspiracy targeting U.S. hospitals and schools was also charged with violating the TAKE IT DOWN Act. The post Alleged ransomware group…
SRC // CyberScoop -
Microsoft Warns of Coordinated Phishing Campaign Leveraging M365 Service Outage
Microsoft said the high volume campaign was likely designed to capture user credentials, and urged organizations to investigate signs of compromise
SRC // Infosecurity Magazine