JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Ransomware claim: A***** T****** (doommageddon)
upcoming | — | 0 filesGroup: doommageddonDiscovered: 2026-10-30 10:34 UTCThis entry reflects a claim published by an extortion group and collected by a public tracker. It has not been independently…
SRC // RansomLook — Recent Posts -
Hackers leak personnel data of 41,000+ Homeland Security staff, including ICE and border agents
The US Department of Homeland Security has had the details of more than 41,000 staff, including ICE and CBP agents, published online. Not ideal for an organisation with “Security” in…
SRC // Graham Cluley -
EU Satellite Imagery Delayed Over Gaza and Parts of West Bank by 24-hours
submitted by /u/Changaco [link] [comments]
SRC // Reddit r/OSINT -
Drupal warns of critical Commerce Core flaw exploited in attacks
Drupal warned admins to patch a critical access bypass vulnerability in the Commerce Core module that attackers are exploiting in the wild. […]
SRC // BleepingComputer -
Filter generation in practice: from algorithms to LLMs
We automate filter generation for security alerts using an algorithm, a large language model, and a group of LLM agents.
SRC // Securelist (Kaspersky GReAT) -
How AIPAC and AI Spent Their Money This Midterm Election
Intercept staff take stock of the big spenders this election cycle. The post How AIPAC and AI Spent Their Money This Midterm Election appeared first on The Intercept.
SRC // The Intercept -
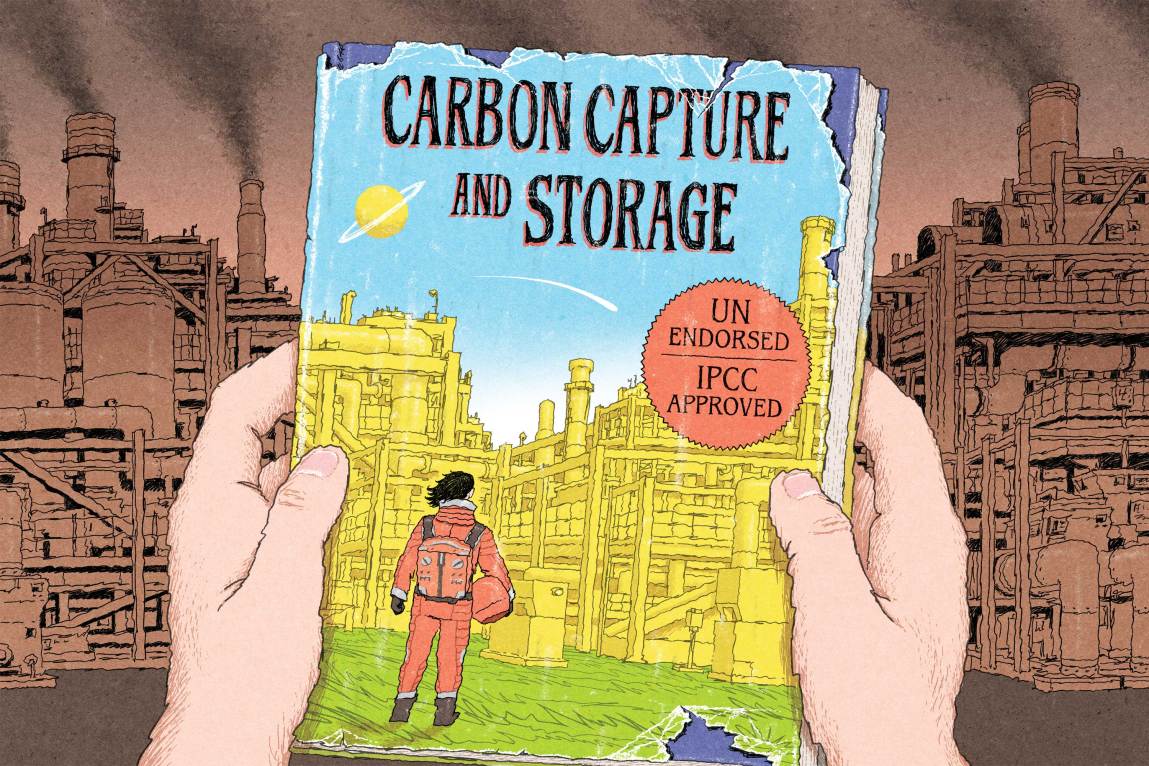
How a Secret Vote by U.N. Scientists Legitimized Carbon Capture and Skewed Decades of Climate Policy
The post How a Secret Vote by U.N. Scientists Legitimized Carbon Capture and Skewed Decades of Climate Policy appeared first on ProPublica.
SRC // ProPublica -
$2 Million+ Drained From Polymarket Traders in New Supply Chain Attack
Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds. The post $2 Million+ Drained From Polymarket Traders in New Supply…
SRC // SecurityWeek -
Max-Severity GitLab Vulnerability Exploited Against Alpine Linux
Tracked as CVE-2026-97229, the bug allows unauthenticated attackers to execute arbitrary code on the server. The post Max-Severity GitLab Vulnerability Exploited Against Alpine Linux appeared first on SecurityWeek.
SRC // SecurityWeek -
Open-weight AI model GLM-5.3 cheated its way to correct answers
Irregular evaluated Zhipu AI’s open-weight model GLM-5.3 across 13 offensive cyber scenarios using CyScenarioBench, the company’s framework for measuring an LLM’s ability to plan and execute multistage attacks under realistic…
SRC // Help Net Security