JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Google fixes the eighth actively exploited Chrome zero-day of 2026
Google patched nine Chrome flaws, including a V8 vulnerability tracked as CVE-2026-125350, that attackers have been actively exploiting in the wild. Google has addressed multiple security vulnerabilities, one of which,…
SRC // Security Affairs -
Turla hackers use new Cereal malware to spy on govt Exchange servers
The Russian state-backed threat group Turla has been using a new malicious toolset called ‘Cereal’ to intercept emails on Microsoft Exchange servers at government organizations. […]
SRC // BleepingComputer -
SAP Patches Four CVSS 10.0 Flaws, Including Two Enabling Remote Code Execution
Four flaws that attackers could exploit without logging in were fixed today as part of SAP’s monthly Security Patch Day—the vendor rates all four 10.0, the maximum CVSS score. Three…
SRC // The Hacker News -
Turla’s Cereal malware turns victims’ Exchange servers into spy hubs
Russia-aligned group Turla planted a modular .NET toolset on Microsoft Exchange servers at two government organizations, one in Kazakhstan and one in Romania, and used it to copy selected email…
SRC // Help Net Security -
The Garbage Man: Bill Gates Has Earned Billions Investing in Climate-Polluting Landfills
The post The Garbage Man: Bill Gates Has Earned Billions Investing in Climate-Polluting Landfills appeared first on ProPublica.
SRC // ProPublica -
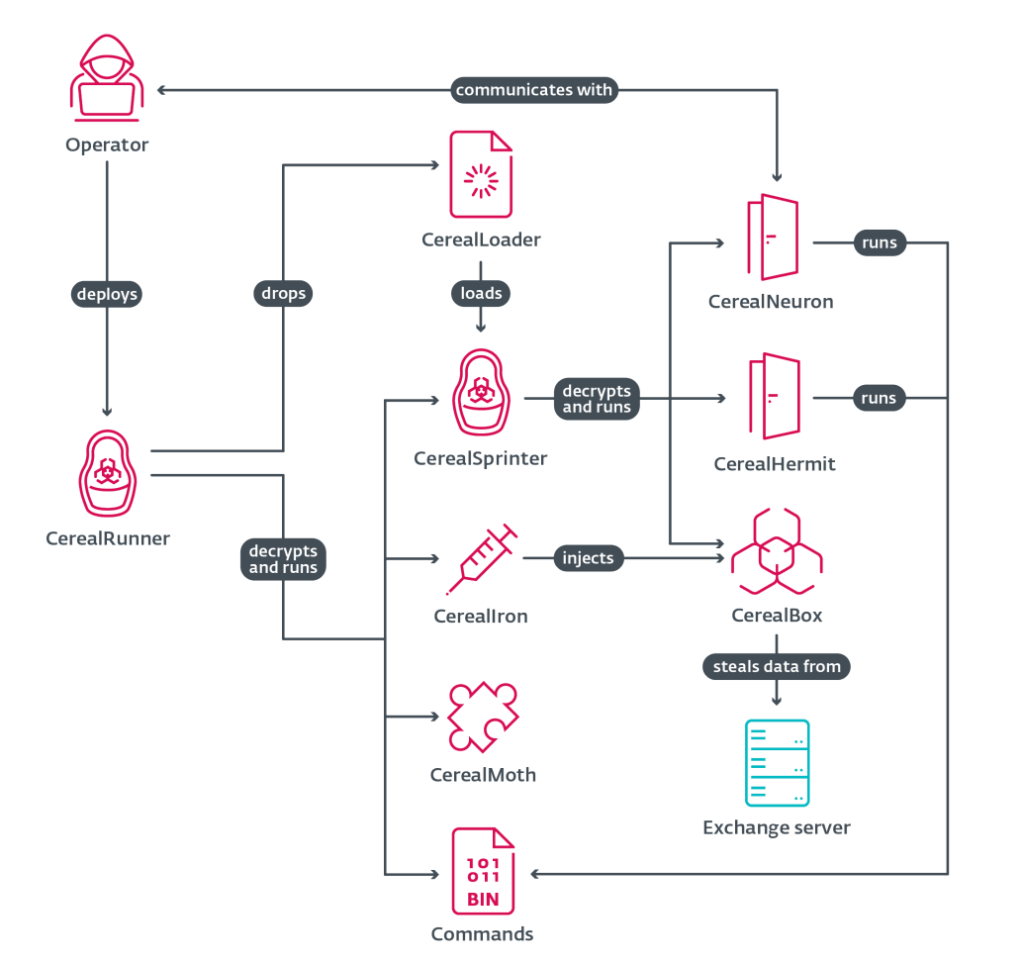
Russian Turla group used new toolset to silently pilfer emails from Kazakhstan, Romanian governments
Nicknamed “Turla’s Cereal,” the tools target Microsoft Exchange servers and lack many obvious indicators of compromise or malicious telemetry, per a new ESET report. The post Russian Turla group used…
SRC // CyberScoop -
Exchange for breakfast: Turla’s Cereal tricks are not for kids
ESET Research describes Turla’s Cereal toolset, featuring a novel Exchange email collection module, a unique C&C mechanism, and sophisticated .NET execution tricks
SRC // WeLiveSecurity (ESET) -
N-able Takes N-central Offline as Researcher Drops Over 30 Zero-Days
Attackers could exploit the flaws for remote code execution, credential theft, and administrator account creation. The post N-able Takes N-central Offline as Researcher Drops Over 30 Zero-Days appeared first on…
SRC // SecurityWeek -
IBM Aspera Faspex, SignalWire FreeSwitch Vulnerabilities Exploited in Attacks
CISA has added CVE-2026-123218 and CVE-2026-116779 to KEV, urging federal agencies to patch them within three days. The post IBM Aspera Faspex, SignalWire FreeSwitch Vulnerabilities Exploited in Attacks appeared first…
SRC // SecurityWeek