JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
GHSA-pcrw-h46h-c93h: Mongoose: sanitizeFilter not applied on countDocuments
Severity: CRITICALCVE: CVE-2026-125120Ecosystems: npm, npm, npm, npmPackages: mongoose, mongoose, mongoose, mongoose### Impact `sanitizeFilter` is Mongoose's mechanism for protecting against query selector injection attacks. In older versions of Mongoose, `sanitizeFilter` was…
SRC // GitHub Security Advisories -
GHSA-5v64-555j-wjxm: Rack: Multipart parsing allows DoS via unbounded scan buffer growth
Severity: HIGHCVE: CVE-2026-125111Ecosystems: rubygems, rubygems, rubygemsPackages: rack, rack, rack## Summary `Rack::Multipart::Parser` reads the request body in chunks of `rack.multipart.buffer_size` (1 MiB by default) into an internal scan buffer. Parsed bytes…
SRC // GitHub Security Advisories -
Hackers exploit trusted AWS access to breach multiple cloud environments
A threat actor used compromised identity and access management (IAM) credentials for a Qubole big data platform’s AWS account to access and exfiltrate data from multiple customers’ AWS environments. […]
SRC // BleepingComputer -
Lithos DEX Database Sale Claim Lists 173,146 Wallet Addresses and 50,239 IP Addresses
An actor using the handle “ChimeraZ” claims to be selling a database associated with Lithos, described in the listing as a decentralized exchange built on the Plasma blockchain.
SRC // Dark Web Informer -
GHSA-p8x9-v4hv-2w4g: Rack: Multipart boundary ambiguity guard in Rack::Multipart::Parser can be bypassed with a quoted boundary value, allowing WAF bypass
Severity: LOWCVE: CVE-2026-125108Ecosystems: rubygems, rubygems, rubygemsPackages: rack, rack, rack## Summary The guard added for CVE-2026-26961 (GHSA-vgpv-f759-9wx3), which rejects multipart requests with more than one `boundary` parameter, only inspects the part…
SRC // GitHub Security Advisories -
Git Patches Flaw That Lets Malicious Repositories Execute Code During Recursive Clones
A flaw in Git can let a malicious repository run an attacker’s code on a computer that clones it recursively, together with its submodules. The Git project fixed it this…
SRC // The Hacker News -
GHSA-wrr5-j383-f7h2: NocoBase: @nocobase/plugin-action-custom-request allows server-side request forgery through runtime URL overrides
Severity: MEDIUMCVE: CVE-2026-79914Ecosystems: npm, npmPackages: @nocobase/plugin-action-custom-request, @nocobase/plugin-action-custom-request### Summary A Server-Side Request Forgery vulnerability exists in NocoBase v2.1.10 in the `@nocobase/plugin-action-custom-request` plugin. A low-privileged authenticated user can call the `customRequests:send` endpoint…
SRC // GitHub Security Advisories -
Exploited Outlook Zero-Day Among 1,094 Flaws Patched by Microsoft
CVE-2026-124194 is the Outlook zero-day for which Microsoft says it’s aware of active exploitation. The post Exploited Outlook Zero-Day Among 1,094 Flaws Patched by Microsoft appeared first on SecurityWeek.
SRC // SecurityWeek -
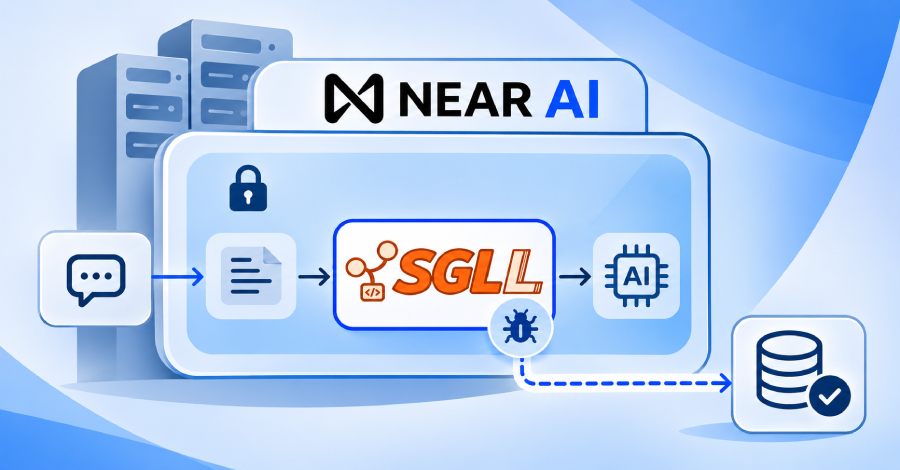
SGLang RCE Exploit Breaches NEAR AI, Steals Data From 18 Agents and About 100 Users
An attacker exploited a remote code execution flaw in SGLang, an open-source inference engine, and ran code on one of NEAR AI’s inference servers last Sunday. The attacker could also…
SRC // The Hacker News -
GHSA-2j8w-xcrc-x985: Rack: Rack::Request#host_with_port (and #base_url / #url) return the raw invalid Host header — incomplete fix of CVE-2026-34835
Severity: MEDIUMCVE: CVE-2026-125109Ecosystems: rubygems, rubygemsPackages: rack, rack## Summary `Rack::Request#host_with_port`, and therefore `#base_url` and `#url`, return the raw authority string when it fails validation. An attacker-controlled `Host`, `X-Forwarded-Host`, or `Forwarded: host=`…
SRC // GitHub Security Advisories