JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
GHSA-539f-xcgw-2gjg: Addressable display_uri can show misleading hosts containing bidi and invisible characters
Severity: LOWCVE: CVE-2026-126349Ecosystems: rubygemsPackages: addressable### Impact `Addressable::IDNA.to_unicode` decodes Punycode labels (labels beginning with `xn--`) that contain characters which change how text is displayed without being visible themselves. These include bidirectional…
SRC // GitHub Security Advisories -
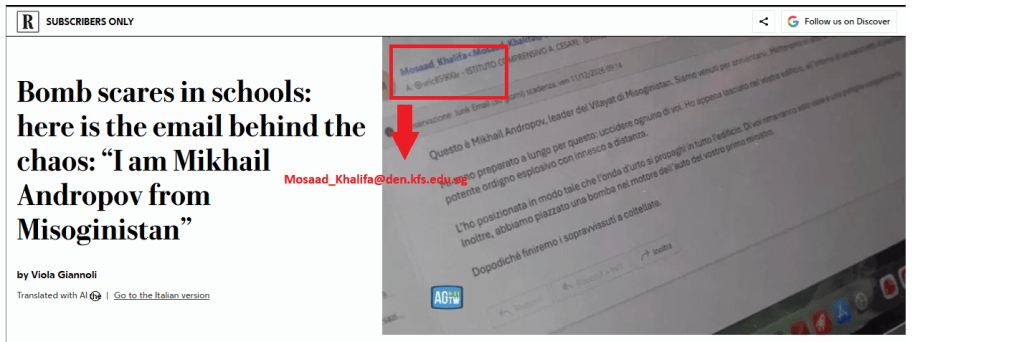
The School Bomb Threats Came From Accounts Already in Stolen Data
Hudson Rock researchers found that two university addresses tied to Italy’s school bomb threats were in infostealer data. On 11 November, bomb-threat emails hit schools across Europe. ANSA, citing the…
SRC // Security Affairs -
GHSA-qq38-m9mg-xjj5: Addressable: Denial of service in URI path normalization
Severity: MEDIUMCVE: CVE-2026-126351Ecosystems: rubygemsPackages: addressable### Impact `Addressable::URI.normalize_path` takes time quadratic in the number of nested dot segments in a path (e.g., `"/" + "a/" * n + "../" * n`,…
SRC // GitHub Security Advisories -
GHSA-jmv2-qgxf-f995: Astro: Reflected XSS via unescaped slot names in @astrojs/solid-js
Severity: LOWCVE: CVE-2026-126363Ecosystems: npmPackages: @astrojs/solid-js## Summary The `@astrojs/solid-js` renderer wraps named slot content passed to Solid components in an “ element, and writes the slot name into its `name` attribute…
SRC // GitHub Security Advisories -
GHSA-f4j9-crrj-867q: Astro: Reflected XSS via unescaped slot names in @astrojs/svelte
Severity: LOWCVE: CVE-2026-126362Ecosystems: npmPackages: @astrojs/svelte## Summary The `@astrojs/svelte` renderer wraps slotted content passed to Svelte components in an “ element, and writes the slot name into its `name` attribute without…
SRC // GitHub Security Advisories -
GHSA-j82w-28jv-3pmj: Addressable: Regular Expression Denial of Service in templates with certain exploded expressions
Severity: MEDIUMCVE: CVE-2026-126350Ecosystems: rubygemsPackages: addressable### Impact Within the URI template implementation in Addressable, templates using the `*` (explode) modifier with the `/`, `.`, `;`, `?` or `&` operators (e.g., `{/segments*}`,…
SRC // GitHub Security Advisories -
GHSA-9f42-57jx-vpp3: Addressable: Regular Expression Denial of Service in templates with multiple variables
Severity: MEDIUMCVE: CVE-2026-126352Ecosystems: rubygemsPackages: addressable### Impact Within the URI template implementation in Addressable, templates that put several variables in one expression generate regular expressions vulnerable to excessive backtracking: 1. Expressions…
SRC // GitHub Security Advisories -
GHSA-8gmh-2hhj-2hv9: Addressable URI normalization resolves some dotted path segments to the wrong path
Severity: MEDIUMCVE: CVE-2026-126354Ecosystems: rubygemsPackages: addressable### Summary `Addressable::URI.normalize_path` resolves some paths containing `..` segments to a different path than RFC 3986 does. When a path climbs above the root before any…
SRC // GitHub Security Advisories -
Hackers compromise 4,800 GitHub accounts to steal cloud credentials
A new campaign dubbed ‘wfx-loot’ has unfolded on GitHub where threat actors used 4,837 compromised accounts to probe 61,764 repositories, open pull requests, and push secrets-stealing malware. […]
SRC // BleepingComputer -
Ransomware claim: toyokiki-thailand.com (safepay)
Established in 2013 as a subsidiary of Toyokiki Industrial Co., Ltd. of Japan, the company specializes in manufacturing and processing …Group: safepayCountry: THSector: ManufacturingVictim website: toyokiki-thailand.comDiscovered: 2026-11-12 22:02 UTCAttack date:…