JEDI-SEC // FIELD NOTES
Research & Field Notes
Security news, leaks and breaches, ransomware and dark-web monitoring, advisories and OSINT, each item linked back to its source.
-
Ransomware claim: The Tidewater Inn (aoqin leaks)
Country: United States | Employees: 37 | Revenue: $23,000,000 | Data: 480 GB | Type: clientsData, confidential, personal, banking, Contracts | Data publication: 2026-11-20 | Status: not_paid Tidewater Inn’s newly…
SRC // RansomLook — Recent Posts -
Ransomware claim: Airblue (aoqin leaks)
Country: Pakistan | Employees: 2440 | Revenue: $402,000,000 | Data: 710 GB | Type: Contracts, clientsData, confidential, banking, personal, Incidents | Data publication: 2026-11-23 | Status: not_paid Airblue Limited is…
SRC // RansomLook — Recent Posts -
Android’s Clipboard Warning Can Be Hidden, and Google Has Closed the Report
Any Android app you open can read what you just copied and hide the system’s warning, a developer showed. Google closed his report without a fix date.
SRC // Privacy Affairs -
Researchers continue to find serious vulnerabilities in internet connected refrigerators
VulnCheck disclosed 14 vulnerabilities in Dixell refrigeration units that give an attacker root access, while online honeypots are being flooded with hacks and malicious probes. The post Researchers continue to…
SRC // CyberScoop -
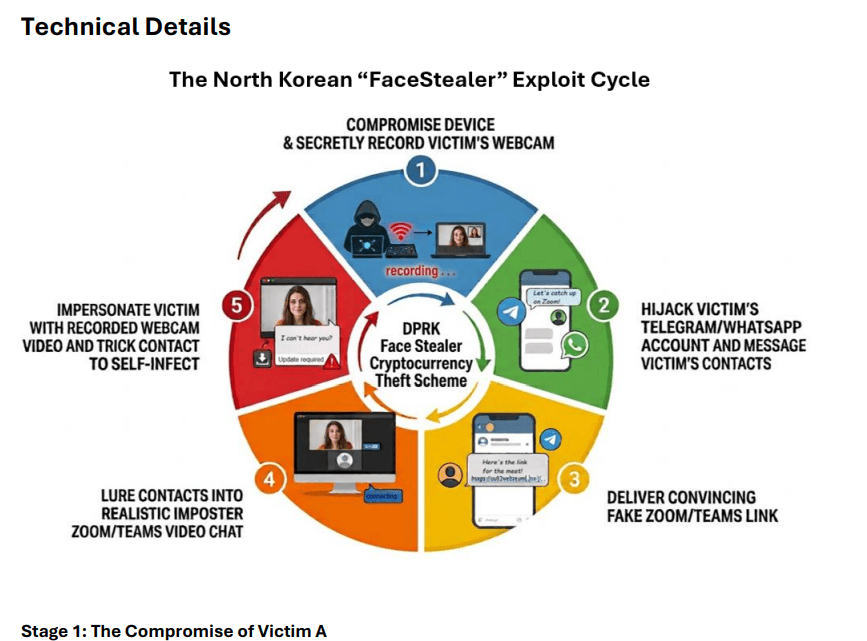
North Korea ‘s Crypto Theft Operations: DOJ Seizes $1.2 Billion and Disrupts Hacker Infrastructure
The DOJ seized over $1.2 billion from North Korea ‘s Binance theft, and says the same hackers are targeting open-source developers The U.S. Department of Justice announced two separate but…
SRC // Security Affairs -
GHSA-gpwc-27cw-rh9r: NLTK: Quadratic CPU exhaustion in LegalitySyllableTokenizer.tokenize via unguarded onset reversal loop
Severity: MEDIUMEcosystems: pipPackages: nltk## Summary `LegalitySyllableTokenizer.tokenize` in the NLTK tokenizer package contains an unguarded O(n^2) processing loop. When the method is called on a single token that consists of a…
SRC // GitHub Security Advisories -
GHSA-ffr9-mgrr-wcvr: NLTK: Quadratic CPU exhaustion in TreebankWordTokenizer.span_tokenize via list.pop(0) in quote-restore loop
Severity: MEDIUMCVE: CVE-2026-126300Ecosystems: pipPackages: nltk## Summary `TreebankWordTokenizer.span_tokenize` in the NLTK tokenizer package contains an unguarded O(n^2) processing loop in its quote-restoration step. When the method is invoked on text containing…
SRC // GitHub Security Advisories -
GHSA-8fx7-8jr8-84rv: NLTK: Unbounded CPU consumption in SteppingRecursiveDescentParser.parse() with ambiguous or self-embedding grammars
Severity: HIGHCVE: CVE-2026-126303Ecosystems: pipPackages: nltk## Summary `nltk.parse.recursivedescent.SteppingRecursiveDescentParser.parse()` performs an unbounded top-down search over ambiguous or self-embedding context-free grammars with no wall-clock or step limit. An actor who can influence the…
SRC // GitHub Security Advisories -
GNSS Spoofing and Jamming: What They Do to RTK Positioning and How Field Teams Can Spot Them
Satellite positioning can fail even when a rover appears normal. Its fixed solution may disappear or its coordinates…
SRC // HackRead -
ARTEX and beyond: AI-enabled penetration testing platforms
AI-enabled penetration testing and red team frameworks can automate and chain reconnaissance, vulnerability testing, and follow-on actions, lowering the skill threshold for attackers and accelerating intrusions when the tools are…
SRC // Cisco Talos Intelligence