ARCHIVE
Security News
-
Hijacked email accounts complicate investigations into European bomb hoaxes
Bomb threats sent to thousands of schools across Europe this week came from a compromised email account at a Taiwanese university, the latest incident in a series of hoax threats…
SRC // The Record -
Apify rotates API tokens, prompts 2FA resets after breach
Apify has rotated critical internal secrets and revoked some third-party OAuth connections after detecting unauthorized access to its internal systems. [...]
SRC // BleepingComputer -
Hacked Asian Telcos Used to Intercept Taiwanese Calls and Texts
Enea linked SilentAir and Liminal Panda to attacks on Asian mobile operators
SRC // Infosecurity Magazine -
LEGO’s BrickLink taken offline: What users should know
BrickLink, the LEGO marketplace, has gone offline after detecting unusual activity, without disclosing whether customer data was affected.
SRC // Malwarebytes Labs -
Lego Takes BrickLink Marketplace Offline After Detecting Unusual Activity
Lego has taken its BrickLink Marketplace offline after detecting unusual activity as the company investigates the incident
SRC // Infosecurity Magazine -
Apple’s HomeView Tries Face Authentication Without FaceID
Apple’s FaceID has long provided robust authentication. But for its smart home device, HomeView, the company is betting on new “person recognition” technology that has yet to be challenged in…
SRC // WIRED Security -
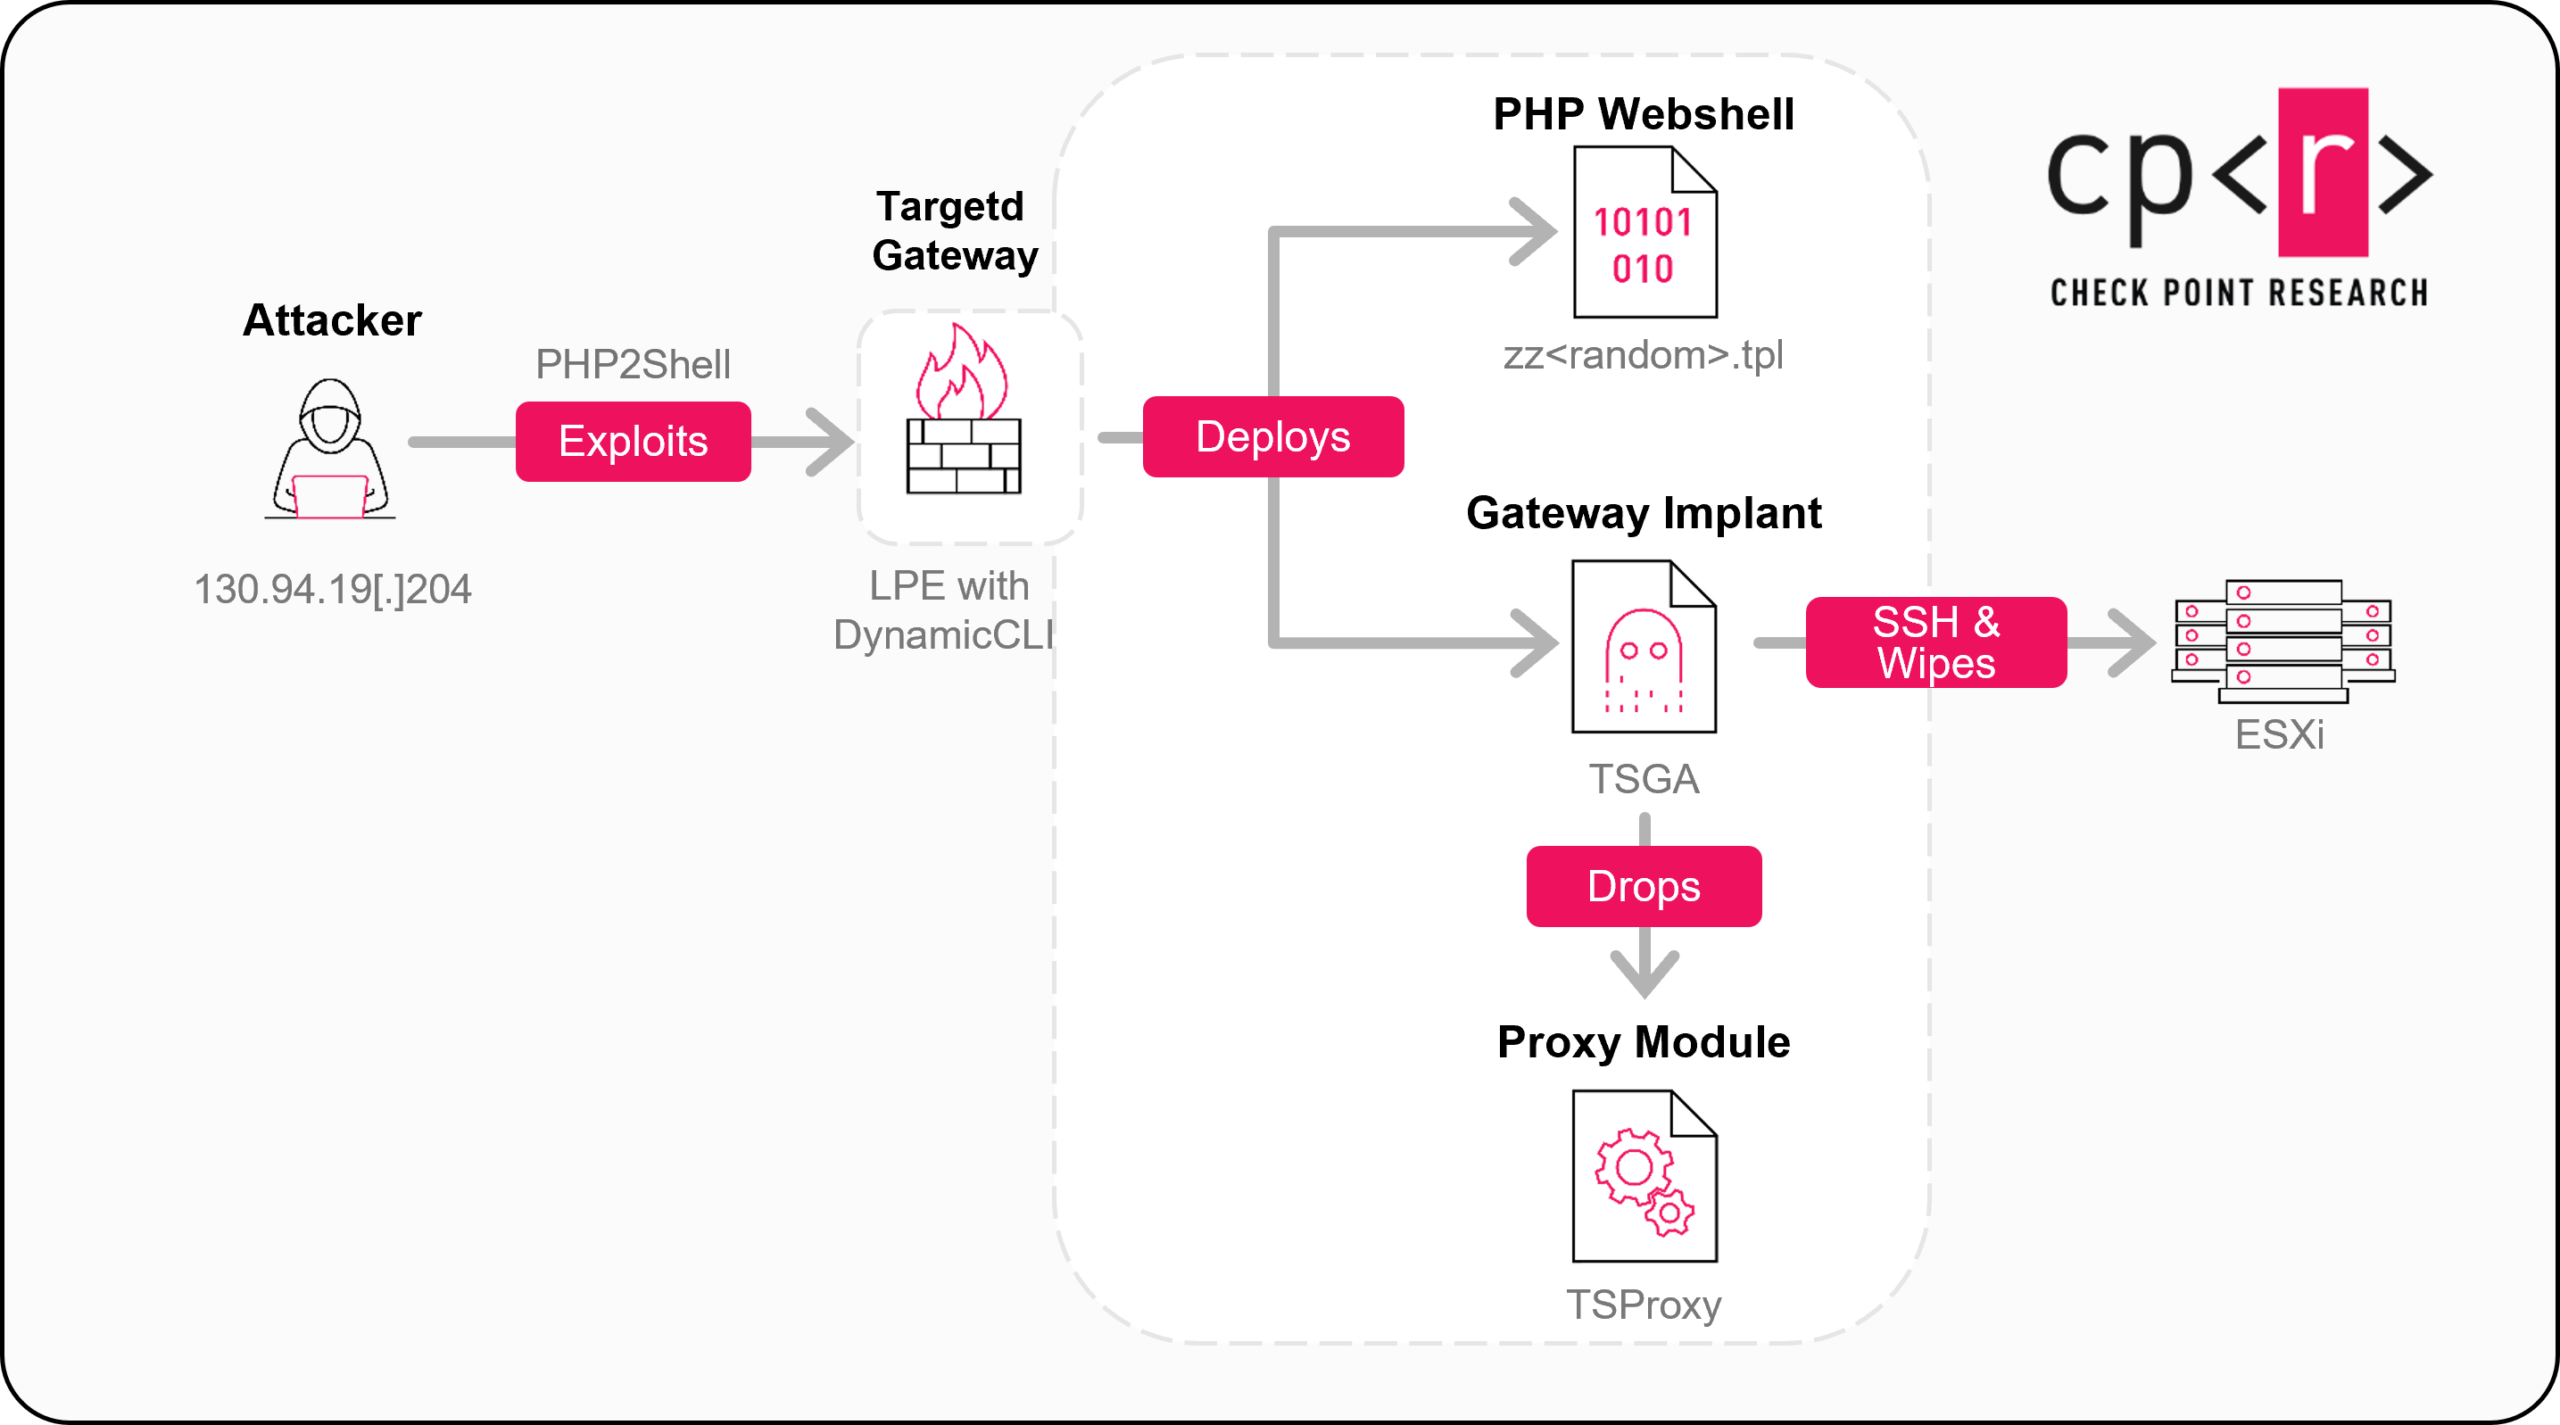
PHP2Shell Exploitation on Check Point Gateway
Key findings Introduction We have now confirmed that, in late October 2026, approximately one week after a security fix became available, activity originating from 130.94.19[.]204 targeted Israeli organizations through vulnerable…
SRC // Check Point Research -
Chrome, Firefox Updates Patch Over 180 Vulnerabilities
Google fixed 83 flaws with a new Chrome 157 release, and Mozilla addressed 99 bugs in Firefox 160. The post Chrome, Firefox Updates Patch Over 180 Vulnerabilities appeared first on…
SRC // SecurityWeek -
Attacker Targets 60,000 GitHub Repositories in Credential Theft Campaign
Using thousands of hijacked accounts, the wfx-loot campaign planted a CI secret stealer that ran in over 1,800 GitHub repositories. The post Attacker Targets 60,000 GitHub Repositories in Credential Theft…
SRC // SecurityWeek -
Operation Endgame malware takedown turns up over 6 million stolen logins
Police in nine countries, working with Europol, took down servers behind the Gootloader, CastleRAT and StealC malware operations this week and recovered more than 6 million credentials stolen from infected…
SRC // Help Net Security