ARCHIVE
Security News
-
International operation dismantles malware networks, exposes 6.4 million stolen credentials
The Operation Endgame action dismantled the loaders, remote access trojans and infostealers that give ransomware gangs their way into corporate networks. The post International operation dismantles malware networks, exposes 6.4…
SRC // CyberScoop -
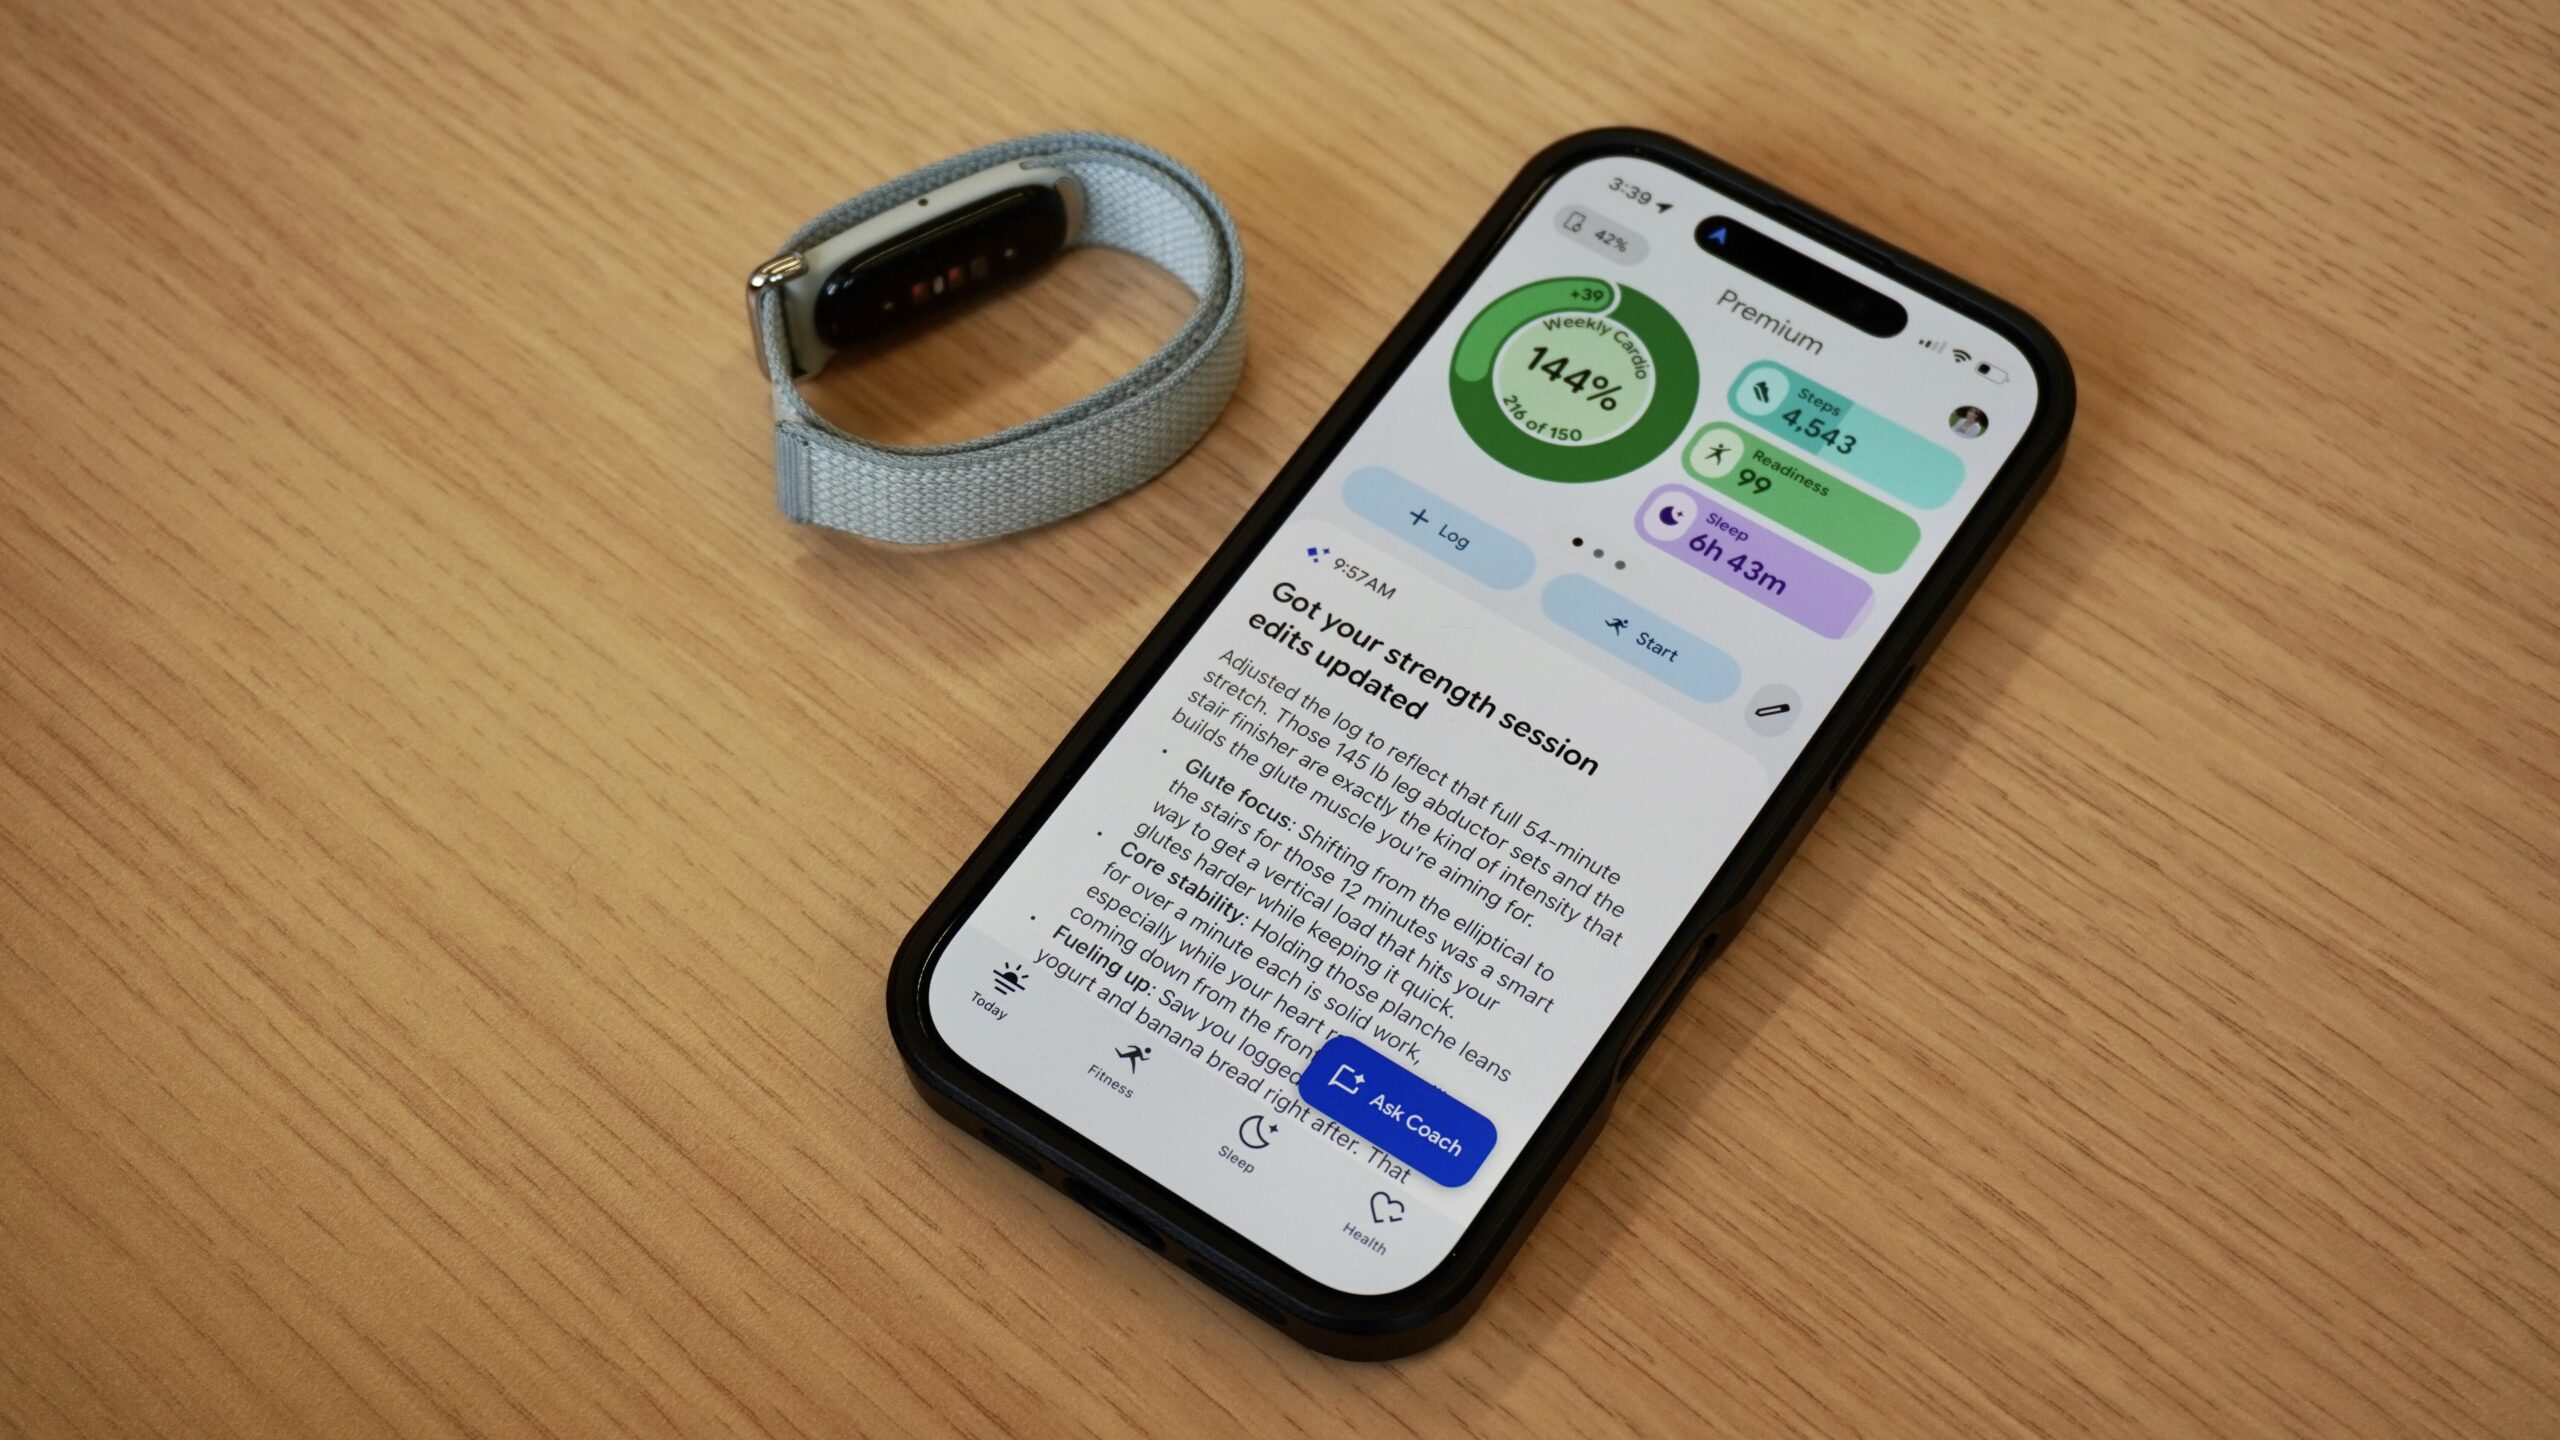
Fitbit users can’t see Google Health metrics after update – how to fix it
Google says it’s working on a fix – meantime, users have found workarounds.
SRC // ZDNet Security -
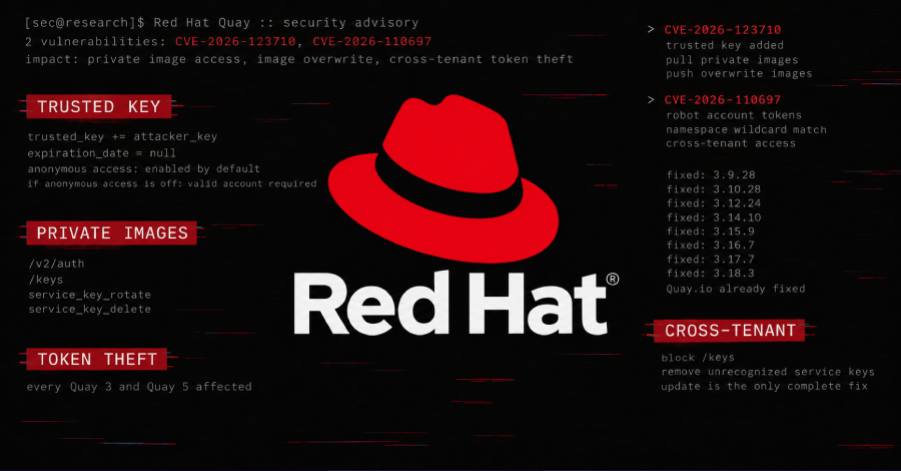
Critical Red Hat Quay Flaw Lets Attackers Read and Overwrite All Private Container Images in a Registry
A critical flaw in Red Hat Quay allows an attacker who can access a Quay registry to read and overwrite private container images in every repository. Quay enables anonymous access…
SRC // The Hacker News -
European authorities take down SteaIC malware servers for second time this year
German authorities on Thursday said investigators traced the rebuilt network to the Virtualine bulletproof hosting provider, seized by the FBI in October, with the assistance of police in Frankfurt and…
SRC // The Record -
ConnectWise investigates ScreenConnect breaches after reports of incidents at nearly 50 organizations
Abuse of an independent third-party tool led to breaches at ScreenConnect customers, confirmed the software's maker, ConnectWise. Cybersecurity researchers had spotted intrusions at nearly 50.
SRC // The Record -
New Windows SignDrop zero-day gives hackers SYSTEM privileges
Security researcher Abdelhamid Naceri (also known as Nightmare Eclipse) has released a new Windows zero-day exploit that can let attackers gain SYSTEM privileges. [...]
SRC // BleepingComputer -
Weak Passwords Expose SQL Servers to Cryptominer and Gh0st RAT
Fortinet finds weak SQL Server passwords used to deliver a miner and Gh0st RAT
SRC // Infosecurity Magazine -
Citrix Patches 12 NetScaler and Secure Access Client Flaws, Including Authentication Bypass
Citrix has released patches for multiple critical security flaws impacting NetScaler ADC, Citrix NetScaler Gateway, and NetScaler Console that could lead to denial-of-service (DoS) or an authentication bypass. The critical…
SRC // The Hacker News -
Apache Patches Critical HTTP Server RCE Found by Anthropic, Google
The mod_http2 race condition, CVE-2026-119618, could let unauthenticated attackers execute code on servers with HTTP/2 enabled. The post Apache Patches Critical HTTP Server RCE Found by Anthropic, Google appeared first…
SRC // SecurityWeek