There must have been red faces in the social media department of Ireland’s police headquarters after two of its accounts were hijacked this week.
Read more in my article on the Hot for Security blog.
Source: Graham Cluley · 2026-10-16
There must have been red faces in the social media department of Ireland’s police headquarters after two of its accounts were hijacked this week.
Read more in my article on the Hot for Security blog.
Source: Graham Cluley · 2026-10-16
Unit 42 details the top initial access vectors adversaries use to breach organizations, led by edge exploits, credential abuse and phishing
Source: Palo Alto Networks Unit 42 · 2026-10-16
Krybit is a fast-growing ransomware gang that was hacked by a rival, hit back, and is still extorting victims. Find out how it works, who it has targeted, and what organisations can do to protect themselves.
Read more in my article on the Fortra blog.
Source: Graham Cluley · 2026-10-16
If you’re suddenly being overwhelmed with sign-up emails, it could very well be a sign of something more serious
Source: WeLiveSecurity (ESET) · 2026-10-16
Our analysis an AI-powered espionage campaign targeting government Linux infrastructure with custom malware, web shells, and advanced credential theft.
Source: Palo Alto Networks Unit 42 · 2026-10-15
Welcome to this week’s edition of the Threat Source newsletter.
I’ve been following a lot of (sometimes heated) threads and discussions lately about the current vulnerability landscape. I learned new words/phrases such as Summer of Hell (although I’m writing this with 1°C/34°F outside), Vulnpocalypse, Bugmageddon, Bugpocalypse, Breachpocalypse…
Let’s look at some numbers:
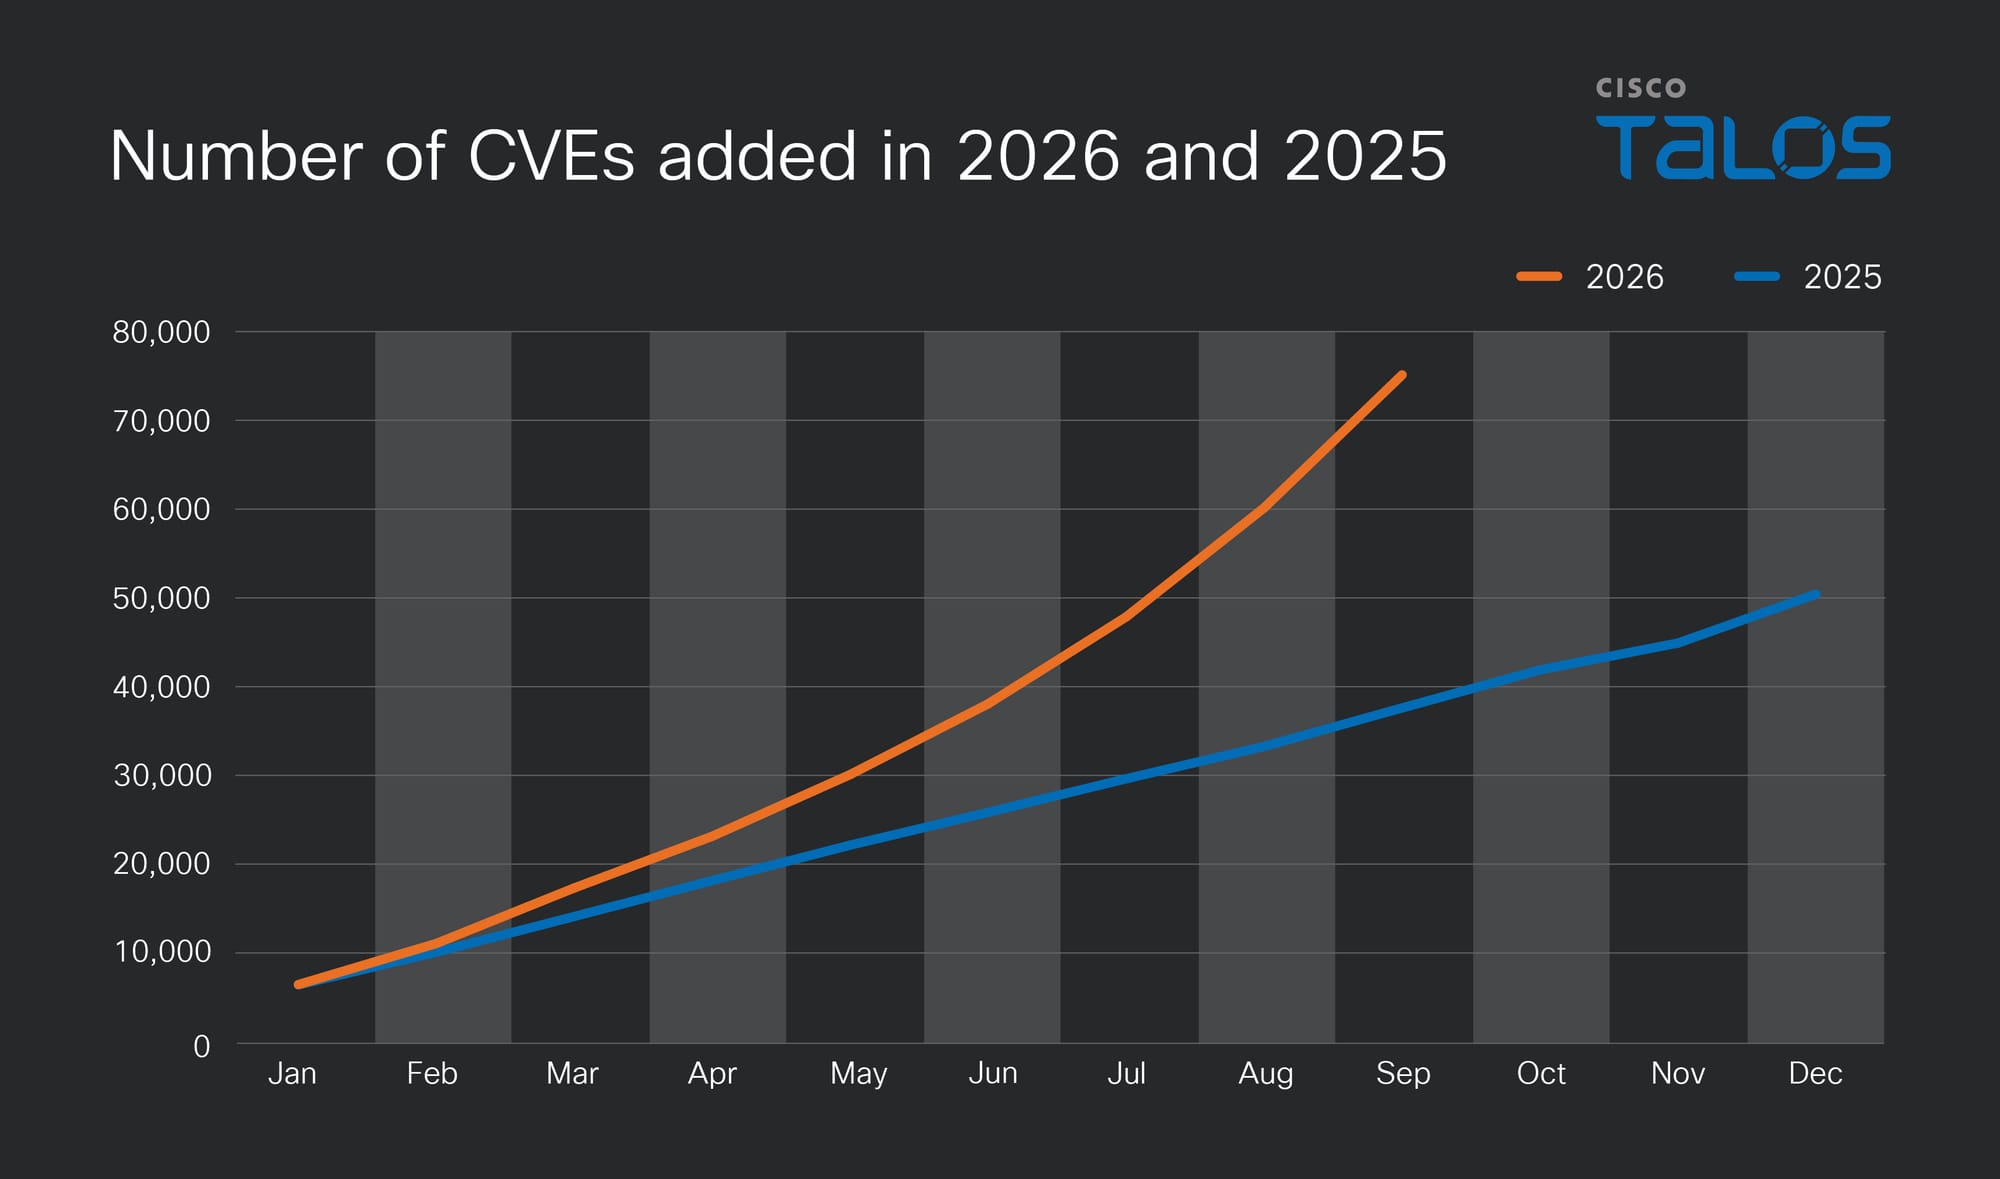
We crossed the 70k mark, and it’s only the end of September. This has never been seen before — I think we can agree this number is skyrocketing. Also, CVE numbering organically grew into the six-digit range. Check your tooling. Some might say we broke that barrier already in 2014 (CVE-2014-125110), or even hit seven digits in 2015 (CVE-2015-1000013), but those were allocated artificially. (History note: Before 2014, 9999 was the highest possible identifier.)
So that could be seen as the apocalypse argument. On the other hand, we have the KEV numbers:
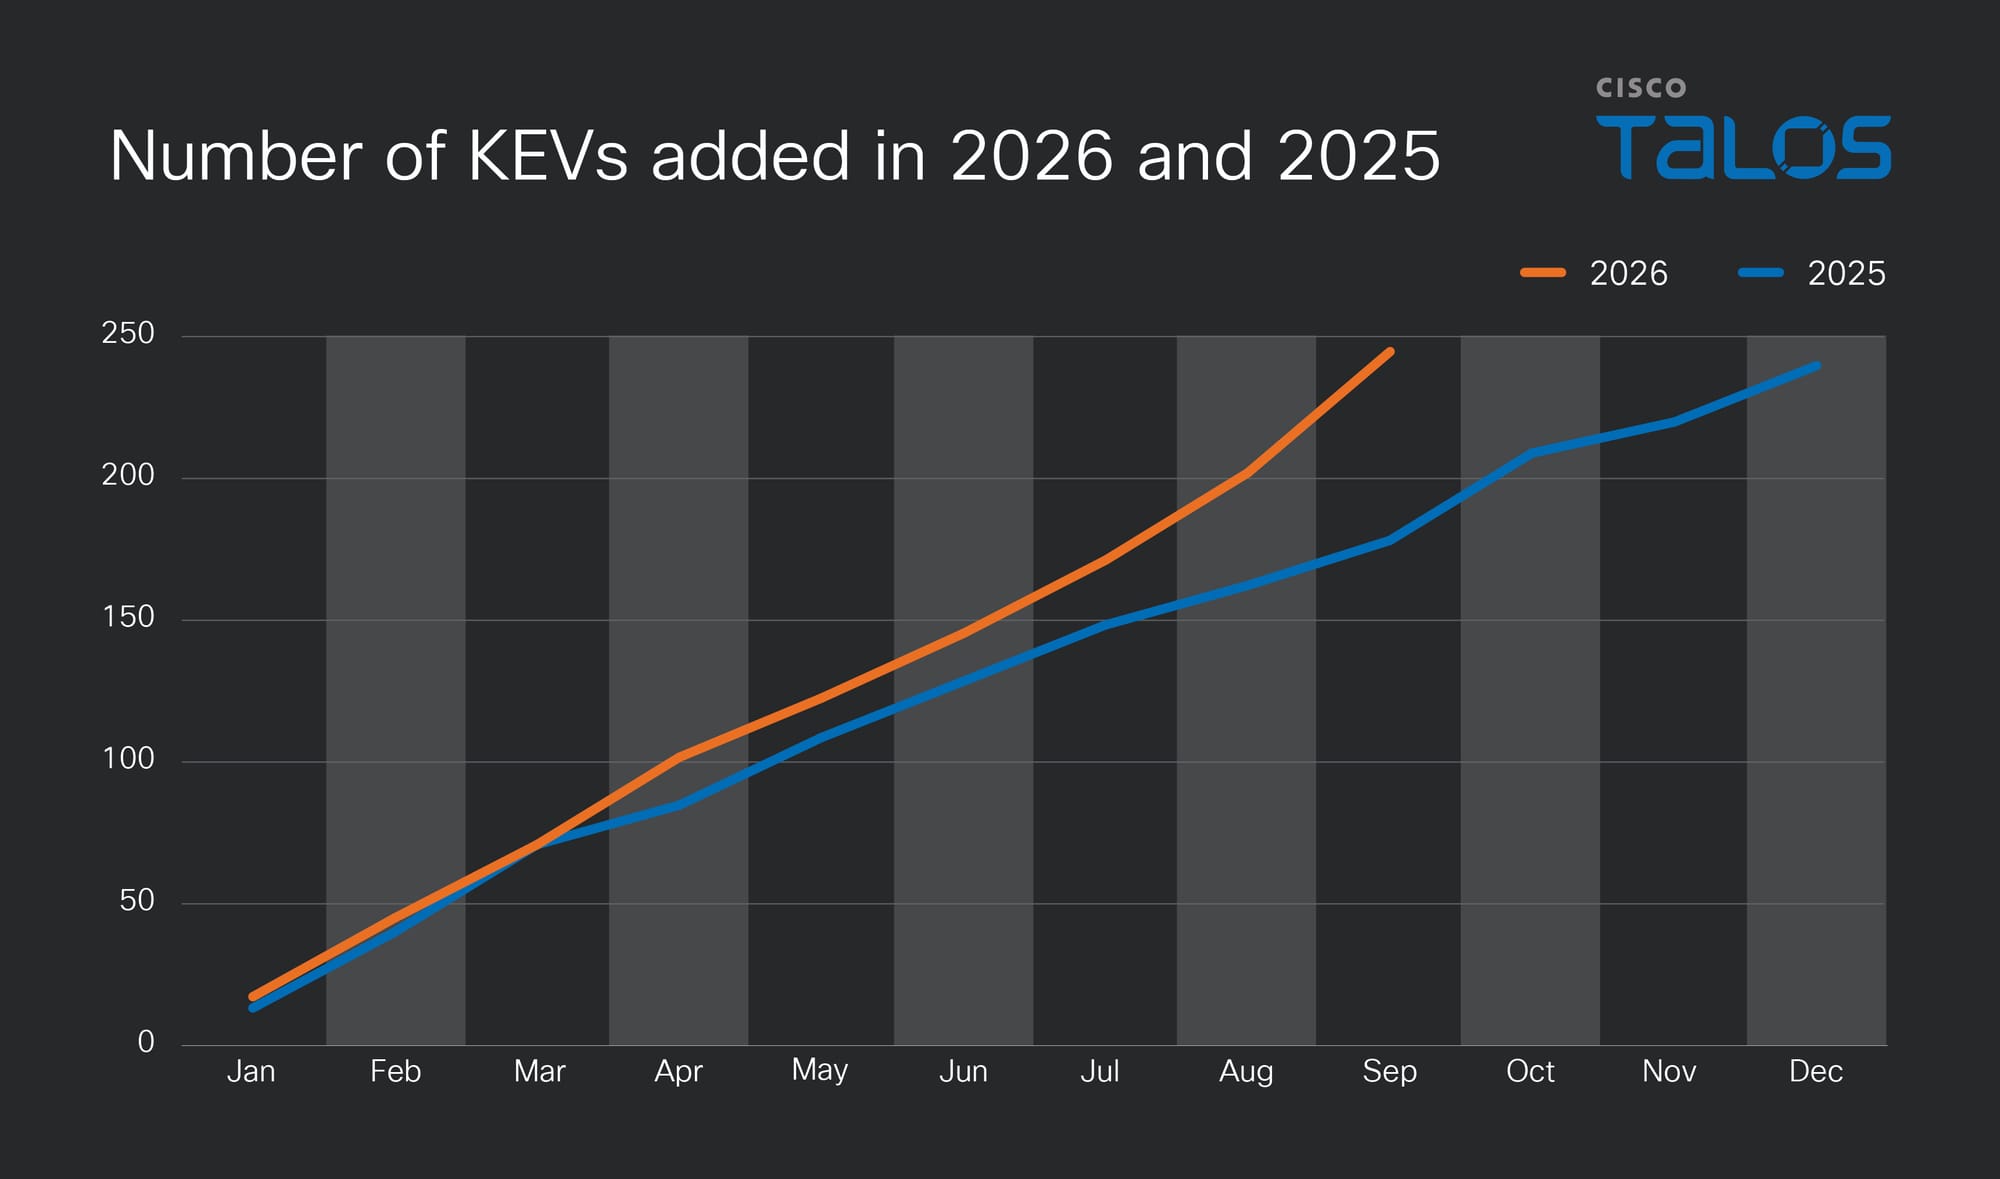
They didn’t explode… yet? Counting by sheer volume, YoY, CVEs increased by 105%, while KEV only grew 37%. Sounds huge at first, but following a 30% increase from 2024 to 2025, that’s less dramatic — a counter-argument of sorts.
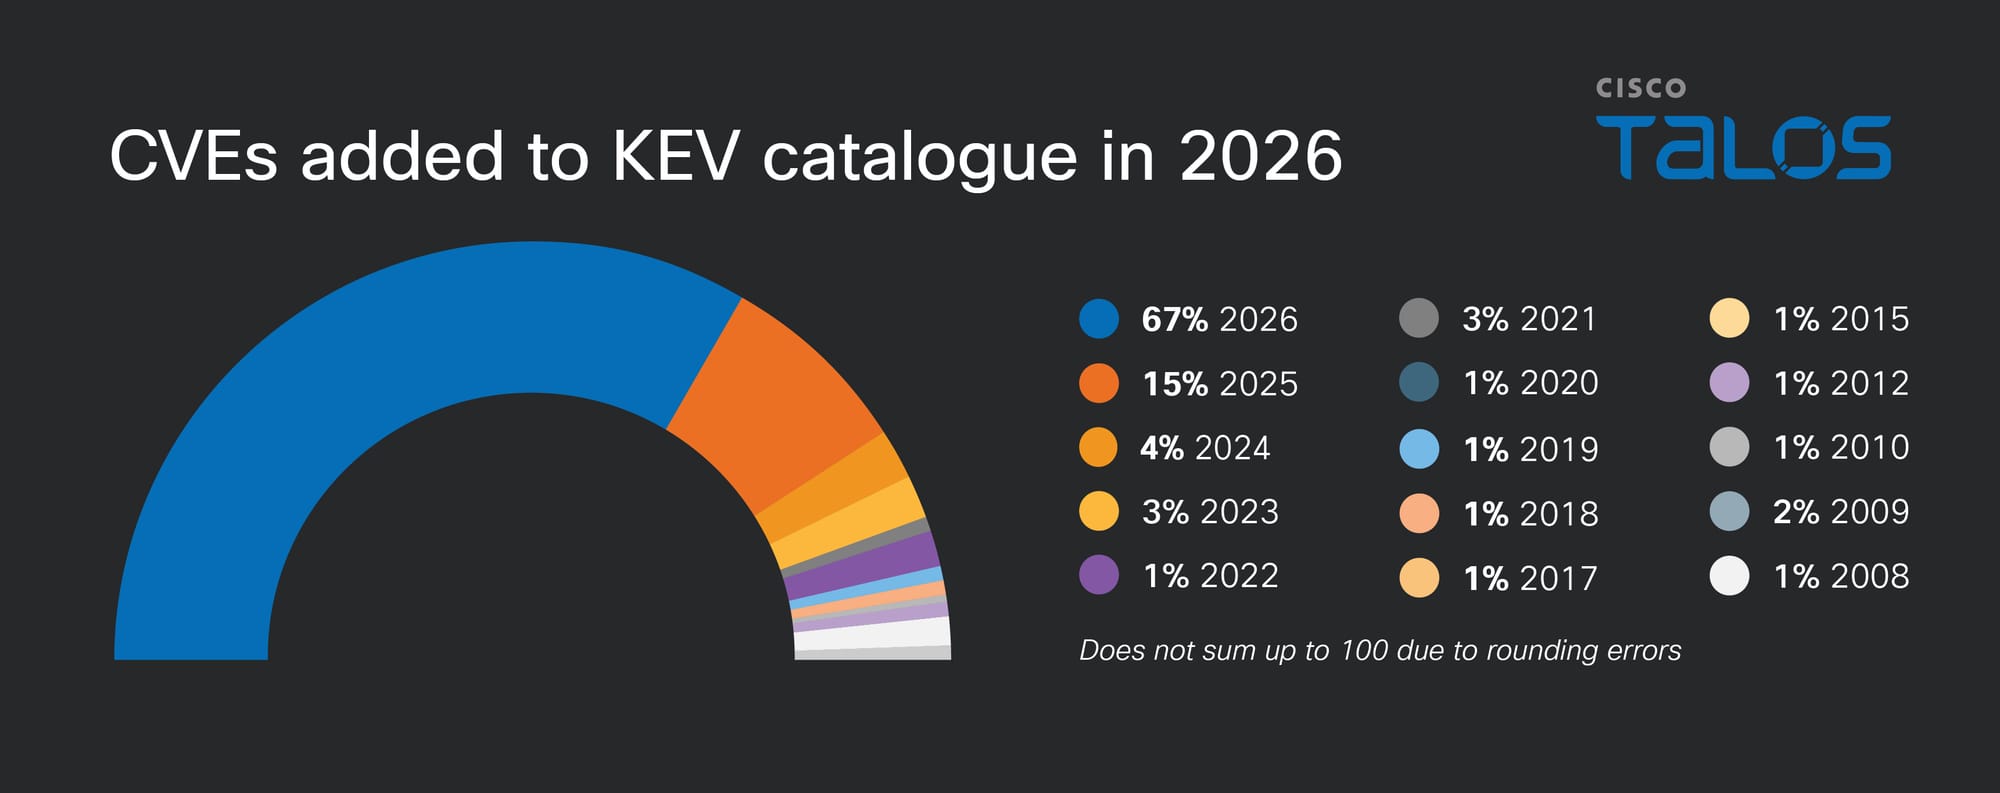
CVEs from 2025 or older still account for 33%. In other words, a good third of the KEVs are suggesting there is a patch gap. Looking at the 2026 CVEs, the share where the publication date matches the date added to KEV is 29%, which is only 2% more than (all of) 2025. Acknowledging this “math” is not the whole ball of wax, but it still tells me we are not living in a zero-day apocalypse right now. There’s also a slight uptick in networking gear-related CVEs, to 27%.
This is the second time I’ll ask you to check your tooling. A new column, “forensicTriage,” was added to the KEV to flag which high-risk vulnerabilities require mandatory forensic triage and incident response workflows. You can read more about it in BOD 26-04, or the Implementation Guidance.
So where does that leave us? The CVE numbers alone — that +70k mark, now that Q3 is behind us — make a decent case for Vulnpocalypse, or whichever name you prefer. That part of the story is real. But discovery isn’t exploitation, and that gap is exactly what the KEV numbers remind us of. Vendors seem to be keeping pace too, at least partially — KEV is growing, just not nearly at CVE’s speed, which on its own would almost be good news.
Where the story breaks down is on the practical side. More than a third of actively exploited vulnerabilities still trace back to 2025 or earlier. Patch debt doesn’t care how many new apocalypse-themed hashtags we invent.
So, panic? I still don’t think so. Relax? Definitely not either. Somewhere between the two is where the real work sits — chipping away at that backlog, one legacy system at a time. Maybe by next quarter it’ll feel less like Bugmageddon and more like business as usual. Or maybe I won’t even need a warmer jacket for the upcoming “Winter of Hell.”
Cisco Talos and Recorded Future’s Insikt Group are disclosing new espionage activity from UAT-6275 targeting government and critical infrastructure across the Commonwealth of Independent States (CIS). Thanks to the threat actor’s own operational security lapses, researchers gained direct visibility into their infrastructure and malware development. We observed four distinct infection chains delivering custom reverse shells via macro-enabled documents, GitHub-hosted scripts, and a WinRAR vulnerability.
Regional government and critical infrastructure entities are actively being targeted for diplomatic and economic intelligence. UAT-6275 is consistently evolving its tradecraft, abusing legitimate platforms like GitHub to host payloads and deploying lightweight reverse shells. Furthermore, recovered tooling suggests the group is preparing to expand its reach into Linux hosts and internet-facing appliances.
Defenders in targeted regions and sectors should monitor for unexpected PowerShell activity and payload downloads originating from public services like GitHub. It is also critical to watch for suspicious scheduled tasks and unauthorized changes to the Windows Startup folder, which this group uses for persistence. Finally, ensure archive utilities are fully patched to prevent exploit-assisted delivery. ClamAV signatures and indicators of compromise (IOCs) to detect this threat can be found in the full blog post.
Hackers heat supermarket fridges to 50°C in France cyber attack
The attack began overnight from Sunday to Monday. The unknown attackers reportedly abused the defrosting function in older control software, setting some equipment to heat continuously, with temperatures said to have reached 50°C. (Hack Read)
Ivanti zero-day chain gave attackers root access to fully patched VPN
CVE-2026-104935 affects Ivanti Connect Secure and it can be exploited for unauthenticated remote code execution with elevated privileges. (SecurityWeek)
U.S. arrests two in crackdown on North Korean IT worker laptop farms
As part of the scheme, which allegedly ran between 2019 and July 2025, the two housed and configured laptops issued by victim U.S. companies so ITWs would appear to work from the U.S. (SecurityWeek)
Canadian cybersecurity executive arrested in U.S. federal extortion case
While the FBI did not publicly announce Dubrovsky’s arrest, the case appears to align with actions taken in the wake of the ShinyHunters’ attack on the FBI’s IT systems, which exposed personal data about thousands of bureau employees. (CyberScoop)
Maximum-severity SSRF flaw in SonicWall SMA devices under attack
The vulnerability, which SonicWall assigned a maximum 10 out of 10 CVSS score, stems from an “unintended alternate access path,” according to the vendor’s advisory. (Dark Reading)
You’ve got to lurk before you can smirk
How do you get under a cybercriminal’s skin? Sometimes you expose their operations. Sometimes you make every step through a network painfully slow. And sometimes, if you’re Azim, you join a dark web forum where they’re insulting you, and help them to do it.
Microsoft Patch Tuesday for October 2026
Microsoft has released its monthly security update for October 2026, which includes 1,415 vulnerabilities affecting a range of products, including 85 that Microsoft marked as “critical.”
One breach, please, and make no mistakes
The cybersecurity community has seen examples of autonomous agents, built inside AI labs, attacking public infrastructure. How you prepare for agentic threats is what makes the difference during real incidents.
SHA256: 9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507
MD5: 2915b3f8b703eb744fc54c81f4a9c67f
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=9f1f11a708d393e0a4109ae189bc64f1f3e312653dcf317a2bd406f18ffcc507
Example Filename: sample.exe
Detection Name: W32.9F1F11A708-100.SBX.TG**
SHA256: 73ac1bbfaee6c76c34f655ac0477a4cd930f2aa55e658c8e312ff81aac9a741f
MD5: 63f3351cfdf618bec6045f60203e7978
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=73ac1bbfaee6c76c34f655ac0477a4cd930f2aa55e658c8e312ff81aac9a741f
Example Filename: f_00478d.exe
Detection Name: W32.PUP:PulseBrowser.29kh.in12.Talos
SHA256: 58d6fec4ba24c32d38c9a0c7c39df3cb0e91f500b323e841121d703c7b718681
MD5: f1fe671bcefd4630e5ed8b87c9283534
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=58d6fec4ba24c32d38c9a0c7c39df3cb0e91f500b323e841121d703c7b718681
Example Filename: KMSAuto Net.exe
Detection Name: W32.58D6FEC4BA-95.SBX.TG
SHA256: fed979f93bcaf4e73ebd25748093a92095d5109cbd01d55f97bdc50ce509ad2f
MD5: 207d9d891ac756b2bfad88aba5682c65
Talos Rep: https://talosintelligence.com/talos_file_reputation?s=fed979f93bcaf4e73ebd25748093a92095d5109cbd01d55f97bdc50ce509ad2f
Example Filename: sample.exe
Detection Name: W32.FED979F93B-95.SBX.TG
Source: Cisco Talos Intelligence · 2026-10-15
Researchers at The Citizen Lab have for the first time released technical evidence of sophisticated mercenary spyware being distributed via online advertising.
Source: WIRED Security · 2026-10-15
A ransomware negotiator attended a cybersecurity conference, only to be arrested by the FBI in connection with its investigation into the ShinyHunters gang.
Meanwhile, hackers get the keys to ASOS’s app and the chance to message every single customer. What did they say? And how did the company respond? We have thoughts.
All this and more is discussed in episode 488 of the “Smashing Security” podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Paul Ducklin.
Source: Graham Cluley · 2026-10-14
We investigated an intrusion where attackers exploited CVE-2024-47575 to target 500+ firewalls and deploy PEERSTITCH, a memory-resident ARM64 malware.
Source: Palo Alto Networks Unit 42 · 2026-10-14
The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud and cybercrime services that are helping Russia circumvent existing financial restrictions.
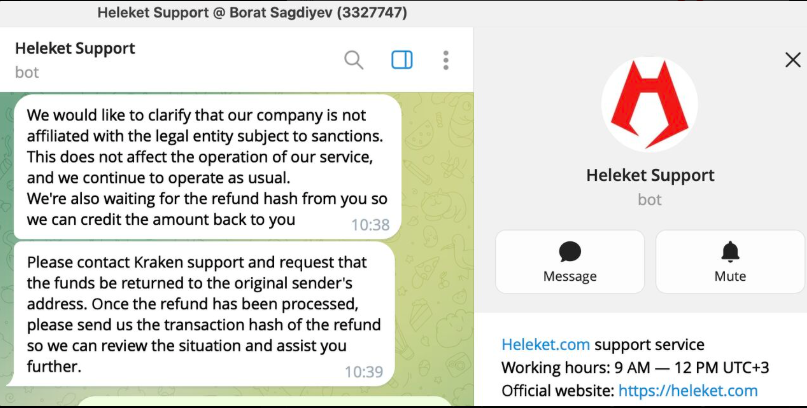
Heleket’s support agent on Telegram claims, despite all evidence to the contrary, that it is not affiliated with Cryptomus. Image: Richard Sanders.
On October 8, the U.K. issued sanctions (PDF) against Cryptomus — previously known as Certa Payments and Xeltox Enterprises — for processing payments that benefit the Russian government and its financial institutions. The sanctions freeze any Cryptomus assets at U.K. banks, and bar British companies from offering it any business, virtual or otherwise. Also targeted in these sanctions were the virtual payment platforms VexPay, TokenSpot, and the Tsunami Payments service.
As explained in our December 2024 investigation, “How Cryptocurrency Turns to Cash in Russian Banks,” Cryptomus has been a key payment processor for dozens of Russian cryptocurrency exchanges and websites hawking cybercrime services. The company has changed its name several times since emerging in 2022, most recently to “Heleket” last year after Canada levied a record CAD $176 million fine against the platform for anti-money laundering violations.
The blockchain data-crunching firm Chainalysis said the U.K. sanctions target the broader infrastructure supporting Russia’s wartime economy.
“Cryptomus and Heleket have emerged as major payment hubs for illicit activity,” Chainalysis wrote in an October 8 blog post. “Together, these services received more illicit funds across tracked categories than the mixers in our dataset and the number of illicit counterparties surged to more than 900 in a single month in late 2025.”

The Cryptomus support bot on Telegram, responding on Oct. 8 to an inquiry by saying the platform was suddenly unable to process transactions.
In April 2026, the blockchain analysis firm TRM Labs found Cryptomus had processed more than $7 billion in transactions since its inception in 2022, including transactions associated with child sexual abuse material vendors, terrorist financing networks, and human trafficking operations.
TRM noted that Cryptomus’s transaction volume cratered after the platform instituted new “know your customer” or KYC rules, and that the cryptocurrency platform responded to the Canadian fines by launching Heleket as a parallel service that continued to offer no-KYC payment processing.
Richard Sanders is a blockchain analyst and investigator who spent months mapping out Cryptomus’s payment infrastructure and transacting with its customers. Sanders said the U.K. sanctions on Cryptomus are important because Canada’s fine against the platform was ultimately unenforceable and uncollectible.
“A fine doesn’t stop a cryptocurrency payment processor from processing payments,” Sanders wrote on LinkedIn. “Sanctions kill the operation. The distinction matters.”
As our 2024 investigation noted, Cryptomus shared a Vancouver address with dozens of other foreign currency dealers and money transfer businesses — none of which appeared to be physically located there. Following the CAD $176 million fine for alleged money laundering violations, Cryptomus appealed the penalty, launched Heleket as a parallel service, and kept on processing large volumes of sketchy transactions, Sanders said.
Sanders said the sanctions also are notable because they are the first known instance of a “Five Eyes” country (referring to the Australia, Canada, New Zealand, the U.K. and the U.S.) sanctioning a cryptocurrency operation incorporated in another Five Eyes jurisdiction.
Where do entities like Cryptomus and Heleket derive their authority to offer international financial services? The answer appears to involve fake financial institutions overseen by a phony regulatory body positioned in a country that is not widely recognized as a sovereign nation.
Our 2024 investigation found the sole shareholder of Cryptomus’s parent company Certa Payments was a 25-year-old Ukrainian woman who also headed several other firms, including the WS Management and Advisory Corporation, which bills itself as the regulatory body that exclusively oversees licenses for cryptocurrency, foreign exchange and online gaming businesses incorporated in the disputed region in northwest Africa known as the Western Sahara.
That entity’s website — crasadr.com — says it assists applicants with bank setup and formation, online gaming licenses, and the creation and licensing of foreign exchange brokers. One of Certa Payments’ former sites — certa[.]website — also shared a server with 12 other domains, including rasd-state[.]ws, a website for the Central Reserve Authority of the Western Sahara.
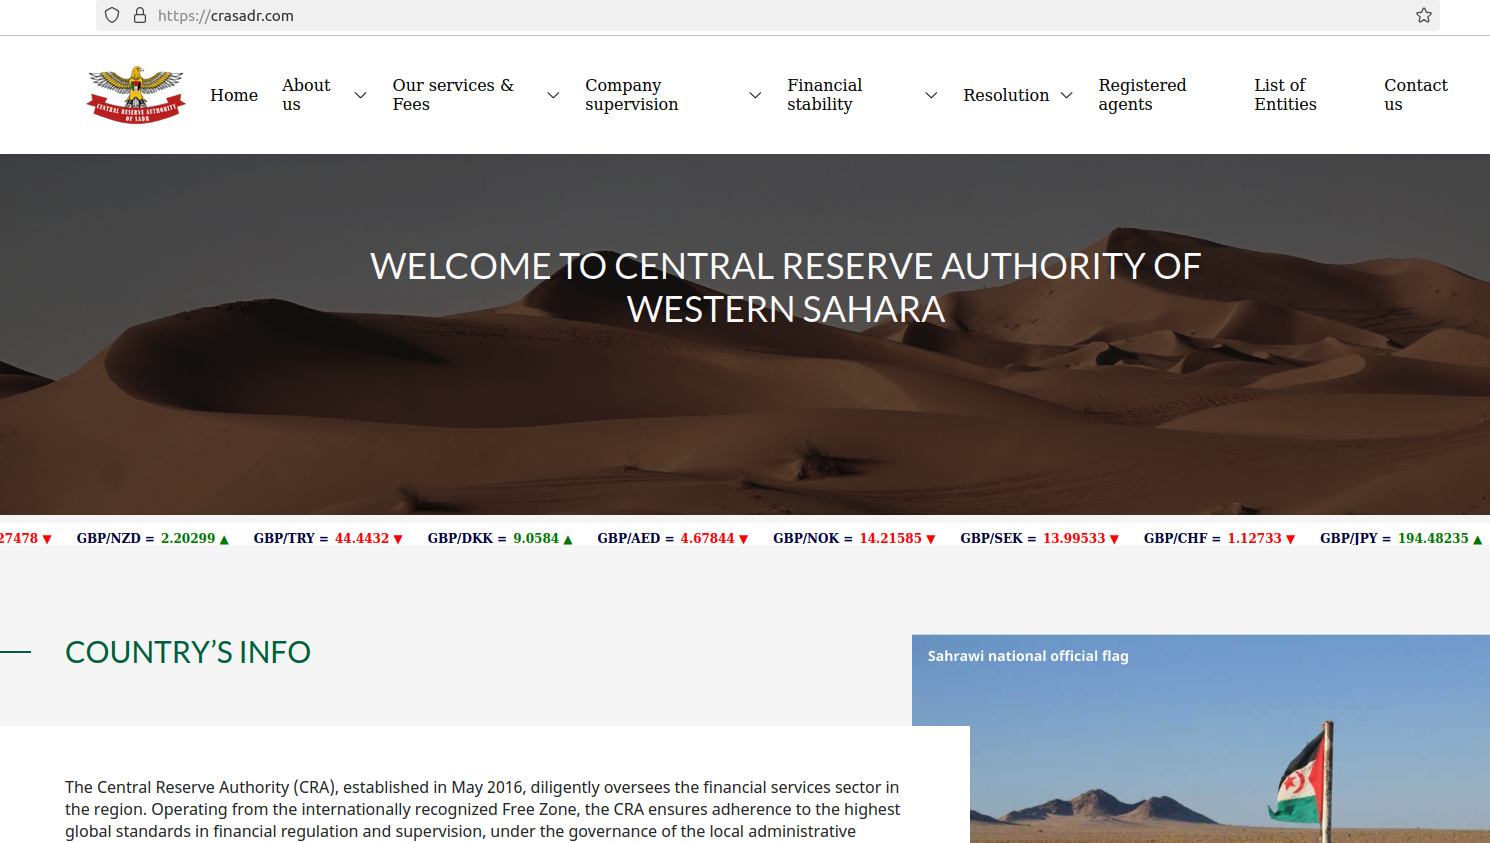
The website crasadr dot com, the official website of the Central Reserve Authority of Western Sahara, which lists the entities awarded licenses for cryptocurrencies, gaming and foreign exchange services.
Source: Krebs on Security · 2026-10-14