ARCHIVE
Security News
-
U.S. CISA adds Perforce Puppet Enterprise flaw to its Known Exploited Vulnerabilities catalog
U.S. CISA adds Perforce Puppet Enterprise vulnerability CVE-2026-115731 to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Perforce Puppet Enterprise flaw, tracked as CVE-2026-115731…
SRC // Security Affairs -
Hackers Exploiting Critical Puppet RCE Flaw Affecting Enterprise Management Servers
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added a critical security flaw impacting Perforce Puppet, an enterprise infrastructure-as-code (IaC) and configuration management platform, to its Known Exploited…
SRC // The Hacker News -
CISA Urges Immediate Patching of Java4Shell Flaw That Could Allow Remote Code Execution
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has urged organizations to immediately patch a newly disclosed critical security flaw impacting Oracle Java. The flaw, tracked as CVE-2026-114938 (CVSS score:…
SRC // The Hacker News -
British Scattered Spider hacker sentenced to 6 years in prison
A leader of the Scattered Spider cybercrime collective has been sentenced to six years in prison in the United States for stealing millions in cryptocurrency and conspiring to hack a…
SRC // BleepingComputer -
Java4Shell Vulnerability Puts Many Enterprise Applications at Risk of Takeover
Calif demonstrated remote code execution in Jira, Jenkins and Keycloak, while VulnCheck says real-world RCE requires per-target work The post Java4Shell Vulnerability Puts Many Enterprise Applications at Risk of Takeover…
SRC // SecurityWeek -
Deutsche Telekom IoT’s CEO on securing devices that run for 20 years
In this Help Net Security interview, Christian Schwalbe, CEO of Deutsche Telekom IoT, talks about the forgotten devices that create the most risk in IoT deployments. He explains what the…
SRC // Help Net Security -
The forced audit: how AuditTeam’s OpsAgent framework masks ransomware as consulting
How does a ransomware gang sell a “forced audit”? We break down AuditTeam’s OpsAgent implant, its Rust rewrite, and the extortion model demanding a consulting fee to delete stolen data.
SRC // Securelist (Kaspersky GReAT) -
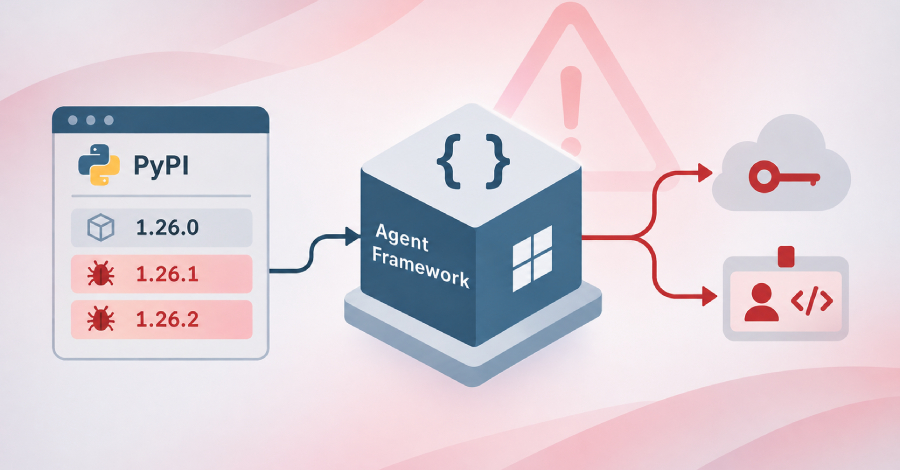
Attackers Compromise Microsoft’s Agent Framework PyPI Package to Steal Cloud Credentials
Threat actors have compromised Microsoft's agent-framework package to push a credential stealer, according to reports from Aikido, Chainguard, Endor Labs, OX Security, SafeDep, Socket, StepSecurity, and Google-owned Wiz. The malicious…
SRC // The Hacker News -
TapMap: Free, open-source network map
TapMap is a free, open-source desktop app that plots a computer’s active network connections on an interactive world map. It scans open sockets, pulls out the remote IP addresses and…
SRC // Help Net Security