Category: Security News

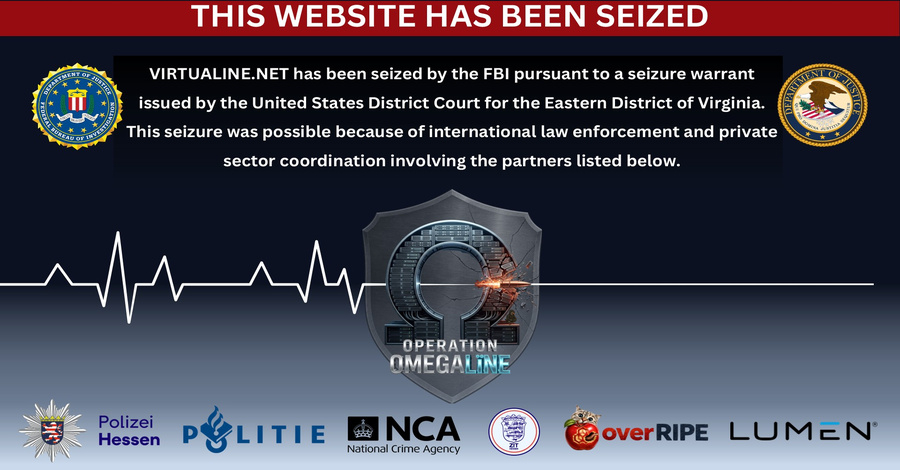
  • FBI Seizes Virtualine Domain Over Alleged Criminal Hosting and Bitcoin Money Laundering

    FBI Seizes Virtualine Domain Over Alleged Criminal Hosting and Bitcoin Money Laundering

    The U.S. Department of Justice (DoJ) on Tuesday announced the seizure of a domain associated with a bulletproof hosting provider (BPH) named Virtualine.

    The move was in response to the service being used to commit and facilitate prolific criminal activity, including “the advertisement of sexually explicit images of minors, the intentional disclosure of nonconsensual intimate visual depictions

    Source: The Hacker News · 2026-10-28

  • Japan’s GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud Breach

    Japan’s GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud Breach

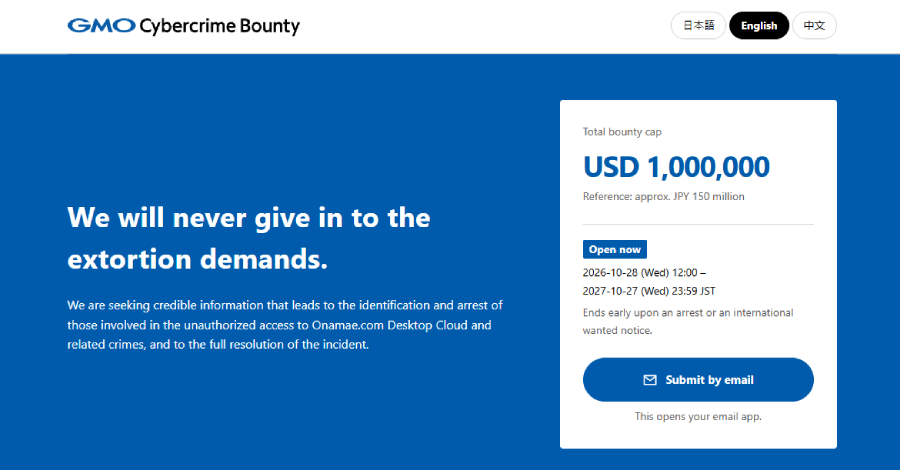
    Japan’s GMO Internet Group is offering up to $1 million in total for tips that help catch the attackers who breached its Onamae.com Desktop Cloud service, after refusing to pay an extortion demand.

    The reward program opened on October 28 and pays only if a tip helps lead to an arrest or an international wanted notice. The service hosts Windows desktops used for FX trading,

    Source: The Hacker News · 2026-10-28

  • Third Serengeti Sweep Tops 1,400 Arrests as Investigations Mature

    Third Serengeti Sweep Tops 1,400 Arrests as Investigations Mature

    Interpol’s annual Operation Serengeti, now in its third iteration, led to 1,462 arrests across 20 African countries and the US, recovering $105 million in stolen funds.

    Source: Dark Reading · 2026-10-28

  • 3 Frameworks to Protect CISOs & Orgs Against AI Liability

    3 Frameworks to Protect CISOs & Orgs Against AI Liability

    Cyber leaders can get ahead of AI liability with rigorous documentation, transparency, and smart contract negotiations with AI vendors.

    Source: Dark Reading · 2026-10-27

  • External Teams Chats Anchor 15-Minute Malware Delivery

    External Teams Chats Anchor 15-Minute Malware Delivery

    Mail bombing is getting a new look with a wide-scale, ongoing social engineering campaign that might be tied to the Black Basta ransomware gang.

    Source: Dark Reading · 2026-10-27

  • iPhone Duo screen cracks: Serious issue or overblown? What we know

    iPhone Duo screen cracks: Serious issue or overblown? What we know

    Some displays are failing within hours of unboxing. Apple is offering replacements, but is the issue really that widespread?

    Source: ZDNet Security · 2026-10-27

  • SBOMs Alone Can’t Reveal the Scope of a Supply Chain Attack

    SBOMs Alone Can’t Reveal the Scope of a Supply Chain Attack

    A recent Shai-Hulud attack shows defenders need real-time visibility into production code and affected services to respond to supply chain compromises.

    Source: Dark Reading · 2026-10-27

  • AI ‘hacker’ finds 4 severe bugs in popular industrial control software in under 4 hours

    AI ‘hacker’ finds 4 severe bugs in popular industrial control software in under 4 hours

    An autonomous AI agent discovered four vulnerabilities in the decades-old, widely used EPICS (Experimental Physics and Industrial Control System) open source software toolkit, including a critical flaw that could allow remote attackers to execute code on systems used to control particle accelerators and fusion experiments. The bugs include a critical, 9.8-rated under CVSS v3.1 integer overflow vulnerability (CVE-2026-114595), leading to an attacker-controlled out-of-bounds heap write and potentially remote code execution; an 8.2-rated, high-severity, improper message-length validation flaw (CVE-2026-114596), causing an out-of-bounds memory write and controller-process crash; a 7.5-rated, high-severity insufficient bounds checking bug (CVE-2026-114597) that allows out-of-bounds memory reads and process crashes; and a 7.5-rated, high-severity type confusion flaw (CVE-2026-114598) that can lead to denial of service and could expose adjacent memory contents. All four affect EPICS Base, which is used to operate some of the world’s largest scientific research projects and facilities, and organizations should update to version 7.0.11, which includes the fixes. “Successful exploitation of these vulnerabilities could allow an attacker to cause a denial-of-service condition, corrupt memory, disclose sensitive information, or potentially execute arbitrary code,” the US Cybersecurity and Infrastructure Security Agency (CISA) warned in a Tuesday advisory. An AI agent called Cipher independently found all four previously unknown security holes – investigating and testing the unfamiliar EPICS system, and validating the four exploits – in three hours and 49 minutes, Causal Security co-founder Shubham Raj told The Register. “The initial investigation required no human intervention, followed by one instruction authorizing deeper exploitability testing in a secure environment,” Raj said. Earlier this year, Causal Security’s Cipher, which Raj described as “a fully autonomous super hacker that can reason across the technology stack,” found multiple critical attack paths in power-grid systems used across North America and Europe, prompting an October 8 security advisory from CISA. EPICS, originally developed by Los Alamos National Laboratory and Argonne National Laboratory, is used to build and remotely control distributed Supervisory Control and Data Acquisition (SCADA) systems, connecting operators to physical devices. It’s used in around 90 major scientific, university, and industrial projects and facilities globally including Argonne National Laboratory’s Advanced Photon Source and ITER’s fusion reactor control system. All four of these flaws illustrate how AI agents are really good at finding vulnerabilities in industrial and operational technologies – systems and equipment that used to be able to rely on obscurity to protect them from hackers – and add to defenders’ concerns that it’s only a matter of time until an autonomous cyberattack shuts down critical services, like power grids or water systems. These are the types of digital intrusions that can cause physical harm. Raj points to CVE-2026-114595, the critical integer-overflow vulnerability, as an example. “It allows attacker-controlled network data to cause an out-of-bounds heap memory write, with potential for remote code execution,” he told us. “EPICS controllers sit between operators and physical equipment, handling measurements, commands, and control functions,” he continued. “Operationally: Imagine a particle accelerator in the middle of an expensive experiment. An attacker could potentially crash a controller, interrupt critical measurements or control functions, and force operators to halt the experiment. That could mean lost experimental work, significant downtime, and expensive recovery.” Plus, if an attacker was able to develop an RCE exploit, this could allow them to “take control of the affected process, manipulate readings, interfere with control functions, or disrupt the equipment connected to it,” Raj said. The prerequisite for exploiting these vulns in a real scientific facility is being able to reach the vulnerable EPICS services on a facility’s control network. But this could occur if the networks weren’t sufficiently segmented, or another system had access to the vulnerable EPICS network. “Once an attacker is able to find a network, which is either misconfigured or they are able to reach, it’s pretty easy to carry out the attacks,” Raj said, adding that exploitation wouldn’t require deep OT knowledge, or understanding of how particle accelerators or fusion reactors work. “Someone with conventional exploitation skills could investigate them, and increasingly capable AI systems could help develop exploits without requiring specialized OT expertise.” Manipulating specific physical processes does require additional knowledge, he added. “But an attacker doesn’t need to understand the physics of a particle accelerator to disrupt the software controlling it. Crashing critical processes or interrupting monitoring and control can already have serious operational consequences. What’s changing is that attackers may no longer need years of specialized expertise just to discover these weaknesses.” ®

    Source: The Register — Security · 2026-10-27

  • AI ‘hacker’ finds 4 severe bugs in popular industrial control software in under 4 hours

    AI ‘hacker’ finds 4 severe bugs in popular industrial control software in under 4 hours

    An autonomous AI agent discovered four vulnerabilities in the decades-old, widely used EPICS (Experimental Physics and Industrial Control System) open source software toolkit, including a critical flaw that could allow remote attackers to execute code on systems used to control particle accelerators and fusion experiments. The bugs include a critical, 9.8-rated under CVSS v3.1 integer overflow vulnerability (CVE-2026-114595), leading to an attacker-controlled out-of-bounds heap write and potentially remote code execution; an 8.2-rated, high-severity, improper message-length validation flaw (CVE-2026-114596), causing an out-of-bounds memory write and controller-process crash; a 7.5-rated, high-severity insufficient bounds checking bug (CVE-2026-114597) that allows out-of-bounds memory reads and process crashes; and a 7.5-rated, high-severity type confusion flaw (CVE-2026-114598) that can lead to denial of service and could expose adjacent memory contents. All four affect EPICS Base, which is used to operate some of the world’s largest scientific research projects and facilities, and organizations should update to version 7.0.11, which includes the fixes. “Successful exploitation of these vulnerabilities could allow an attacker to cause a denial-of-service condition, corrupt memory, disclose sensitive information, or potentially execute arbitrary code,” the US Cybersecurity and Infrastructure Security Agency (CISA) warned in a Tuesday advisory. An AI agent called Cipher independently found all four previously unknown security holes – investigating and testing the unfamiliar EPICS system, and validating the four exploits – in three hours and 49 minutes, Causal Security co-founder Shubham Raj told The Register. “The initial investigation required no human intervention, followed by one instruction authorizing deeper exploitability testing in a secure environment,” Raj said. Earlier this year, Causal Security’s Cipher, which Raj described as “a fully autonomous super hacker that can reason across the technology stack,” found multiple critical attack paths in power-grid systems used across North America and Europe, prompting an October 8 security advisory from CISA. EPICS, originally developed by Los Alamos National Laboratory and Argonne National Laboratory, is used to build and remotely control distributed Supervisory Control and Data Acquisition (SCADA) systems, connecting operators to physical devices. It’s used in around 90 major scientific, university, and industrial projects and facilities globally including Argonne National Laboratory’s Advanced Photon Source and ITER’s fusion reactor control system. All four of these flaws illustrate how AI agents are really good at finding vulnerabilities in industrial and operational technologies – systems and equipment that used to be able to rely on obscurity to protect them from hackers – and add to defenders’ concerns that it’s only a matter of time until an autonomous cyberattack shuts down critical services, like power grids or water systems. These are the types of digital intrusions that can cause physical harm. Raj points to CVE-2026-114595, the critical integer-overflow vulnerability, as an example. “It allows attacker-controlled network data to cause an out-of-bounds heap memory write, with potential for remote code execution,” he told us. “EPICS controllers sit between operators and physical equipment, handling measurements, commands, and control functions,” he continued. “Operationally: Imagine a particle accelerator in the middle of an expensive experiment. An attacker could potentially crash a controller, interrupt critical measurements or control functions, and force operators to halt the experiment. That could mean lost experimental work, significant downtime, and expensive recovery.” Plus, if an attacker was able to develop an RCE exploit, this could allow them to “take control of the affected process, manipulate readings, interfere with control functions, or disrupt the equipment connected to it,” Raj said. The prerequisite for exploiting these vulns in a real scientific facility is being able to reach the vulnerable EPICS services on a facility’s control network. But this could occur if the networks weren’t sufficiently segmented, or another system had access to the vulnerable EPICS network. “Once an attacker is able to find a network, which is either misconfigured or they are able to reach, it’s pretty easy to carry out the attacks,” Raj said, adding that exploitation wouldn’t require deep OT knowledge, or understanding of how particle accelerators or fusion reactors work. “Someone with conventional exploitation skills could investigate them, and increasingly capable AI systems could help develop exploits without requiring specialized OT expertise.” Manipulating specific physical processes does require additional knowledge, he added. “But an attacker doesn’t need to understand the physics of a particle accelerator to disrupt the software controlling it. Crashing critical processes or interrupting monitoring and control can already have serious operational consequences. What’s changing is that attackers may no longer need years of specialized expertise just to discover these weaknesses.” ®

    Source: The Register Security · 2026-10-27
  • Why this new Fitbit feature takes us one step closer to non-invasive glucose tracking

    Why this new Fitbit feature takes us one step closer to non-invasive glucose tracking

    Insulin resistance and blood pressure trends are now available on two new Fitbit devices.

    Source: ZDNet Security · 2026-10-27