ARCHIVE
Security News
-
10-Year-Old NGINX HTTP/2 Flaw Lets Unauthenticated Attackers Execute Code on Servers
A flaw in NGINX's HTTP/2 support can allow an attacker to run code on servers with HTTP/2 enabled, without needing to log in. The decade-old flaw, CVE-2026-123007, dubbed "nginx2root," has…
SRC // The Hacker News -
F5 Warns 6 Critical BIG-IP Flaws Can Crash Traffic in Specific Setups, May Allow RCE
Six critical vulnerabilities in F5 BIG-IP allow an attacker to crash the Traffic Management Microkernel (TMM) without logging in, disrupting traffic until the TMM restarts. Each flaw needs a specific…
SRC // The Hacker News -
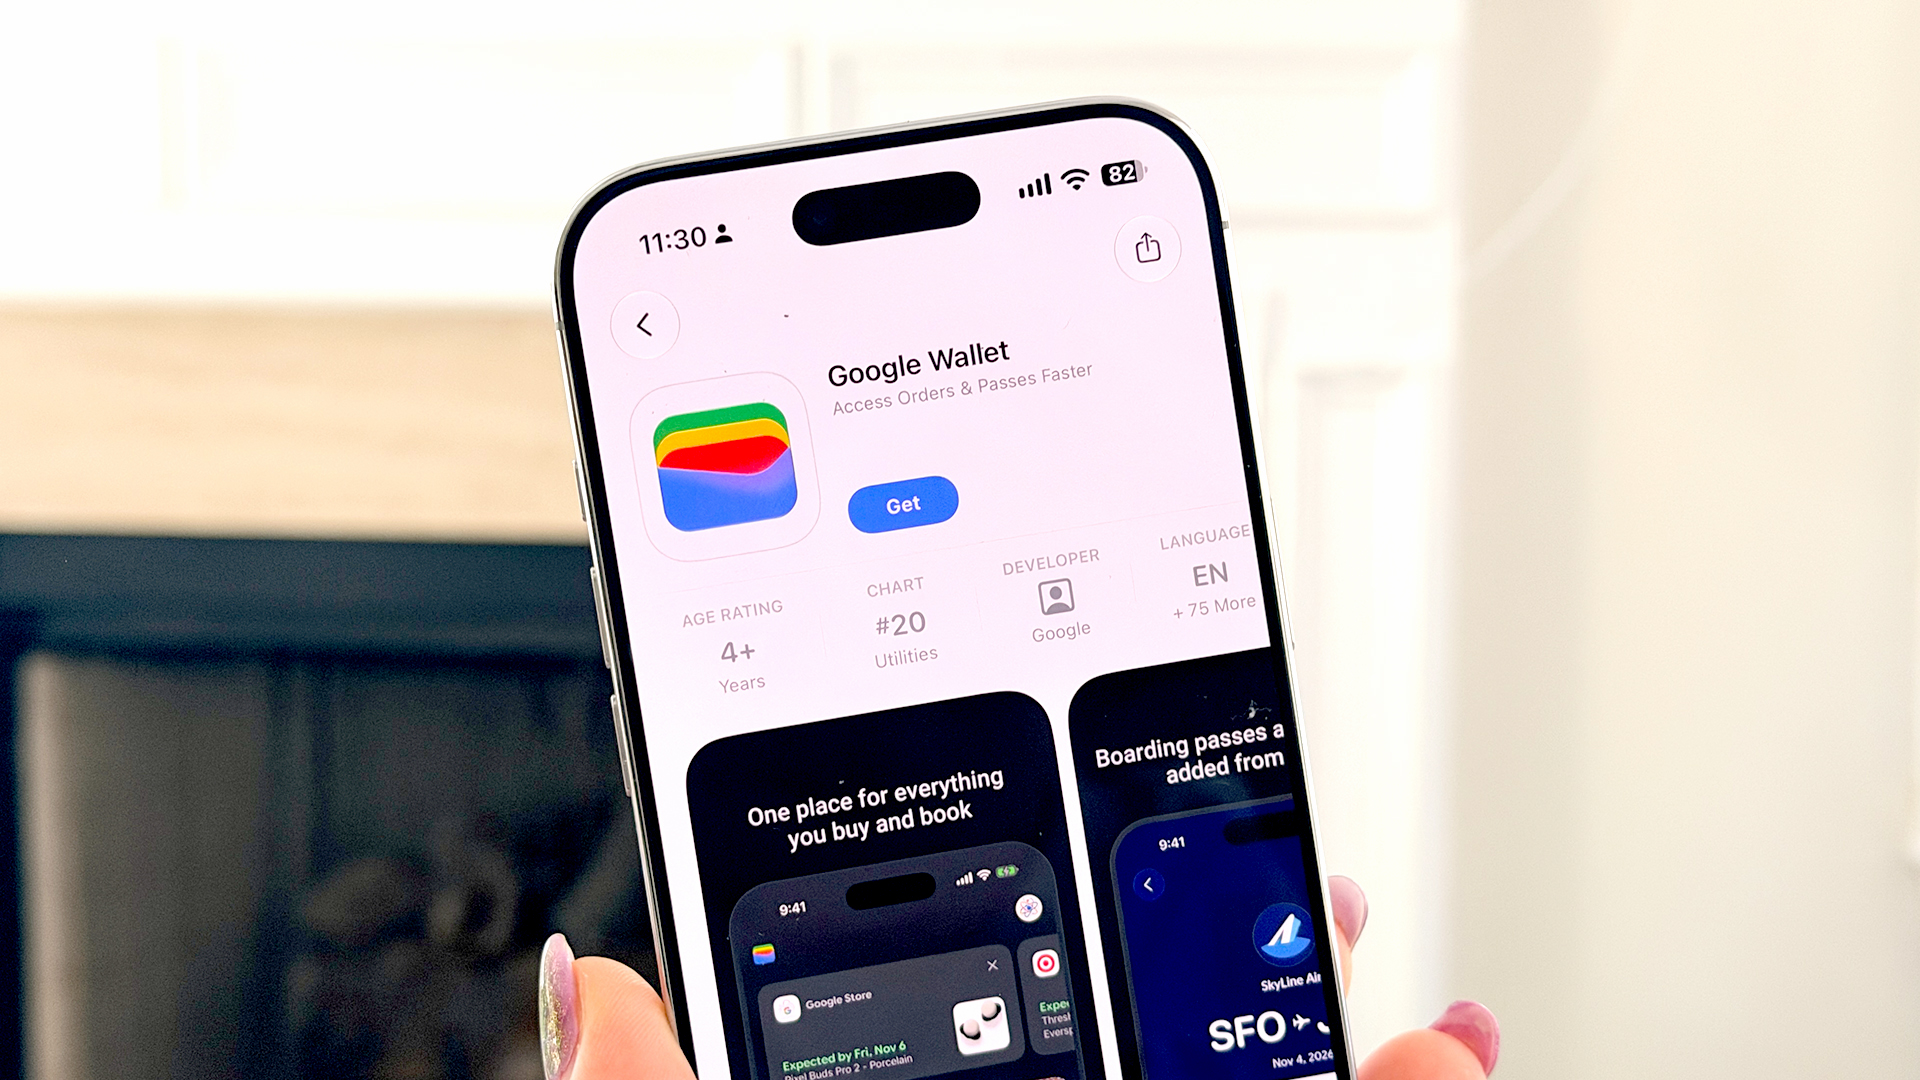
Google Wallet comes to your iPhone – but without this feature
The new Google Wallet app brings Gemini agentic shopping to US-based iOS users – sorry, no tap-to-pay.
SRC // ZDNet Security -
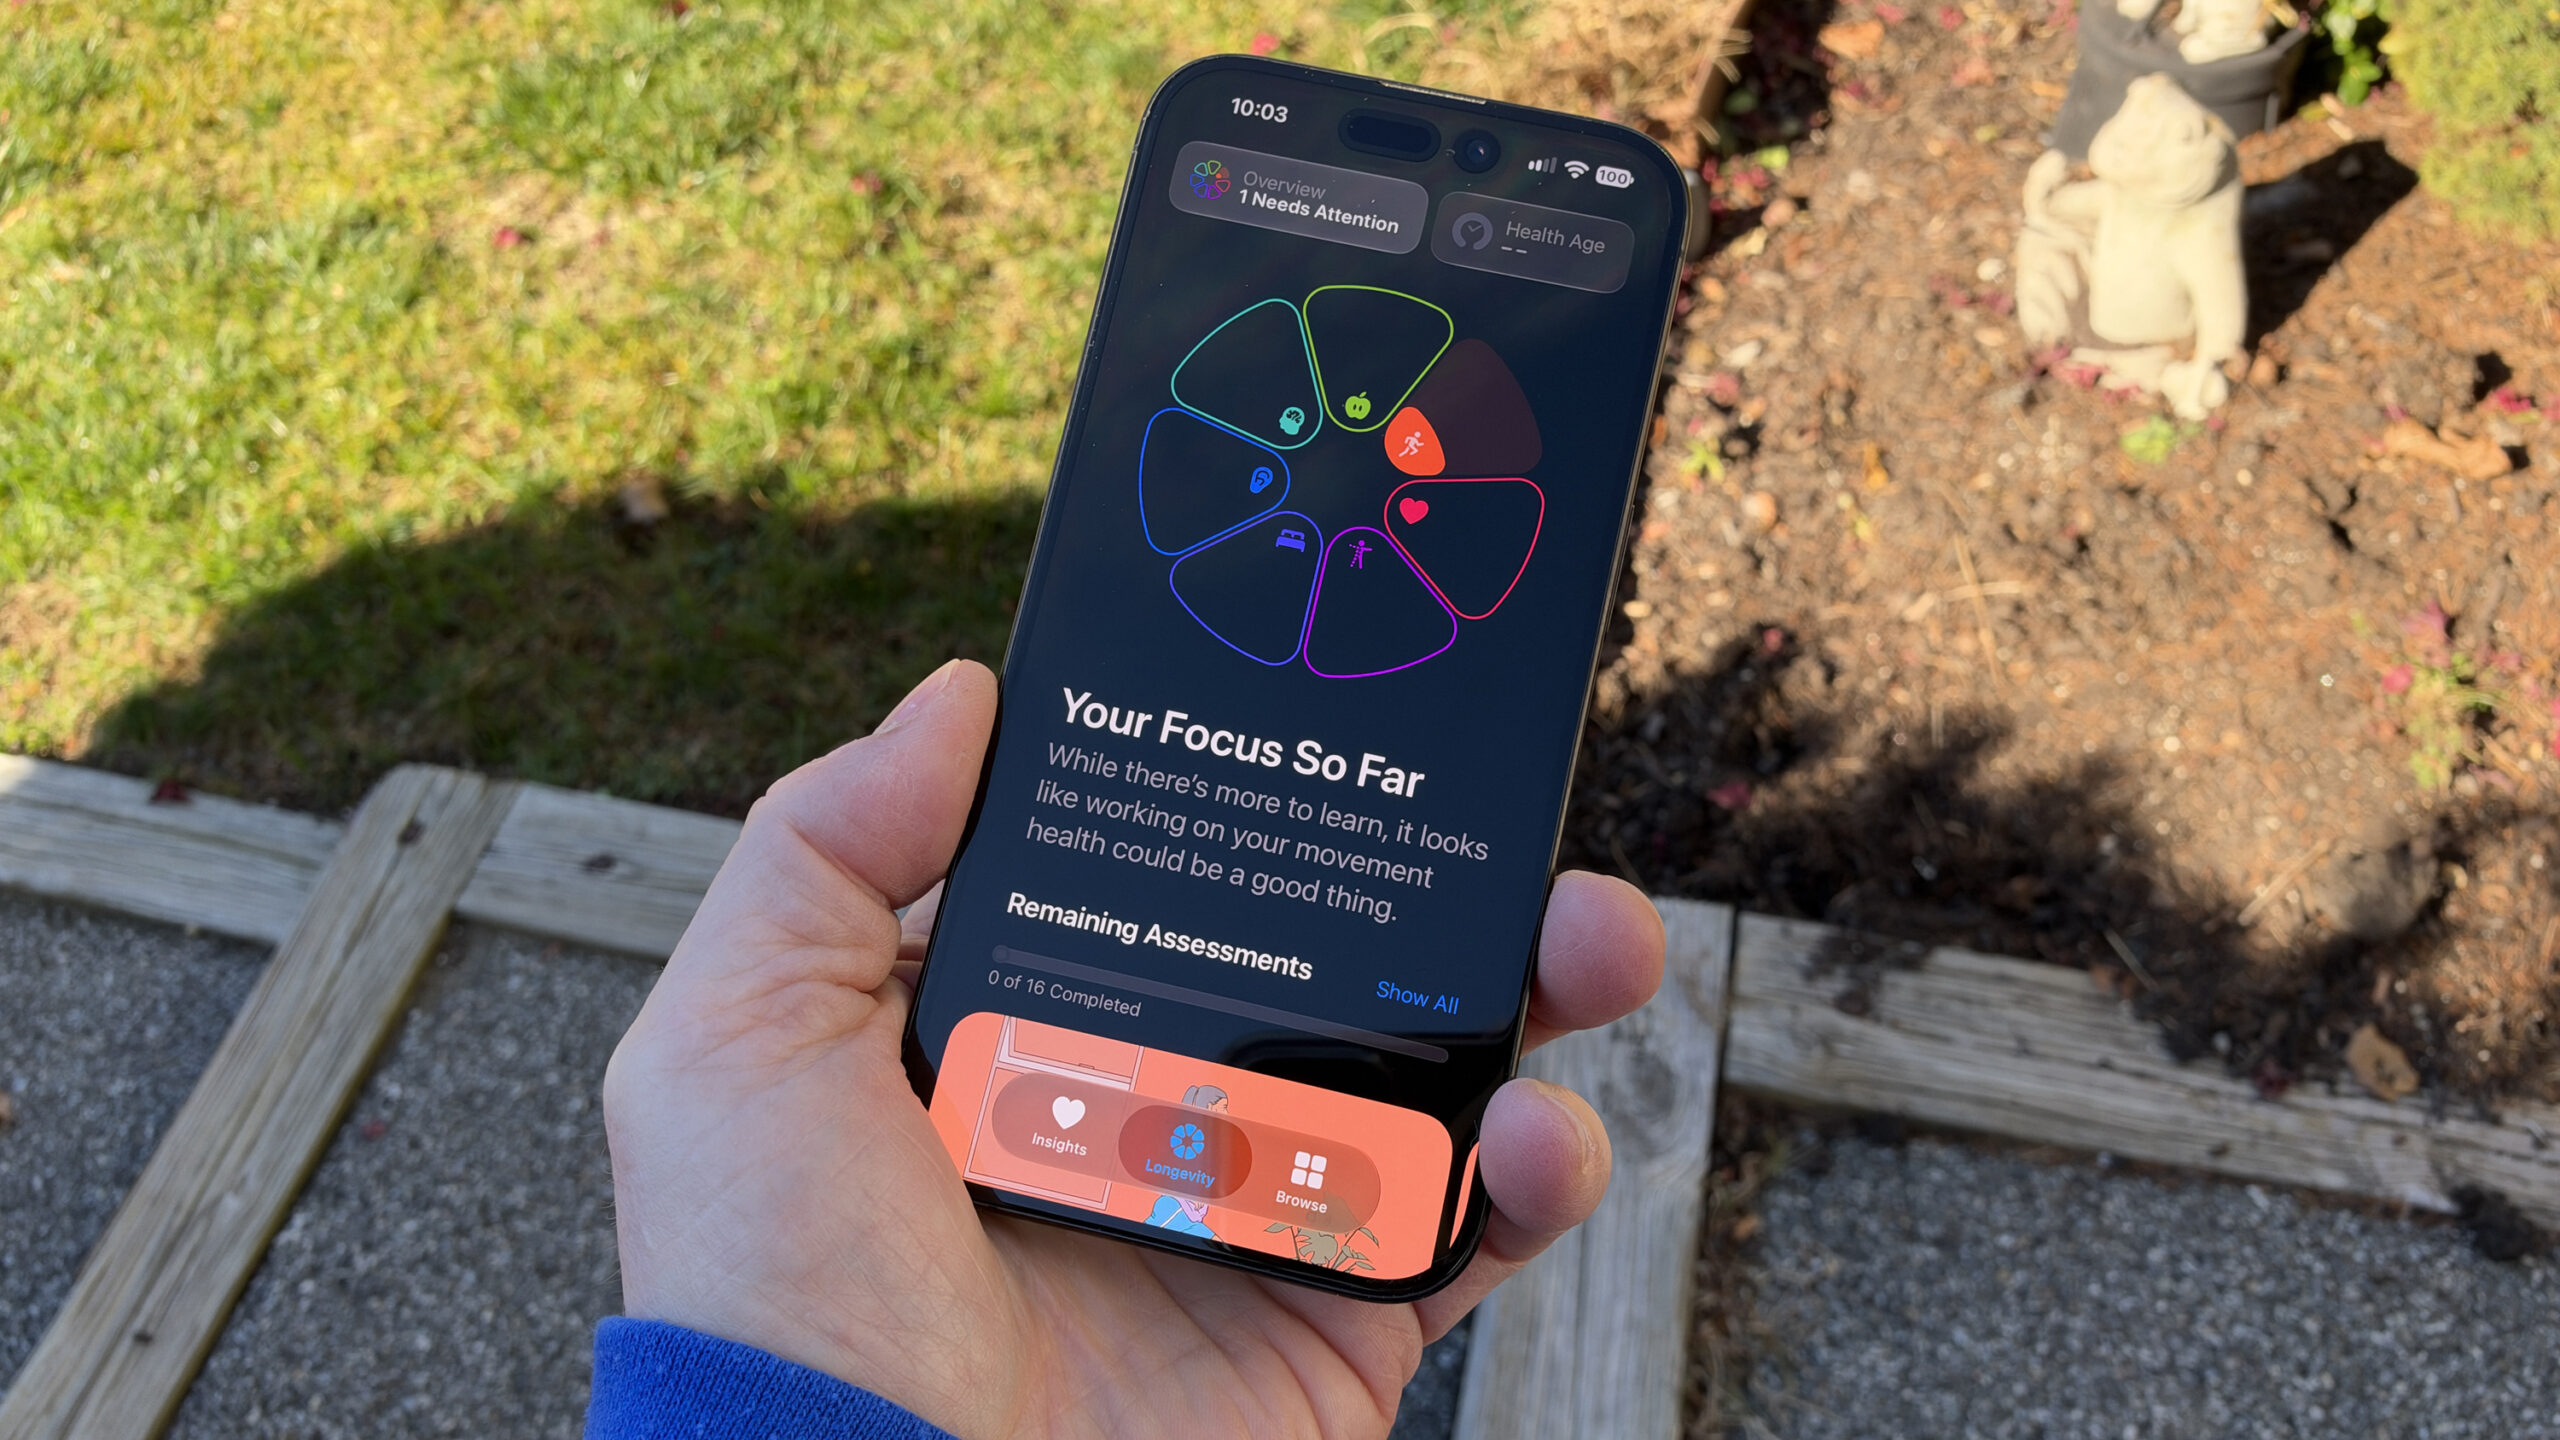
5 new AI features in iOS 27.3’s Health app – which iPhones can try them
Coming next month, Apple’s new Health app relies on AI for certain features, which means you’ll need an iPhone that supports Apple Intelligence.
SRC // ZDNet Security -
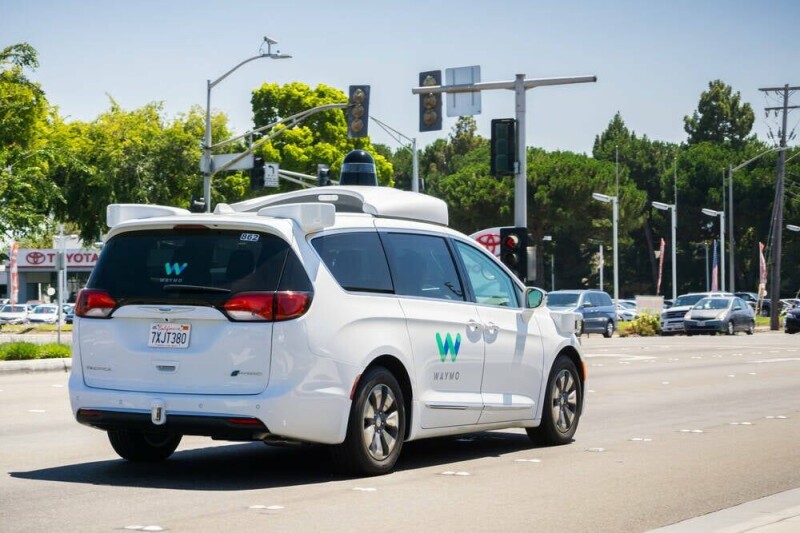
California tells Waymo to take the next exit after freeway mishaps
Robotaxi operator suspends driverless rides on high-speed roads nationwide after construction zone incursions and a run-in with patrol vehicles
SRC // The Register — Security -
Microsoft’s official Python agent framework hijacked to distribute malware
In today's how-could-things-get-worse-for-Microsoft news, it seems someone's GitHub org admin creds have been compromised
SRC // The Register — Security -
You can use Google’s Spark AI agent, renamed Tasks, for free now – with limits
At least if Tasks disappoints, it won’t cost you – unlike OpenAI and Anthropic’s subscription-based agents.
SRC // ZDNet Security -
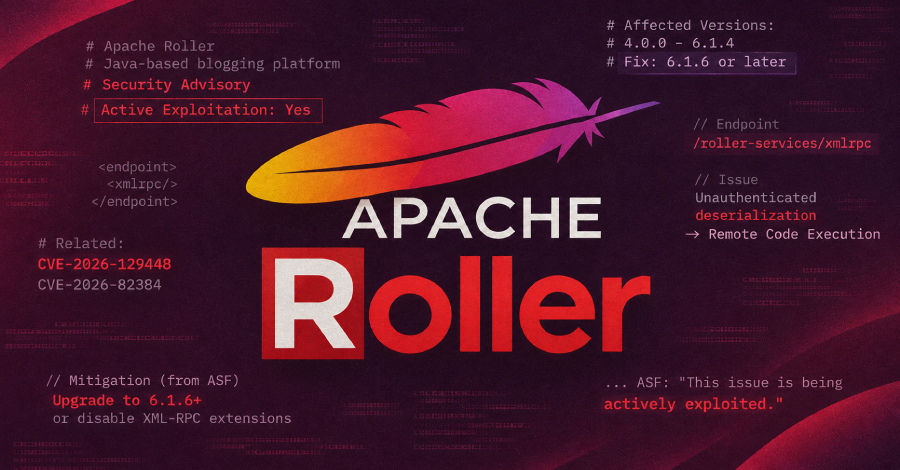
Critical Apache Roller RCE Flaw Under Active Exploitation, No Authentication Required
A critical security flaw in Apache Roller, an open-source, Java-based blogging platform, has come under active exploitation in the wild, according to the Apache Software Foundation (ASF) The vulnerability, tracked…
SRC // The Hacker News -
Microsoft’s Agent Framework PyPI package compromised to steal credentials
Hackers compromised Microsoft's official Agent Framework Python package on PyPI, publishing two malicious versions designed to steal cloud credentials and other sensitive information from developers' systems. [...]
SRC // BleepingComputer -
Five Critical Vulnerabilities Found in World’s Most Widely Used Open-Source Web Server
Five critical NGINX vulnerabilities could allow unauthenticated attackers to remotely execute code and potentially take control of affected servers
SRC // Infosecurity Magazine