ARCHIVE
Ransomware & Dark Web
-
Ransomware claim: SPI Corp / SPI Energy group (spicorp-invest.com) (pixelleaks)
Petroleum staffing & maintenance back-office (accounting services) · Republic of Congo Full data leak: 2026-11-17 13:29 UTC This disclosure concerns a verified set of records from an organization in the…
SRC // RansomLook — Recent Posts -
Ransomware claim: The CCMC (Dark Project)
About The CCMC CCMC specializes in HOA community management for large-scale, master-planned communities across the U.S., offering tailored services that prioritize the unique vision and goals of each community. With…
-
Ransomware claim: World Wide Fittings (bravox)
Global manufacturer of steel and stainless hydraulic tube and pipe fittingsGroup: bravoxCountry: USSector: ManufacturingVictim website: www.worldwidefittings.comDiscovered: 2026-11-13 14:21 UTCAttack date: 2026-11-13 14:21 UTCThis entry reflects a claim published by an…
-
Ransomware claim: Galorath (akira)
Galorath Incorporated has invested more than two decades developing solutions to help governmen t and commercial organizations plan and manage complex software, hardware, electronics, manufac turing and IT projects. Its…
-
Ransomware claim: Replogle Globes (akira)
Founded in 1930, Replogle Globes is a manufacturer and retailer of handcrafted globes, of diffe rent colors, types, and custom globes with online ordering. The company is headquartered in Hil…
-
Ransomware claim: Paragon Mechanical (akira)
Paragon Mechanical Inc. is a premier full-service mechanical contractor based in Silicon Valley , specializing in HVAC, piping, architectural sheet metal, and plumbing services. The company o ffers a wide…
-
Microsoft Outlook Outage: What You Need to Know
The Microsoft Outlook outage that started on November 12, 2026, began as an Exchange Online mailbox access problem in the...
SRC // SOCRadar -
CVE-2026-119618: Apache HTTP/2 Race Condition RCE
The Apache Software Foundation has released Apache HTTP Server 2.4.71 to fix CVE-2026-119618, a critical race...
SRC // SOCRadar -
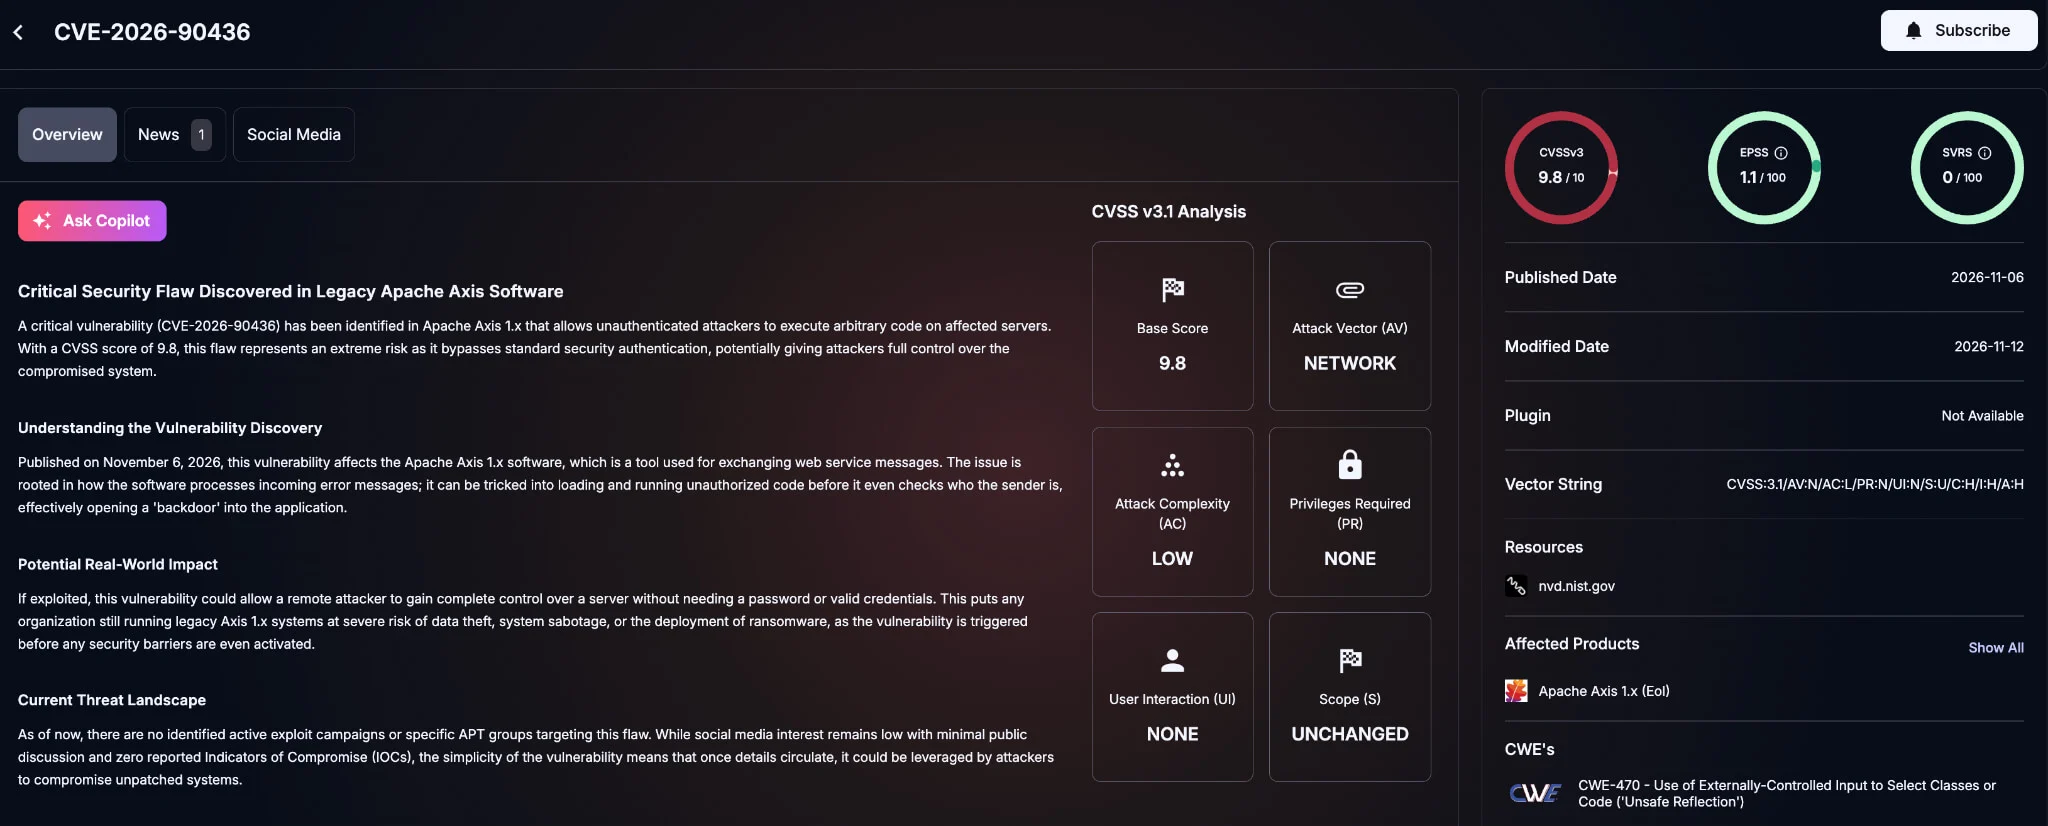
4EverAble2Shell At a Glance
4EverAble2Shell is an N-central zero-day exploit chain that lets an unauthenticated remote attacker run commands as root on an on-premises N-able N-central server. An independent researcher released a proof of…
SRC // SOCRadar -
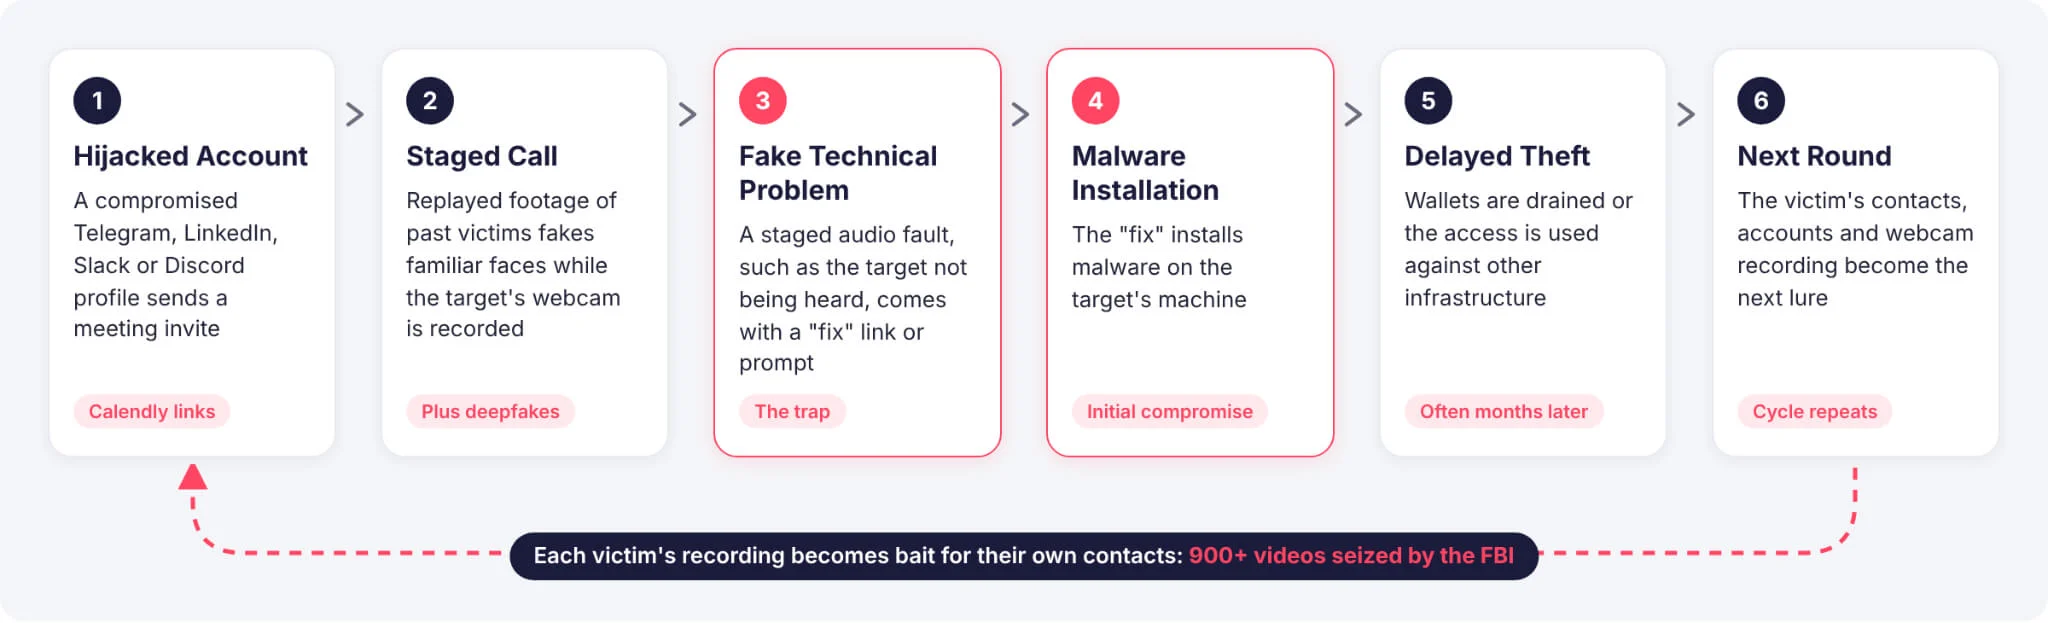
FaceStealer: FBI Disrupts Fake Video Call Crypto Scam
The FBI and the U.S. Department of Justice have disrupted FaceStealer, a North Korean social engineering campaign that used hijacked accounts, replayed webcam footage and fake video calls to steal…
SRC // SOCRadar