ARCHIVE
Ransomware & Dark Web
-
Cyberattack mot Embracer-bolag
Warhorse, un studio d'Embracer, a été victime d'une cyberattaque. Le studio a annoncé sur X qu'il travaillait avec des spécialistes en cybersécurité pour sécuriser ses systèmes et comprendre l'incident.Victim: WarhorseCountry:…
-
Eldorado: el municipio confirmó que el ciberataque no provocó pérdidas económicas y explicó la situación del transporte público – Multimedio Genesis
La Municipalité d'Eldorado a été victime d'une cyberattaque par virus qui a perturbé temporairement son système de gestion informatique. L'incident a entraîné la suspension de l'accueil du public le vendredi,…
-
東建コーポレーションにサイバー攻撃、社内・社外向けシステムの一部が停止 個人情報への影響は調査中|セキュリティニュースのセキュリティ対策Lab
Token Corporation a annoncé le 28 octobre 2026 avoir été victime d'une cyberattaque externe. L'incident a été découvert suite à une panne de réseau interne survenue le 27 octobre. L'entreprise…
-
AI Threat Report: How Artificial Intelligence Is Used Across Illicit Communities
A monthly analysis of how artificial intelligence is used in illicit communities, based on Flashpoint proprietary intelligence and direct visibility into real threat actor environments. The post AI Threat Report:…
SRC // Flashpoint -
ACTIL Dataset Claim Lists 152,187 Records With Patient, Prescription and Reimbursement Data
An actor using the handle "Syrv4x" claims to be sharing an ACTIL dataset for free. The listing describes ACTIL as a French digital health insurance platform that manages third-party payment…
SRC // Dark Web Informer -
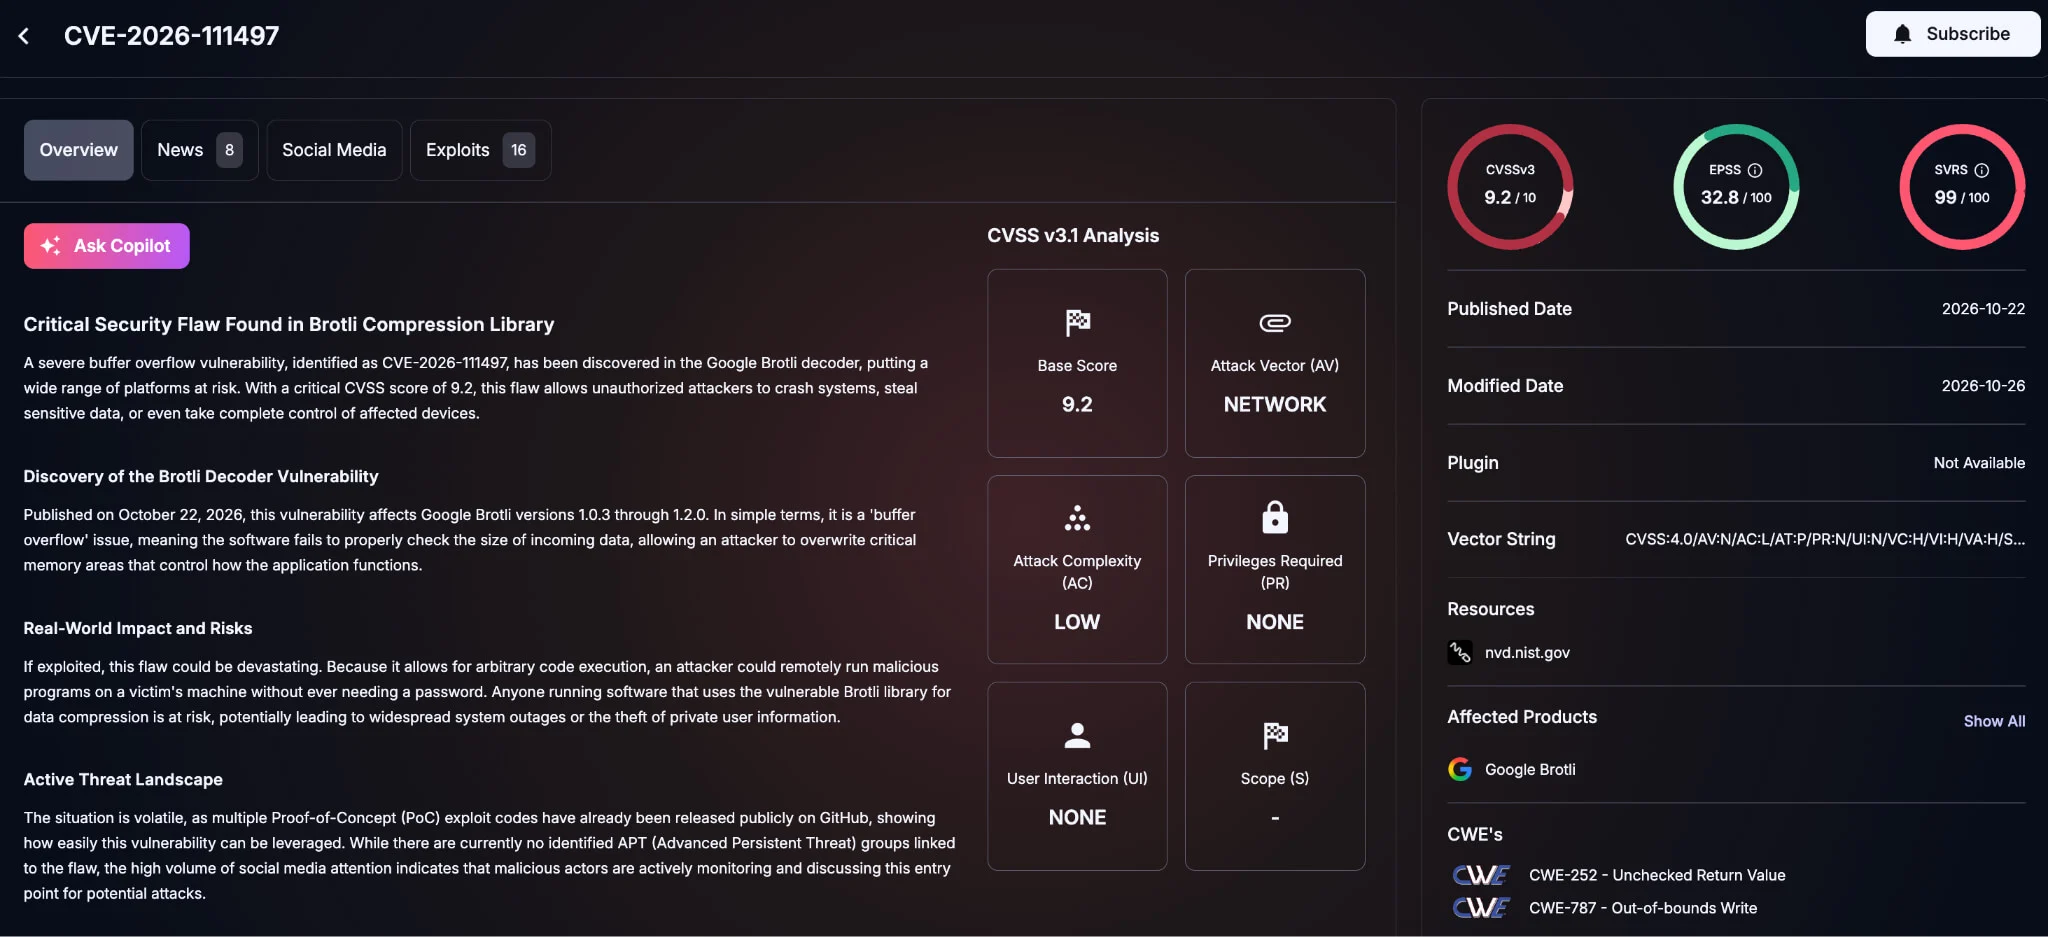
Node2Shell: Brotli Flaw Hits Python Packages
[Update] October 28, 2026: CISA Adds Node2Shell to KEV as Exploit Traffic Emerges [Update] October 27, 2026: PHP Ships Windows Builds With Brotli Fix The Node2Shell Brotli flaw (CVE-2026-111497), disclosed…
SRC // SOCRadar -
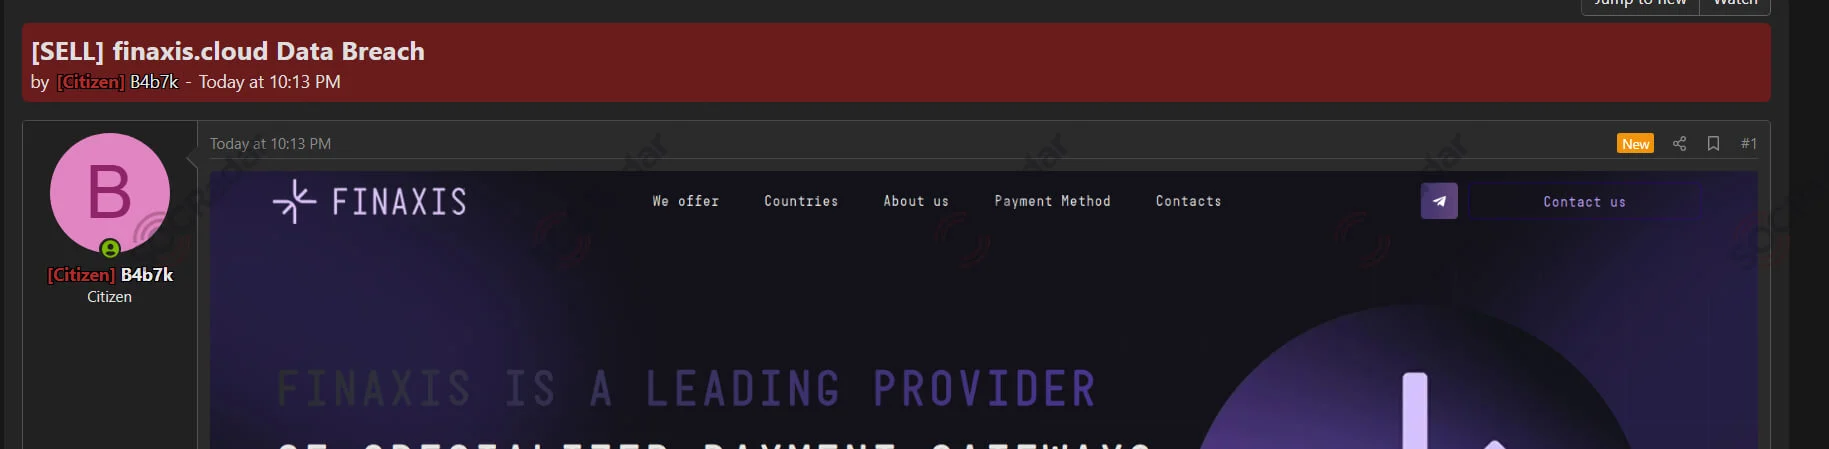
Finaxis, WoWInstaller, Moodle, MyHairCare & HT Médica Leaks
SOCRadar Dark Web Team identified several underground posts, including an alleged Finaxis.cloud data sale involving 400GB of information, a resurfaced WoWInstaller database containing historical user credentials, and an alleged Argentine…
SRC // SOCRadar -
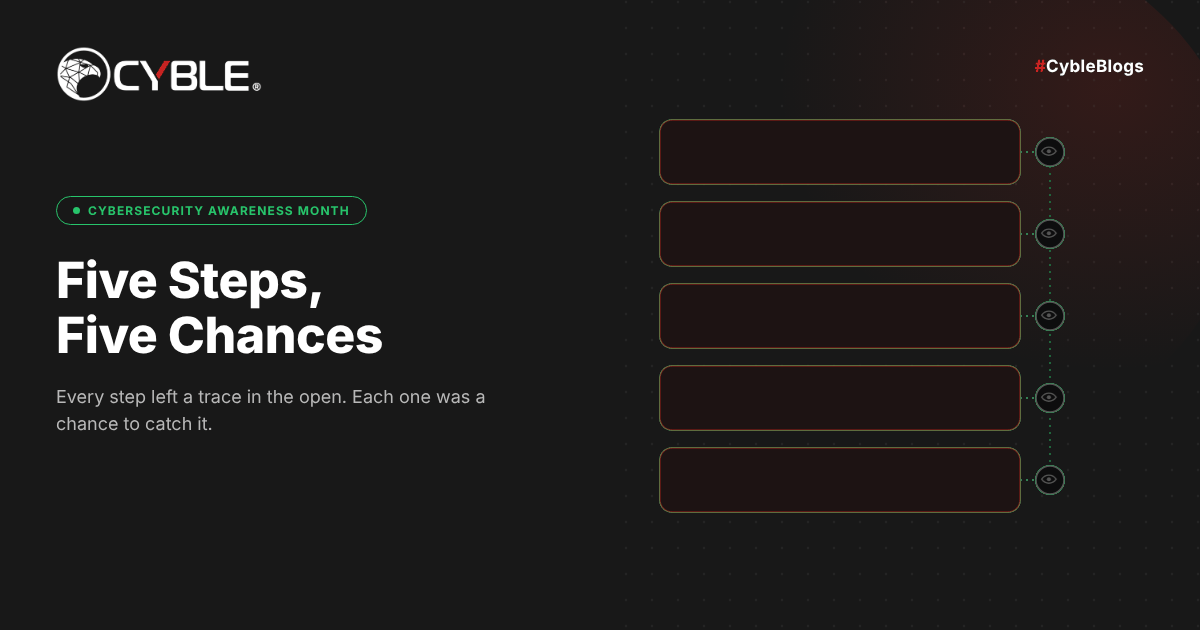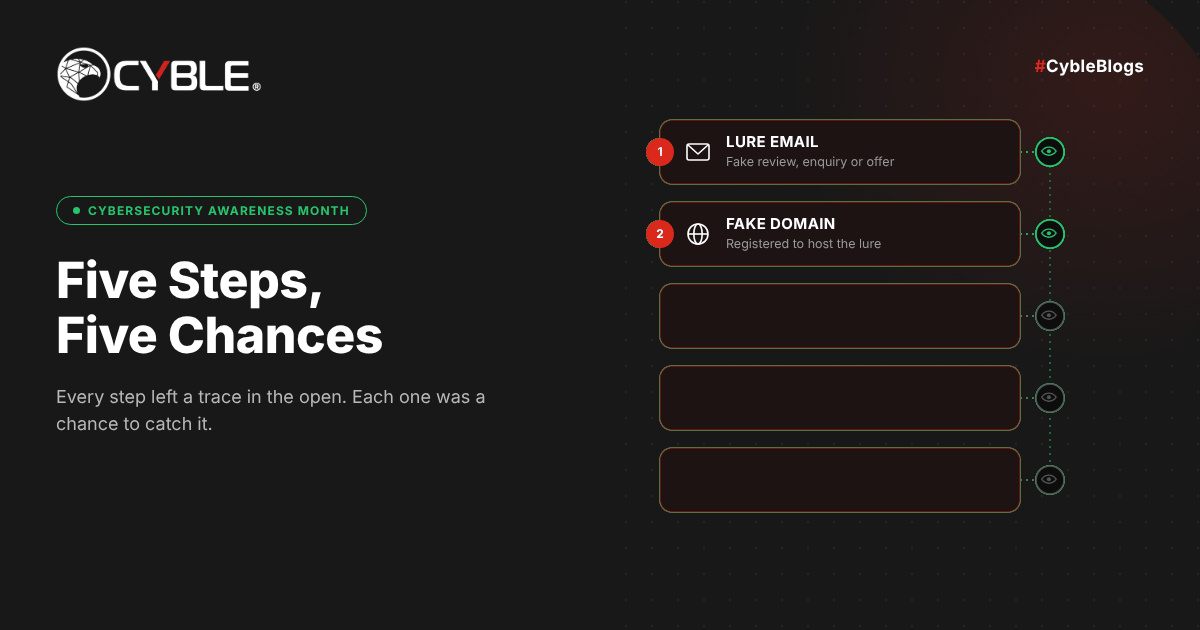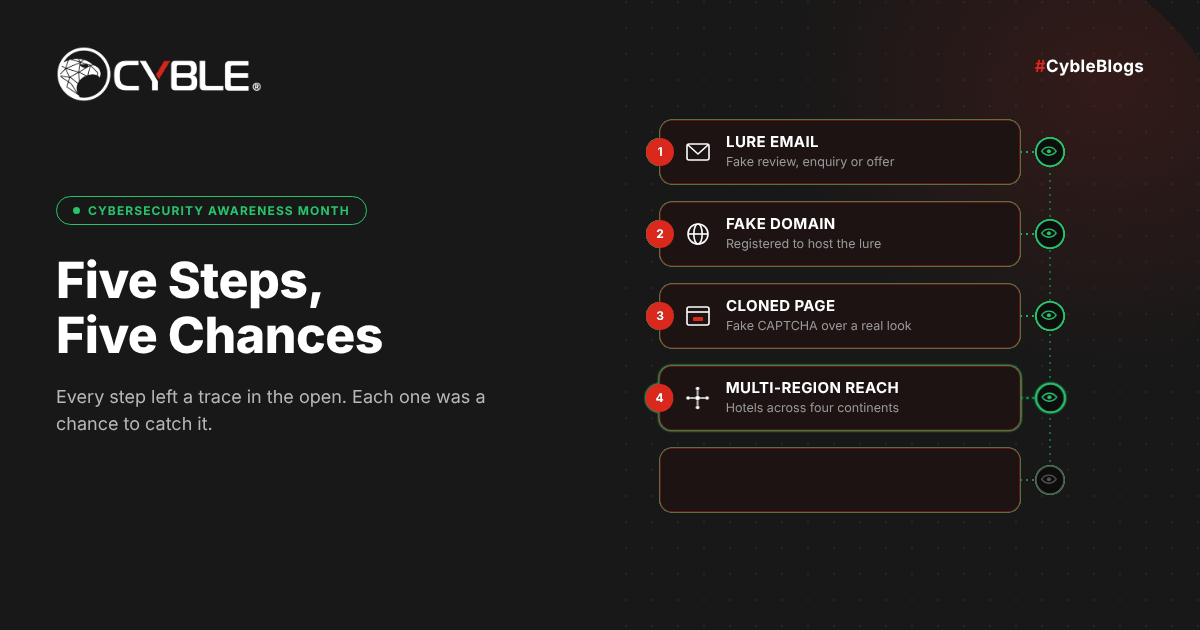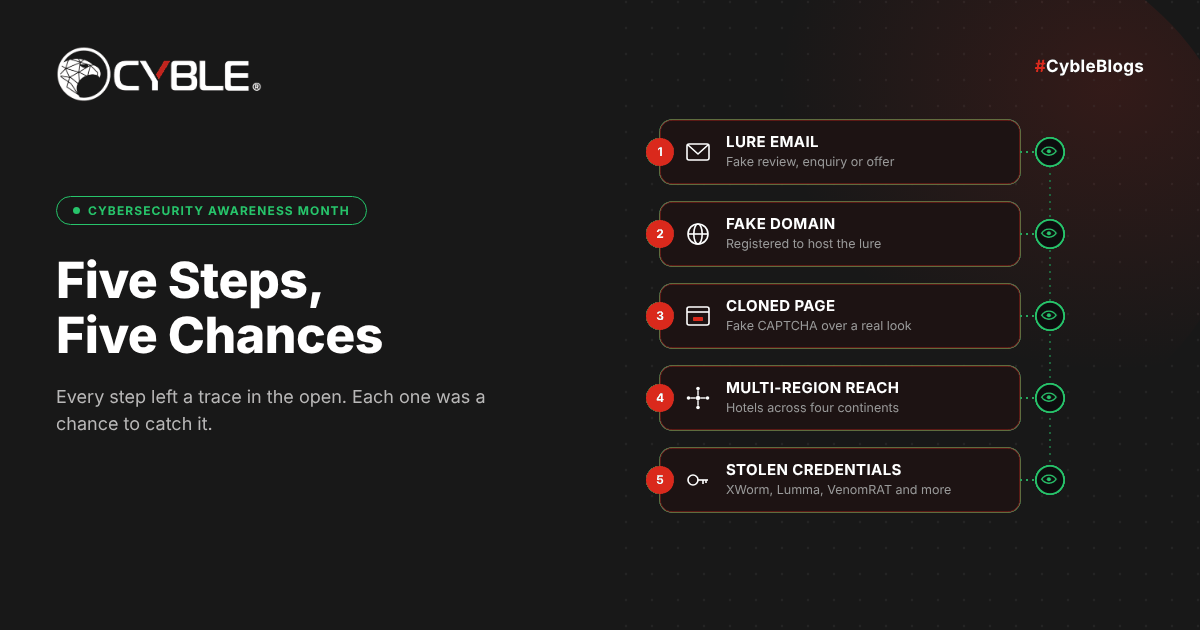
Know How Cyble Brand Intelligence Can Help Stop ClickFix Campaigns in its Tracks
Booking.com's systems were never breached. Its name was. Storm-1865 spent months borrowing Booking.com's identity to get into hotel computers, and every step of that borrowing left traces on the open…
SRC // Cyble Research -
Update on Cybersecurity Event at UNM Health Sciences Center
Le Centre des Sciences de la Santé de l'Université du Nouveau-Mexique (UNM HSC) a été confronté à un incident de cybersécurité le 26 octobre 2026. Cet événement a entraîné des…
-
מתקפת הסייבר על כלמוביל היא רק ההתחלה: הסכנה האמיתית נמצאת על הכביש | כלכליסט
L'importateur de voitures Colmobil a été victime d'une cyberattaque par rançongiciel (ransomware), entraînant une interruption de ses activités, des retards dans les livraisons de véhicules et une déconnexion de ses…