Categories: Threat Research
Tags: advisory, vulnerability, php
Source: Sophos X-Ops Threat Research · 2026-10-21
Categories: Threat Research
Tags: advisory, vulnerability, php
Source: Sophos X-Ops Threat Research · 2026-10-21
 France
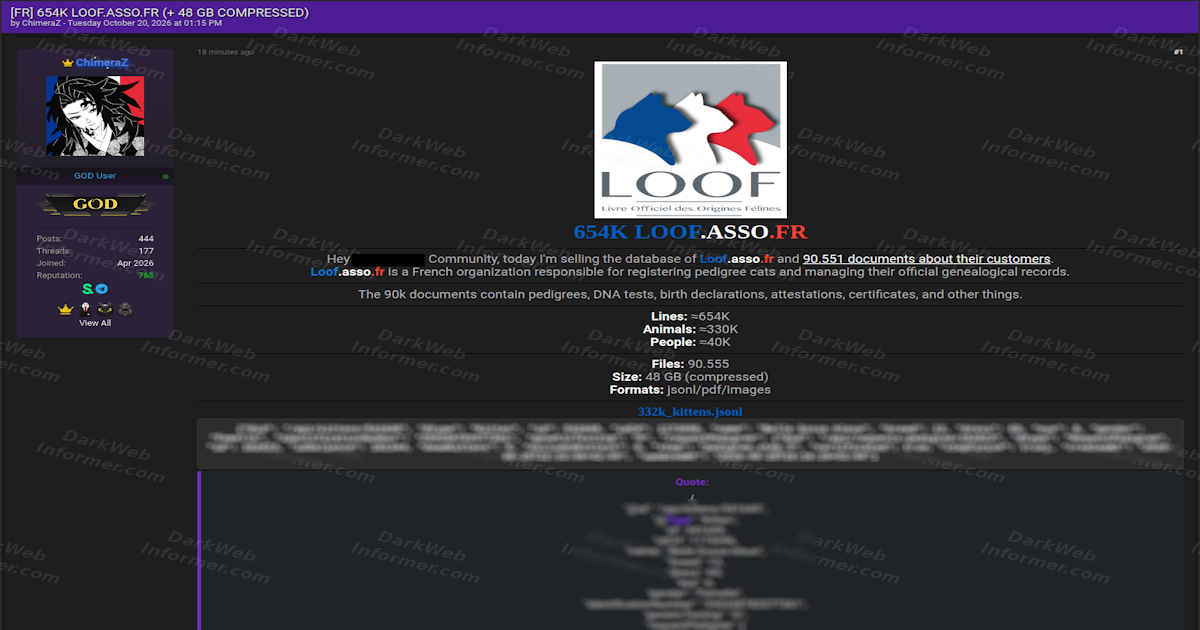
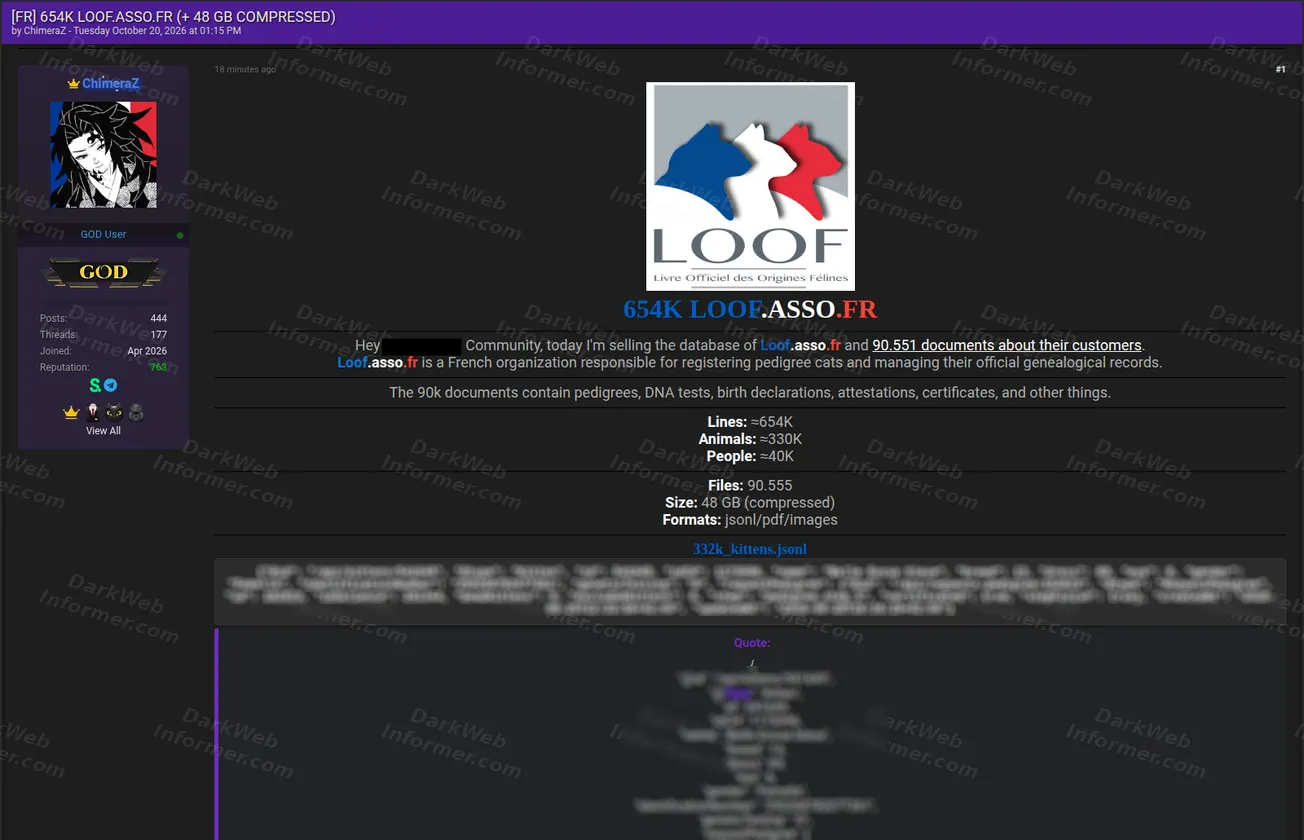
An actor using the handle “ChimeraZ” claims to be selling a LOOF dataset. LOOF, the Livre Officiel des Origines Félines, is described in the listing as the French organization responsible for registering pedigree cats and maintaining official feline genealogical records.
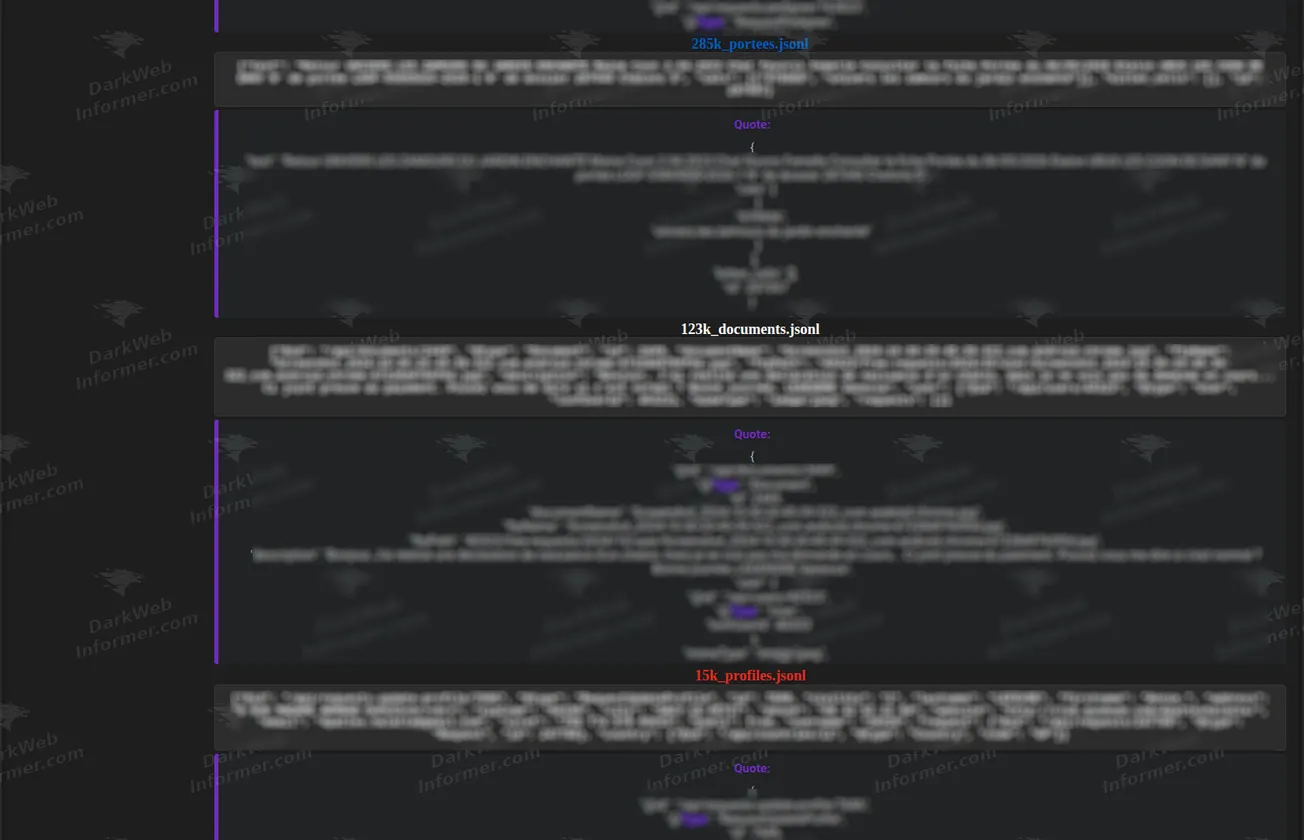
The post advertises approximately 654,000 lines, around 330,000 animal records, roughly 40,000 people and 90,555 files totaling 48 GB compressed. The stated formats are JSONL, PDF and images. The actor says the document collection includes pedigrees, DNA tests, birth declarations, attestations, certificates and other customer-related material. The dataset, its source, the stated counts and current availability have not been independently verified.
FranceThe introductory text says there are 90,551 documents, while the structured summary lists 90,555 files. This report preserves the structured file count and notes the discrepancy rather than reconciling it. Personal values shown in the visible samples are not transcribed here.
Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the dataset claim.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | ChimeraZ |
Screenshots 1–3 |
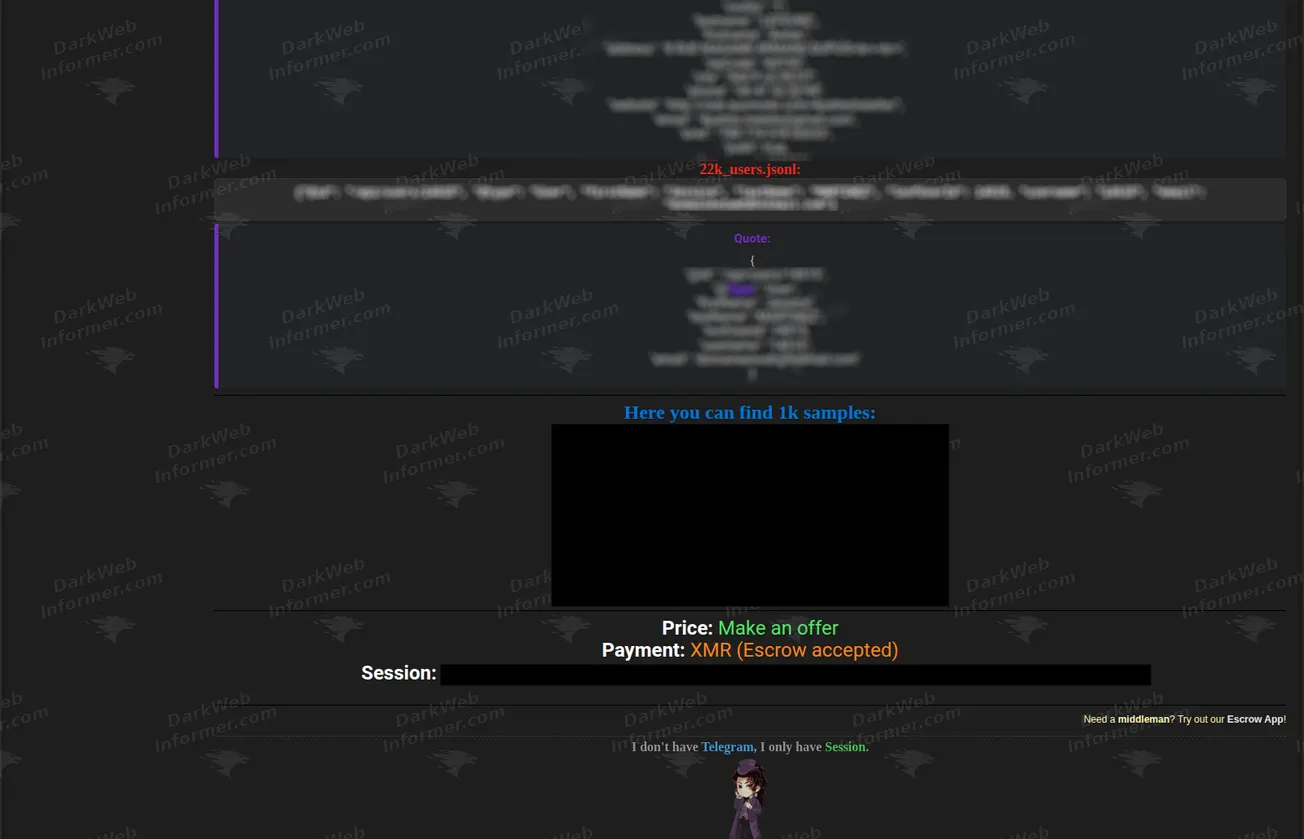
| Session ID | 05c1396ee8a9d6df7ae4497a07f2fbc75b31344f5e0cbd91dacde4c04c88c4c254 |
Screenshot 3 |
| Named organization domain | loof[.]asso[.]fr |
Screenshot 1 |
The organization domain identifies the entity named in the claim, not malicious infrastructure. No Tox ID, Telegram handle, malware hash or attacker-controlled IP address is visible. Direct sample-download mirrors shown in the source material are intentionally not reproduced here.
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
If authentic, the claimed exposure could reveal animal identification and pedigree information, customer names, addresses, phone numbers, email addresses, business identifiers and attached documents. The combination could support targeted phishing, impersonation, fraud involving pedigree or registry records, and broader privacy abuse affecting breeders, owners and other users.
Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, approximate 654,000-line count, animal or people totals, 48 GB compressed size, document count, sample contents or current availability. The supplied screenshots document the listing and visible samples, not independent confirmation of the underlying material.
Source: Dark Web Informer · 2026-10-20
<p>The China-based threat group uses DLL sideloading in these attacks</p>
Categories: Threat Research
Tags: BRONZE SANDCASTLE, Meterpreter, Sandboxie
Source: Sophos X-Ops Threat Research · 2026-10-20
L’administration du district d’Oberspreewald-Lausitz a été paralysée par un incident de sécurité informatique. Les systèmes techniques ont été mis hors service le mardi soir. Bien qu’un cyberangriff ne soit pas officiellement confirmé, les rumeurs internes suggèrent cette possibilité. Les services sont fortement limités, et le bureau est fermé le jeudi 22 octobre. Les citoyens sont invités à utiliser la ligne d’assistance téléphonique pour les demandes.
Source: ransomware.live — Cyberattacks in the News · 2026-10-20
Un incident de sécurité réseau a perturbé les services en ligne de la ville de Columbia, en Caroline du Sud. Les services d’urgence, l’eau et les paiements en ligne sont restés opérationnels. Les perturbations ont affecté les demandes de services, les licences commerciales et les permis. Les autorités enquêtent, mais aucune compromission de données ou attribution d’attaquant n’a été confirmée.
Source: ransomware.live — Cyberattacks in the News · 2026-10-20
Le réseau de médiathèques Graines de Culture(s), géré par la Communauté de communes Pévèle Carembault, a été victime d’une cyberattaque le 20 octobre 2026. Cette attaque a rendu le portail numérique commun (mediatheques.pevelecarembault.fr) inaccessible, affectant les services de 34 médiathèques. Aucune fuite de données personnelles n’a été confirmée à ce stade, mais les usagers sont fortement invités à ne pas saisir d’identifiants ou de données personnelles sur le portail avant son rétablissement sécurisé.
Source: ransomware.live — Cyberattacks in the News · 2026-10-20
 Table Of Contents

More than 3.7 million fraudulent online accounts removed. Twenty-eight arrests across Ghana and Nigeria. More than $11 million in potentially freezable funds identified. And 117 human trafficking victims identified.
These were among the results of Joint Disruption Week, an international operation targeting criminal networks responsible for online fraud, including cryptocurrency investment scams, impersonation schemes, and financial extortion.
“Transnational criminal scam networks operating from West Africa suffered major disruptions last week during a coordinated international ‘Joint Disruption Week,’ an effort that produced arrests, seizures, and the largest-ever takedown of fraudulent social media accounts linked to scam centers in the region.”
Department of Justice
Hosted by the UK’s National Crime Agency (NCA) in London during the week beginning October 6, 2026, Joint Disruption Week brought together investigators from the DOJ, FBI, U.S. Secret Service, Homeland Security Investigations, and international law enforcement agencies, alongside private-sector organizations including Flashpoint.
Throughout the week, participants exchanged real-time intelligence and developed investigative leads to support enforcement actions in Ghana and Nigeria, as well as the disruption of online accounts and infrastructure used by scam networks.
The operation targeted criminal organizations whose activities extend across borders and online platforms. According to the DOJ, scam centers operating in West Africa share characteristics with those previously identified in Southeast Asia, including organized recruitment, training in social engineering techniques, and coordinated fraud campaigns targeting victims internationally. Some operations also involve human trafficking, with individuals coerced into participating in fraudulent activities.
By bringing together law enforcement and private-sector capabilities, Joint Disruption Week targeted both the infrastructure used to perpetrate fraud and the individuals behind these schemes.
The coordinated effort produced results across criminal investigations, financial intelligence, and online infrastructure disruption.
According to the DOJ:
The figures illustrate the reach of these operations. Millions of accounts can support criminal activity across multiple platforms, while the individuals directing those activities may be operating thousands of miles from their intended victims.
The arrests and account removals represent different aspects of the same challenge: identifying the individuals behind criminal operations while disrupting the infrastructure they use to reach victims.
Online scam networks can operate across social media platforms, messaging services, and financial systems, with evidence of criminal activity spread across multiple organizations and jurisdictions. Investigations often depend on connecting information from these different sources to identify the actors involved and the infrastructure supporting their operations.
During Joint Disruption Week, private-sector partners contributed by removing fraudulent accounts, identifying potentially recoverable funds, and sharing investigative leads with law enforcement.
Flashpoint was among the organizations specifically recognized by the DOJ for participating in the operation, alongside Meta, Microsoft, Google, OpenAI, Coinbase, Binance, Chainalysis, Elliptic, TRM Labs, and others. For threat intelligence teams, operations like this highlight the value of identifying criminal actors, understanding how their operations are structured, and connecting activity across disparate sources to support investigative action.
Together, the arrests, account removals, and financial investigations demonstrate how coordinated efforts can target multiple components of criminal operations, from the infrastructure used to perpetrate fraud to the individuals responsible.
Joint Disruption Week marked the first coordinated international operation focused specifically on West African scam networks, according to the DOJ.
The arrests, infrastructure disruptions, and investigative leads generated during the operation represent progress against criminal organizations responsible for large-scale financial fraud and human exploitation.
Flashpoint continues to support efforts to identify and disrupt criminal activity through primary source intelligence that helps investigators understand emerging threats and the networks behind them.
For additional information on the operation and its results, read the full Department of Justice announcement.
Source: Flashpoint · 2026-10-19
France 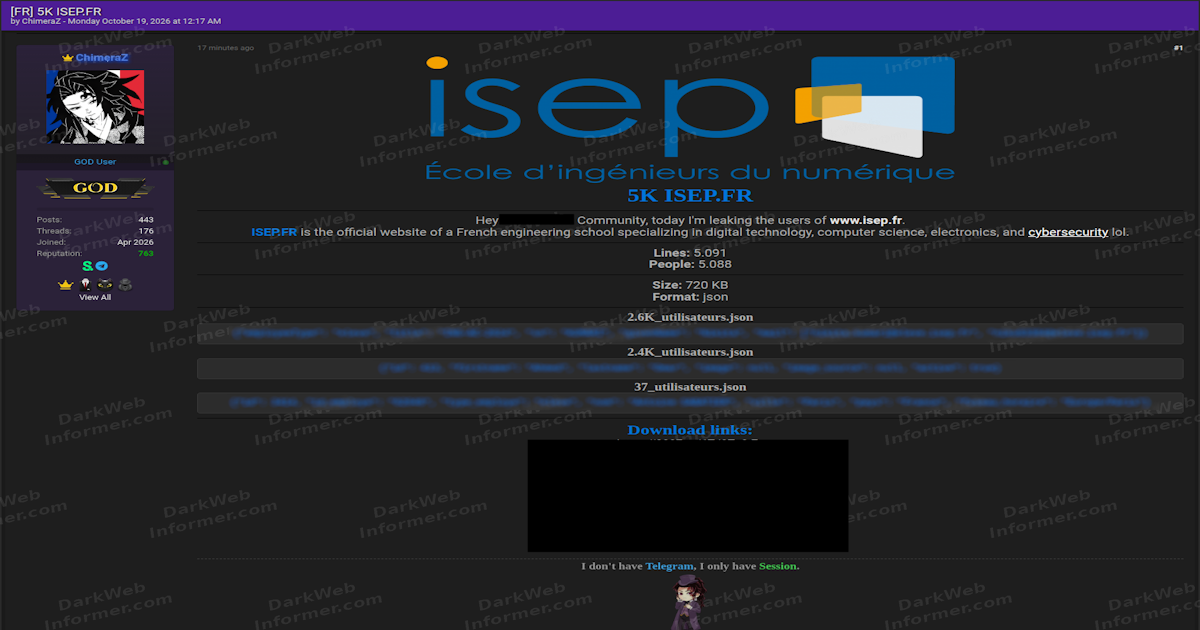
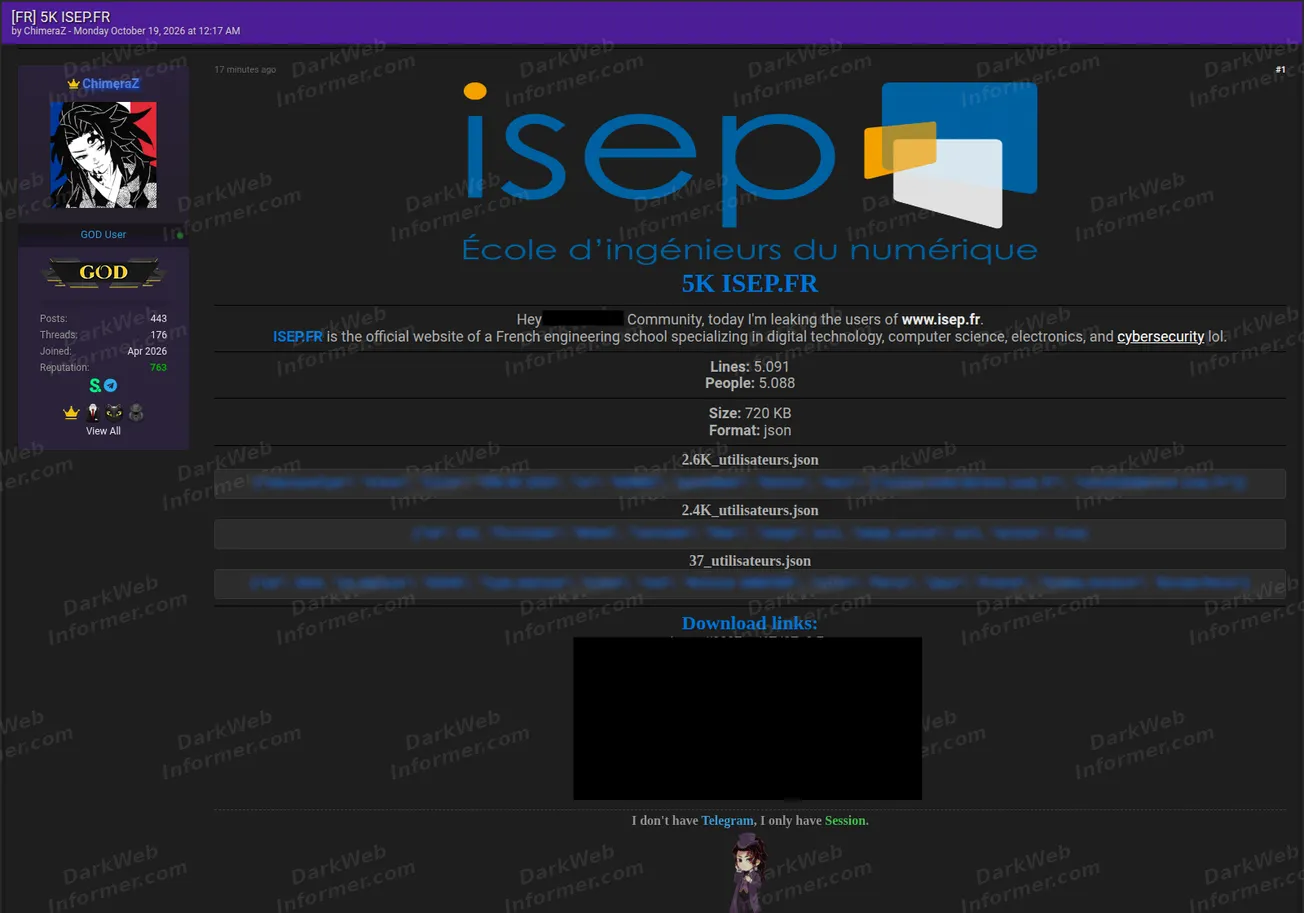
An actor using the handle “ChimeraZ” claims to have leaked a user dataset associated with ISEP, a French engineering school specializing in digital technology, computer science, electronics and cybersecurity.
The listing advertises 5,091 lines representing 5,088 people in a 720 KB JSON dataset. Three files are referenced, containing user and employee-related records with fields such as names, employee or student types, institutional email addresses, internal identifiers, city, country, activity status and timezone information. The dataset, its source, the stated counts and current availability have not been independently verified.
FranceThe visible samples show student or employee profile records from the three referenced JSON files. Personal names, email addresses and internal identifiers shown in the samples are not transcribed in this report.
Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the dataset claim.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | ChimeraZ |
Screenshot 1 |
| Named organization domain | isep[.]fr |
Screenshot 1 |
The domain identifies the organization named in the claim, not malicious infrastructure. The source screenshot states that the actor uses Session rather than Telegram, but no Session ID is visible in the supplied capture. No malware hash, Tox ID or attacker-controlled IP address is visible. Direct download mirrors shown in the source material are intentionally not reproduced here.
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
If authentic, the claimed dataset could expose student or employee names, institutional email addresses, internal identifiers, location information and account-status metadata. The combination could support targeted phishing, impersonation or other social-engineering activity involving ISEP users.
Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, 5,091-line count, 5,088-person count, sample contents or current availability. The supplied screenshot documents the listing and visible sample records, not independent confirmation of the underlying data.
Source: Dark Web Informer · 2026-10-19
No novelty required to be effective
Categories: Threat Research, X-ops, Sophos SecOps
Tags: incident response
Source: Sophos X-Ops Threat Research · 2026-10-19
<p>Automated sign-ins used the vendor’s Entra application identity to request Microsoft Graph tokens across consenting tenants</p>
Categories: Threat Research
Tags: connectwise
Source: Sophos X-Ops Threat Research · 2026-10-19