Polymarket confirms $2.7 million stolen through the compromised third-party script and pledges $3.9 million in refunds, including compensation for pause losses.
Source: HackRead · 2026-10-31
Polymarket confirms $2.7 million stolen through the compromised third-party script and pledges $3.9 million in refunds, including compensation for pause losses.
Source: HackRead · 2026-10-31
A vulnerability in TeamViewer could let attackers run code on an IT support technician’s computer when the technician…
Source: HackRead · 2026-10-30
Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week.
Source: SecurityWeek · 2026-10-30
Threat actors are attempting to exploit a high-severity unauthenticated race condition leading to remote code execution.
Source: SecurityWeek · 2026-10-30
An integer overflow tracked as CVE-2026-111585 could be used to execute arbitrary code on the viewer’s system.
Source: SecurityWeek · 2026-10-30
The AfD has confirmed that hackers breached its hosting provider. A leak site now claims to offer 421,179 of the party’s internal emails, and shows AI-written summaries rather than the emails themselves.
Read more in my article on the Hot for Security blog.
Source: Graham Cluley · 2026-10-23
Imagine buying a brand new hardware wallet for your cryptocurrency with the shrink-wrap still on… what could possibly be hiding inside? We break out a Geiger counter and a cat to find out.
Meanwhile, malicious ads are targeting journalists with zero-click attacks.
Plus, Origin’s Spencer Thompson reveals what AI agents are really getting up to on your employees’ laptops when nobody’s looking.
All this and more in episode 489 of the “Smashing Security” podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Lianne Potter.
Source: Graham Cluley · 2026-10-21
Ransomware operators including Spikey Scorpius (aka Qilin) and Tarnished Scorpius (aka Inc) are exploiting PAN-OS vulnerability CVE-2026-0257.
Source: Palo Alto Networks Unit 42 · 2026-10-20
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Source: Cyble Research · 2026-10-14
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Source: Cyble Research · 2026-10-14
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
| Subject line | Scam type |
| Re: DONATION FOR less-privileged | Charity or donation scam |
| GOD BLESS YOU…. | Emotional appeal, advance-fee scam |
| Re. Compensation funds for your past effort | Compensation fund scam |
| MY PROPOSAL | Business proposal, advance-fee scam |
| Investment Inquiry, Funding for Your Project | Investment or project funding scam |
| Dear Sir/Madam | Advance-fee scam |
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
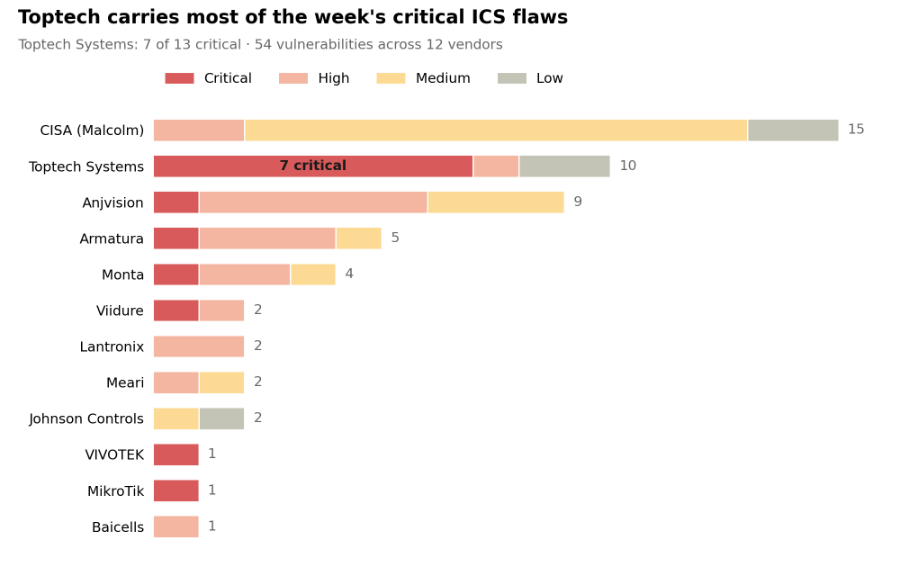
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
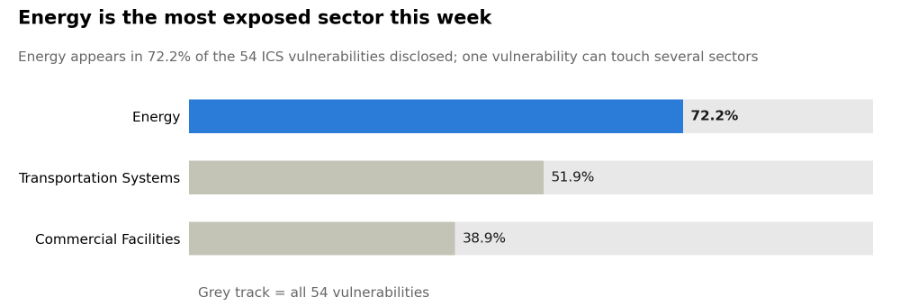
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
This weekly vulnerability report highlights several trends:
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Source: Cyble Research · 2026-10-14
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
| Subject line | Scam type |
| Re: DONATION FOR less-privileged | Charity or donation scam |
| GOD BLESS YOU…. | Emotional appeal, advance-fee scam |
| Re. Compensation funds for your past effort | Compensation fund scam |
| MY PROPOSAL | Business proposal, advance-fee scam |
| Investment Inquiry, Funding for Your Project | Investment or project funding scam |
| Dear Sir/Madam | Advance-fee scam |
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
This weekly vulnerability report highlights several trends:
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Source: Cyble Research · 2026-10-14
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Files collected from Cyble sensors were linked to several malware families:
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
| Subject line | Scam type |
| Re: DONATION FOR less-privileged | Charity or donation scam |
| GOD BLESS YOU…. | Emotional appeal, advance-fee scam |
| Re. Compensation funds for your past effort | Compensation fund scam |
| MY PROPOSAL | Business proposal, advance-fee scam |
| Investment Inquiry, Funding for Your Project | Investment or project funding scam |
| Dear Sir/Madam | Advance-fee scam |
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
This weekly vulnerability report highlights several trends:
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Source: Cyble Research · 2026-10-14
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Files collected from Cyble sensors were linked to several malware families:
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
| Subject line | Scam type |
| Re: DONATION FOR less-privileged | Charity or donation scam |
| GOD BLESS YOU…. | Emotional appeal, advance-fee scam |
| Re. Compensation funds for your past effort | Compensation fund scam |
| MY PROPOSAL | Business proposal, advance-fee scam |
| Investment Inquiry, Funding for Your Project | Investment or project funding scam |
| Dear Sir/Madam | Advance-fee scam |
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
This weekly vulnerability report highlights several trends:
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Source: Cyble Research · 2026-10-14
This Cyble Research & Intelligence Labs (CRIL) weekly vulnerability report covers two views of risk: what attackers tried against Cyble’s global honeypot sensors, and what the Cybersecurity and Infrastructure Security Agency (CISA) disclosed for industrial control systems (ICS).
The Cyble Global Sensor Intelligence (CGSI) network observed exploitation attempts against about 20 known vulnerabilities. They range from newly disclosed flaws in WordPress, Apache Solr, and Langflow to years-old bugs in GPON home routers and embedded TCP/IP stacks.
On the industrial side, CISA issued 14 ICS advisories covering 54 vulnerabilities. Of these, 13 were rated critical, 18 high, 18 medium, and five low.
Affected vendors include Toptech Systems, Lantronix, VIVOTEK, MikroTik, Armatura, Monta, Anjvision, and, unusually, CISA itself.
Cyble sensors also recorded active malware campaigns, phishing emails, and brute-force attacks against internet-exposed services.
Attackers moved quickly against newly disclosed flaws in web platforms and AI tooling, while older IoT and embedded-device bugs continued to draw steady traffic.
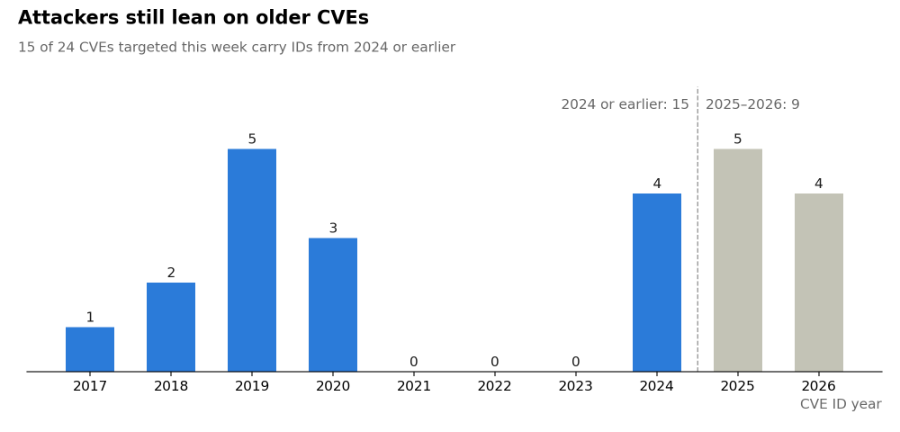
CVE-2026-63030 is a route-confusion flaw in a WordPress REST API batch endpoint. It affects WordPress 6.9.x before 6.9.5 and 7.0.x before 7.0.2.
Attackers can chain it with CVE-2026-60137 to achieve SQL injection and potentially remote code execution (RCE).
CVE-2026-44825 is a hardcoded credential in the Basic Authentication setup tool of Apache Solr 9.4.0 through 9.10.1 and 10.0.0.
Remote attackers can use it to access a Solr cluster with administrative privileges.
CVE-2026-9198 affects IBM Langflow OSS 1.0.0 through 1.10.0. Unauthenticated attackers can chain two API endpoints to obtain superuser tokens and execute arbitrary code.
Sensors also caught attempts against an older Langflow code injection flaw, CVE-2025-3248. Repeated targeting of the same AI workflow platform signals sustained attacker interest.
CVE-2025-68613 is a critical RCE flaw in the n8n workflow automation platform. Expressions supplied by authenticated users can run in an insufficiently isolated context, enabling full system compromise.
Fixes are available in versions 1.120.4, 1.121.1, and 1.122.0.
CVE-2026-4020 affects the Gravity SMTP WordPress plugin, versions 2.1.4 and earlier. An exposed REST API endpoint lets unauthenticated users pull system reports containing server details, database metadata, and configured API keys or tokens.
CVE-2024-6587 is a server-side request forgery (SSRF) flaw in LiteLLM. Exploitation can expose OpenAI API keys.
Cyble sensors also logged exploitation attempts against:
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Files collected from Cyble sensors were linked to several malware families:
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
| Subject line | Scam type |
| Re: DONATION FOR less-privileged | Charity or donation scam |
| GOD BLESS YOU…. | Emotional appeal, advance-fee scam |
| Re. Compensation funds for your past effort | Compensation fund scam |
| MY PROPOSAL | Business proposal, advance-fee scam |
| Investment Inquiry, Funding for Your Project | Investment or project funding scam |
| Dear Sir/Madam | Advance-fee scam |
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
This weekly vulnerability report highlights several trends:
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Source: Cyble Research · 2026-10-14
This Cyble Research & Intelligence Labs (CRIL) weekly vulnerability report covers two views of risk: what attackers tried against Cyble’s global honeypot sensors, and what the Cybersecurity and Infrastructure Security Agency (CISA) disclosed for industrial control systems (ICS).
The Cyble Global Sensor Intelligence (CGSI) network observed exploitation attempts against about 20 known vulnerabilities. They range from newly disclosed flaws in WordPress, Apache Solr, and Langflow to years-old bugs in GPON home routers and embedded TCP/IP stacks.
On the industrial side, CISA issued 14 ICS advisories covering 54 vulnerabilities. Of these, 13 were rated critical, 18 high, 18 medium, and five low.
Affected vendors include Toptech Systems, Lantronix, VIVOTEK, MikroTik, Armatura, Monta, Anjvision, and, unusually, CISA itself.
Cyble sensors also recorded active malware campaigns, phishing emails, and brute-force attacks against internet-exposed services.
Attackers moved quickly against newly disclosed flaws in web platforms and AI tooling, while older IoT and embedded-device bugs continued to draw steady traffic.
CVE-2026-63030 is a route-confusion flaw in a WordPress REST API batch endpoint. It affects WordPress 6.9.x before 6.9.5 and 7.0.x before 7.0.2.
Attackers can chain it with CVE-2026-60137 to achieve SQL injection and potentially remote code execution (RCE).
CVE-2026-44825 is a hardcoded credential in the Basic Authentication setup tool of Apache Solr 9.4.0 through 9.10.1 and 10.0.0.
Remote attackers can use it to access a Solr cluster with administrative privileges.
CVE-2026-9198 affects IBM Langflow OSS 1.0.0 through 1.10.0. Unauthenticated attackers can chain two API endpoints to obtain superuser tokens and execute arbitrary code.
Sensors also caught attempts against an older Langflow code injection flaw, CVE-2025-3248. Repeated targeting of the same AI workflow platform signals sustained attacker interest.
CVE-2025-68613 is a critical RCE flaw in the n8n workflow automation platform. Expressions supplied by authenticated users can run in an insufficiently isolated context, enabling full system compromise.
Fixes are available in versions 1.120.4, 1.121.1, and 1.122.0.
CVE-2026-4020 affects the Gravity SMTP WordPress plugin, versions 2.1.4 and earlier. An exposed REST API endpoint lets unauthenticated users pull system reports containing server details, database metadata, and configured API keys or tokens.
CVE-2024-6587 is a server-side request forgery (SSRF) flaw in LiteLLM. Exploitation can expose OpenAI API keys.
Cyble sensors also logged exploitation attempts against:
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Files collected from Cyble sensors were linked to several malware families:
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
| Subject line | Scam type |
| Re: DONATION FOR less-privileged | Charity or donation scam |
| GOD BLESS YOU…. | Emotional appeal, advance-fee scam |
| Re. Compensation funds for your past effort | Compensation fund scam |
| MY PROPOSAL | Business proposal, advance-fee scam |
| Investment Inquiry, Funding for Your Project | Investment or project funding scam |
| Dear Sir/Madam | Advance-fee scam |
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
This weekly vulnerability report highlights several trends:
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Source: Cyble Research · 2026-10-14