Container security has a familiar problem. Teams identify vulnerabilities, but turning those findings into lower risk is much harder. A standard container image may include operating-system packages, development tools, debugging utilities and libraries that an application never uses. Each unnecessary component can expand the attack surface and add vulnerabilities to investigate, patch or explain during an audit. Consider an NGINX image that contains 274 categorized vulnerabilities straight from download. Scanning makes those findings visible, but … More →
Novee’s External Surface Testing is a new capability in its AI penetration testing platform that helps security teams discover internet-facing assets and validate exploitable vulnerabilities. It tests newly disclosed CVEs and findings imported from third-party external attack surface management (EASM) tools. “Attackers don’t limit themselves to the applications you’re already testing. They look for anything exposed to the internet – forgotten subdomains, staging servers left online, and infrastructure your team may not even know exists. … More →
Security teams have more vulnerability data at their disposal than ever. But even the best intelligence has limited value if teams can’t determine where those vulnerabilities exist within their own environment.
For many organizations, that visibility remains a challenge. Asset inventories, scanners, and ticketing systems provide valuable information, but connecting those insights with real-world exploit activity isn’t always straightforward. And as environments evolve, undocumented assets, forgotten infrastructure, and newly exposed systems can introduce risks that traditional inventories may miss.
Flashpoint External Attack Surface Management (EASM) helps close that gap by connecting continuous discovery of internet-facing assets with Flashpoint’s threat-informed Vulnerability Intelligence. With coverage of more than 480,000 vulnerabilities, including over 105,000 not found in NVD or CVE, Flashpoint provides context on active exploitation, exploit maturity, and ransomware risk through its patented Ransomware Risk model. Together, these capabilities help teams identify which exposures warrant the most immediate attention.
What is EASM? External Attack Surface Management (EASM) is the continuous discovery and monitoring of an organization’s internet-facing assets, including domains, subdomains, IPs, and infrastructure that isn’t formally tracked. It gives security teams visibility into what’s exposed to the internet, whether or not that infrastructure was deliberately set up or documented.
How EASM Extends Vulnerability Prioritization to Your Full Environment
EASM continuously discovers internet-facing assets associated with an organization, including domains, subdomains, IP addresses, and infrastructure that may not appear in existing inventories. This could include a subsidiary’s infrastructure following an acquisition, a forgotten staging environment, or a cloud instance that remains active long after a project ends.
With Flashpoint EASM, discovered assets enter a triage queue organized by relevance, helping teams focus on assets that warrant further investigation. Once ownership is confirmed, Flashpoint maps those assets against its Vulnerability Intelligence to identify vulnerabilities associated with the software versions running on them.
Findings are prioritized using Flashpoint KEV, EPSS, and Ransomware Risk scores. Asset-level details also show the products and versions responsible for identified exposures, along with potentially high-risk open ports such as RDP and SSH. This gives teams the context they need to assess risk and determine where remediation should begin.
Example Scenario
Consider a development team that deploys a staging server running an outdated web framework. The project ends, but the server remains online and is never added to the organization’s asset inventory.
Flashpoint EASM discovers the server and shows how it connects to the organization’s infrastructure. Once the team confirms ownership, Flashpoint Vulnerability Intelligence identifies an actively exploited CVE affecting the framework version.
The team can now investigate an exposure that might otherwise have gone unnoticed and prioritize remediation based on evidence of active exploitation.
Why This Matters More in Regulated Industries
For organizations in heavily regulated industries such as financial services and healthcare, incomplete asset visibility can introduce additional compliance and security risks. Requirements under frameworks and regulations such as GLBA and HIPAA make maintaining appropriate safeguards especially important. An unknown, internet-facing asset with an exploitable vulnerability can create exposure regardless of whether it appears in the organization’s CMDB.
Mergers and acquisitions can complicate this further. Acquired organizations bring infrastructure that security teams may have limited visibility into, including assets that have not yet been incorporated into existing monitoring processes.
Continuous external asset discovery helps teams identify and assess that infrastructure earlier, reducing reliance on periodic audits or manual inventory updates to uncover potential exposures.
Discovery and Prioritization, Built Into One Platform
When attack surface discovery and vulnerability intelligence operate in separate systems, security teams may need to manually correlate asset inventories with vulnerability findings. That process becomes increasingly difficult as infrastructure changes and new vulnerabilities emerge.
Flashpoint brings these capabilities together in one platform, an approach we call attack surface intelligence. Newly discovered assets can be evaluated against Flashpoint’s Vulnerability Intelligence, giving teams access to threat-informed prioritization within the same workflow.
For teams already using Flashpoint Vulnerability Intelligence, EASM can be added as a module within the existing Ignite platform, with no separate console to manage. Contact your account team to learn more about adding EASM to your deployment. New to Flashpoint? Schedule a demo to explore how Vulnerability Intelligence and EASM work together to help your team identify and prioritize external exposures.
Frequently Asked Questions
How is EASM different from a vulnerability scanner?
Traditional vulnerability scanners scan assets you already know about and tell them to check, typically from inside the network perimeter. EASM continuously discovers internet-facing assets from the outside, including unknown infrastructure like forgotten test environments and acquired systems, then enriches them with vulnerability intelligence beyond public sources like NVD and CVE. The two are complementary: scanners provide depth on known internal assets, while EASM extends that visibility to what’s exposed externally.
Can EASM help identify compound risk on a single asset?
Yes. The Vulnerable Assets view surfaces how many vulnerabilities are tied to a given asset, so teams can quickly spot assets carrying disproportionate risk and prioritize accordingly, rather than treating every finding as an isolated issue.
If we’re already running Flashpoint Vulnerability Intelligence, do we need a new implementation to add EASM?
No. EASM is a module inside the platform you’re already using. It appears inside the same Ignite workflows your team relies on today, with no separate console or parallel rollout required.
How is EASM priced?
EASM is priced based on company size rather than asset count or seats, so costs are predictable and don’t scale up just because the attack surface grows.
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
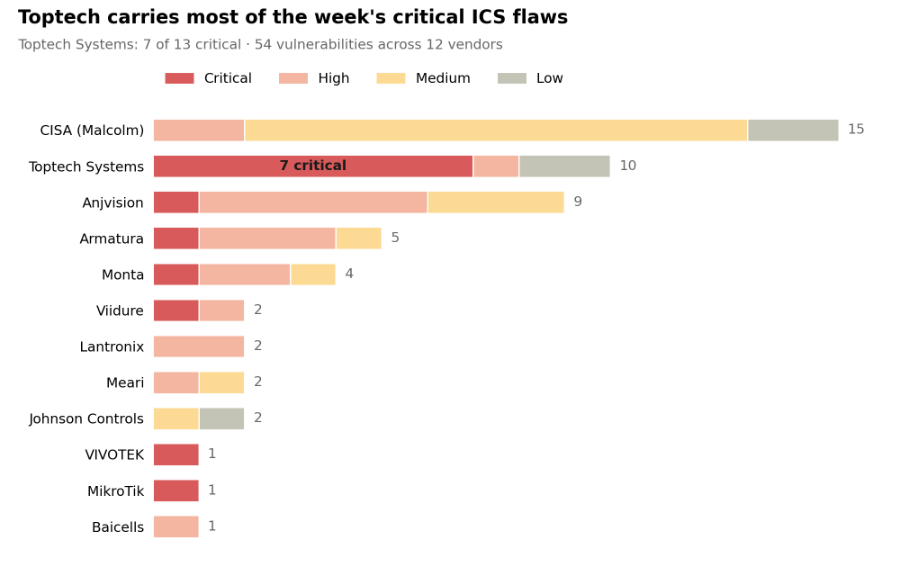
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
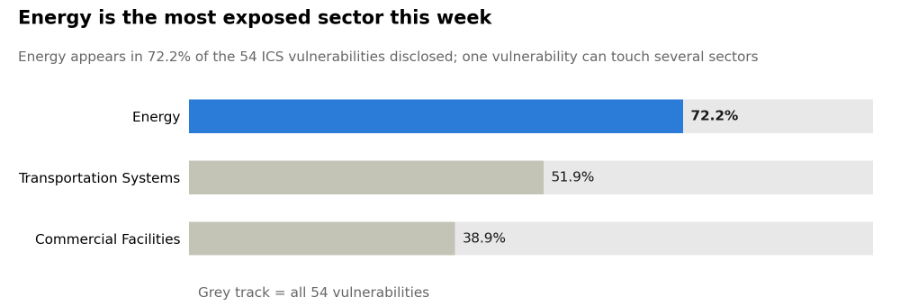
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2025-46565, a file access control bypass in the Vite development server
Command injection flaws in QNAP QTS firmware
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2025-2010, an unauthenticated SQL injection flaw in the JobWP WordPress plugin
CVE-2025-46565, a file access control bypass in the Vite development server
Command injection flaws in QNAP QTS firmware
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2024-25600, a code injection flaw in Bricks Builder 1.9.6 and earlier
CVE-2025-2010, an unauthenticated SQL injection flaw in the JobWP WordPress plugin
CVE-2025-46565, a file access control bypass in the Vite development server
Command injection flaws in QNAP QTS firmware
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2024-4577, a critical PHP-CGI argument injection flaw
CVE-2024-25600, a code injection flaw in Bricks Builder 1.9.6 and earlier
CVE-2025-2010, an unauthenticated SQL injection flaw in the JobWP WordPress plugin
CVE-2025-46565, a file access control bypass in the Vite development server
Command injection flaws in QNAP QTS firmware
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2024-7591, an OS command injection flaw in Progress LoadMaster
CVE-2024-4577, a critical PHP-CGI argument injection flaw
CVE-2024-25600, a code injection flaw in Bricks Builder 1.9.6 and earlier
CVE-2025-2010, an unauthenticated SQL injection flaw in the JobWP WordPress plugin
CVE-2025-46565, a file access control bypass in the Vite development server
Command injection flaws in QNAP QTS firmware
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
CVE-2025-58360, an XML external entity (XXE) flaw in GeoServer’s GetMap operation
CVE-2024-7591, an OS command injection flaw in Progress LoadMaster
CVE-2024-4577, a critical PHP-CGI argument injection flaw
CVE-2024-25600, a code injection flaw in Bricks Builder 1.9.6 and earlier
CVE-2025-2010, an unauthenticated SQL injection flaw in the JobWP WordPress plugin
CVE-2025-46565, a file access control bypass in the Vite development server
Command injection flaws in QNAP QTS firmware
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
This Cyble Research & Intelligence Labs (CRIL) weekly vulnerability report covers two views of risk: what attackers tried against Cyble’s global honeypot sensors, and what the Cybersecurity and Infrastructure Security Agency (CISA) disclosed for industrial control systems (ICS).
The Cyble Global Sensor Intelligence (CGSI) network observed exploitation attempts against about 20 known vulnerabilities. They range from newly disclosed flaws in WordPress, Apache Solr, and Langflow to years-old bugs in GPON home routers and embedded TCP/IP stacks.
On the industrial side, CISA issued 14 ICS advisories covering 54 vulnerabilities. Of these, 13 were rated critical, 18 high, 18 medium, and five low.
Cyble sensors also recorded active malware campaigns, phishing emails, and brute-force attacks against internet-exposed services.
Real-World Attacks Observed by Cyble Sensors
Attackers moved quickly against newly disclosed flaws in web platforms and AI tooling, while older IoT and embedded-device bugs continued to draw steady traffic.
Source: Cyble sensor intelligence. The 24 CVEs named in this post, counted by CVE ID year
CVE-2026-63030 — WordPress REST API
CVE-2026-63030 is a route-confusion flaw in a WordPress REST API batch endpoint. It affects WordPress 6.9.x before 6.9.5 and 7.0.x before 7.0.2.
Attackers can chain it with CVE-2026-60137 to achieve SQL injection and potentially remote code execution (RCE).
CVE-2026-44825 — Apache Solr
CVE-2026-44825 is a hardcoded credential in the Basic Authentication setup tool of Apache Solr 9.4.0 through 9.10.1 and 10.0.0.
Remote attackers can use it to access a Solr cluster with administrative privileges.
CVE-2026-9198 — Langflow
CVE-2026-9198 affects IBM Langflow OSS 1.0.0 through 1.10.0. Unauthenticated attackers can chain two API endpoints to obtain superuser tokens and execute arbitrary code.
Sensors also caught attempts against an older Langflow code injection flaw, CVE-2025-3248. Repeated targeting of the same AI workflow platform signals sustained attacker interest.
CVE-2025-68613 — n8n
CVE-2025-68613 is a critical RCE flaw in the n8n workflow automation platform. Expressions supplied by authenticated users can run in an insufficiently isolated context, enabling full system compromise.
Fixes are available in versions 1.120.4, 1.121.1, and 1.122.0.
CVE-2026-4020 — Gravity SMTP
CVE-2026-4020 affects the Gravity SMTP WordPress plugin, versions 2.1.4 and earlier. An exposed REST API endpoint lets unauthenticated users pull system reports containing server details, database metadata, and configured API keys or tokens.
CVE-2024-6587 — LiteLLM
CVE-2024-6587 is a server-side request forgery (SSRF) flaw in LiteLLM. Exploitation can expose OpenAI API keys.
Older Flaws Still in Rotation
Cyble sensors also logged exploitation attempts against:
CVE-2025-58360, an XML external entity (XXE) flaw in GeoServer’s GetMap operation
CVE-2024-7591, an OS command injection flaw in Progress LoadMaster
CVE-2024-4577, a critical PHP-CGI argument injection flaw
CVE-2024-25600, a code injection flaw in Bricks Builder 1.9.6 and earlier
CVE-2025-2010, an unauthenticated SQL injection flaw in the JobWP WordPress plugin
CVE-2025-46565, a file access control bypass in the Vite development server
Command injection flaws in QNAP QTS firmware
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
This Cyble Research & Intelligence Labs (CRIL) weekly vulnerability report covers two views of risk: what attackers tried against Cyble’s global honeypot sensors, and what the Cybersecurity and Infrastructure Security Agency (CISA) disclosed for industrial control systems (ICS).
The Cyble Global Sensor Intelligence (CGSI) network observed exploitation attempts against about 20 known vulnerabilities. They range from newly disclosed flaws in WordPress, Apache Solr, and Langflow to years-old bugs in GPON home routers and embedded TCP/IP stacks.
On the industrial side, CISA issued 14 ICS advisories covering 54 vulnerabilities. Of these, 13 were rated critical, 18 high, 18 medium, and five low.
Cyble sensors also recorded active malware campaigns, phishing emails, and brute-force attacks against internet-exposed services.
Real-World Attacks Observed by Cyble Sensors
Attackers moved quickly against newly disclosed flaws in web platforms and AI tooling, while older IoT and embedded-device bugs continued to draw steady traffic.
Source: Cyble sensor intelligence. The 24 CVEs named in this post, counted by CVE ID year
CVE-2026-63030 — WordPress REST API
CVE-2026-63030 is a route-confusion flaw in a WordPress REST API batch endpoint. It affects WordPress 6.9.x before 6.9.5 and 7.0.x before 7.0.2.
Attackers can chain it with CVE-2026-60137 to achieve SQL injection and potentially remote code execution (RCE).
CVE-2026-44825 — Apache Solr
CVE-2026-44825 is a hardcoded credential in the Basic Authentication setup tool of Apache Solr 9.4.0 through 9.10.1 and 10.0.0.
Remote attackers can use it to access a Solr cluster with administrative privileges.
CVE-2026-9198 — Langflow
CVE-2026-9198 affects IBM Langflow OSS 1.0.0 through 1.10.0. Unauthenticated attackers can chain two API endpoints to obtain superuser tokens and execute arbitrary code.
Sensors also caught attempts against an older Langflow code injection flaw, CVE-2025-3248. Repeated targeting of the same AI workflow platform signals sustained attacker interest.
CVE-2025-68613 — n8n
CVE-2025-68613 is a critical RCE flaw in the n8n workflow automation platform. Expressions supplied by authenticated users can run in an insufficiently isolated context, enabling full system compromise.
Fixes are available in versions 1.120.4, 1.121.1, and 1.122.0.
CVE-2026-4020 — Gravity SMTP
CVE-2026-4020 affects the Gravity SMTP WordPress plugin, versions 2.1.4 and earlier. An exposed REST API endpoint lets unauthenticated users pull system reports containing server details, database metadata, and configured API keys or tokens.
CVE-2024-6587 — LiteLLM
CVE-2024-6587 is a server-side request forgery (SSRF) flaw in LiteLLM. Exploitation can expose OpenAI API keys.
Older Flaws Still in Rotation
Cyble sensors also logged exploitation attempts against:
CVE-2025-58360, an XML external entity (XXE) flaw in GeoServer’s GetMap operation
CVE-2024-7591, an OS command injection flaw in Progress LoadMaster
CVE-2024-4577, a critical PHP-CGI argument injection flaw
CVE-2024-25600, a code injection flaw in Bricks Builder 1.9.6 and earlier
CVE-2025-2010, an unauthenticated SQL injection flaw in the JobWP WordPress plugin
CVE-2025-46565, a file access control bypass in the Vite development server
Command injection flaws in QNAP QTS firmware
Scanning for the Cisco Adaptive Security Appliance (ASA) WebVPN login page
A Mirai variant is also targeting Dasan GPON home routers by chaining CVE-2018-10561 and CVE-2018-10562. Together, the two flaws let an unauthenticated remote attacker run commands on the device.
Most-Attempted CVEs
CVE-2020-11899, an IPv6 out-of-bounds read in the Treck TCP/IP stack, drew far more exploitation attempts than any other CVE this week. The rest of the top five, in order:
A group of four Wind River VxWorks TCP buffer overflows: CVE-2019-12255, CVE-2019-12260, CVE-2019-12261, and CVE-2019-12263
CVE-2020-11900, an IPv4 tunneling double-free in the Treck TCP/IP stack
CVE-2019-0708, a critical unauthenticated RCE in Microsoft Remote Desktop Services
CVE-2020-11910, an ICMPv4 out-of-bounds read in the Treck TCP/IP stack
Most of these flaws sit in networking code embedded in IoT and industrial devices, which often go unpatched for years.
Malware Families Observed
Files collected from Cyble sensors were linked to several malware families:
CoinMiner: Linux cryptominers that hijack CPU and GPU resources
WannaCry: Ransomware that spreads through the EternalBlue exploit, targeting CVE-2017-0147
Mirai: A botnet that turns IoT devices and Linux servers into remotely controlled bots
IRCBot: Linux malware that uses IRC connections as a backdoor
CRIL also observed Hajime, Gafgyt, and Wacatac activity.
MacSync Infostealer Targets Crypto Users
CRIL is also tracking a new version of MacSync, a macOS infostealer sold as malware-as-a-service. Kaspersky’s Securelist reported that the latest campaign targets cryptocurrency users and developers.
According to Securelist, attackers distribute MacSync through malicious disk images posing as a fake crypto wallet app. In one case, they abused a public iCloud calendar event to deliver commands.
The malware steals browser data, saved credentials, crypto wallet data, Keychain files, and SSH, AWS, Kubernetes, and Git configurations. It also installs a backdoor disguised as Finder that persists through a LaunchAgent, shell profile changes, and Git hooks.
Security teams should watch macOS endpoints for unexpected disk-image apps, removal of quarantine attributes, and new LaunchAgents.
Phishing and Advance-Fee Scams
Phishing emails captured by Cyble sensors relied on emotional appeals and promises of money. Common lures this week:
Subject line
Scam type
Re: DONATION FOR less-privileged
Charity or donation scam
GOD BLESS YOU….
Emotional appeal, advance-fee scam
Re. Compensation funds for your past effort
Compensation fund scam
MY PROPOSAL
Business proposal, advance-fee scam
Investment Inquiry, Funding for Your Project
Investment or project funding scam
Dear Sir/Madam
Advance-fee scam
Many of these emails use look-alike domains or impersonate known organizations to appear credible.
Brute-Force Attacks
Brute-force traffic focused on remote access and database ports, including VNC (5900), RDP (3389), SSH (22), Telnet (23), HTTP (80), Microsoft SQL Server (1433), and PPTP (1723).
Targets included Elasticsearch, Hadoop, Oracle, GitLab, MySQL, and PostgreSQL. Attackers leaned on default and weak credentials such as “sa,” “root,” “password,” and “123456.”
The largest share of attack traffic, 39%, came from sources with a known bad reputation.
Critical ICS Vulnerabilities
CISA’s 14 ICS advisories covered 54 vulnerabilities, two-thirds of them rated high or medium. Toptech Systems and CISA itself disclosed the most flaws this week.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · 54 vulnerabilities by vendor and severity
Toptech Systems TMS7 and TopHAT (Critical)
Toptech Systems’ TMS7 and TopHAT version 7.6.3 carried more critical-rated ICS vulnerabilities than any other product this week. They include multiple SQL injection flaws (such as CVE-2026-72510 and CVE-2026-63713), an unrestricted file upload flaw (CVE-2026-70356), and files exposed to external parties (CVE-2026-71379).
TMS7 is a terminal management system that controls liquid fuel and chemical distribution in the Energy, Chemical, and Transportation Systems sectors. In a product that governs fuel terminal operations, these flaws could enable interference with physical processes, not just data theft. Toptech has published security update information.
CVE-2026-91191 and CVE-2026-84409 — Lantronix G520 Series (High)
Two flaws affect Lantronix G520 Series cellular gateways running 2.6.0.4R6_stable. CVE-2026-91191 is an improper cryptographic signature verification flaw, and CVE-2026-84409 is a cross-site scripting (XSS) flaw.
The signature flaw could let attackers bypass firmware integrity checks and push unauthorized firmware to remote field devices. Combined with the XSS bug, it creates a realistic multistage attack path against devices that may be hard to inspect physically. Lantronix has published remediation details.
CVE-2026-84411 — MikroTik RouterOS (Critical)
CVE-2026-84411 is a critical integer underflow vulnerability in MikroTik RouterOS versions before 7.24. Updated versions are available from MikroTik’s download page.
CVE-2026-22755 — VIVOTEK Cameras (Critical)
CVE-2026-22755 is a critical command injection flaw affecting 37 VIVOTEK camera models across its V, C, S, Dome, Bullet, and Panoramic series. VIVOTEK has posted an update package.
CVE-2026-95102 — Monta (Critical)
CVE-2026-95102 is a missing-authentication flaw for a critical function in all versions of monta.app. Three other Monta flaws involve excessive authentication attempts, session expiration, and credential protection. The advisory data referenced no vendor fix.
Anjvision, Viidure, and Armatura One
Anjvision’s YSSD-RTMP-H5 firmware has nine vulnerabilities, led by CVE-2026-100291, a critical insecure default setting. Others include OS command injection, hardcoded credentials, and improper signature verification.
The Viidure Dashcam Android app, version 3.3.1.260403 and earlier, contains hardcoded credentials (CVE-2026-96587, critical). Armatura One is affected by CVE-2023-46604, a critical deserialization flaw, plus hardcoded key and credential issues.
No vendor fixes were referenced for these products, so compensating controls such as network isolation are the main option for now.
CISA Malcolm (15 Vulnerabilities)
In an unusual disclosure, CISA reported 15 vulnerabilities in Malcolm, its own open-source network traffic analysis and threat-hunting platform. The flaws affect versions before 26.06.0.
They span authentication bypass, missing authorization, default credentials, OS command injection, path traversal, and SSRF. Most are rated medium, and two are rated high. Users should update through the Malcolm releases page.
The remaining advisories covered Baicells Technologies, Meari, and Johnson Controls products.
Impacted Critical Infrastructure Sectors
Energy was the most exposed sector this week, followed by Transportation Systems and Commercial Facilities.
Source: CISA ICS advisories analyzed by CRIL, Sept. 29–Oct. 5, 2026 · share of 54 vulnerabilities touching each sector
The largest single combination, Energy, Information Technology, and Water and Wastewater, accounted for 27.8% of vulnerabilities. Energy, Chemical, and Transportation Systems made up another 18.5%, driven largely by the Toptech disclosures.
These disclosures cut across traditional infrastructure boundaries rather than clustering in one domain. A single flaw in a shared product can create risk for fuel, water, and transportation operators at once.
Conclusion
This weekly vulnerability report highlights several trends:
Fast exploitation of newly disclosed flaws in WordPress, Apache Solr, and AI workflow tools such as Langflow and n8n
Persistent attacks on years-old embedded-device and router vulnerabilities
Critical ICS flaws in fuel distribution, cellular gateway, and camera products
Several ICS products with no vendor fix referenced, leaving compensating controls as the main defense
Ongoing phishing and brute-force activity that relies on weak and default credentials
With 13 critical ICS vulnerabilities and active exploitation attempts against both new and legacy flaws, organizations face risk across enterprise IT and operational technology (OT) environments.
Key Recommendations From This Weekly Vulnerability Report
Patch internet-exposed web platforms, plugins, and AI workflow tools first, starting with the flaws under active exploitation above
Replace default usernames and passwords, and enforce strong, unique credentials on servers and devices
Restrict or block exposed remote access and database ports, including VNC, RDP, SSH, Telnet, and SQL Server
Segment IT and OT networks with firewalls and demilitarized zones (DMZs) to limit lateral movement
Apply compensating controls, such as network isolation, for ICS products without available fixes
Verify firmware integrity on remote field devices and cellular gateways
Monitor macOS endpoints for unexpected disk-image apps and new LaunchAgents
Track CISA advisories and the Known Exploited Vulnerabilities (KEV) catalog, and prioritize by exploitability and operational impact
Conduct regular vulnerability assessments and penetration testing
Cyble’s attack surface management and vulnerability intelligence solutions help organizations identify exposed assets, prioritize remediation, and detect early signs of compromise. Combined with real-time sensor intelligence, they help security teams stay ahead of threats across enterprise and critical infrastructure environments. To see these capabilities in action, schedule a demo with Cyble.
Disclaimer: The data and content written in this blog is based on certain sensor and open web information available. Analysts and researchers are advised to confirm once again from original sources.
 Table Of Contents