Tag: Leaks

  • Bangkok Post Breach Claim Includes 822,140 Member Accounts and 6.9 GB Infrastructure Dump

    Data Exposure Report
    Bangkok Post Breach Claim Includes 822,140 Member Accounts and 6.9 GB Infrastructure DumpThailand
    Media
    Member & Infrastructure Data
    Leak Claim
    Unverified

    Bangkok Post Breach Claim Includes 822,140 Member Accounts and 6.9 GB Infrastructure Dump

    Claimed members822,140
    Claimed files49,783
    Employees385
    Extracted size6.9 GB

    Bangkok Post Breach Claim Includes 822,140 Member Accounts and 6.9 GB Infrastructure Dump

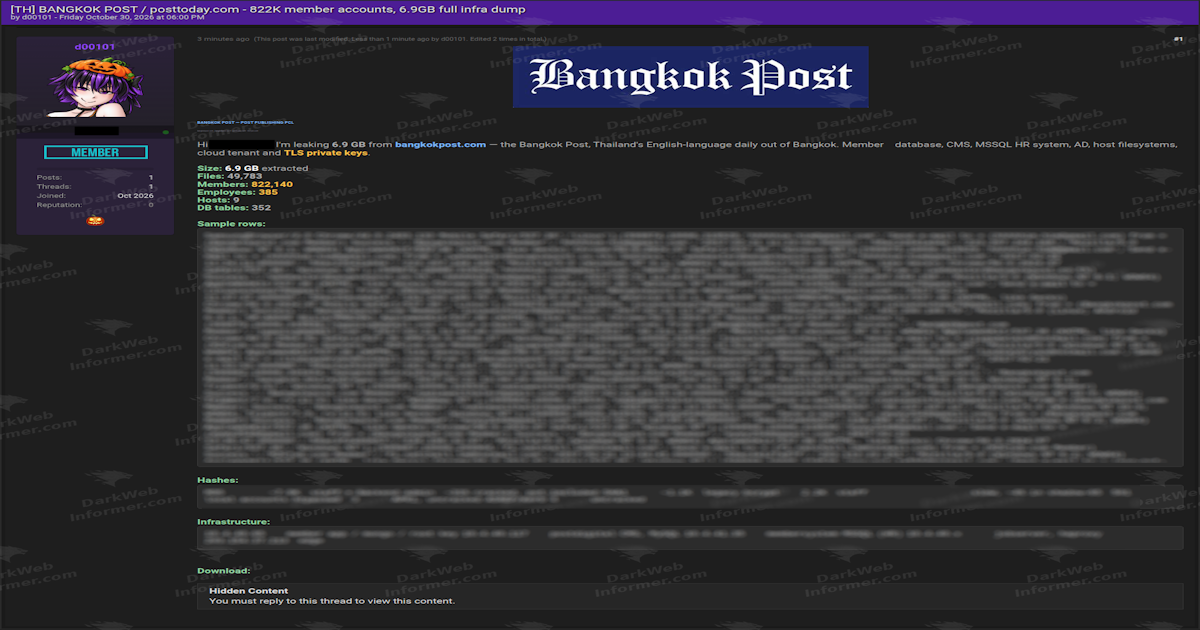
    An actor using the handle “d00101” claims to have leaked approximately 6.9 GB of data associated with Bangkok Post, including member data and internal infrastructure material.

    The listing advertises 49,783 files, 822,140 member records, 385 employee records, 9 hosts and 352 database tables. The actor says the dump includes member databases, CMS data, an MSSQL HR system, Active Directory-related material, host filesystems, cloud-tenant data and TLS private-key material. The breach, dataset contents, record counts and infrastructure claims have not been independently verified.

    Post details

    OrganizationBangkok Post
    CountryBangkok Post Breach Claim Includes 822,140 Member Accounts and 6.9 GB Infrastructure DumpThailand
    SectorMedia / publishing
    Actor“d00101”
    Claimed size6.9 GB
    Claimed files49,783
    Claimed members822,140
    Post date shown

    What the post claims

    • 6.9 GB extracted
    • 49,783 files
    • 822,140 member records
    • 385 employee records
    • 9 internal hosts referenced
    • 352 database tables
    • Member database material included
    • CMS data included
    • MSSQL HR system data included
    • Active Directory-related material included
    • Host filesystem data included
    • Cloud-tenant data included
    • TLS private-key material claimed
    • Password-hash material listed
    • Sample member records displayed
    • Internal infrastructure services listed

    The actor also lists password-hash collections using MD5, SHA-1 and bcrypt and claims that a portion of the hashes were already cracked. The screenshot includes sample member emails, public IP addresses and internal infrastructure details; those values are not transcribed in this report.

    Screenshots

    The supplied capture shows the Bangkok Post claim, the stated file, member, employee, host and database-table counts, sample member rows, password-hash references and internal infrastructure categories. Personal sample data and sensitive infrastructure values are not repeated here.

    IOCs & identifiers

    Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the breach claim.

    Type Identifier Source
    Actor handle d00101 Screenshot 1
    Named organization domain bangkokpost[.]com Screenshot 1

    The organization domain identifies the entity named in the claim, not malicious infrastructure. Internal RFC1918 addresses, private-key material, sample user emails and other sensitive values shown in the screenshot are intentionally not reproduced here.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    Potential impact

    If authentic, the claimed exposure could affect member accounts, employee records, authentication material, internal systems and cryptographic assets. The combination of member data, password hashes, internal infrastructure information and claimed TLS key material could increase risks of account takeover, phishing, credential reuse, internal-system targeting and broader follow-on compromise.

    Status Unverified

    Dark Web Informer has not independently verified the breach, 6.9 GB extraction size, file counts, member or employee totals, password-hash claims, private-key claims, infrastructure access or current availability of the purported material. The supplied screenshot documents the actor’s listing and visible evidence only.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-30

  • Defy Club Data Leak Claim Exposes 23,149 User Accounts With 23K+ Phone Numbers and 9K+ Emails

    Data Exposure Report
    Defy Club Data Leak Claim Exposes 23,149 User Accounts With 23K+ Phone Numbers and 9K+ EmailsIndia
    Social Crypto Platform
    User Contact Data
    Free Leak
    Unverified

    Defy Club Data Leak Claim Exposes 23,149 User Accounts With 23K+ Phone Numbers and 9K+ Emails

    Claimed accounts23,149
    Phone numbers23K+
    Email addresses9K+
    Compressed size805 KB

    Defy Club Data Leak Claim Exposes 23,149 User Accounts With 23K+ Phone Numbers and 9K+ Emails

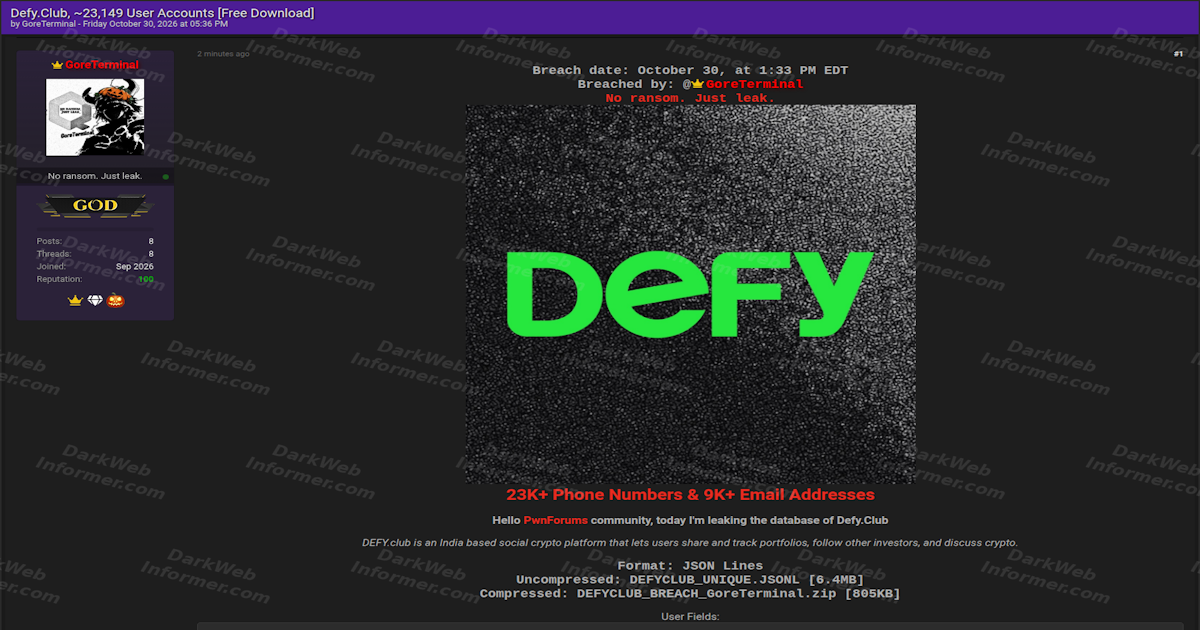
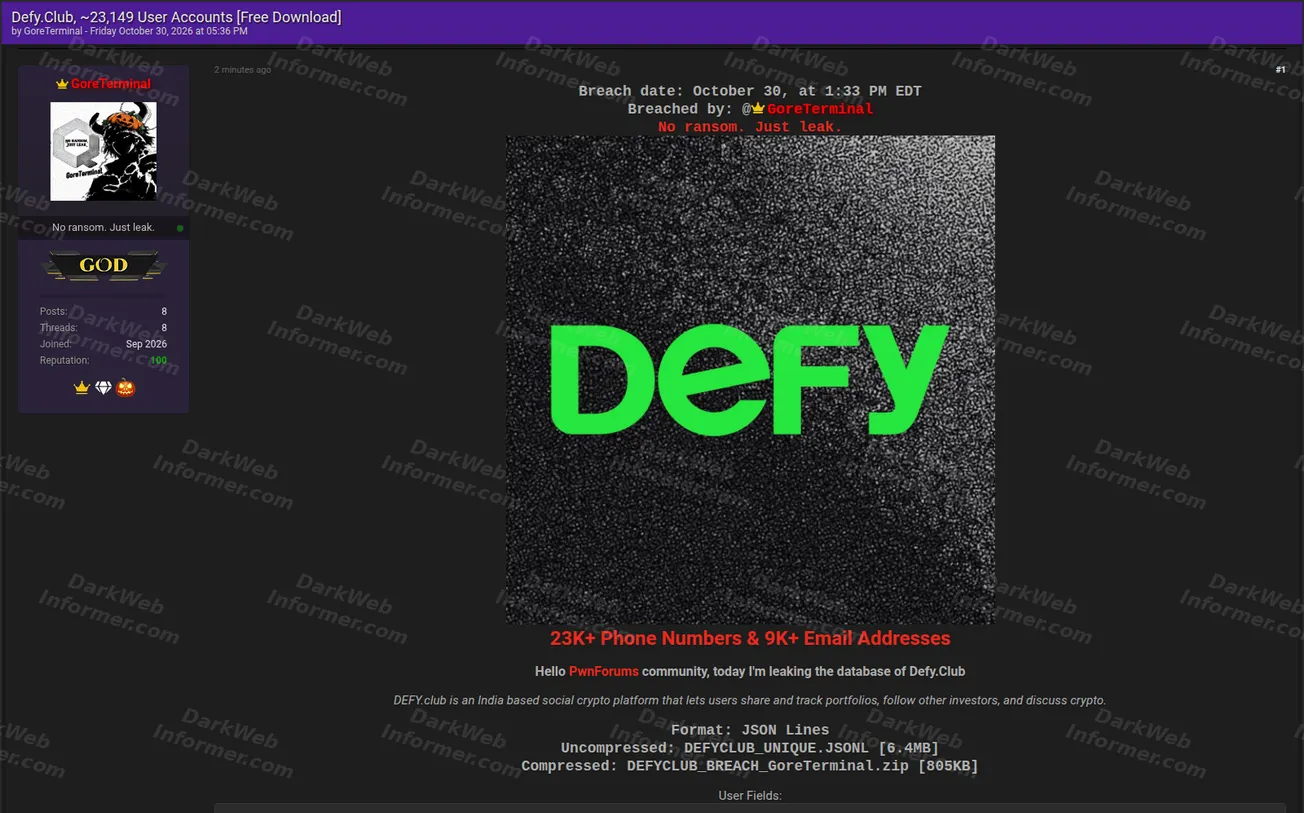
    An actor using the handle “GoreTerminal” claims to have leaked a Defy Club dataset containing approximately 23,149 user accounts. The post describes DEFY.club as an India-based social crypto platform that lets users share and track portfolios, follow other investors and discuss cryptocurrency.

    The actor says the breach occurred on October 30, 2026 at 1:33 PM EDT and characterizes the release as a leak rather than a ransom event. The post highlights 23K+ phone numbers and 9K+ email addresses. The archive is described as JSON Lines, with an uncompressed file named DEFYCLUB_UNIQUE.JSONL at 6.4 MB and a compressed archive at 805 KB. The dataset, its source, the stated counts and current availability have not been independently verified.

    Post details

    OrganizationDefy Club
    CountryDefy Club Data Leak Claim Exposes 23,149 User Accounts With 23K+ Phone Numbers and 9K+ EmailsIndia
    SectorSocial crypto / investment community
    Actor“GoreTerminal”
    Claimed accountsApproximately 23,149
    FormatJSON Lines
    Archive sizes6.4 MB raw / 805 KB compressed
    Claimed breach timeOct 30, 2026 at 1:33 PM EDT

    What the post claims

    • Approximately 23,149 user accounts
    • 23K+ phone numbers
    • 9K+ email addresses
    • JSON Lines format
    • 6.4 MB uncompressed file
    • 805 KB compressed archive
    • Country field included
    • Email field included
    • Phone and international-phone fields included
    • Mobile-carrier field included
    • Internet-protocol address field included
    • User and account identifiers included
    • Platform / device fields included
    • Build and previous-version fields included
    • Registration-region fields included
    • Profile-created timestamp included
    • Source / status fields included
    • Sample records displayed
    • Free download advertised

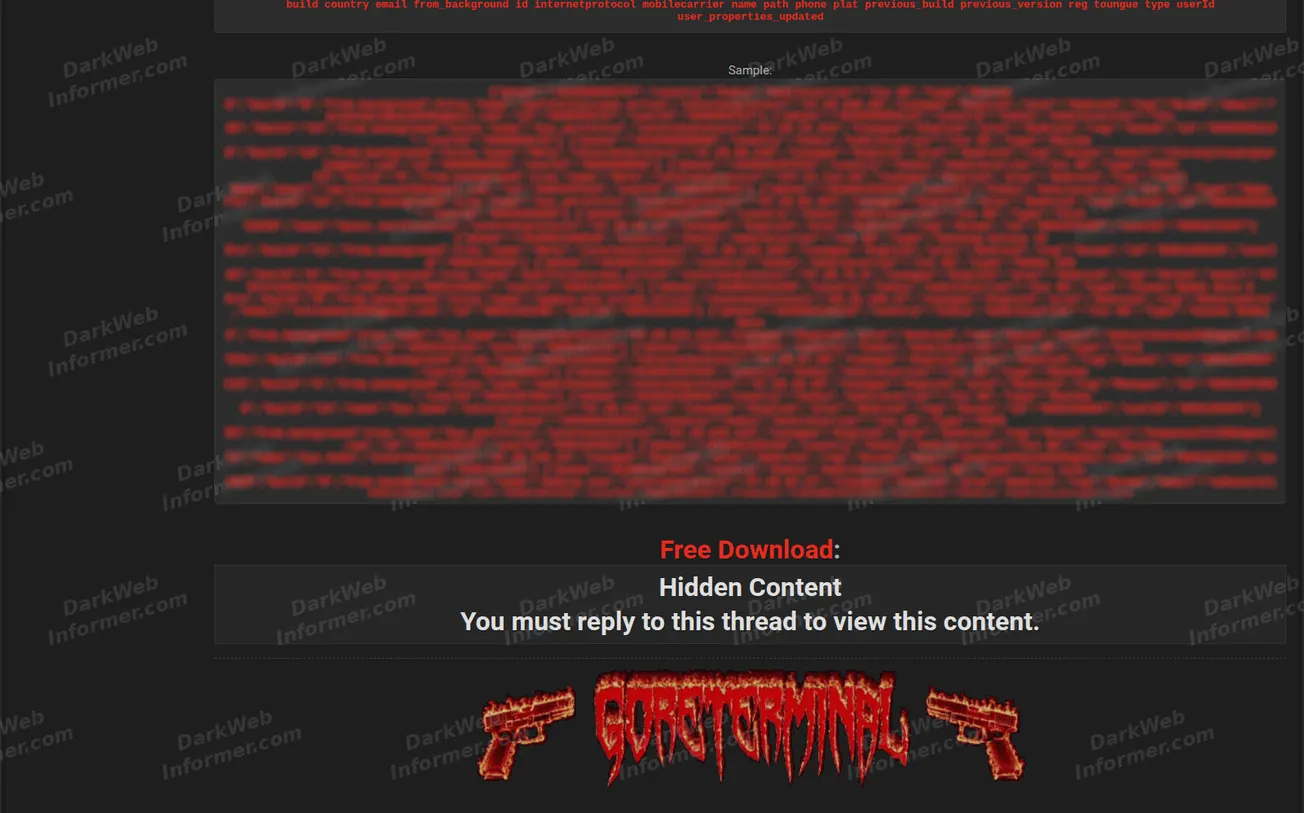
    The visible sample contains structured user-account records including contact, carrier, device and network-related metadata. Individual phone numbers, email addresses, IP addresses and user identifiers shown in the sample are not transcribed in this report.

    Screenshots

    The supplied captures show the Defy Club leak claim, the stated breach time, account, phone-number and email scope, JSONL archive sizes, schema fields, sample records and a free-download section. Direct download access and personal sample values are not reproduced here.

    IOCs & identifiers

    Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the breach claim.

    Type Identifier Source
    Actor handle GoreTerminal Screenshots 1–2
    Named organization domain defy[.]club Screenshots 1–2

    The organization domain identifies the entity named in the claim, not malicious infrastructure. No malware hash, Tox ID, Session ID, Telegram handle or attacker-controlled infrastructure is visible in the supplied screenshots. Personal identifiers shown in the sample are not included in this table.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    • Collection
      T1213.006
      Data from Information Repositories: Databases
      Inferred
      The listing presents a structured JSONL user dataset containing account, contact, carrier, device and network-related fields. The supplied material does not disclose how the data was obtained or independently establish unauthorized access to Defy Club systems.

    Potential impact

    If authentic, the claimed dataset could expose phone numbers, email addresses, IP addresses, mobile-carrier information, device/platform details and account identifiers for more than 23,000 users. The combination could support targeted phishing, SMS abuse, account impersonation, profiling or other privacy-related abuse.

    Status Unverified

    Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, approximately 23,149-account count, phone or email totals, archive sizes, sample contents or the actor’s claimed October 30 breach time. The supplied screenshots document the listing and visible sample records, not independent confirmation of the underlying data.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-30

  • Buenos Aires Student Database Leak Claim Lists 1.7 Million Enrollment Records

    Data Exposure Report
    Buenos Aires Student Database Leak Claim Lists 1.7 Million Enrollment RecordsArgentina
    Government
    Student & Education Data
    Leak Claim
    Unverified

    Buenos Aires Student Database Leak Claim Lists 1.7 Million Enrollment Records

    Claimed records1.7M
    Academic year2025
    RegionBuenos Aires
    Data typeStudent enrollment

    Buenos Aires Student Database Leak Claim Lists 1.7 Million Enrollment Records

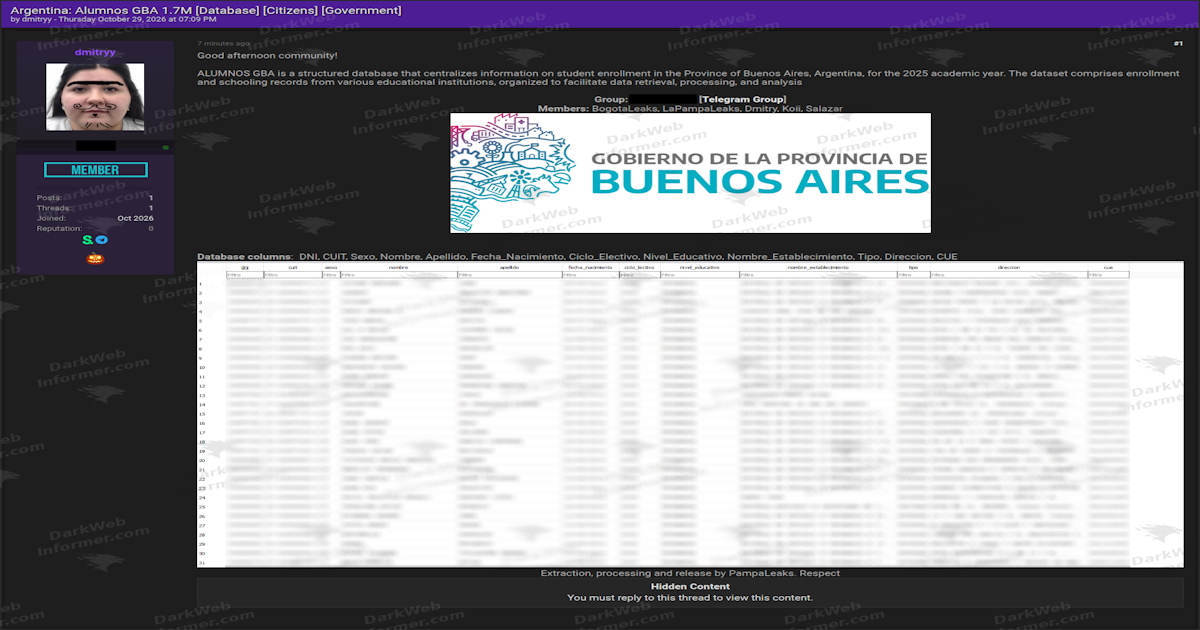
    An actor using the handle “dmitryy” claims to have released a database called ALUMNOS GBA, described as a structured dataset containing student enrollment information from the Province of Buenos Aires, Argentina, for the 2025 academic year.

    The post advertises approximately 1.7 million records and says the dataset centralizes enrollment and school records from multiple educational institutions. The visible columns include DNI, CUIT, sex, first name, last name, date of birth, academic year, education level, school name, institution type, address and CUE. The dataset, its source, the claimed volume and current availability have not been independently verified.

    Post details

    OrganizationGovernment of the Province of Buenos Aires
    CountryBuenos Aires Student Database Leak Claim Lists 1.7 Million Enrollment RecordsArgentina
    SectorGovernment / education
    Actor“dmitryy”
    Dataset nameALUMNOS GBA
    Claimed volumeApproximately 1.7 million records
    Academic year2025
    Post date shown

    What the post claims

    • Approximately 1.7 million student records
    • 2025 academic-year data
    • DNI field included
    • CUIT field included
    • Sex field included
    • First-name and last-name fields included
    • Date-of-birth field included
    • Academic-year field included
    • Education-level field included
    • School-name field included
    • Institution-type field included
    • School-address field included
    • CUE institution code included
    • Sample rows displayed

    The visible sample contains student identity information and school-enrollment details. Individual student names, DNI/CUIT values, dates of birth, school names and addresses shown in the screenshot are not transcribed in this report.

    Screenshots

    The supplied capture shows the ALUMNOS GBA claim, the Province of Buenos Aires branding, the advertised student-enrollment columns and sample rows containing identity and school information. Personal student data from the sample is not repeated here.

    IOCs & identifiers

    Identifiers directly visible in the supplied material. These support correlation and do not independently verify the dataset claim.

    Type Identifier Source
    Actor handle dmitryy Screenshot 1
    Group PampaLeaks Screenshot 1
    Named organization Gobierno de la Provincia de Buenos Aires Screenshot 1

    The screenshot references PampaLeaks as a Telegram group and lists several member handles. Those names are not expanded here because they are not necessary to describe the exposed student dataset. No malware hash, Tox ID, Session ID, attacker-controlled domain or attacker-controlled IP address is visible in the supplied material.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    • Collection
      T1213.006
      Data from Information Repositories: Databases
      Inferred
      The listing presents a structured student-enrollment database containing identity and school information. The supplied material does not disclose how the data was obtained or independently establish unauthorized access to Buenos Aires government systems.

    Potential impact

    If authentic, the claimed dataset could expose student names, national identifiers, dates of birth, sex, education level, school names and school addresses at very large scale. Because the sample visibly includes school-age students, the exposure could create heightened risks of identity fraud, targeted phishing, impersonation, harassment or other privacy-related abuse.

    Status Unverified

    Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, approximate 1.7 million-record count, sample contents or current availability. The supplied screenshot documents the listing and visible sample rows, not independent confirmation of the underlying database.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-29

  • Capiter Data Leak Claim Exposes 208,206 User Accounts and Phone Numbers

    Data Exposure Report
    Capiter Data Leak Claim Exposes 208,206 User Accounts and Phone NumbersEgypt
    B2B Commerce
    User & Phone Data
    Free Leak
    Unverified

    Capiter Data Leak Claim Exposes 208,206 User Accounts and Phone Numbers

    Claimed accounts208,206
    Phone numbers208K+
    Uncompressed size150 MB
    Compressed size34 MB

    Capiter Data Leak Claim Exposes 208,206 User Accounts and Phone Numbers

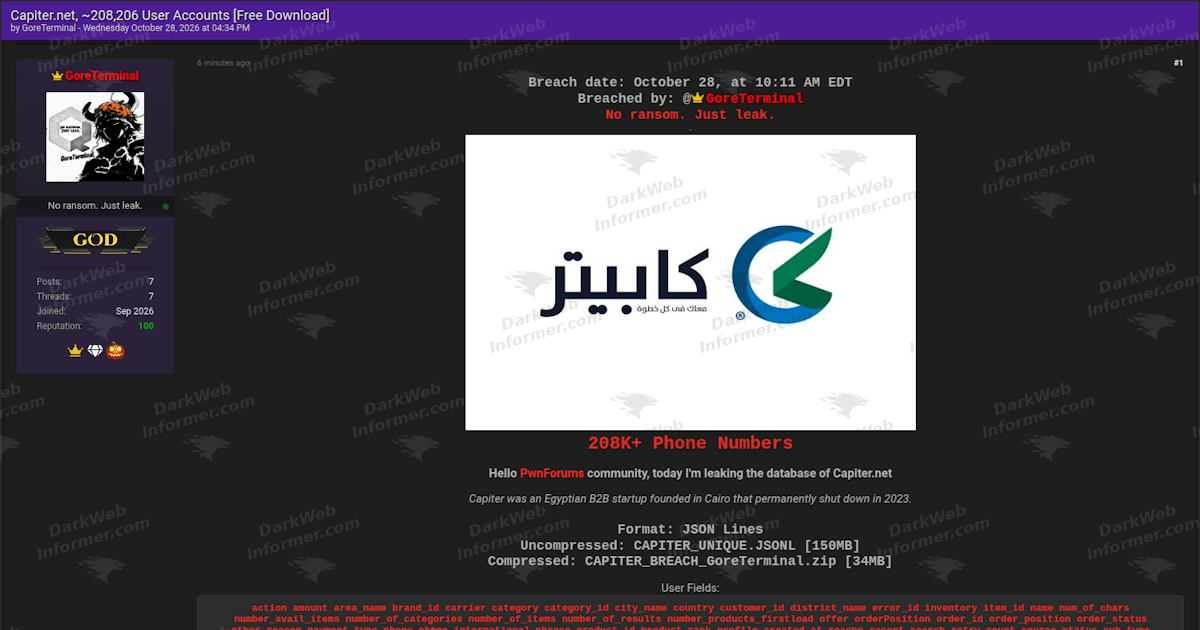
    An actor using the handle “GoreTerminal” claims to have leaked a Capiter dataset containing approximately 208,206 user accounts. The post describes Capiter as an Egyptian B2B startup founded in Cairo that permanently shut down in 2023.

    The actor states the breach occurred on October 28, 2026 at 10:11 AM EDT and characterizes the release as a leak rather than a ransom event. The archive is described as JSON Lines, with an uncompressed file named CAPITER_UNIQUE.JSONL at 150 MB and a compressed archive at 34 MB. The visible schema includes phone numbers, international phone numbers, customer IDs, country, carrier, city, district, area, order and product metadata, payment type, inventory data and profile timestamps. The dataset, its source, the stated counts and current availability have not been independently verified.

    Post details

    OrganizationCapiter
    CountryCapiter Data Leak Claim Exposes 208,206 User Accounts and Phone NumbersEgypt
    SectorB2B commerce / distribution technology
    Actor“GoreTerminal”
    Claimed accountsApproximately 208,206
    FormatJSON Lines
    Archive sizes150 MB raw / 34 MB compressed
    Claimed breach timeOct 28, 2026 at 10:11 AM EDT

    What the post claims

    • Approximately 208,206 user accounts
    • 208K+ phone numbers
    • JSON Lines format
    • 150 MB uncompressed file
    • 34 MB compressed archive
    • Phone and international-phone fields included
    • Customer IDs included
    • Country and carrier fields included
    • City, district and area fields included
    • Order IDs and order-position fields included
    • Order-status fields included
    • Product IDs, ranks and categories included
    • Inventory-related fields included
    • Payment-type fields included
    • Offer and retry-count fields included
    • Profile-created timestamps included
    • Sample records displayed
    • Free download advertised

    The sample shown in the source material contains structured customer and transaction-related records. Individual phone numbers, customer identifiers and other personal values visible in the sample are not transcribed in this report.

    Screenshots

    The supplied captures show the Capiter leak claim, the stated breach time, user-account and phone-number scope, JSONL archive sizes, schema fields, sample records and a free-download section. Direct download access is not reproduced here.

    IOCs & identifiers

    Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the breach claim.

    Type Identifier Source
    Actor handle GoreTerminal Screenshots 1–2
    Named organization Capiter Screenshots 1–2

    No organization domain, malware hash, Tox ID, Session ID, Telegram handle or attacker-controlled IP address is visible in the supplied screenshots. Personal identifiers shown in the sample are not included in this table.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    • Collection
      T1213.006
      Data from Information Repositories: Databases
      Inferred
      The listing presents a structured JSONL dataset containing customer, phone, order and product-related fields. The supplied material does not disclose how the data was obtained or independently establish unauthorized access to Capiter systems.

    Potential impact

    If authentic, the claimed dataset could expose mobile phone numbers, customer identifiers, location information and transaction-related metadata for more than 200,000 accounts. The combination could support targeted phishing, SMS abuse, impersonation, profiling or other customer-focused social engineering.

    Status Unverified

    Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, 208,206-account count, archive sizes, sample contents or the actor’s claimed October 28 breach time. The supplied screenshots document the listing and visible sample records, not independent confirmation of the underlying data.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-28

  • INBI School of English WhatsApp Data Claim Includes 3.34 Million Messages and 171,967 Phone Numbers

    Data Exposure Report
    INBI School of English WhatsApp Data Claim Includes 3.34 Million Messages and 171,967 Phone NumbersMexico
    Education
    WhatsApp Communications
    Published
    Unverified

    INBI School of English WhatsApp Data Claim Includes 3.34 Million Messages and 171,967 Phone Numbers

    Claimed messages3,337,394
    Phone numbers171,967
    CountryMexico
    Data typeWhatsApp messages

    INBI School of English WhatsApp Data Claim Includes 3.34 Million Messages and 171,967 Phone Numbers

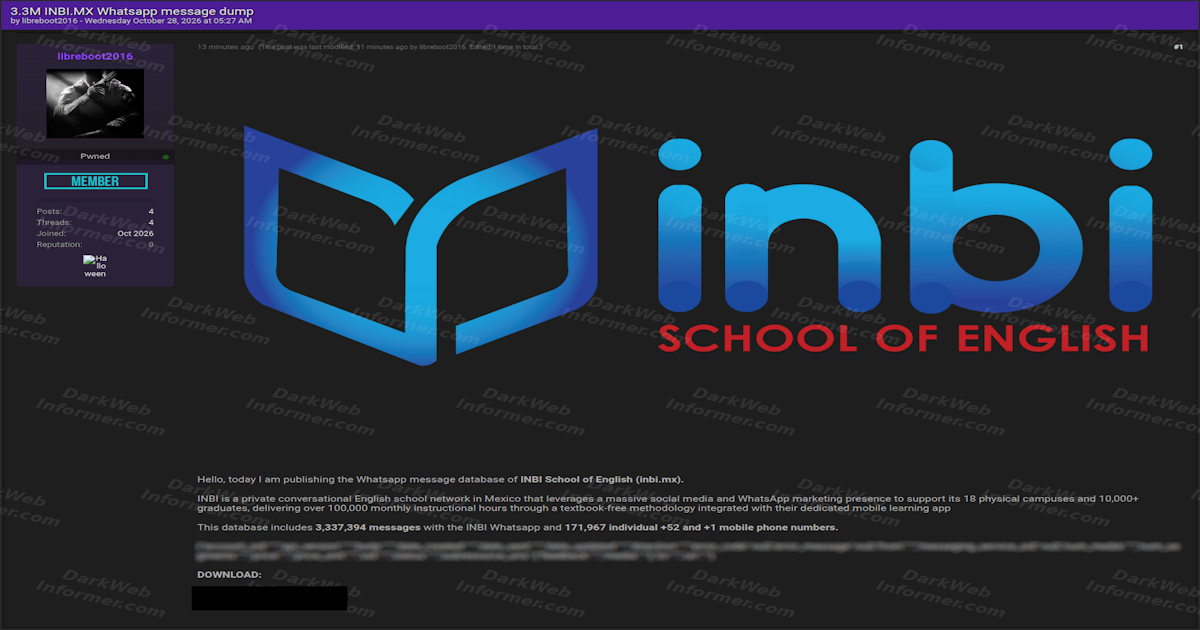
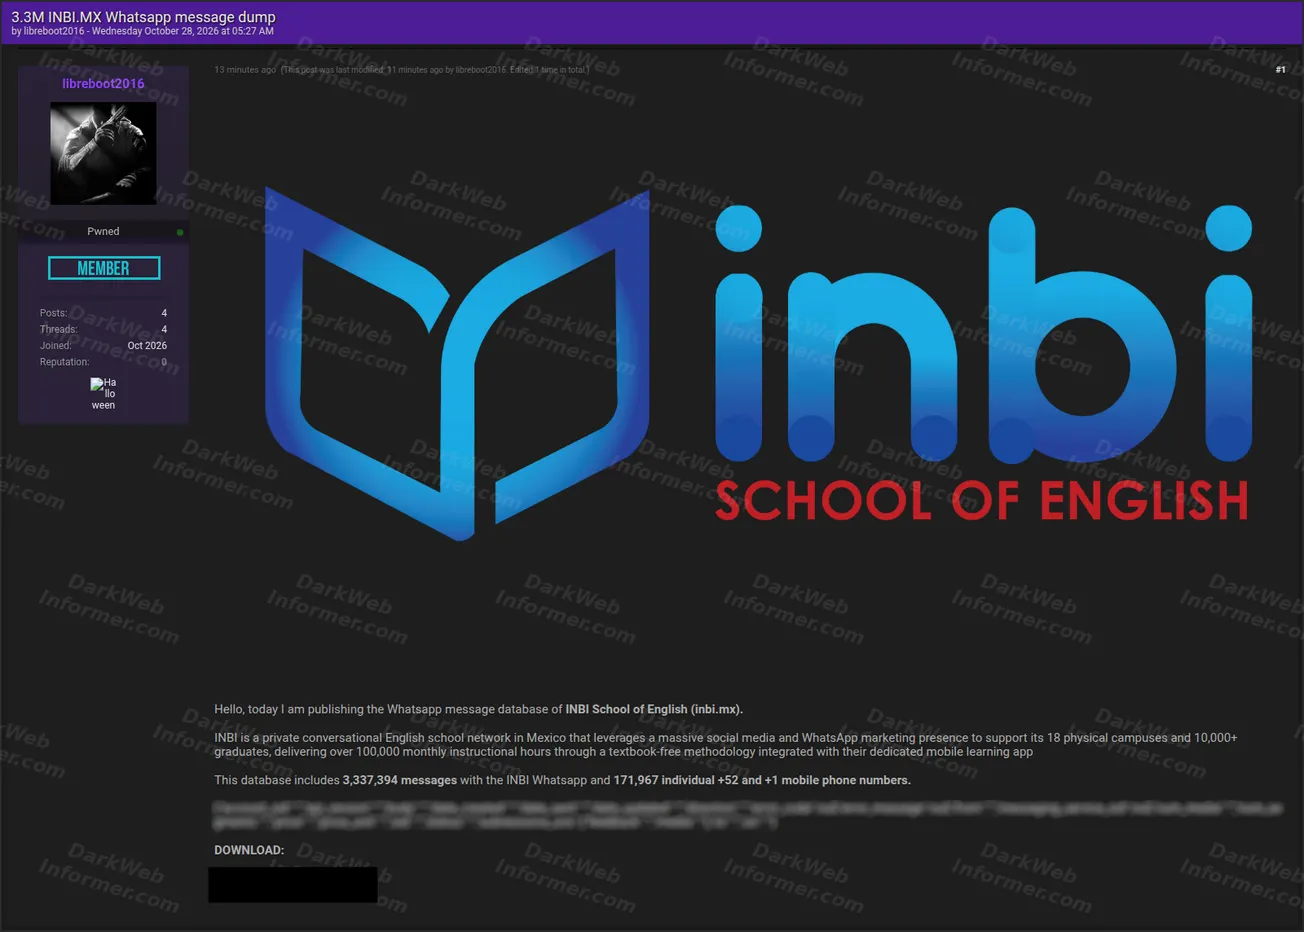
    An actor using the handle “libreboot2016” claims to have published a WhatsApp message dataset associated with INBI School of English, a private conversational English school network in Mexico.

    The post states that the dataset contains 3,337,394 WhatsApp messages and 171,967 individual mobile phone numbers using +52 and +1 country codes. A visible field list includes message body, creation and sent timestamps, direction, error fields, sender and recipient fields, messaging-service identifiers, media-related fields, pricing fields, message SID, status, feedback, media metadata and URI data. The dataset, its source, the stated counts and current availability have not been independently verified.

    Post details

    OrganizationINBI School of English
    CountryINBI School of English WhatsApp Data Claim Includes 3.34 Million Messages and 171,967 Phone NumbersMexico
    SectorPrivate education / English-language training
    Actor“libreboot2016”
    Claimed messages3,337,394
    Claimed phone numbers171,967
    Number ranges named+52 and +1
    Post date shown

    What the post claims

    • 3,337,394 WhatsApp messages
    • 171,967 individual mobile phone numbers
    • +52 and +1 number ranges represented
    • Message-body field included
    • Creation, sent and update timestamps included
    • Message-direction field included
    • Error-code and error-message fields included
    • Sender and recipient fields included
    • Messaging-service identifier included
    • Media-count and media metadata fields included
    • Segment-count field included
    • Pricing and price-unit fields included
    • Message SID field included
    • Status field included
    • Feedback and subresource-URI fields included
    • Download mirrors provided

    The visible field list resembles structured messaging-platform export data rather than a simple contact list. The screenshot does not show individual message contents, so the sensitivity and subject matter of the communications cannot be independently assessed from the supplied material alone.

    Screenshots

    The supplied capture shows the INBI School of English claim, the stated WhatsApp message and phone-number counts, a structured message-field list and direct download mirrors. Those download links are not reproduced here.

    IOCs & identifiers

    Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the dataset claim.

    Type Identifier Source
    Actor handle libreboot2016 Screenshot 1
    Named organization domain inbi[.]mx Screenshot 1

    The organization domain identifies the entity named in the claim, not malicious infrastructure. No Tox ID, Session ID, Telegram handle, malware hash or attacker-controlled IP address is visible in the supplied screenshot. Direct download mirrors shown in the source material are intentionally not reproduced here.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    • Collection
      T1213.006
      Data from Information Repositories: Databases
      Inferred
      The listing presents a structured message dataset containing communications metadata and phone-number information. The supplied material does not reveal how the data was obtained or independently establish unauthorized access to INBI systems.

    Potential impact

    If authentic, the claimed dataset could expose large-scale messaging metadata, mobile phone numbers and potentially the content of communications involving students, prospects, graduates or staff. Depending on the underlying message bodies, the material could enable targeted phishing, impersonation, spam, social engineering or significant privacy violations.

    Status Unverified

    Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, 3,337,394-message count, 171,967-number count or current availability. The supplied screenshot documents the listing and visible field structure, not independent confirmation of the underlying data.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-28

  • LOOF Data Sale Claim Includes 654K Records and 90,555 Documents in 48 GB Archive

    Data Exposure Report
    LOOF Data Sale Claim Includes 654K Records and 90,555 Documents in 48 GB ArchiveFrance
    Animal Registry
    Customer & Pedigree Data
    For Sale
    Unverified

    LOOF Data Sale Claim Includes 654K Records and 90,555 Documents in 48 GB Archive

    Claimed lines~654K
    Animals~330K
    People~40K
    Compressed size48 GB

    LOOF Data Sale Claim Includes 654K Records and 90,555 Documents in 48 GB Archive

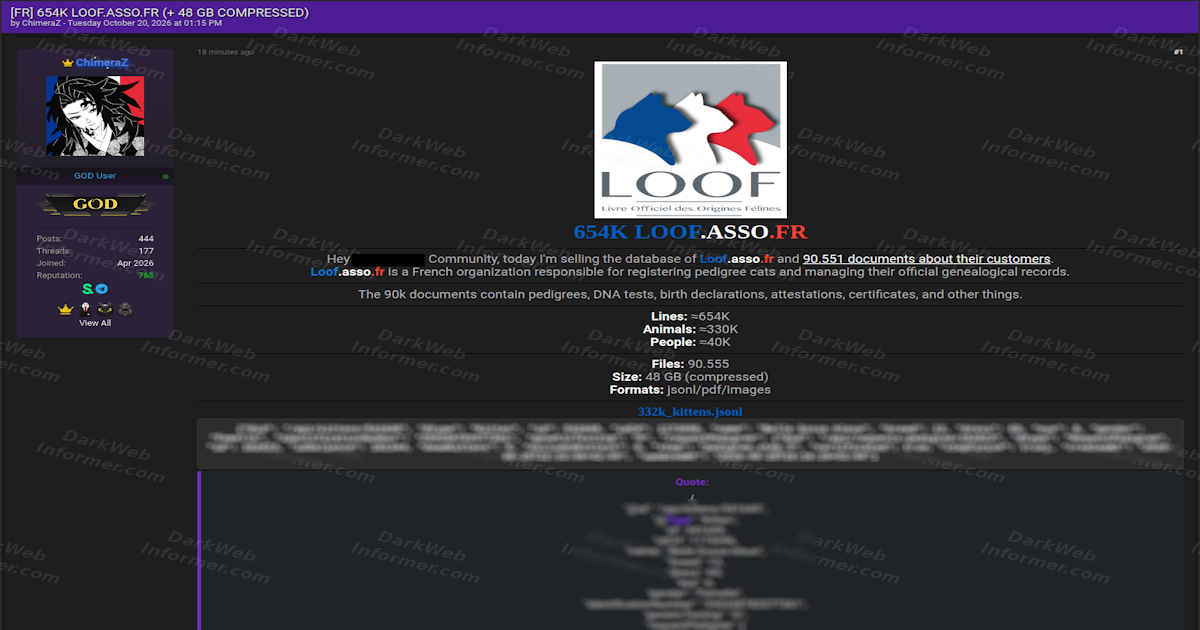
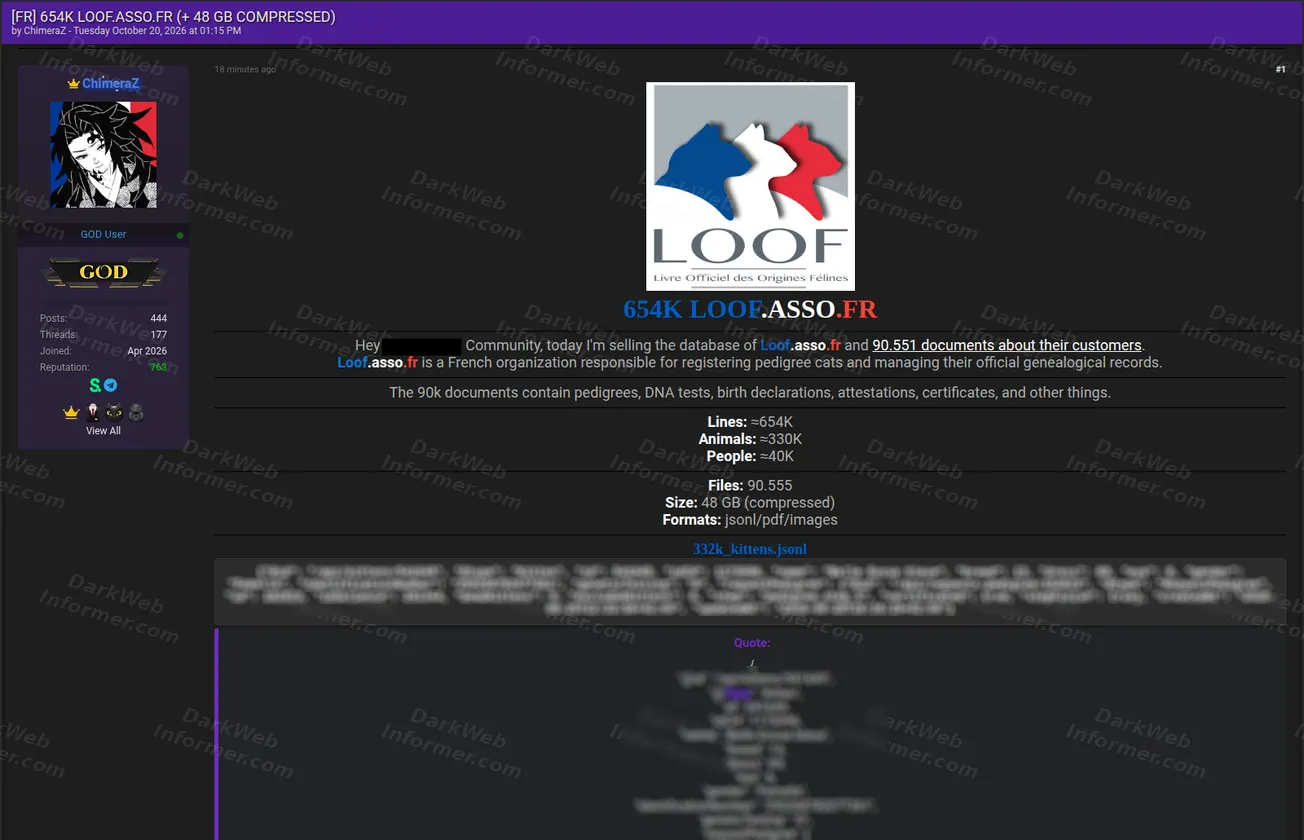
    An actor using the handle “ChimeraZ” claims to be selling a LOOF dataset. LOOF, the Livre Officiel des Origines Félines, is described in the listing as the French organization responsible for registering pedigree cats and maintaining official feline genealogical records.

    The post advertises approximately 654,000 lines, around 330,000 animal records, roughly 40,000 people and 90,555 files totaling 48 GB compressed. The stated formats are JSONL, PDF and images. The actor says the document collection includes pedigrees, DNA tests, birth declarations, attestations, certificates and other customer-related material. The dataset, its source, the stated counts and current availability have not been independently verified.

    Post details

    OrganizationLOOF
    CountryLOOF Data Sale Claim Includes 654K Records and 90,555 Documents in 48 GB ArchiveFrance
    SectorPedigree cat registry / animal identification
    Actor“ChimeraZ”
    Claimed linesApproximately 654,000
    Claimed animalsApproximately 330,000
    Claimed peopleApproximately 40,000
    Post date shown

    What the post claims

    • Approximately 654,000 lines
    • Approximately 330,000 animal records
    • Approximately 40,000 people
    • 90,555 files listed
    • 48 GB compressed size
    • JSONL, PDF and image formats
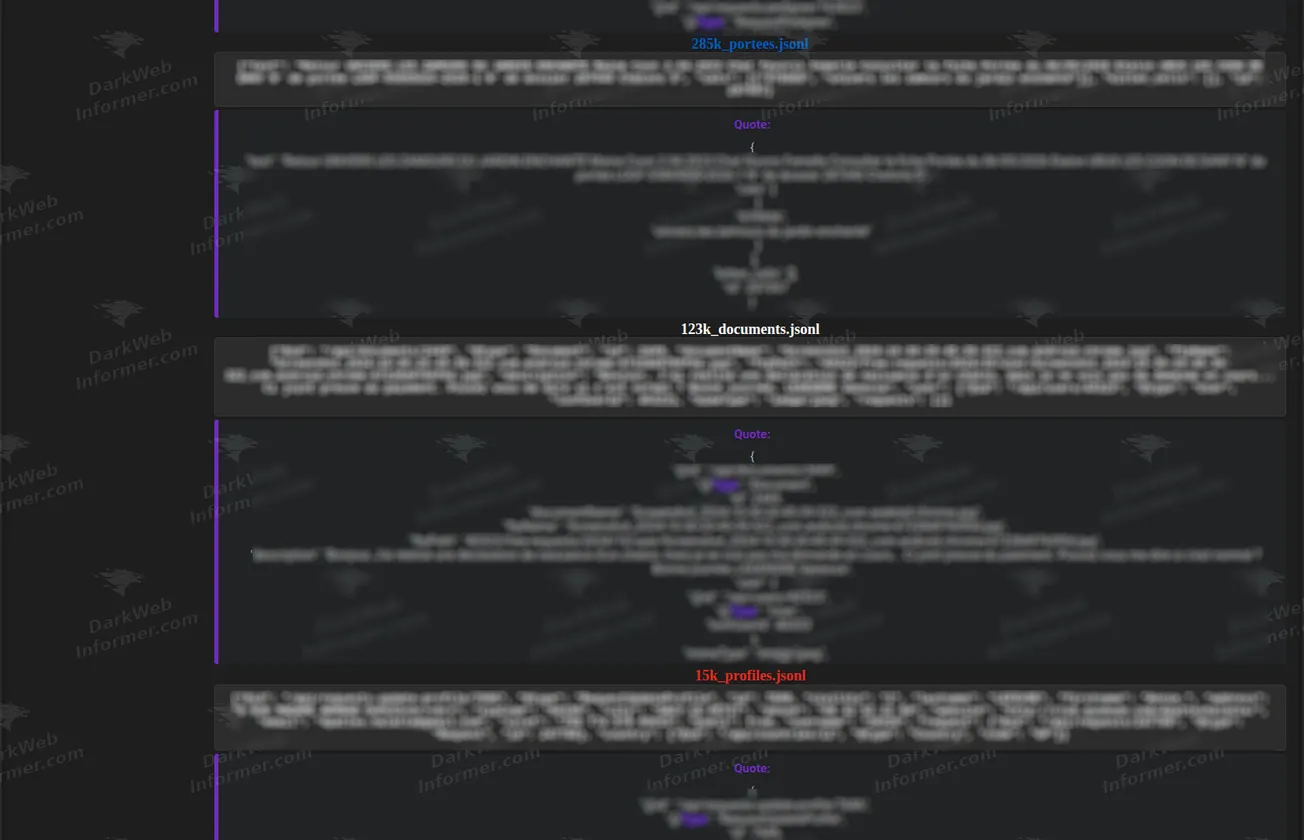
    • 332K kittens JSONL dataset
    • 285K litter / portée JSONL dataset
    • 123K documents JSONL dataset
    • 15K profile JSONL dataset
    • 22K user JSONL dataset
    • Animal chip and identification fields
    • Pedigree-request and genetic-testing fields
    • Birth and breed information
    • Customer names, addresses, phone numbers and emails
    • Business / SIRET fields visible in profile records
    • Pedigrees, DNA tests and birth declarations claimed
    • Attestations and certificates claimed
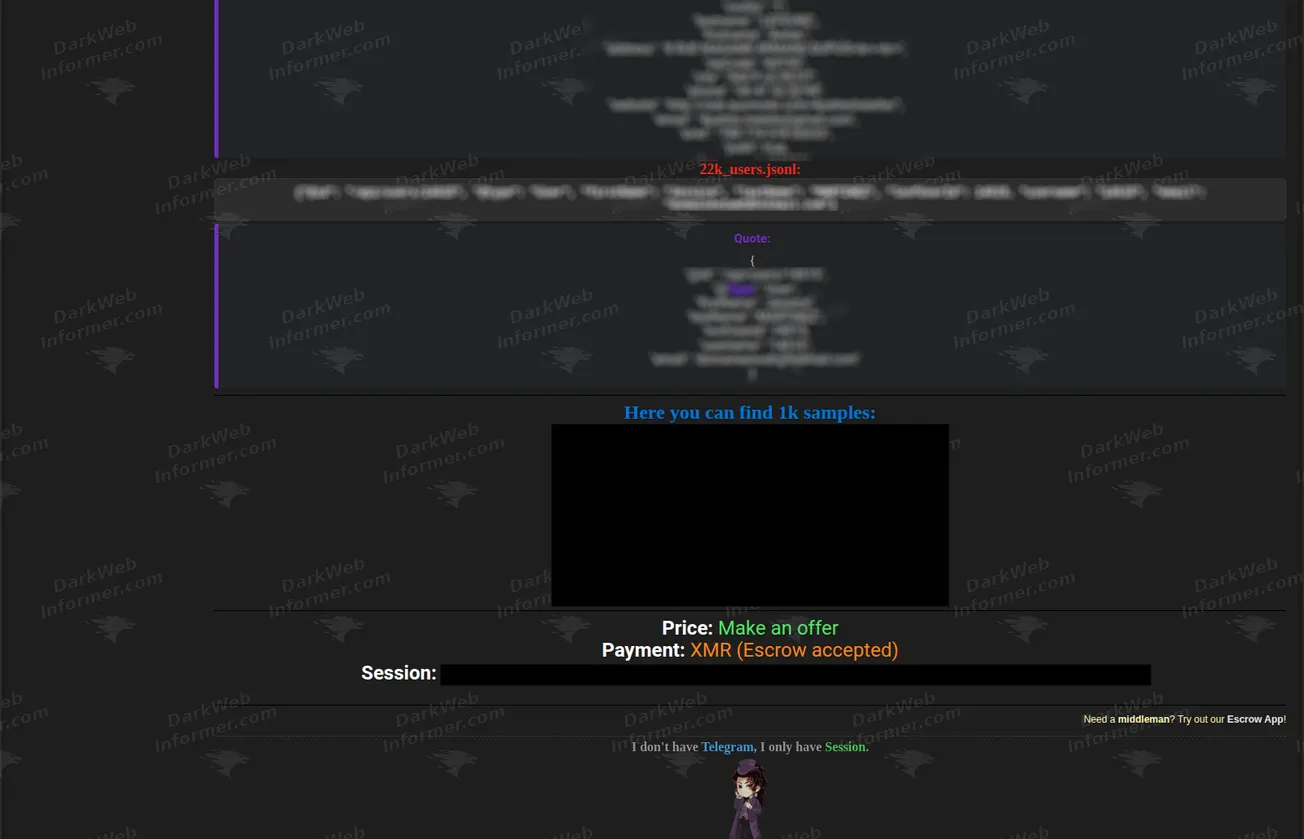
    • 1,000 samples advertised
    • Price listed as make offer
    • XMR payment requested; escrow accepted

    The introductory text says there are 90,551 documents, while the structured summary lists 90,555 files. This report preserves the structured file count and notes the discrepancy rather than reconciling it. Personal values shown in the visible samples are not transcribed here.

    Screenshots

    The supplied captures show the LOOF sale claim, stated volumes and formats, kitten, litter, document, profile and user samples, sample mirrors, pricing terms and a Session contact identifier. Direct sample-download links and personal sample values are not reproduced here.

    IOCs & identifiers

    Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the dataset claim.

    Type Identifier Source
    Actor handle ChimeraZ Screenshots 1–3
    Session ID 05c1396ee8a9d6df7ae4497a07f2fbc75b31344f5e0cbd91dacde4c04c88c4c254 Screenshot 3
    Named organization domain loof[.]asso[.]fr Screenshot 1

    The organization domain identifies the entity named in the claim, not malicious infrastructure. No Tox ID, Telegram handle, malware hash or attacker-controlled IP address is visible. Direct sample-download mirrors shown in the source material are intentionally not reproduced here.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    • CollectionT1213.006Data from Information Repositories: DatabasesInferredThe listing presents multiple structured JSONL datasets covering animals, litters, documents, profiles and users. The supplied material does not reveal how the data was obtained or independently establish unauthorized access to LOOF systems.

    Potential impact

    If authentic, the claimed exposure could reveal animal identification and pedigree information, customer names, addresses, phone numbers, email addresses, business identifiers and attached documents. The combination could support targeted phishing, impersonation, fraud involving pedigree or registry records, and broader privacy abuse affecting breeders, owners and other users.

    Status Unverified

    Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, approximate 654,000-line count, animal or people totals, 48 GB compressed size, document count, sample contents or current availability. The supplied screenshots document the listing and visible samples, not independent confirmation of the underlying material.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-20

  • Possible new Cellebrite iPhone Radio Zero-Day

    Justin.sh is reporting on a confidential Cellebrite document that has been leaked to him:

    Cellebrite calls it Advanced Unlocks (AU from here on), not to be confused with the “advanced unlocking services” they’ve marketed for years. A press release from earlier this year confirms AU is a new product for 2026.

    […]

    According to Cellebrite, AU:

    • is a “next-generation AFU vector that is more resilient to Apple’s OS changes”
    • works with Stolen Device Protection enabled, which tightens USB restrictions
    • is enabled by a dedicated appliance with a stated range (!) of about 8 meters.

    AU = Advanced Unlocks, Cellebrite’s term. AFU = after first unlock.

    Source: Schneier on Security · 2026-10-20

  • ISEP France User Database Leak Claim Lists 5,088 People Across 5,091 JSON Records

    Data Exposure Report
    ISEP France User Database Leak Claim Lists 5,088 People Across 5,091 JSON RecordsFrance
    Higher Education
    Student & User Data
    Leak Claim
    Unverified

    ISEP France User Database Leak Claim Lists 5,088 People Across 5,091 JSON Records

    Claimed lines5,091
    Claimed people5,088
    Claimed size720 KB
    FormatJSON

    ISEP France User Database Leak Claim Lists 5,088 People Across 5,091 JSON Records

    An actor using the handle “ChimeraZ” claims to have leaked a user dataset associated with ISEP, a French engineering school specializing in digital technology, computer science, electronics and cybersecurity.

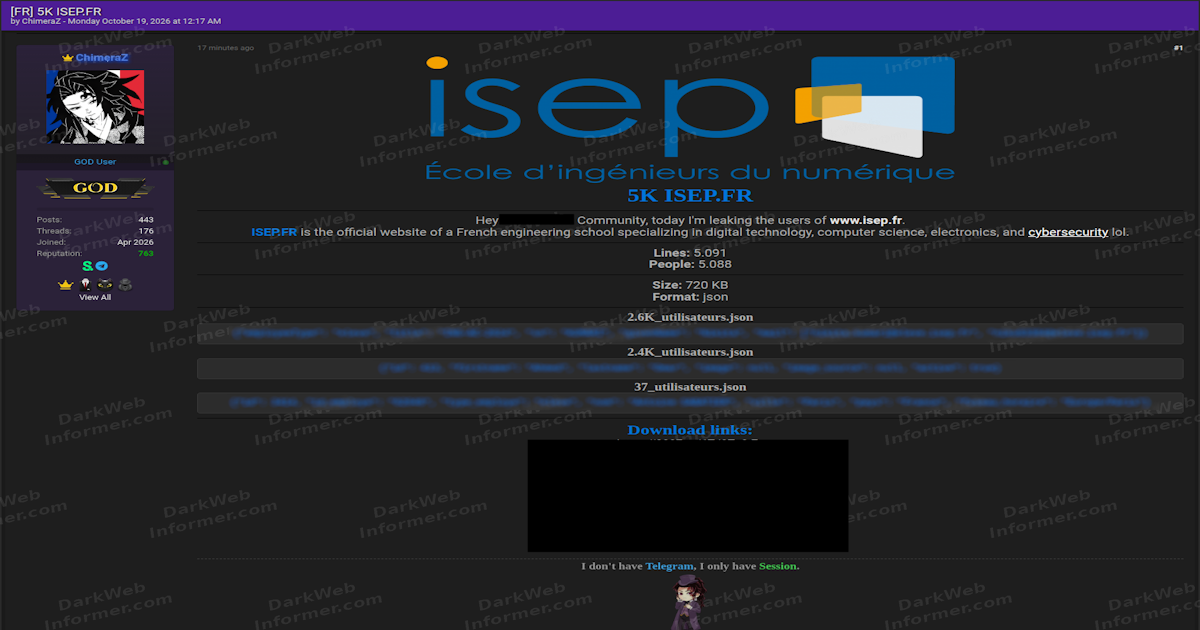
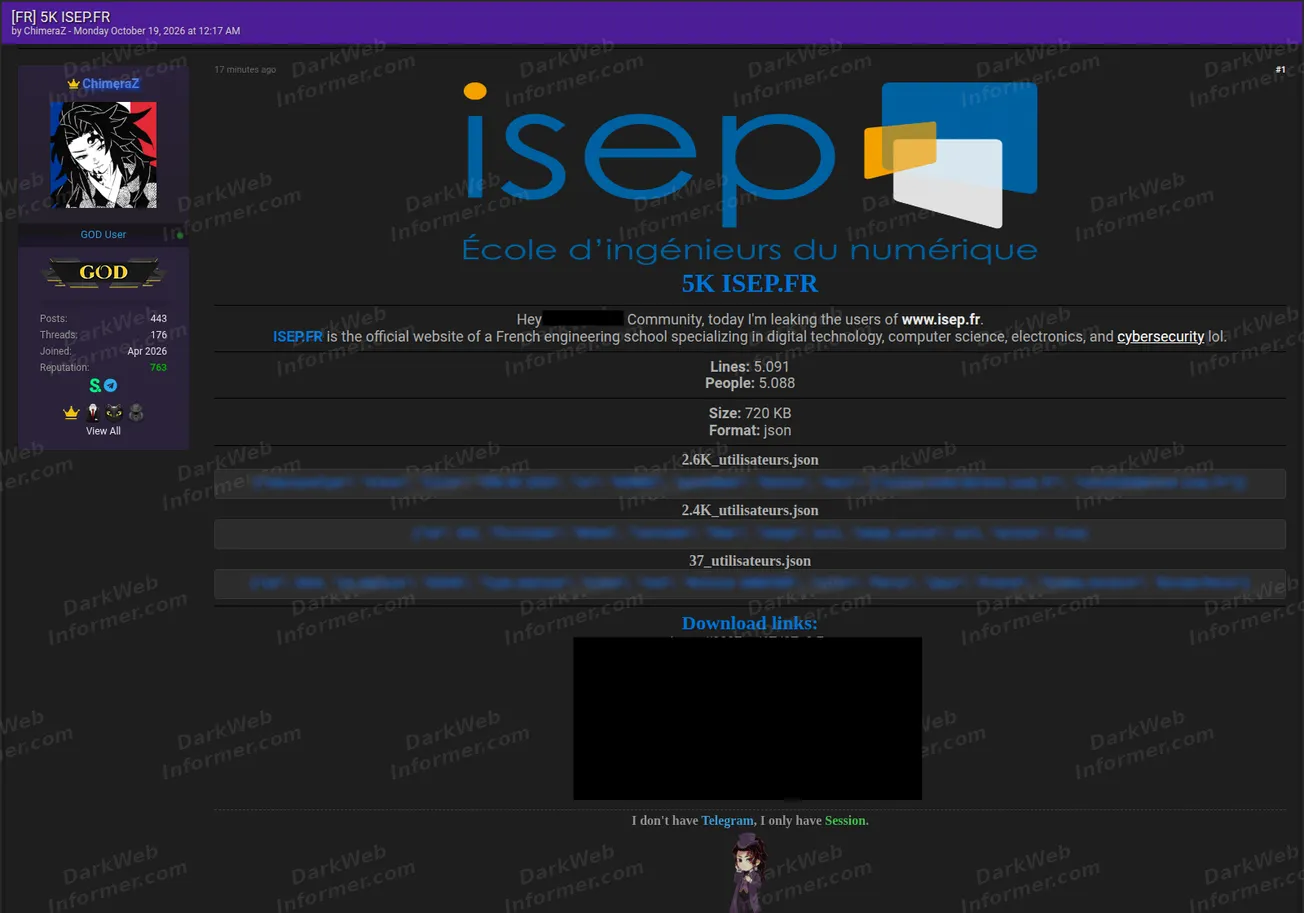
    The listing advertises 5,091 lines representing 5,088 people in a 720 KB JSON dataset. Three files are referenced, containing user and employee-related records with fields such as names, employee or student types, institutional email addresses, internal identifiers, city, country, activity status and timezone information. The dataset, its source, the stated counts and current availability have not been independently verified.

    Post details

    OrganizationISEP
    CountryISEP France User Database Leak Claim Lists 5,088 People Across 5,091 JSON RecordsFrance
    SectorHigher education / engineering
    Actor“ChimeraZ”
    Claimed lines5,091
    Claimed people5,088
    Format / sizeJSON / 720 KB
    Post date shown

    What the post claims

    • 5,091 lines advertised
    • 5,088 people advertised
    • 720 KB total size
    • JSON format
    • 2.6K_utilisateurs.json referenced
    • 2.4K_utilisateurs.json referenced
    • 37_utilisateurs.json referenced
    • Employee or student-type fields included
    • Names included
    • Institutional email addresses included
    • Internal identifiers included
    • City and country fields included
    • Activity-status fields included
    • Timezone information included
    • Multiple download mirrors provided

    The visible samples show student or employee profile records from the three referenced JSON files. Personal names, email addresses and internal identifiers shown in the samples are not transcribed in this report.

    Screenshots

    The supplied capture shows the ISEP claim, the stated line and person counts, JSON format and file size, three referenced user files, sample records and multiple download mirrors. Direct download links and personal sample values are not reproduced here.

    IOCs & identifiers

    Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the dataset claim.

    Type Identifier Source
    Actor handle ChimeraZ Screenshot 1
    Named organization domain isep[.]fr Screenshot 1

    The domain identifies the organization named in the claim, not malicious infrastructure. The source screenshot states that the actor uses Session rather than Telegram, but no Session ID is visible in the supplied capture. No malware hash, Tox ID or attacker-controlled IP address is visible. Direct download mirrors shown in the source material are intentionally not reproduced here.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    • Collection
      T1213.006
      Data from Information Repositories: Databases
      Inferred
      The listing presents structured user datasets containing student or employee identity and contact information. The supplied material does not reveal how the data was obtained or independently establish unauthorized access to ISEP systems.

    Potential impact

    If authentic, the claimed dataset could expose student or employee names, institutional email addresses, internal identifiers, location information and account-status metadata. The combination could support targeted phishing, impersonation or other social-engineering activity involving ISEP users.

    Status Unverified

    Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, 5,091-line count, 5,088-person count, sample contents or current availability. The supplied screenshot documents the listing and visible sample records, not independent confirmation of the underlying data.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-19

  • Cast AI Data Leak Claim Includes AWS, GCP and GitLab Backups Across 20 GB Archive

    Data Exposure Report
    Cloud Infrastructure
    Source Code & Backups
    20 GB Download Claim
    Unverified

    Cast AI Data Leak Claim Includes AWS, GCP and GitLab Backups Across 20 GB Archive

    Claimed size20 GB
    Cloud platformsAWS + GCP
    Code platformGitLab
    Unlock cost1 point

    Cast AI Data Leak Claim Includes AWS, GCP and GitLab Backups Across 20 GB Archive

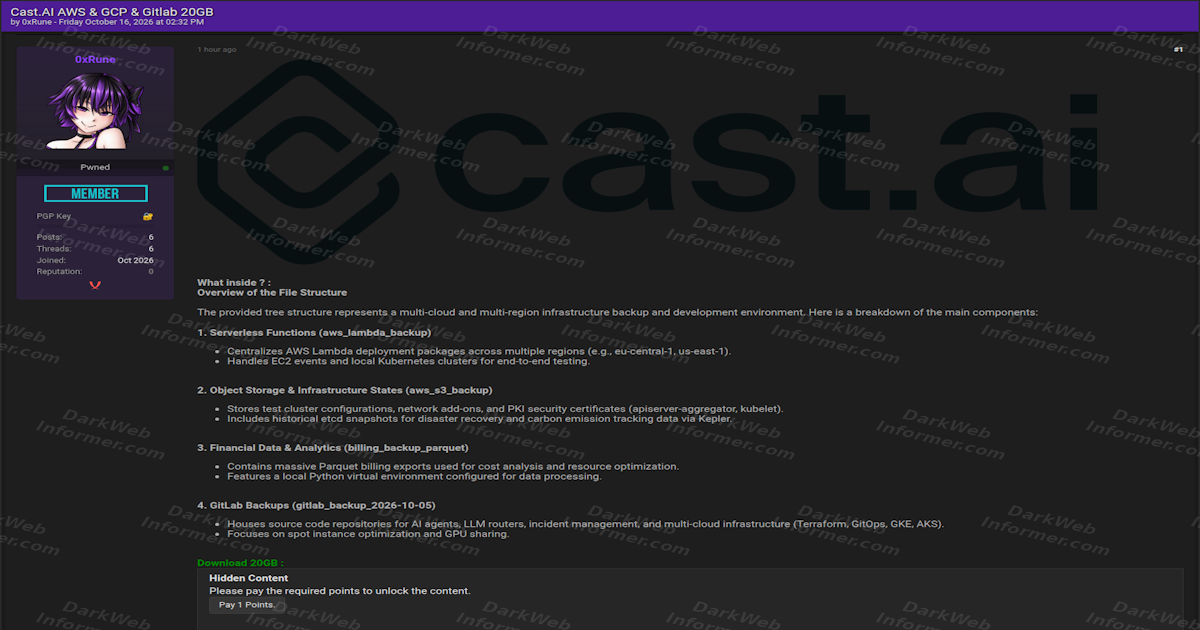
    An actor using the handle “0xRune” claims to have uploaded approximately 20 GB of Cast AI data. The listing describes the material as a multi-cloud and multi-region infrastructure backup and development environment containing AWS, GCP and GitLab-related data.

    The post specifically references AWS Lambda deployment packages, S3 backups, infrastructure-state data, billing exports and a GitLab backup dated October 5, 2026. It also says the GitLab material contains source code for AI agents, LLM routers, incident-management tooling and multi-cloud infrastructure including Terraform, GitOps, GKE and AKS-related content. The archive, its source, the stated 20 GB size and the claimed contents have not been independently verified.

    Post details

    OrganizationCast AI
    SectorCloud infrastructure / Kubernetes optimization
    Actor“0xRune”
    Claimed size20 GB
    Cloud platforms namedAWS, GCP
    Code platform namedGitLab
    Unlock access1 point required
    Post date shown

    What the post claims

    • 20 GB archive advertised
    • AWS Lambda backup material
    • Deployment packages across multiple AWS regions
    • EC2 event handling references
    • Local Kubernetes test-cluster material
    • AWS S3 backup content
    • Infrastructure-state and test-cluster configurations
    • Network add-on configuration
    • PKI security certificate material
    • Historical etcd snapshots
    • Billing exports in Parquet format
    • GitLab backup dated October 5, 2026
    • Source code for AI agents
    • LLM router code
    • Incident-management tooling
    • Terraform and GitOps content
    • GKE and AKS-related infrastructure code
    • Spot-instance and GPU-sharing optimization code

    The listing describes a mixed infrastructure and development-data collection rather than a single database. No underlying files, credentials, secrets or source-code contents are visible in the supplied screenshot.

    Screenshots

    The supplied capture shows the Cast AI claim and a high-level breakdown of the allegedly included AWS Lambda, S3, billing, GitLab and multi-cloud development material. The hidden download requires 1 point.

    IOCs & identifiers

    Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the data claim.

    Type Identifier Source
    Actor handle 0xRune Screenshot 1
    Named organization domain cast[.]ai Screenshot 1

    The domain identifies the organization named in the claim, not malicious infrastructure. No malware hash, Tox ID, Session ID, Telegram handle or attacker-controlled IP address is visible in the supplied material.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    Potential impact

    If authentic, the claimed archive could expose source code, infrastructure configuration, deployment packages, PKI-related material, historical cluster state, billing data and multi-cloud operational details. Depending on the underlying files, that could create risks involving source-code disclosure, credential or secret exposure, infrastructure mapping, supply-chain abuse or follow-on compromise.

    Status Unverified

    Dark Web Informer has not independently verified the archive’s authenticity, source, 20 GB size, backup dates, file structure or current availability. The supplied screenshot documents the listing and the actor’s summary of the archive, not independent confirmation of the underlying files.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-16

  • APICRYPT Dataset Leak Claim Lists 852,757 Records Across 60,911 Healthcare Users

    Data Exposure Report
    APICRYPT Dataset Leak Claim Lists 852,757 Records Across 60,911 Healthcare UsersFrance
    Healthcare Messaging
    Professional & Contact Data
    Download Listing
    Unverified

    APICRYPT Dataset Leak Claim Lists 852,757 Records Across 60,911 Healthcare Users

    Claimed rows852,757
    Claimed users60,911
    Breach year2026
    Unlock cost5 points

    APICRYPT Dataset Leak Claim Lists 852,757 Records Across 60,911 Healthcare Users

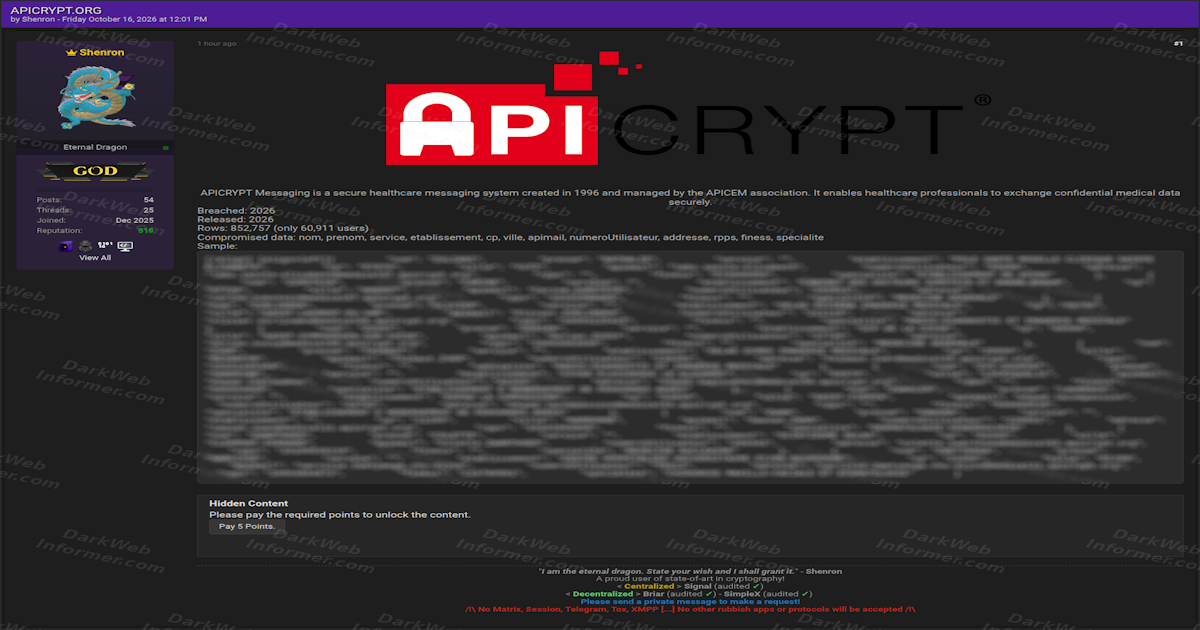
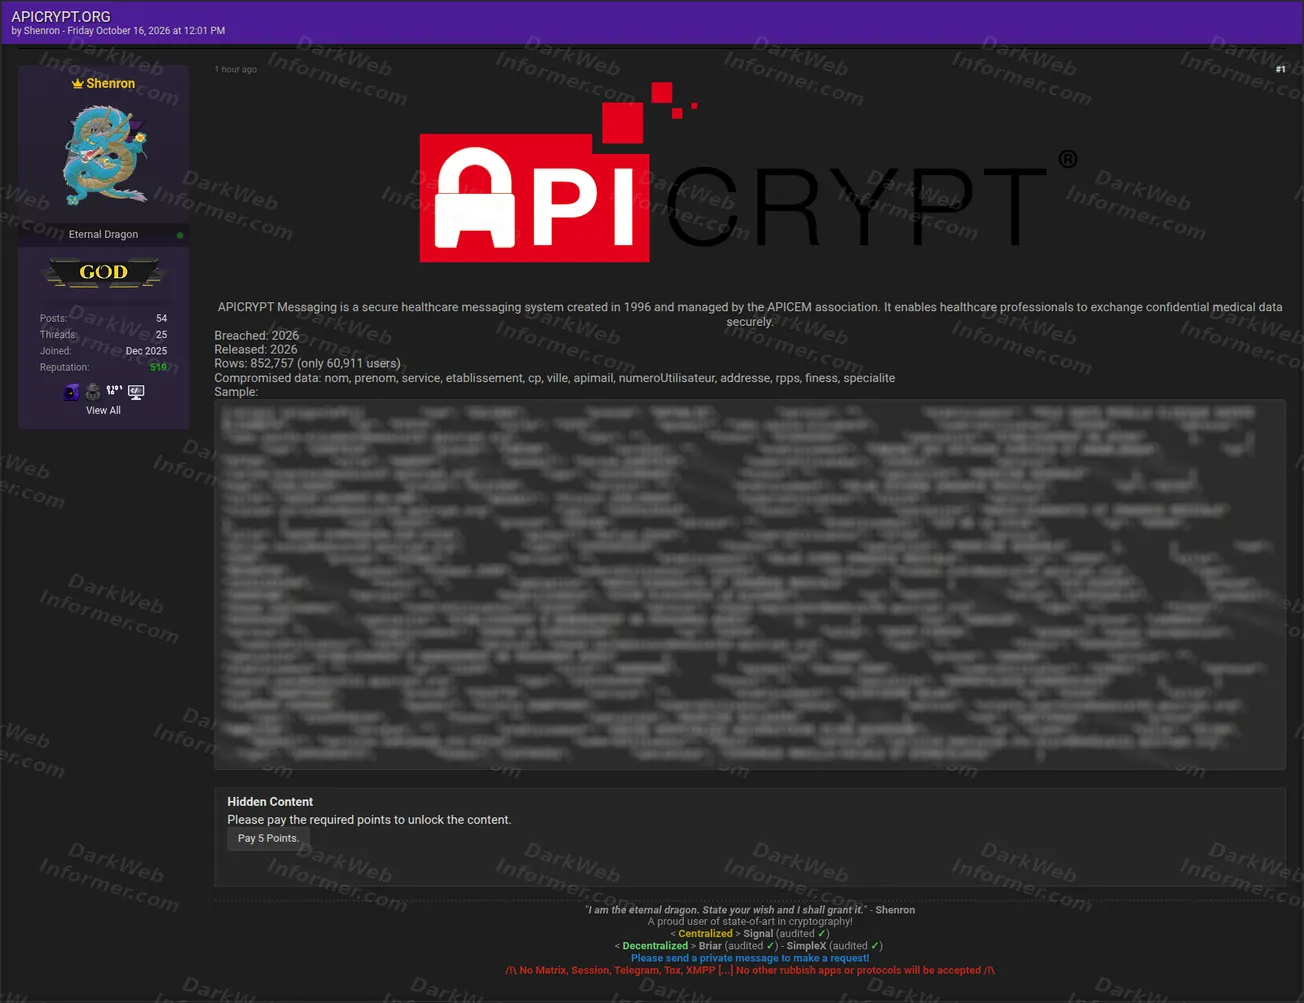
    An actor using the handle “Shenron” claims to have released a dataset associated with APICRYPT Messaging, a secure healthcare messaging system created in 1996 and managed by the APICEM association.

    The listing advertises 852,757 rows tied to 60,911 users. The visible field list includes surnames, given names, services, healthcare establishments, postal codes, cities, APICRYPT email addresses, user numbers, street addresses, RPPS identifiers, FINESS identifiers and specialties. The post marks the breach and release as occurring in 2026. The dataset, its source, the stated counts and current availability have not been independently verified.

    Post details

    OrganizationAPICRYPT / APICEM
    CountryAPICRYPT Dataset Leak Claim Lists 852,757 Records Across 60,911 Healthcare UsersFrance
    SectorHealthcare secure messaging
    Actor“Shenron”
    Claimed rows852,757
    Claimed users60,911
    Breach / release year2026
    Post date shown

    What the post claims

    • 852,757 rows advertised
    • 60,911 users advertised
    • Breach dated to 2026
    • Release dated to 2026
    • Surname field listed
    • Given-name field listed
    • Service field listed
    • Healthcare-establishment field listed
    • Postal-code and city fields listed
    • APICRYPT email-address field listed
    • User-number field listed
    • Street-address field listed
    • RPPS identifier field listed
    • FINESS identifier field listed
    • Medical-specialty field listed
    • Sample records displayed
    • Hidden download requires 5 points

    The visible sample contains healthcare-professional directory and contact information. Individual names, email addresses, RPPS numbers, FINESS identifiers and physical addresses shown in the sample are not transcribed in this report.

    Screenshots

    The supplied capture shows the APICRYPT claim, the stated 852,757-row and 60,911-user figures, the listed professional and contact-data fields, sample records and a hidden download area requiring 5 points.

    IOCs & identifiers

    Identifiers directly visible or supported by the supplied material. These support correlation and do not independently verify the dataset claim.

    Type Identifier Source
    Actor handle Shenron Screenshot 1
    Named organization domain apicrypt[.]org Screenshot 1

    The domain identifies the organization named in the claim, not malicious infrastructure. The actor’s footer explicitly states that Matrix, Session, Telegram, Tox and XMPP are not used. No malware hash, attacker-controlled domain or attacker-controlled IP address is visible in the supplied material. Personal and professional identifiers shown in the sample are not included in this table.

    Mapped techniques

    Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.

    • Collection
      T1213.006
      Data from Information Repositories: Databases
      Inferred
      The listing presents a structured dataset containing healthcare-professional identity, contact, organizational and professional-registration fields. The supplied material does not disclose how the data was obtained or independently establish unauthorized access to APICRYPT systems.

    Potential impact

    If authentic, the claimed dataset could expose healthcare-professional names, APICRYPT email addresses, physical addresses, RPPS identifiers, FINESS identifiers, specialties and workplace information. The combination could support targeted phishing, impersonation, credential-harvesting attempts or profiling of healthcare professionals and facilities.

    Status Unverified

    Dark Web Informer has not independently verified the dataset’s authenticity, source, completeness, 852,757-row count, 60,911-user count, sample contents or current availability. The supplied screenshot documents the listing and visible sample records, not independent confirmation of the underlying dataset.

    Dark Web Informer

    Source: Dark Web Informer · 2026-10-16