South Africa
 United States
 India
ERP Systems
Multiple Accesses
Unverified
Multiple ERP Access Claims Span 13 Organizations Across Nine Countries After Alleged 0-Day Exploitation
Overview
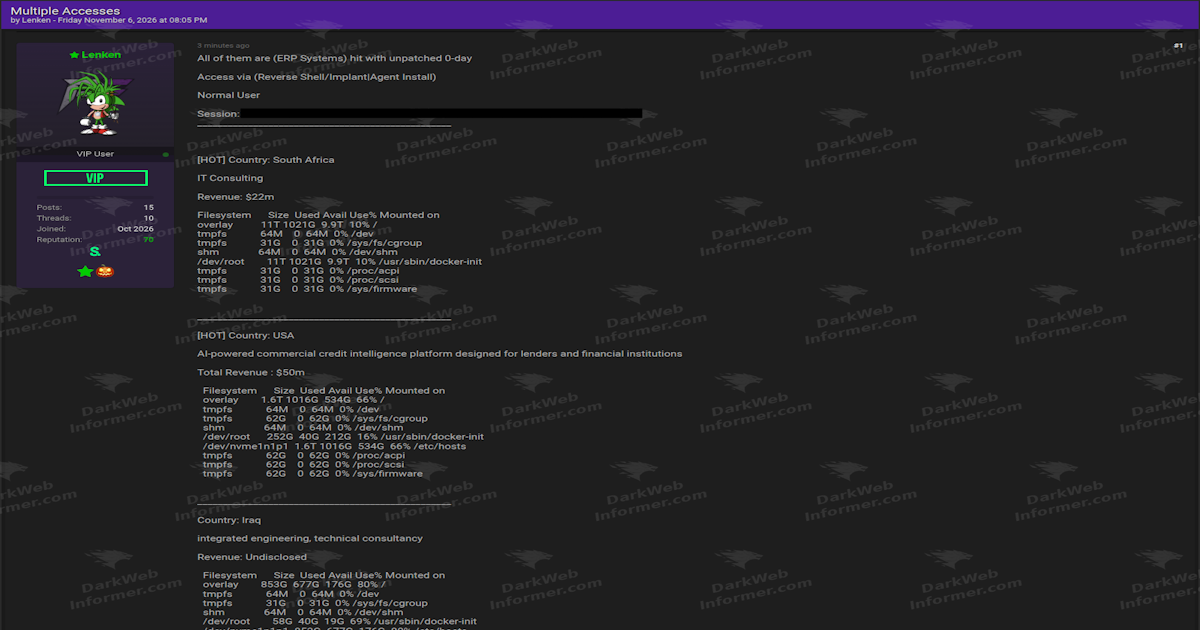
An actor using the handle “Lenken” claims to have access to multiple ERP environments across organizations in South Africa, the United States, Iraq, India, Austria, Saudi Arabia, the United Arab Emirates, Egypt and Tanzania.
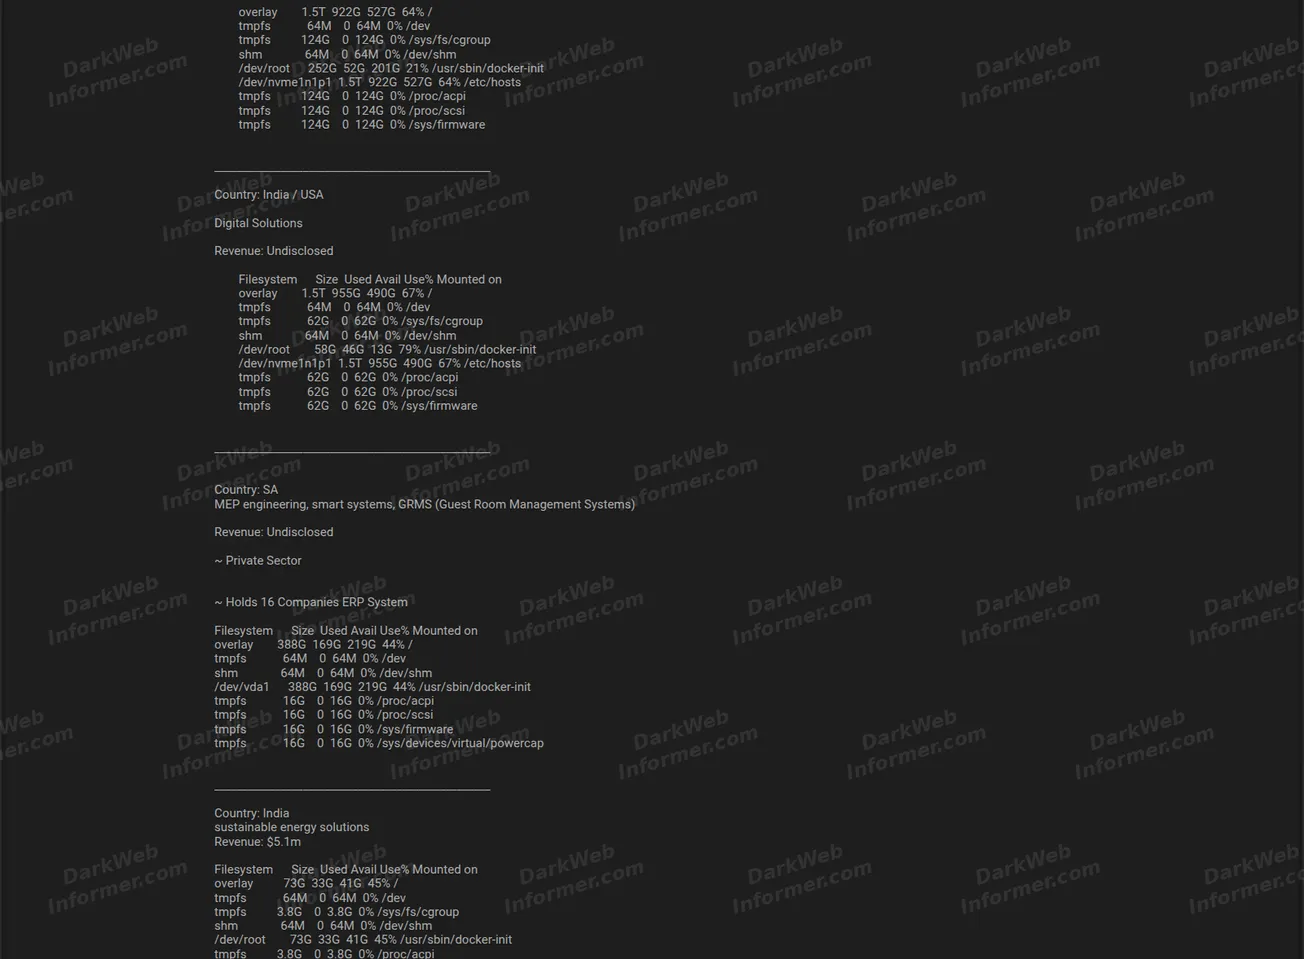
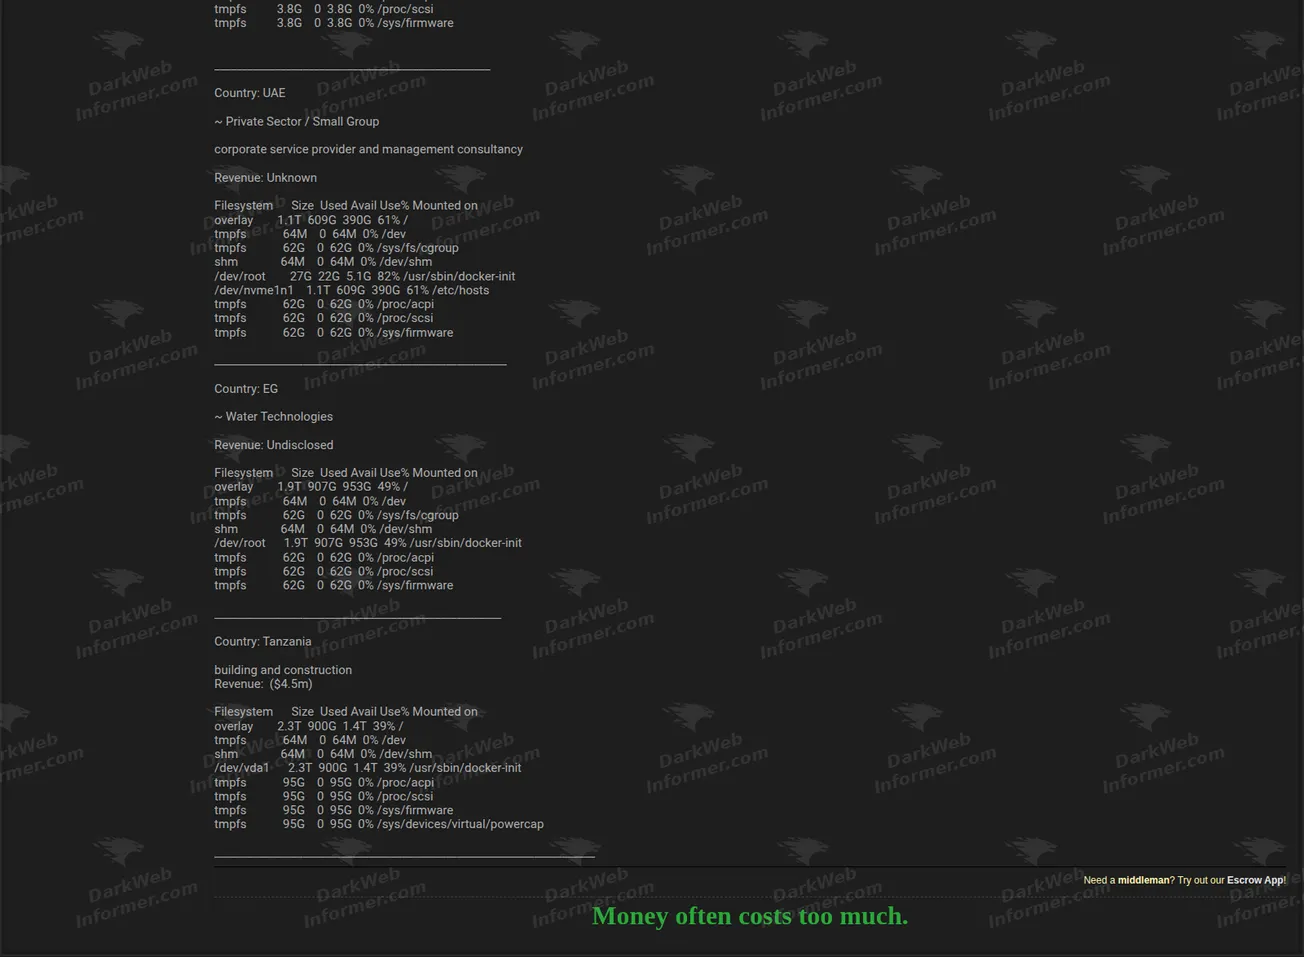
The actor states that all listed systems were compromised through an unpatched 0-day and describes access via a reverse shell, implant or agent installation, with a normal-user privilege level. The post provides sector descriptions, estimated revenue for some organizations, and filesystem/disk-usage output intended to demonstrate access. The access, exploitation method, victim identities, revenues and system details have not been independently verified.
Post details
Accesses described
- South Africa — IT consulting — claimed $22M revenue
- United States — AI-powered commercial credit intelligence — claimed $50M revenue
- Iraq — integrated engineering / technical consultancy — revenue undisclosed
- United States — vitamins, minerals and supplements — claimed $5.5M 2025 revenue
- India — automotive / railways — revenue undisclosed
- Austria — agricultural measurement / weighing / IT equipment — claimed €1.2M 2025 revenue
- India — LED-light industry — claimed $1.2M revenue
- India / United States — digital solutions — revenue undisclosed
- Saudi Arabia — MEP engineering / smart systems / GRMS — private sector
- India — sustainable-energy solutions — claimed $5.1M revenue
- United Arab Emirates — corporate services / management consultancy
- Egypt — water technologies — revenue undisclosed
- Tanzania — building and construction — claimed $4.5M revenue
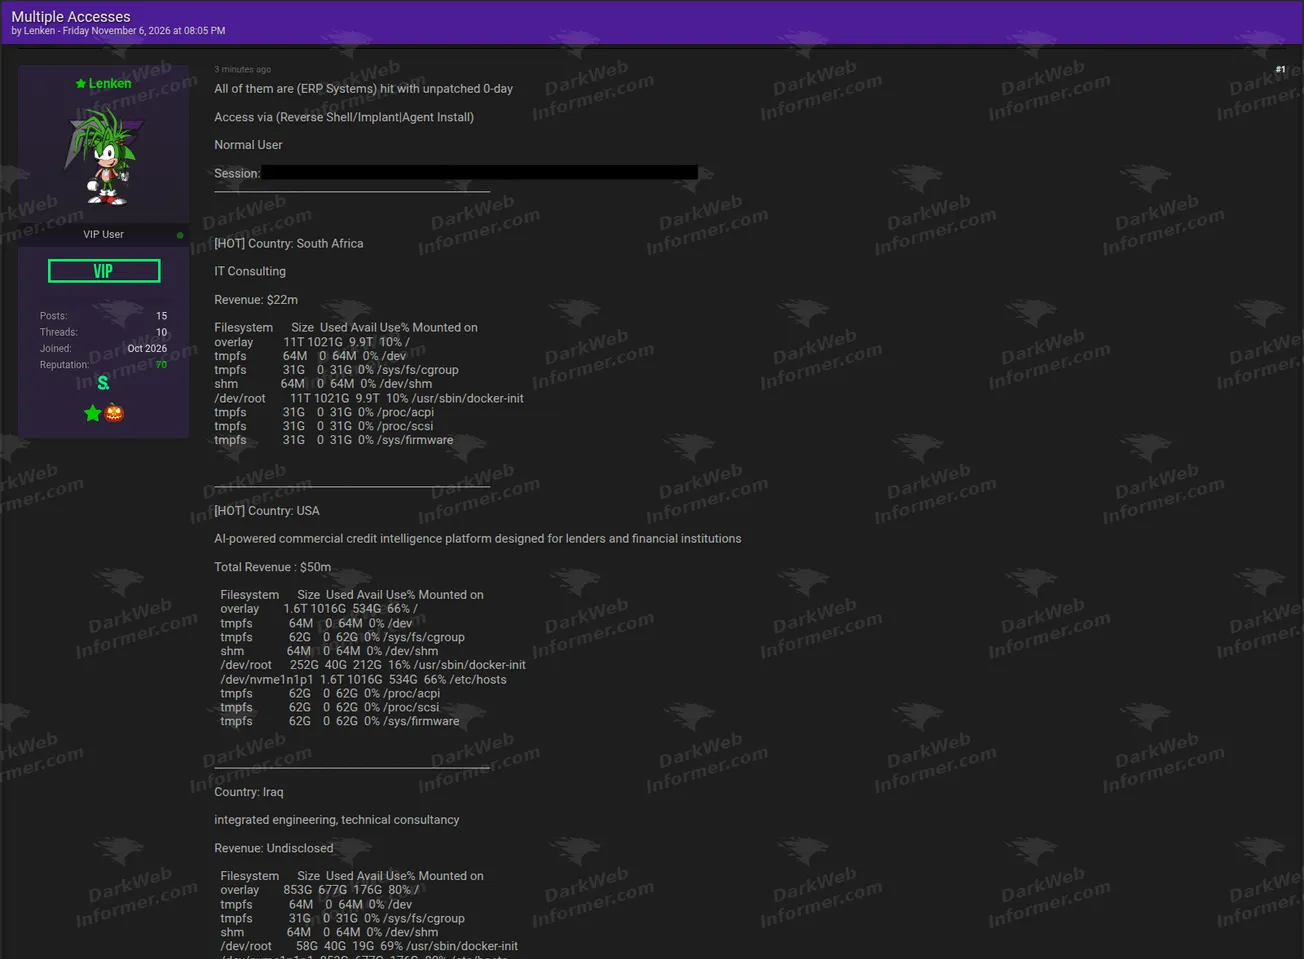
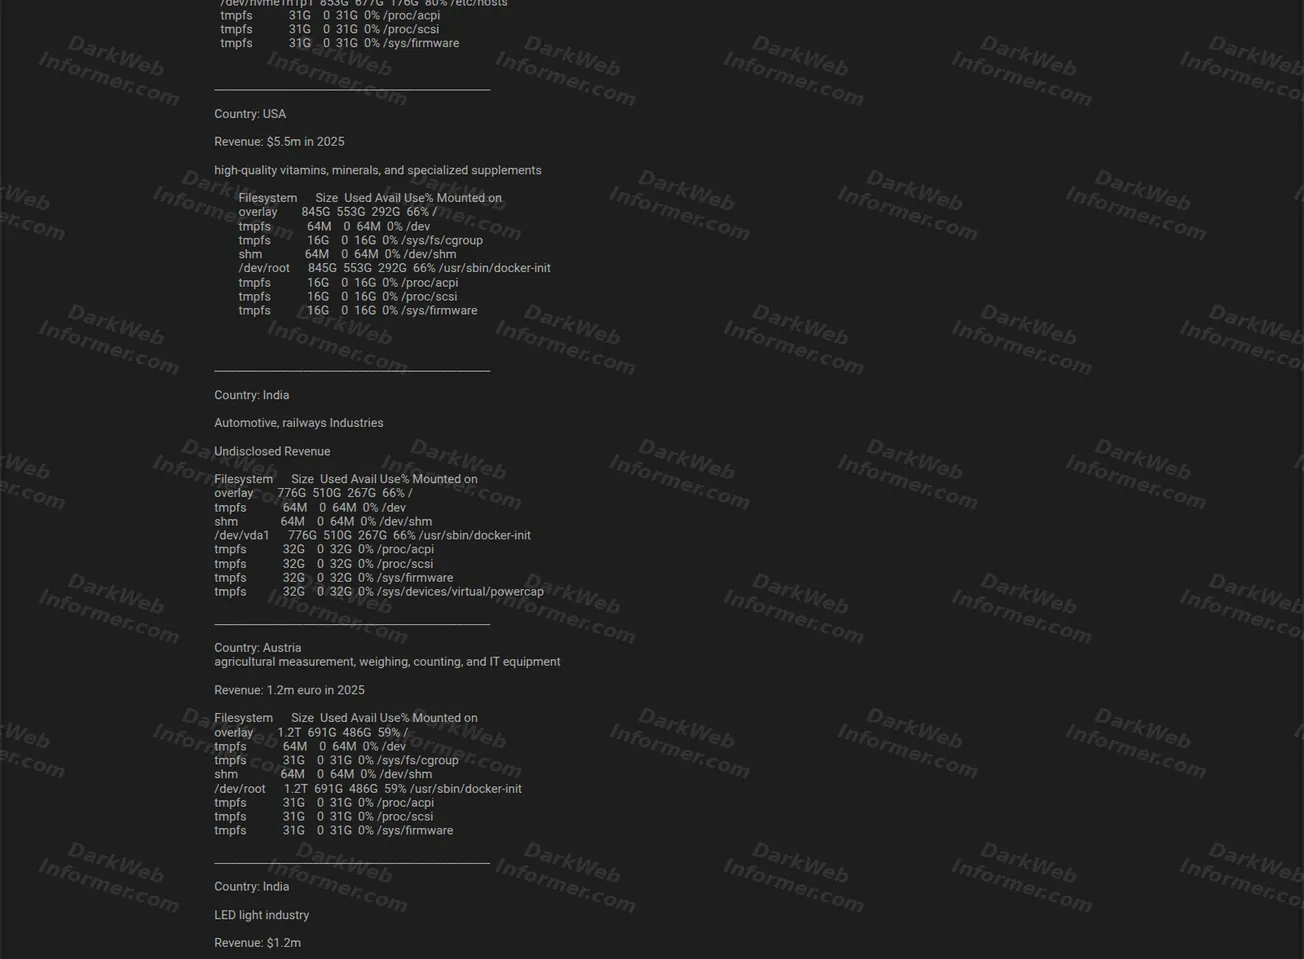
The post includes filesystem and disk-usage output for each entry as apparent proof-of-access. Those low-level system values are summarized rather than reproduced line-for-line here.
Screenshots
IOCs & identifiers
Identifiers directly visible in the supplied material. These support correlation and do not independently verify the access claims.
| Type | Identifier | Source |
|---|---|---|
| Actor handle | Lenken |
Screenshots 1–4 |
| Session ID | 0527974f9062fe413b0f33c25c21be244b9724617e18090af415bff61f845c0a35 |
Screenshot 1 |
No victim domains, malware hashes, Tox IDs, Telegram handles or public attacker-controlled IP addresses are visible in the supplied screenshots. Filesystem output and host-specific values are not reproduced here.
Mapped techniques
Claimed identifies behavior explicitly described by the actor. Inferred identifies an analytical mapping supported by the supplied material. Neither label means the activity has been independently verified.
- Initial AccessT1190Exploit Public-Facing ApplicationInferredThe actor claims the ERP environments were compromised through an unpatched 0-day vulnerability. The exact vulnerable product and exploitation path are not shown.
Potential impact
If authentic, the accesses could give an operator a foothold inside ERP environments across consulting, finance, engineering, manufacturing, energy, construction and other sectors. Even at a claimed normal-user privilege level, persistent shell or agent access could create risks of data theft, credential abuse, lateral movement, operational disruption or resale to other threat actors.
Status Unverified
Dark Web Informer has not independently verified the existence of the alleged 0-day, the listed ERP compromises, victim identities, access level, revenue figures, shell/agent persistence or filesystem evidence. The supplied screenshots document the actor’s claims only.
Source: Dark Web Informer · 2026-11-06